
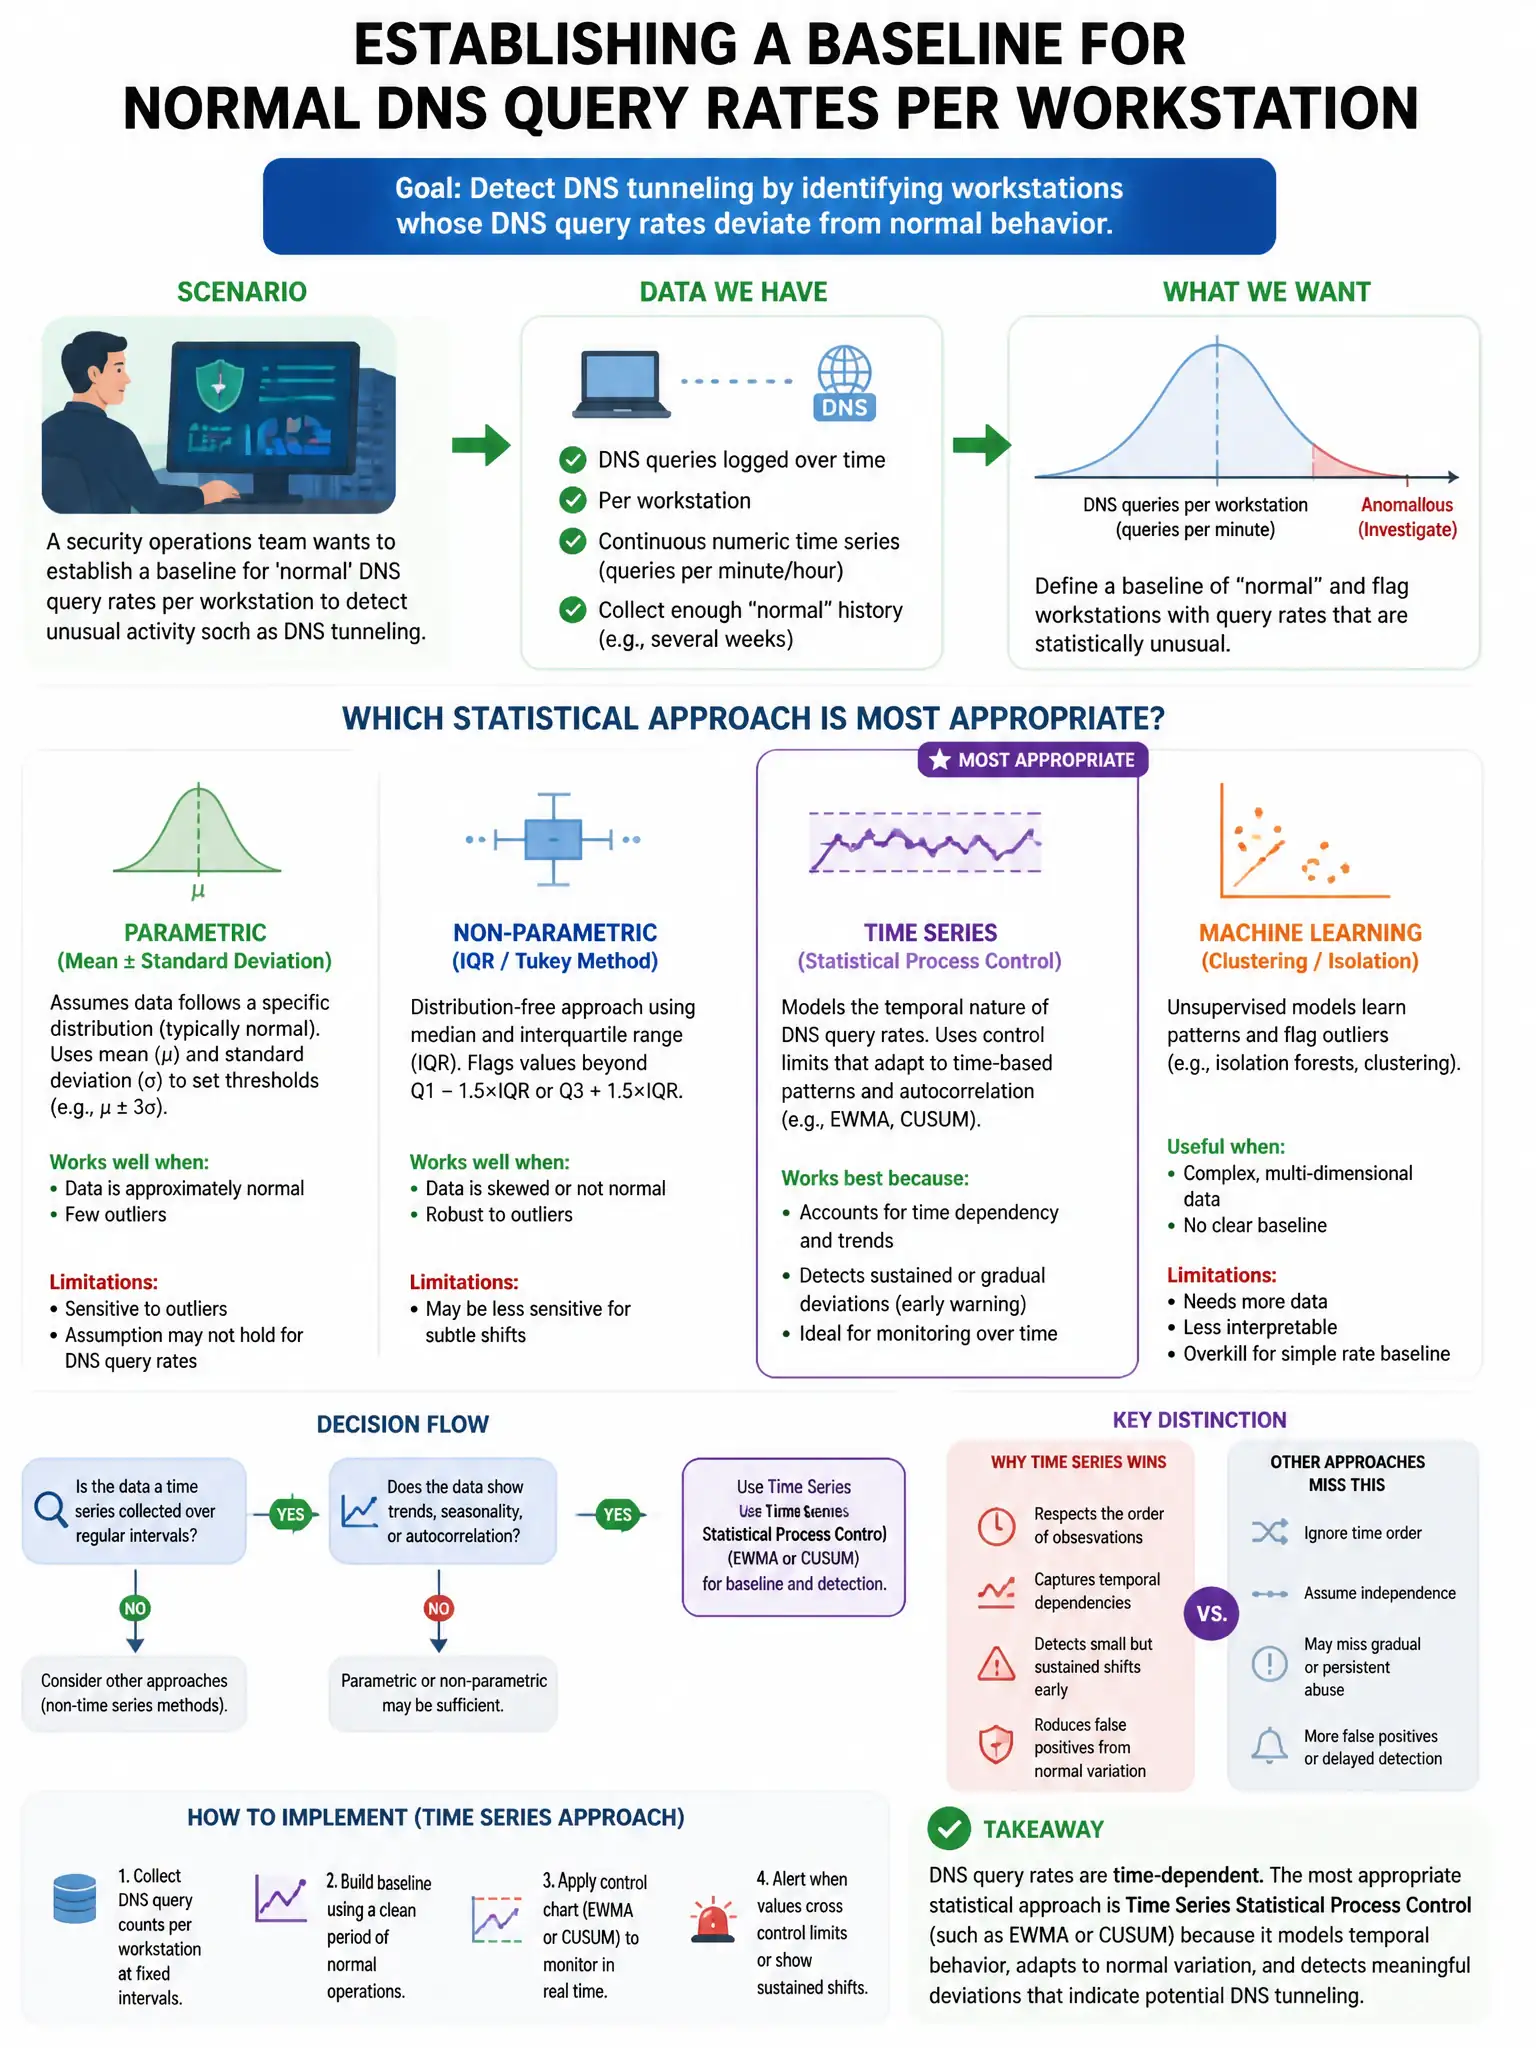
A security operations team wants to establish a baseline for 'normal' DNS query rates per workstation to detect DNS tunneling. Which statistical approach is most appropriate for anomaly detection?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need per-host statistical baselining to spot DNS tunneling. A rolling mean and standard deviation over a 30-day baseline accounts for normal variation between workstations and flags only meaningful anomalies.
Full Explanation
The rolling mean and standard deviation approach is correct because per-host statistical baselining accounts for the natural variation between workstations, such as a developer's laptop versus a kiosk, and detects relative anomalies rather than relying on absolute thresholds that may miss low-and-slow tunneling or over-alert on power users. A static threshold of 100 DNS queries per hour for all workstations is wrong because a universal static threshold generates false positives on high-usage hosts and misses tunneling on low-usage hosts. Counting total organizational DNS queries per day and alerting if the daily total doubles is wrong because org-wide daily totals mask individual host behavior. Alerting on any DNS query containing more than 10 characters in the subdomain label is wrong because many legitimate domains have subdomains exceeding 10 characters, so this threshold would generate massive false positives.