
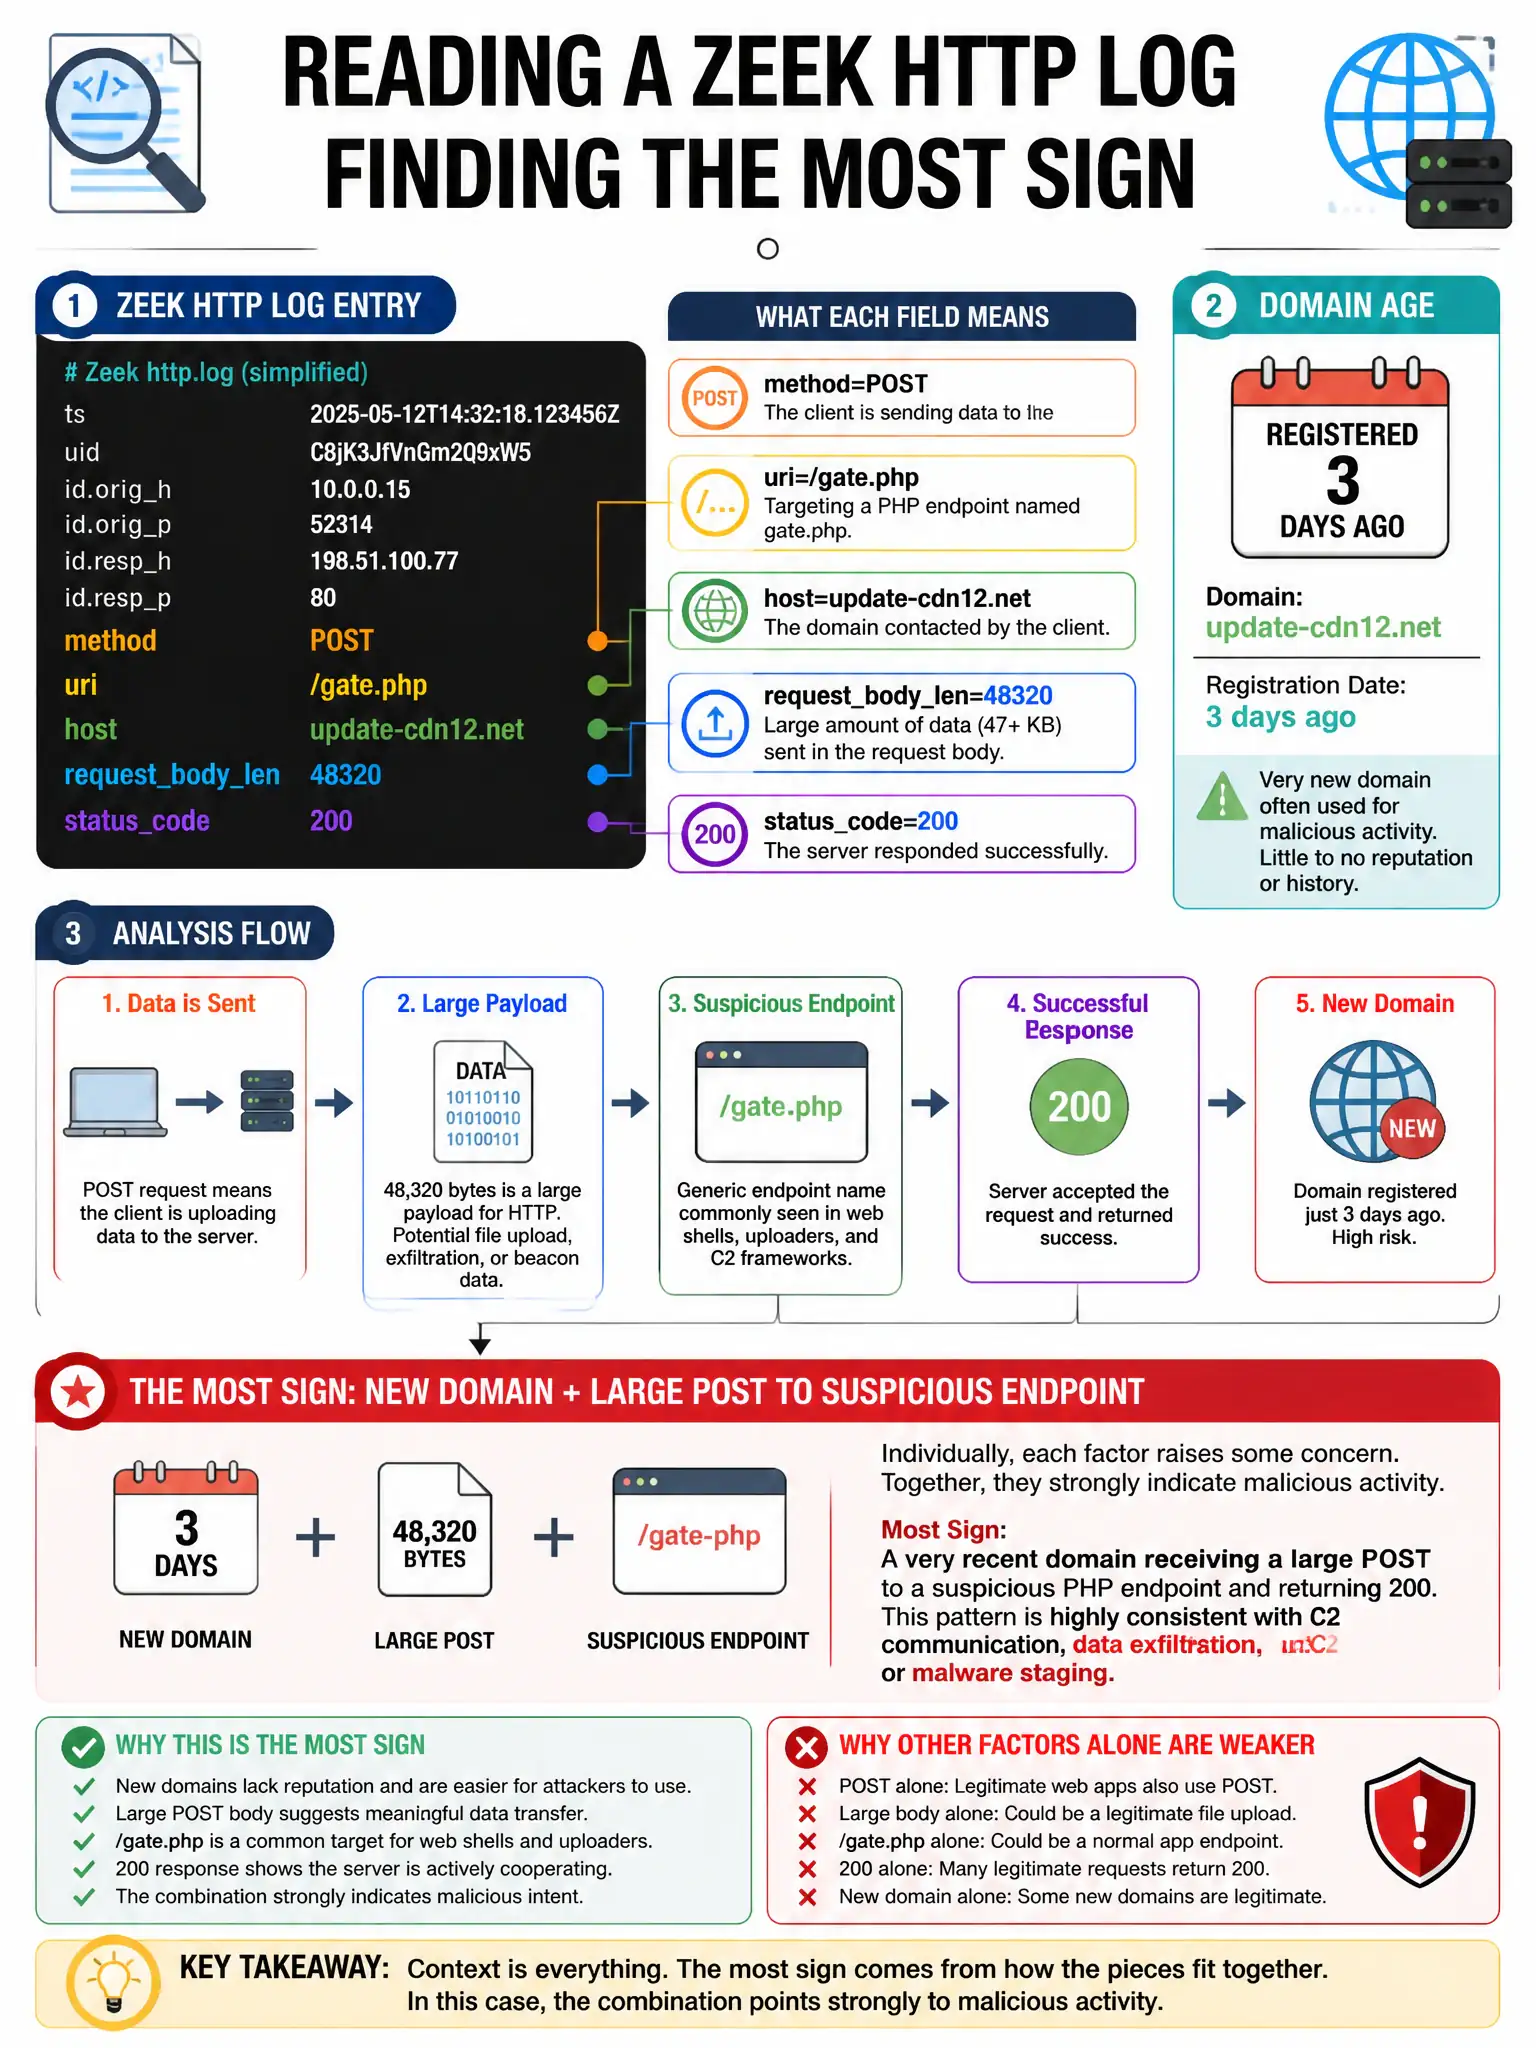
A Zeek http.log entry shows: method=POST, uri=/gate.php, host=update-cdn12.net, request_body_len=48320, status_code=200. The domain was registered 3 days ago. What is the most significant indicator of compromise in this log entry?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you should focus on the combination of a newly registered lookalike domain, a command-and-control-style gate.php URI, and a large outbound POST body. That pattern points to command-and-control and possible data exfiltration. Lone POST usage, a 200 response, or a 48 KB body isn't enough on its own.
Full Explanation
The correct indicator is the combination of a newly registered lookalike domain, a URI path typical of command-and-control gate scripts, and a large outbound POST body. The domain age of 3 days, the gate.php path matching known command-and-control frameworks, and the roughly 47 KB outbound POST body together form a high-confidence exfiltration or command-and-control indicator. The claim that the HTTP POST method is never used legitimately is wrong because POST is a standard HTTP method used constantly for legitimate form submissions, APIs, and uploads. The 200 OK response code is wrong as a primary indicator because it merely indicates the remote server responded; it is neutral. The request body length of 48320 bytes is wrong because HTTP has no standard body size limit, and 48 KB is not inherently anomalous in isolation.