
A security analyst receives a PCAP file and is asked to determine if data exfiltration occurred over HTTPS to a known-bad IP. SSL/TLS inspection is not available. Which technique provides the most useful intelligence without decrypting the traffic?
Select an answer to reveal the explanation.
Short Explanation
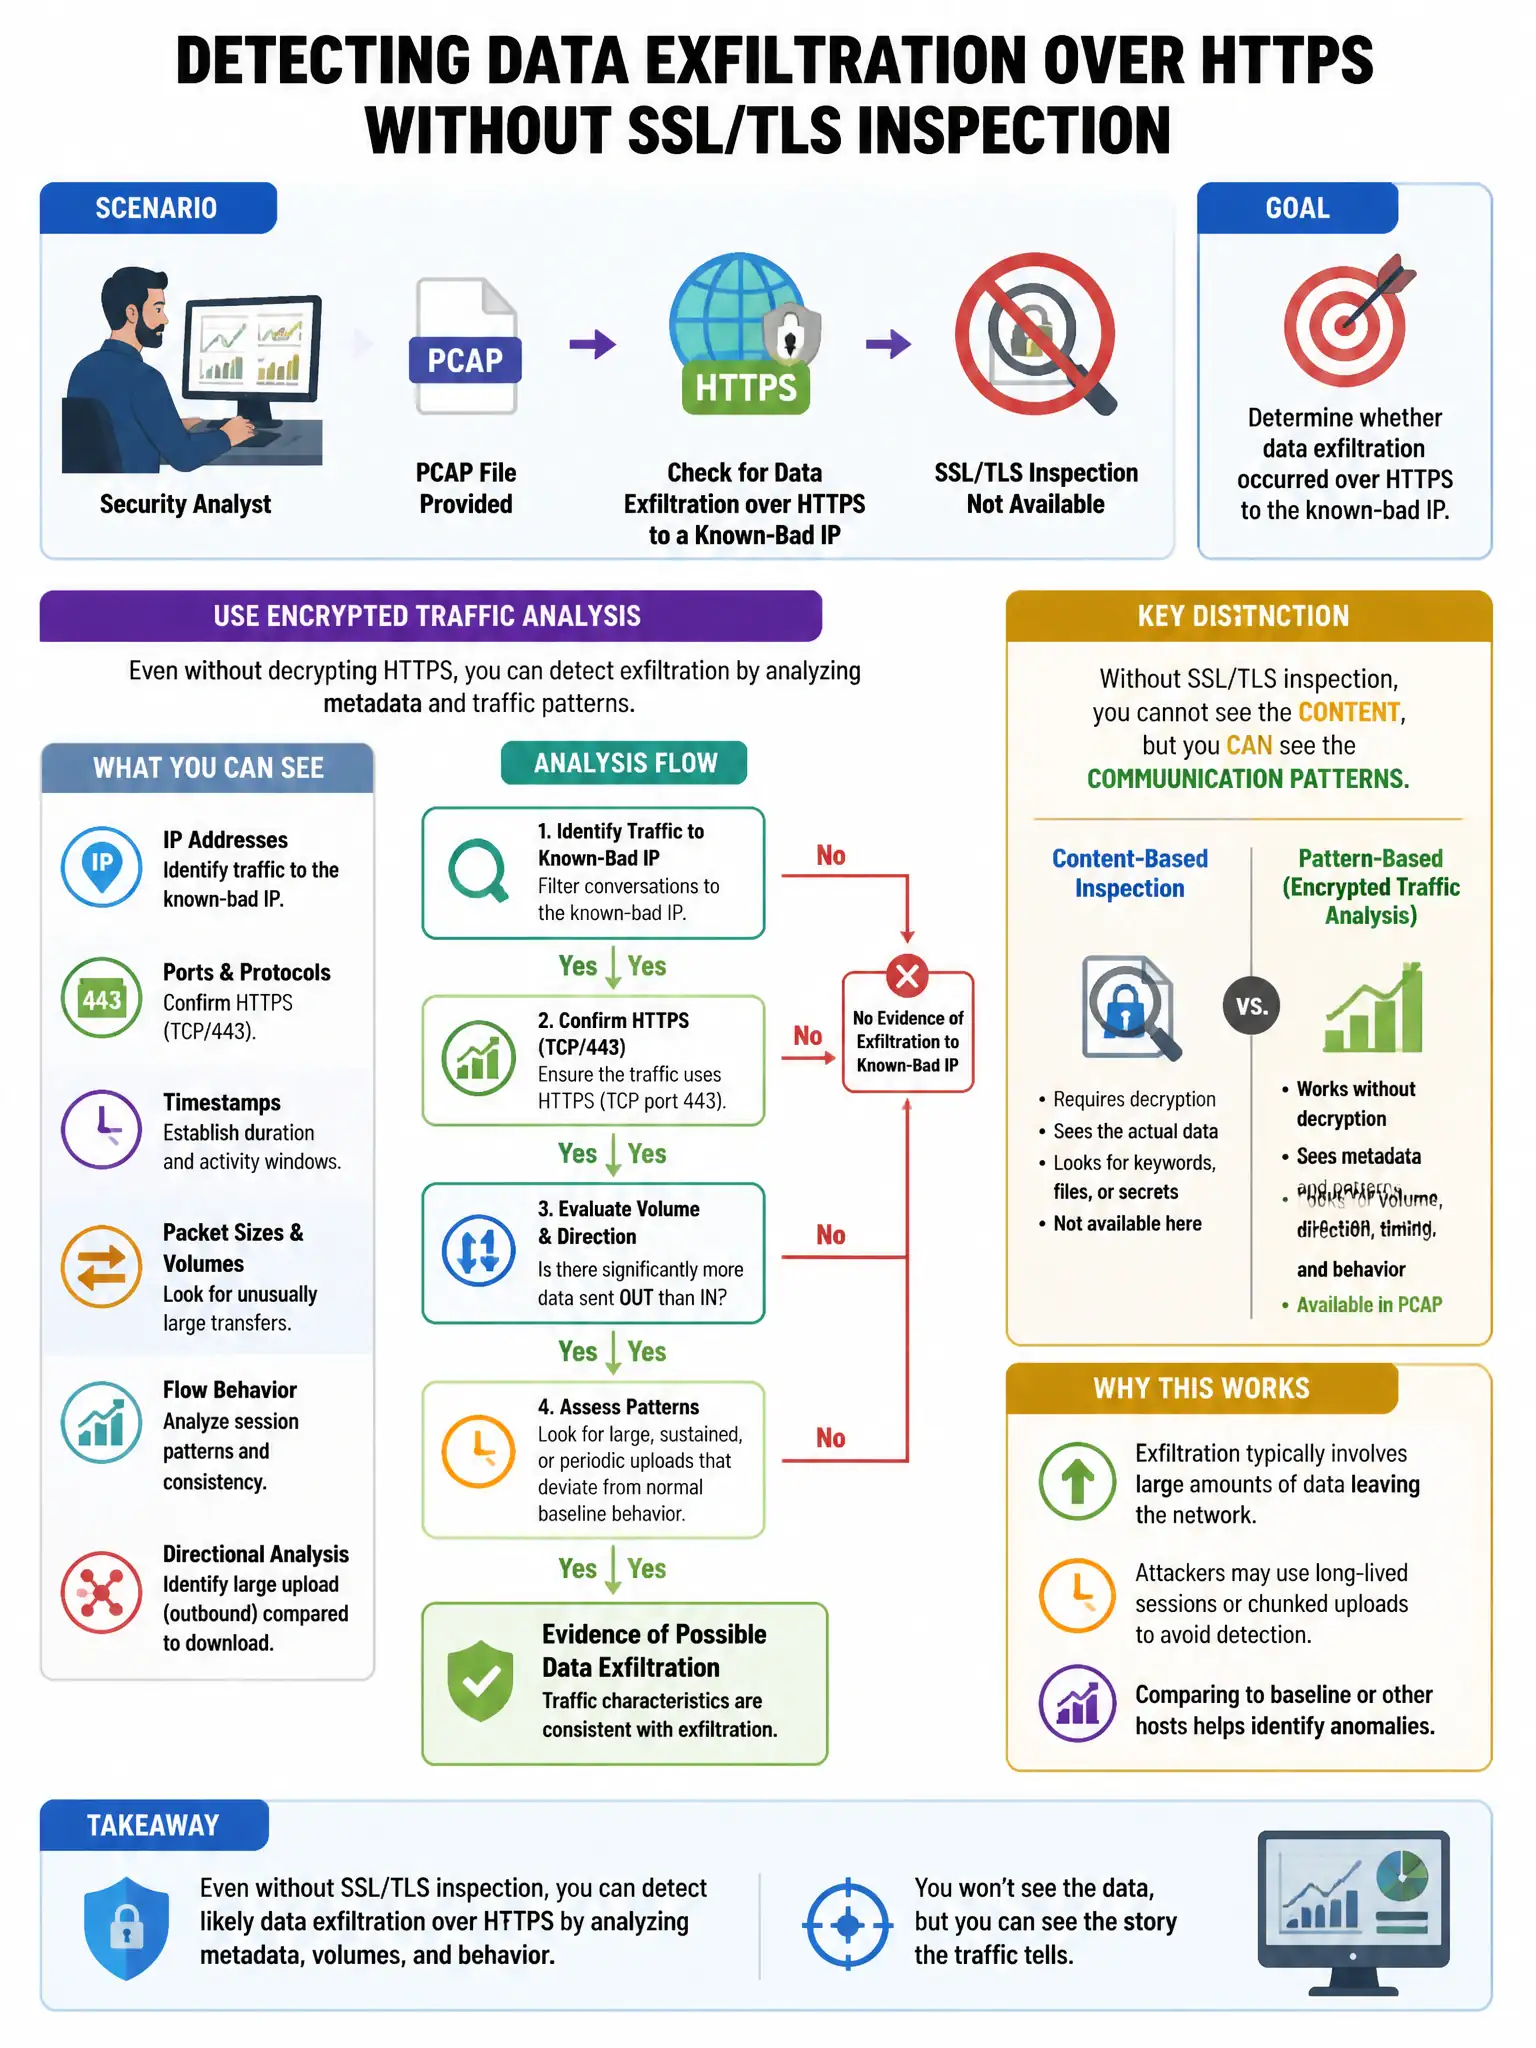
Here's the deal — you analyze TLS metadata because even without decryption, certificate anomalies, TLS fingerprints matching known malware, large asymmetric data transfers, and beaconing intervals give you strong exfiltration indicators without breaking encryption. Brute-forcing TLS session keys is computationally infeasible in practice.
Full Explanation
Analyzing TLS metadata is correct because even without decryption, certificate Subject/Issuer anomalies, JA3/JA3S fingerprints matching known malware, session duration, bytes transferred, and timing/beaconing intervals correlate with known command-and-control profiles and provide strong exfiltration indicators without breaking encryption. Attempting a brute-force decryption of the TLS session keys is wrong because brute-forcing TLS session keys is computationally infeasible in practice. Blocking the IP and declaring the incident closed is wrong because blocking without analysis does not confirm exfiltration and destroys the investigative opportunity. Running strings on the PCAP to extract the plaintext payload is wrong because TLS encrypts the payload; strings will only show handshake metadata, not application data.