
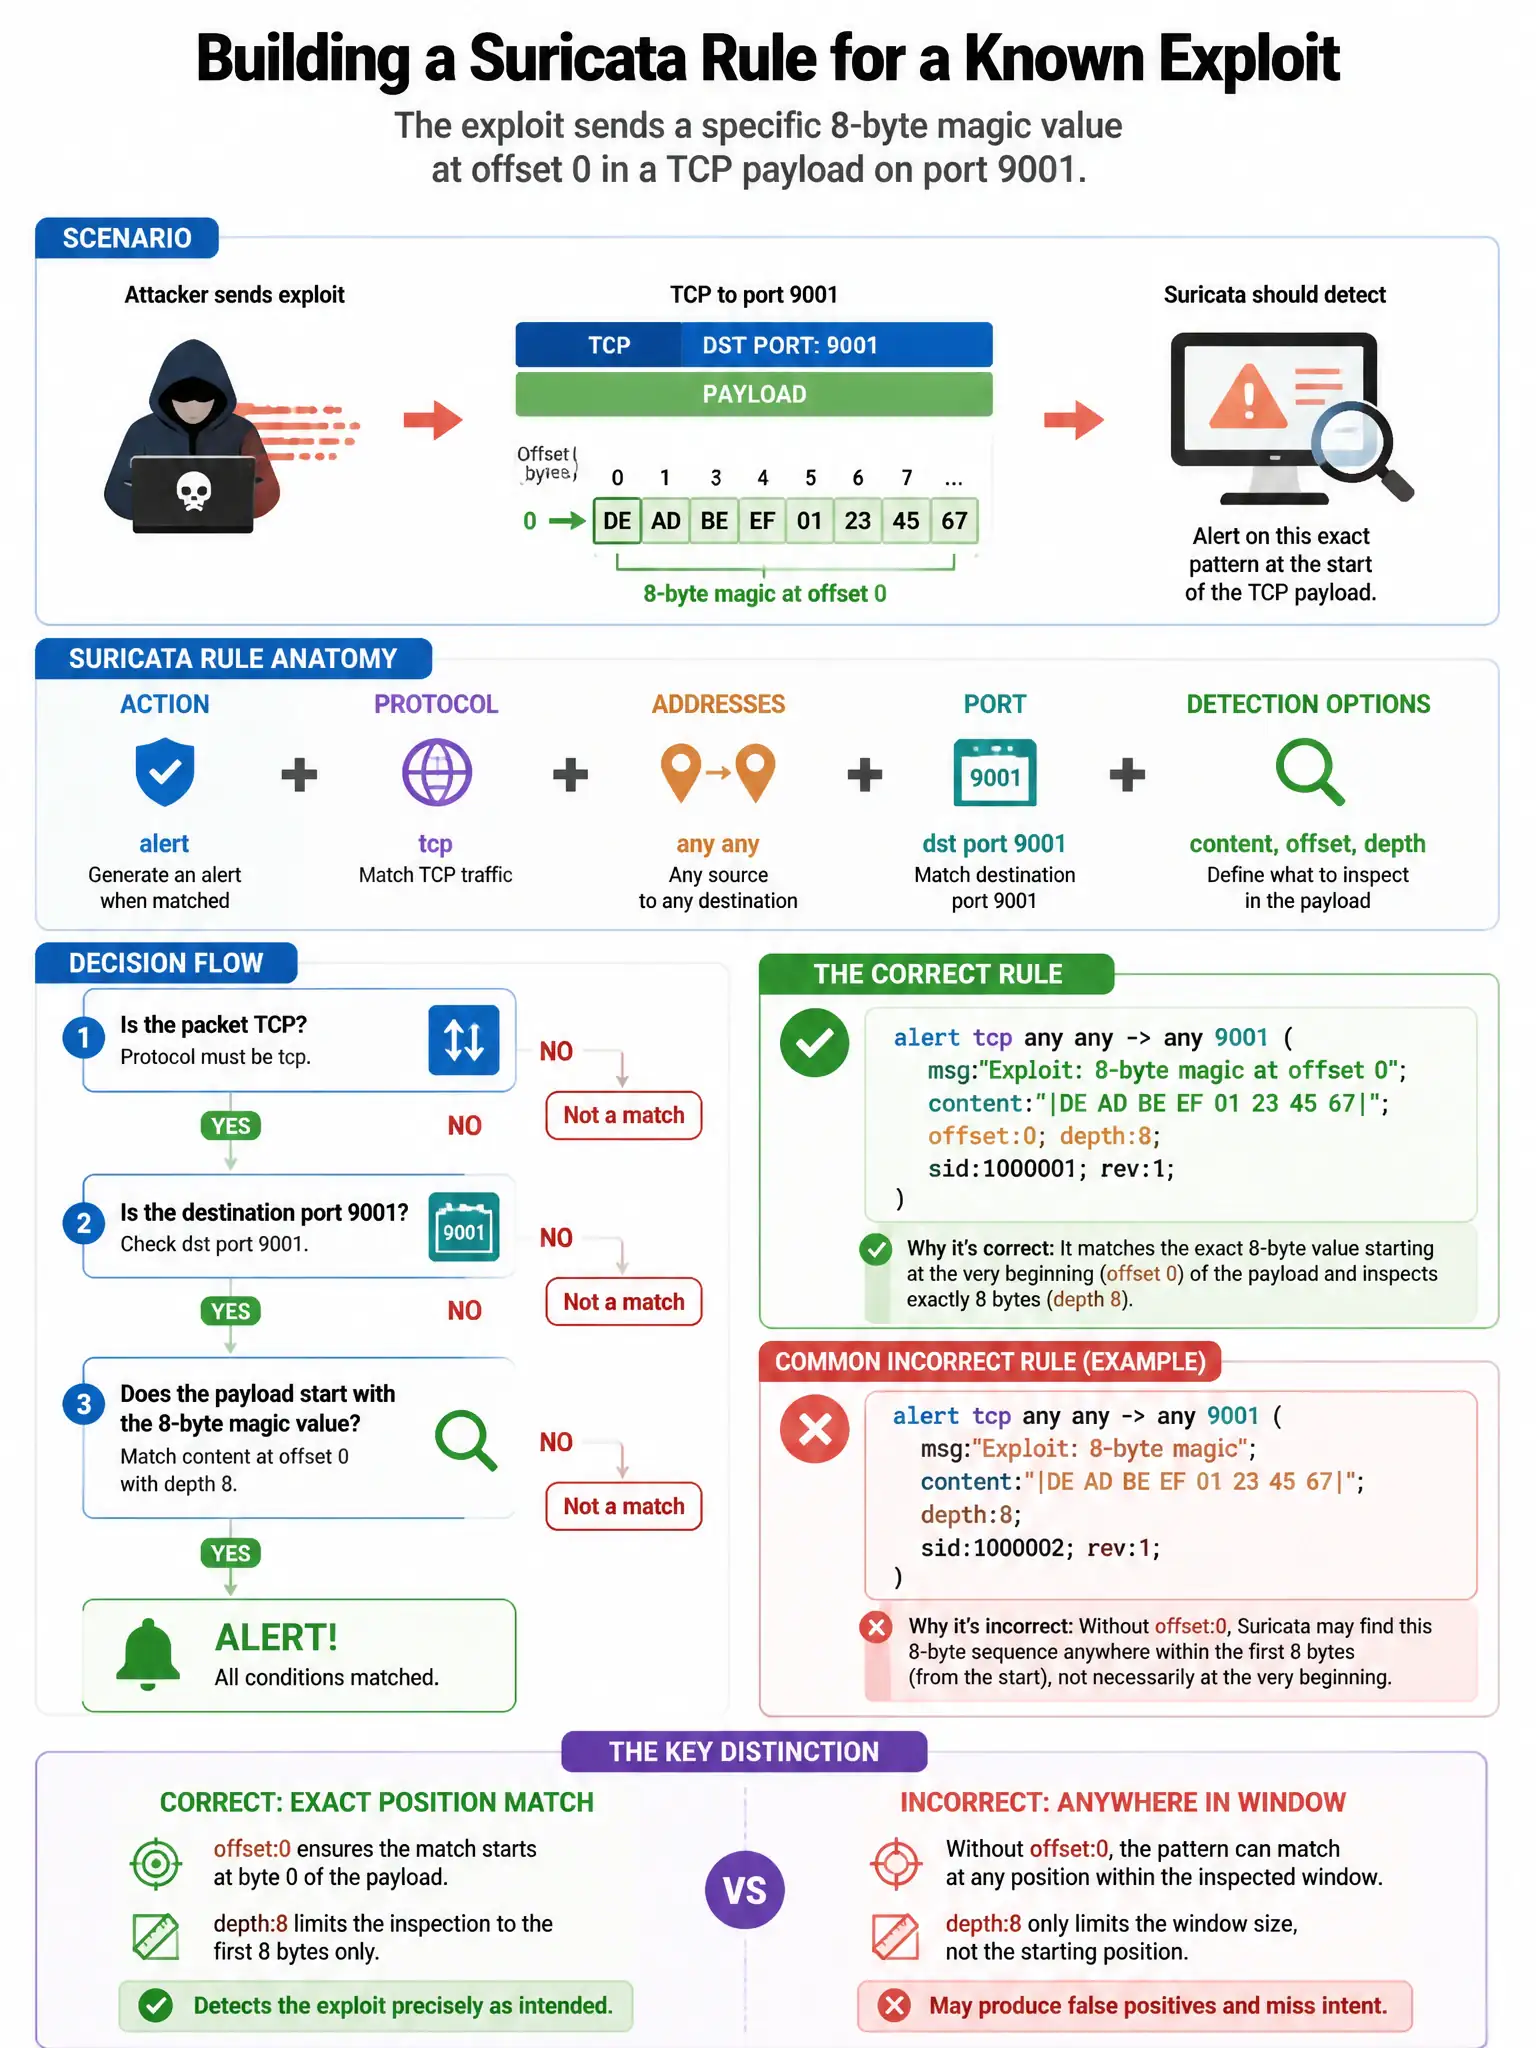
An analyst is building a Suricata detection rule for a known exploit that sends a specific 8-byte magic value at offset 0 in a TCP payload on port 9001. Which rule syntax correctly captures this?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need TCP on port 9001 and the exact magic bytes at the start of the payload, so use the TCP rule with content:'|DE AD BE EF CA FE BA BE|', offset:0, and depth:8. That pins the match to the first 8 bytes.
Full Explanation
The TCP rule with destination port 9001, content:'|DE AD BE EF CA FE BA BE|', offset:0, and depth:8 is correct because it specifies TCP protocol, destination port 9001, the exact hex content, and offset:0 plus depth:8 constraining the match to the first 8 bytes of the payload, which is the precise requirement. The UDP rule with the same content is wrong because UDP is the wrong protocol. The TCP rule using a NOP sled PCRE is wrong because a NOP sled PCRE is unrelated to the described magic bytes pattern. The IP rule using dsize:8 is wrong because matching on IP with dsize:8 only checks packet size, not payload content, and would match any 8-byte IP packet.