
A SIEM analyst needs to establish a behavioral baseline for normal SSH login activity. Which metric combination is MOST useful for effective anomaly detection?
Select an answer to reveal the explanation.
Short Explanation
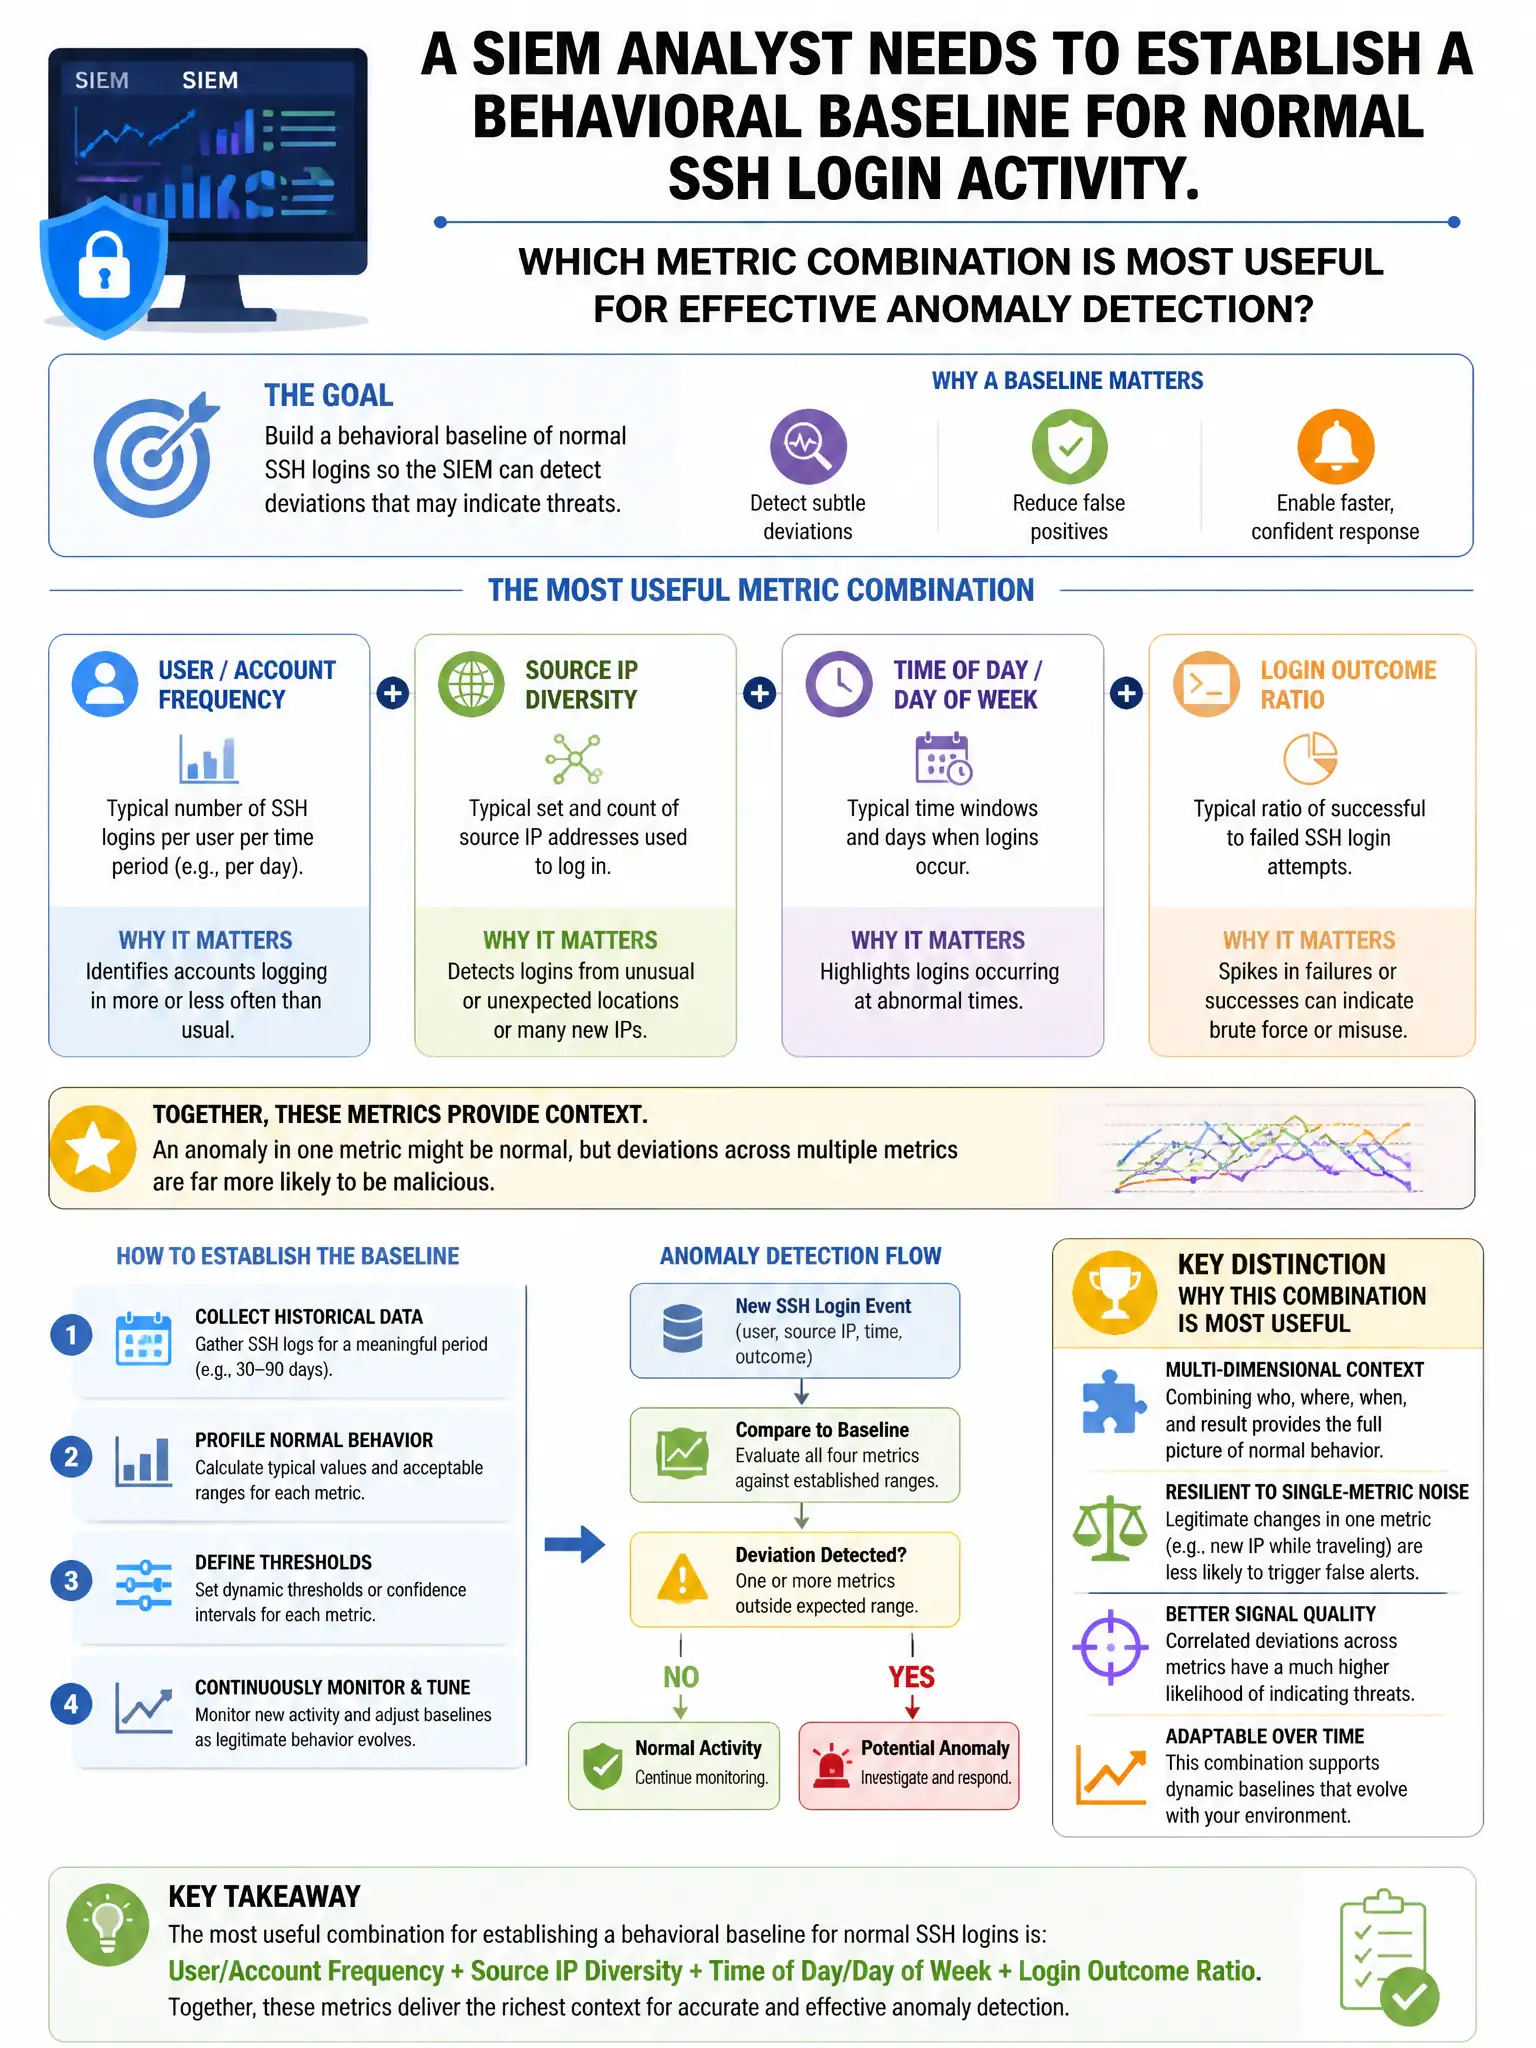
Here's the deal — the comprehensive baseline is correct because it captures who logs in, from where, when, to what systems, and success rates, letting you spot deviations that may indicate brute force, credential stuffing, or unauthorized access. Total connections and session duration alone miss geographic, temporal, and target system anomalies.
Full Explanation
The comprehensive baseline is correct because it captures multiple dimensions — typical source IPs, login times, destination systems, username patterns, and authentication success-to-failure ratios measured over a 30-day period — enabling detection of deviations in any dimension that may indicate brute force, credential stuffing, or unauthorized access. The total connections and session duration option is wrong because total connections and session duration alone miss geographic, temporal, and target system anomalies. The unique usernames per hour option is wrong because unique username counts alone provide insufficient context for meaningful anomaly detection. The SSH daemon version option is wrong because SSH daemon version is a configuration detail, not a behavioral baseline metric.