
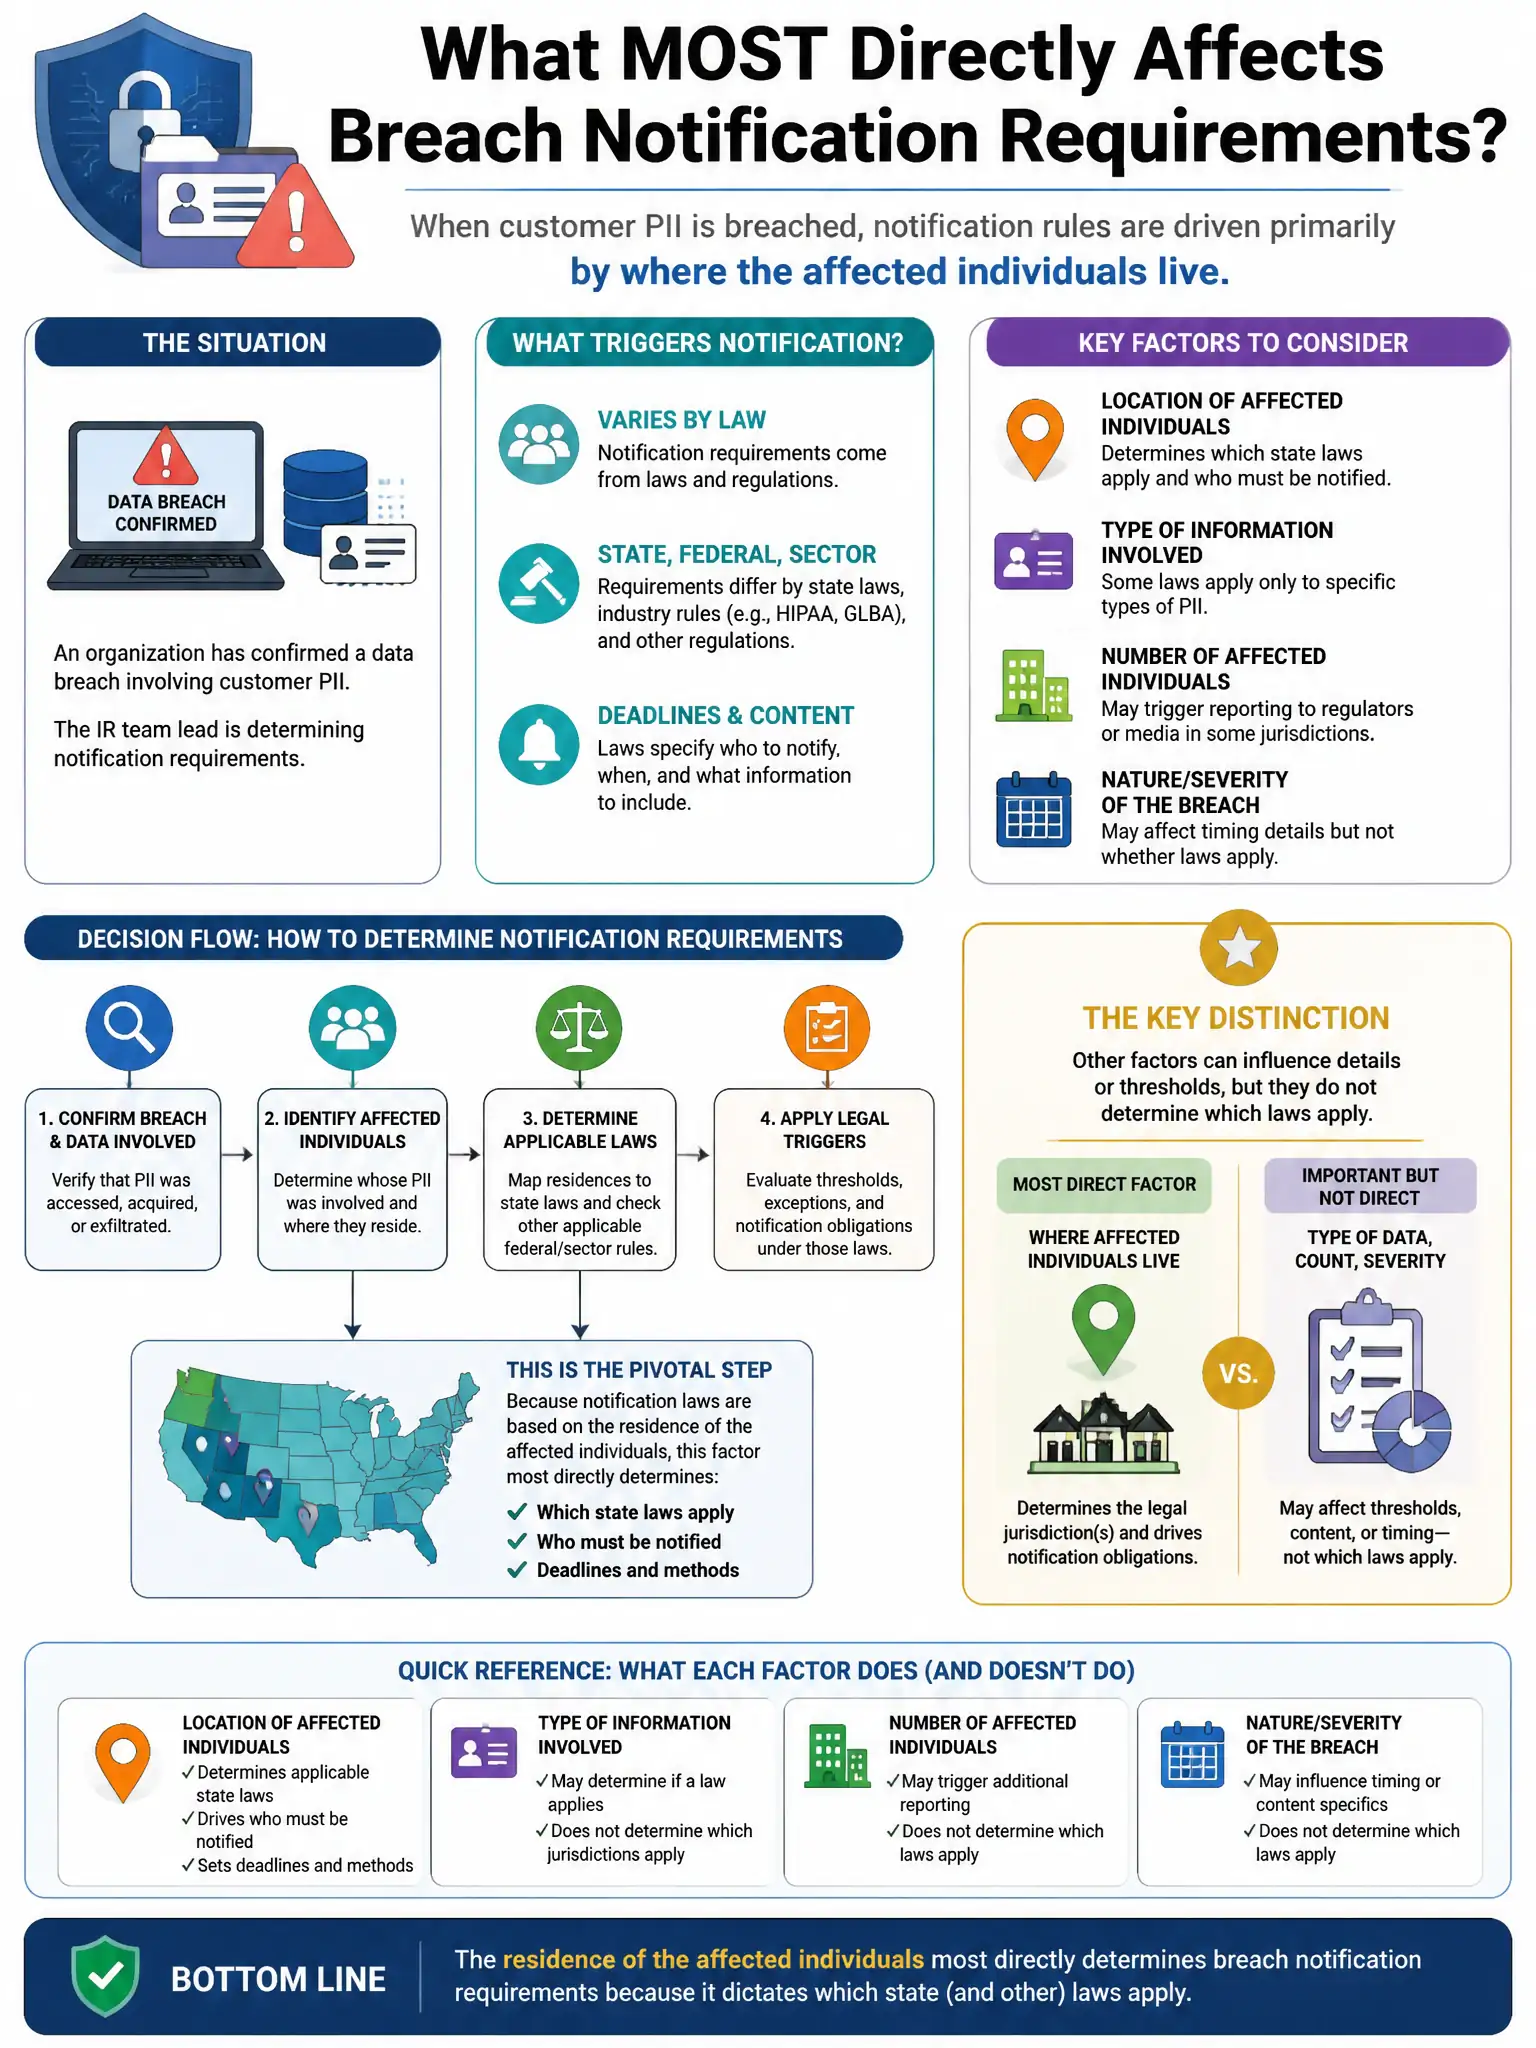
An organization has confirmed a data breach involving customer PII. The IR team lead is determining notification requirements. Which factor MOST directly affects breach notification timelines?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you follow the clock set by applicable regulations and contracts. GDPR's 72-hour rule, HIPAA, state laws, and payment-card agreements drive breach notification timing.
Full Explanation
The correct factor is applicable regulatory requirements such as the GDPR 72-hour rule and state breach notification laws, along with contractual obligations. Notification timelines are primarily governed by regulatory requirements — GDPR mandates 72 hours, HIPAA has specific requirements, US states have varying laws — and contractual obligations including payment card industry agreements. The total cost of the forensic investigation engagement is wrong because investigation cost affects budget, not notification timing requirements. Whether the attacker has been identified and arrested by law enforcement is wrong because attacker identification is not a prerequisite for breach notification under any major regulation. The organization's cyber insurance policy deductible and coverage limits is wrong because insurance deductibles relate to financial recovery, not legal notification obligations.