
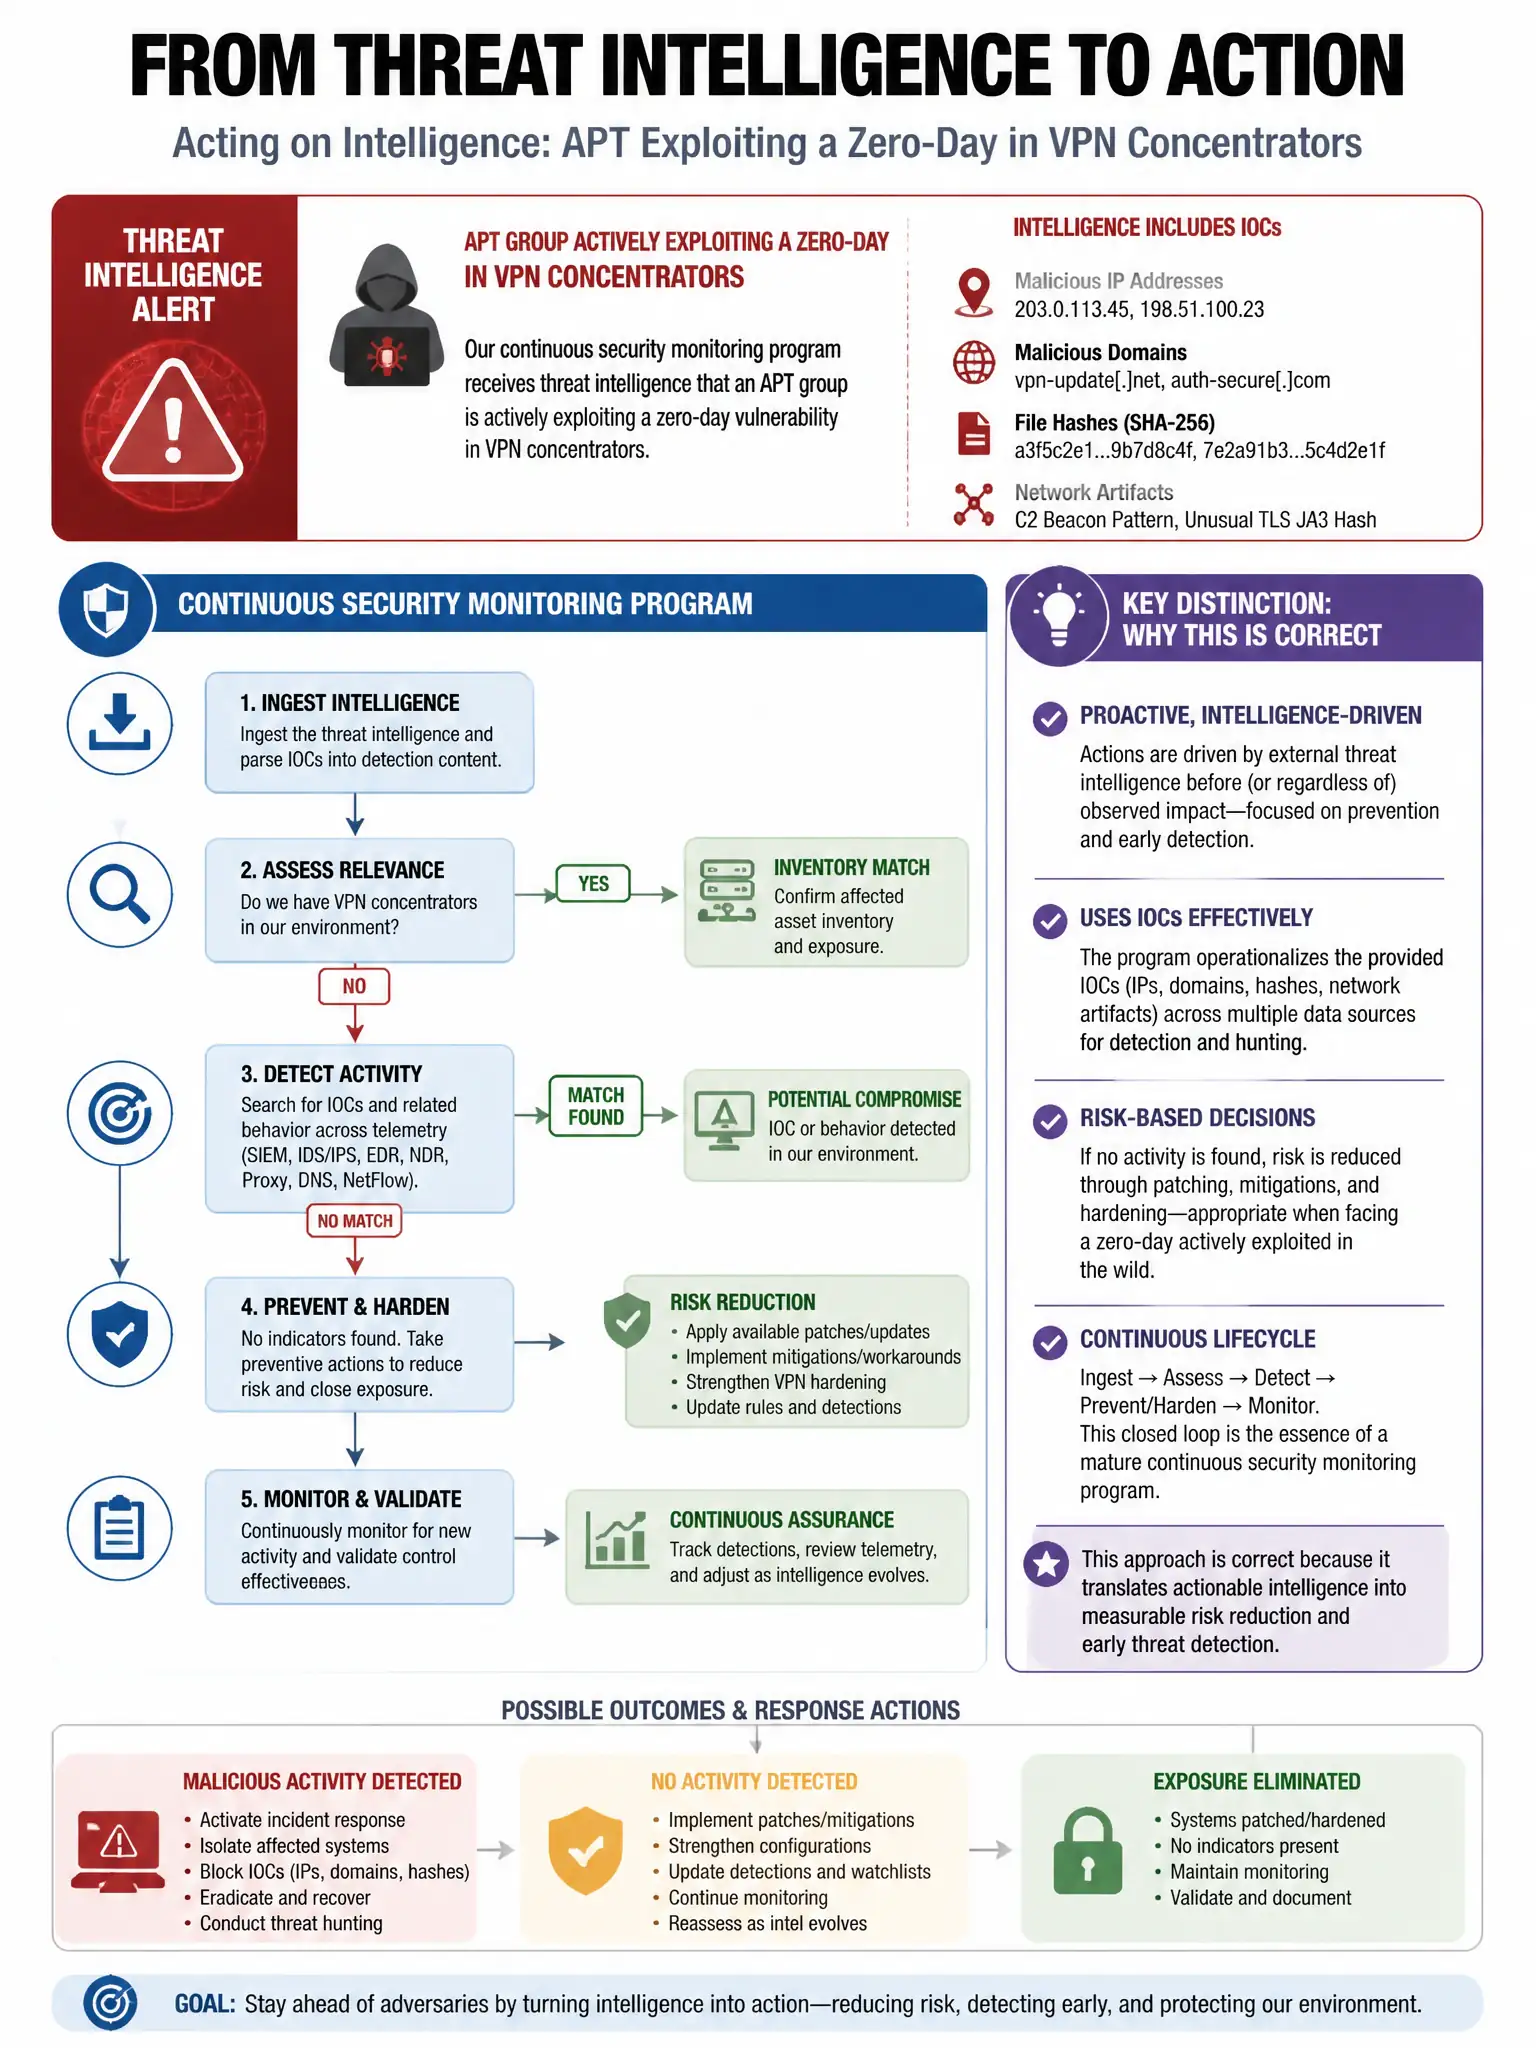
A continuous security monitoring program receives threat intelligence indicating an APT group is actively exploiting a zero-day in VPN concentrators. The intelligence includes IOCs such as specific IP addresses and file hashes. What is the MOST effective immediate use of this intelligence?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you should ingest the IOCs into SIEM and EDR platforms, hunt through historical logs for matches, and set alerting rules for future hits. That turns threat intel into immediate detection and response.
Full Explanation
The most effective immediate use is to ingest the IOCs into SIEM and EDR platforms, search historical logs for matches, and configure alerting rules for future IOC matches. This operationalizes the intelligence by detecting known indicators now, hunting for prior compromise, and enabling rapid response if indicators reappear. Sending the intelligence report to executives for awareness and strategic planning only is wrong because executive awareness without technical action does not reduce risk. Waiting for the vendor to release a patch before taking any defensive action is wrong because it misses the opportunity to detect existing compromises; blocking on IOCs provides immediate value. Blocking all VPN access until the threat is fully resolved is wrong because it causes unacceptable business impact when targeted controls are available.