
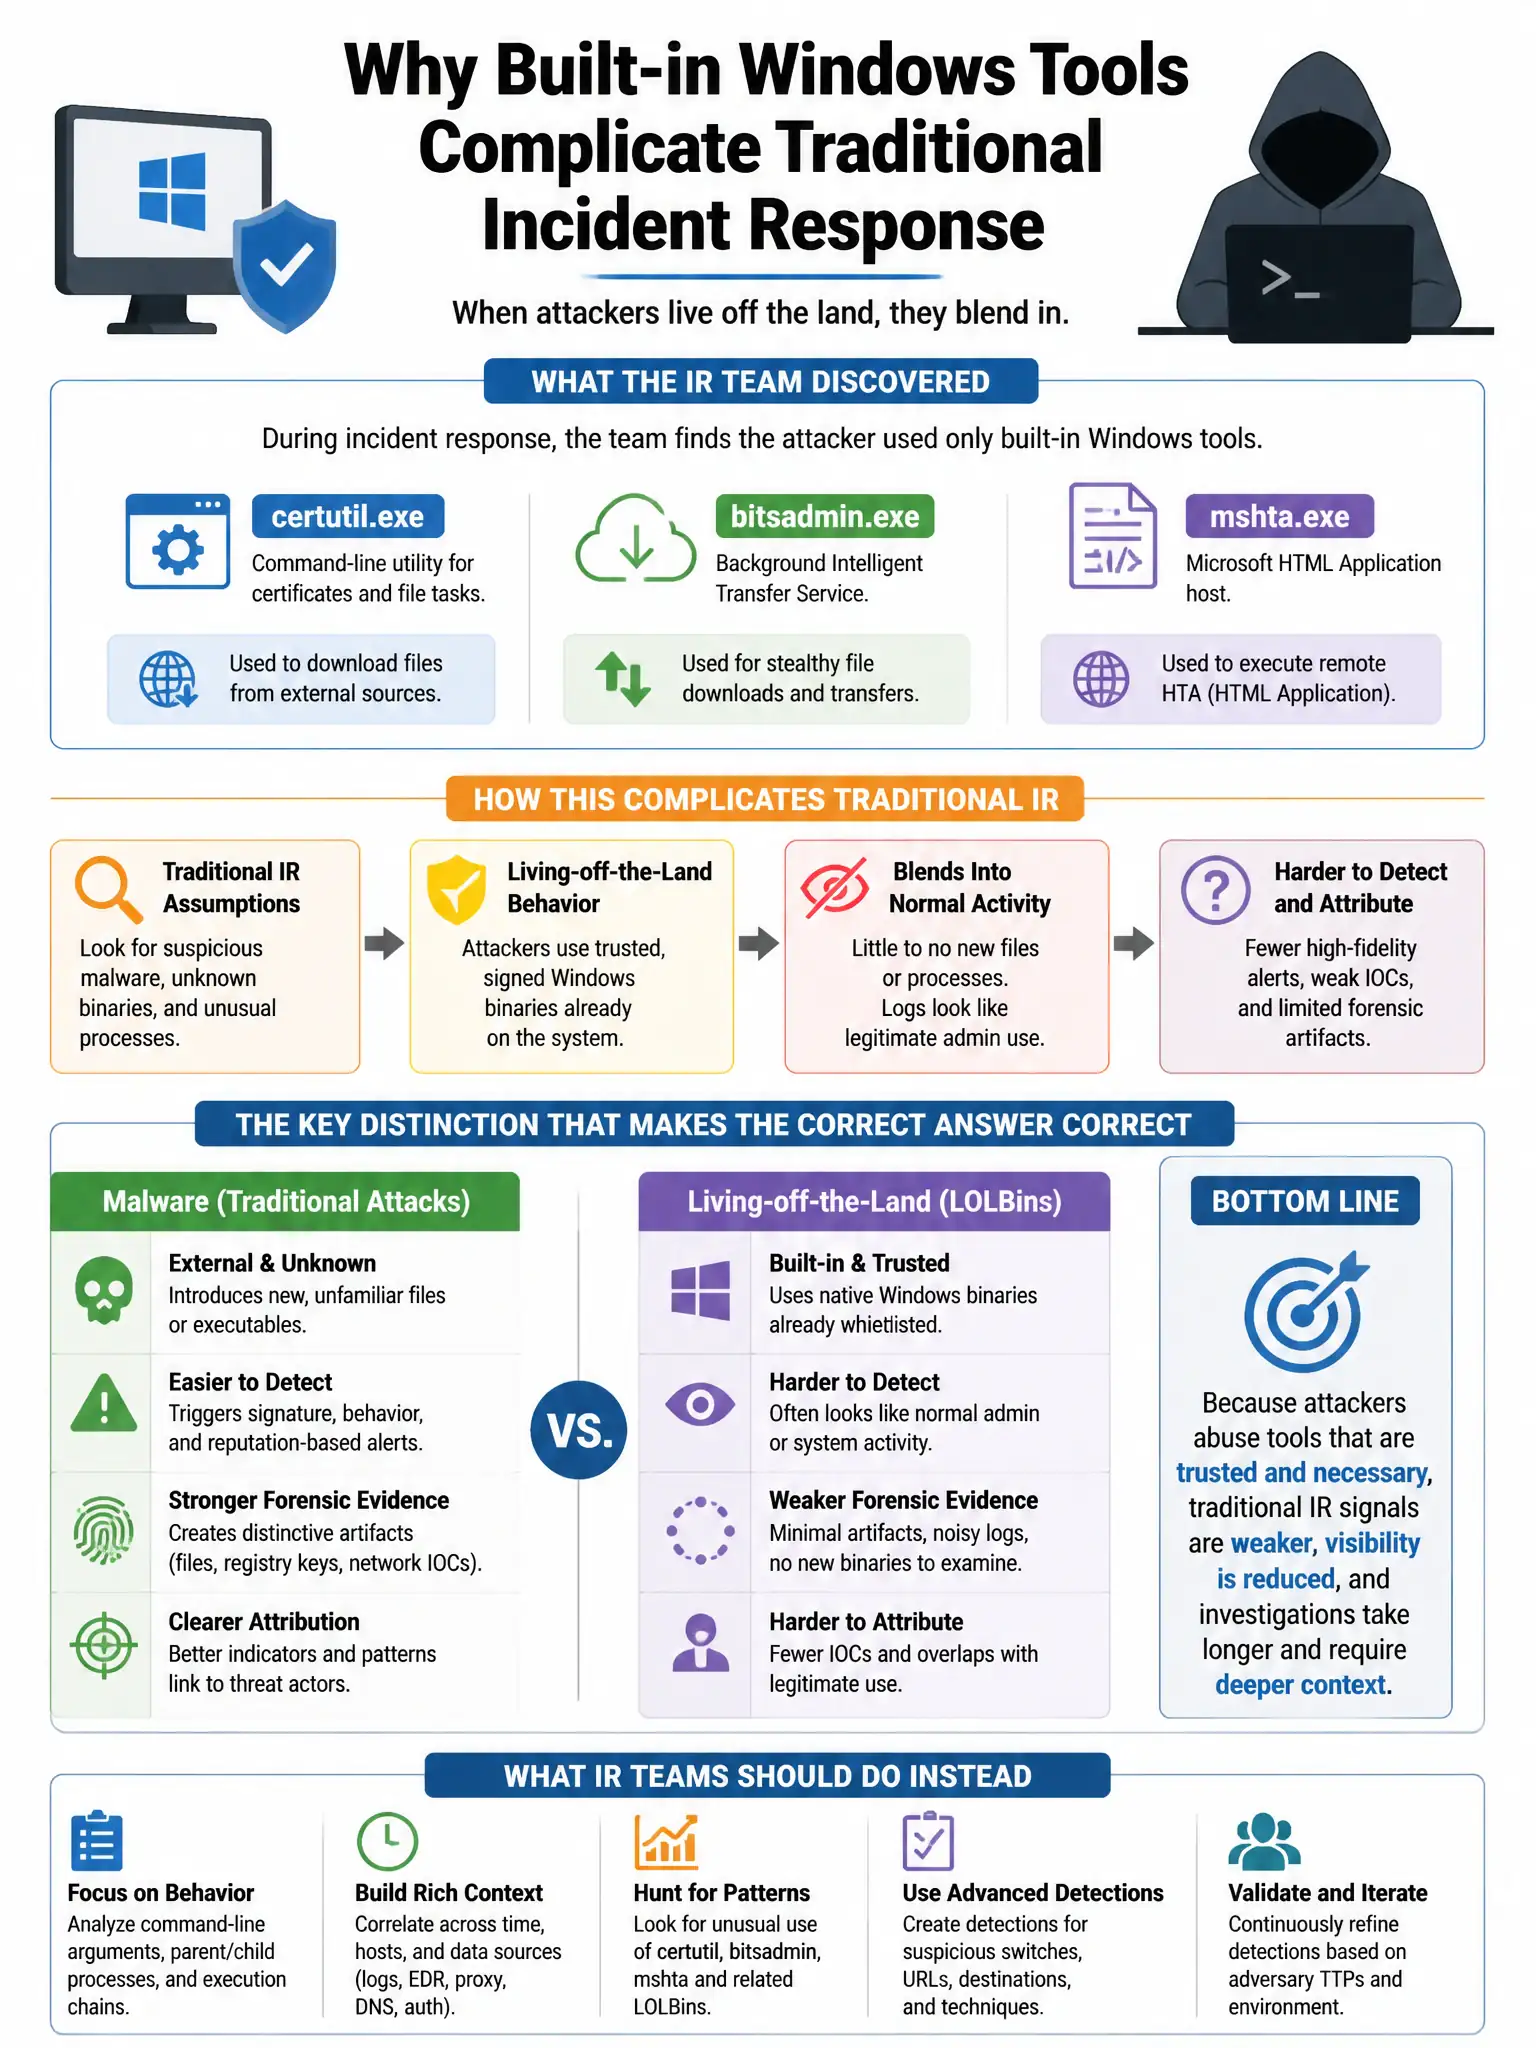
During incident response, the team discovers the attacker used only built-in Windows tools including certutil, bitsadmin, and mshta. Why does this complicate traditional IR approaches?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — living-off-the-land attacks use legitimate system tools, bypassing antivirus and signature-based IDS. Detection requires behavioral baselines, command-line argument logging via Sysmon, and SIEM correlation of anomalous tool usage.
Full Explanation
Living-off-the-land techniques evade signature-based detection because the tools are legitimate; detection requires behavioral analysis and contextual log review. LOLBAS attacks use legitimate system tools, bypassing antivirus and signature-based IDS. Detection requires behavioral baselines, command-line argument logging via Sysmon, and SIEM correlation of anomalous tool usage. The encrypted-tools claim is wrong because they are standard executables, not encrypted. The no-logs claim is wrong because Windows provides extensive logging, including event identifiers, PowerShell logging, and Sysmon, that capture their usage. The Windows XP-only claim is wrong because LOLBAS techniques are effective on all modern Windows versions.