
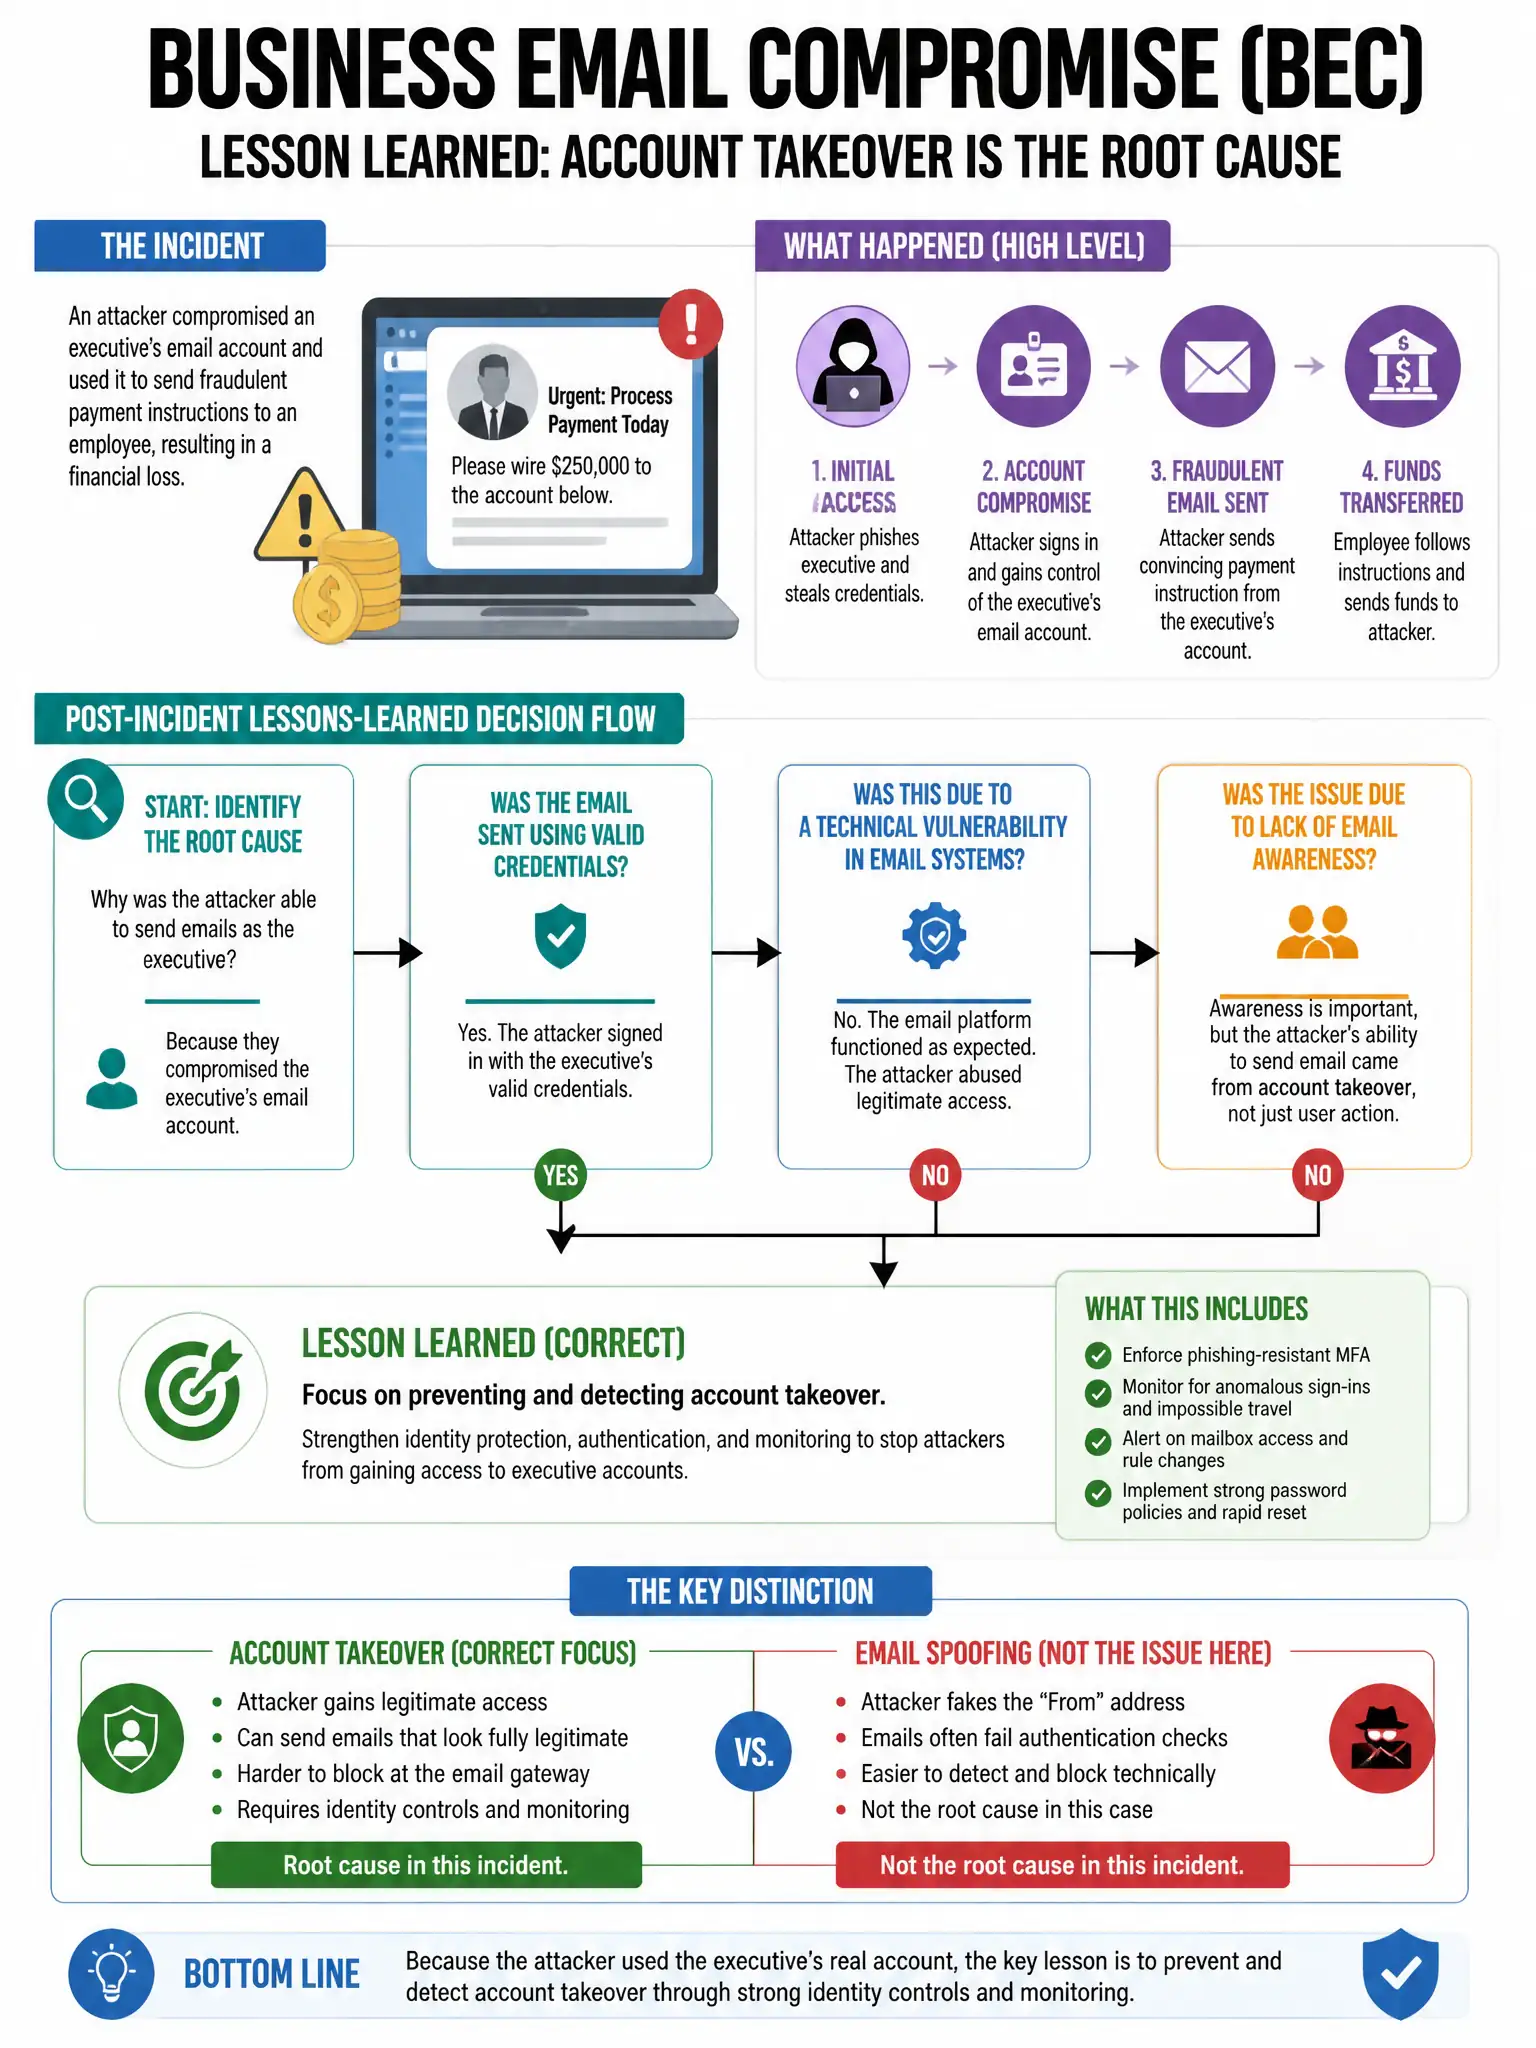
An IR team is responding to a business email compromise where an attacker used a compromised executive's email account. During post-incident activity, which lesson-learned item is MOST valuable?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — when you're doing post-incident work, the most valuable lesson is figuring out why phishing controls and MFA failed, then putting technical controls in place so it doesn't happen again. Blacklisting an IP, insurance math, or telling staff to report faster don't fix the control gap.
Full Explanation
The most valuable lesson-learned item is identifying why phishing controls and MFA failed and implementing technical controls to prevent recurrence, because post-incident activity should focus on root-cause failures in preventive controls — why phishing bypassed email filters and why MFA was not enforced — and then making concrete technical improvements. Documenting the attacker's source IP address for future blacklisting is wrong because IP blacklisting provides minimal future value as attackers change infrastructure frequently. Calculating the financial impact accurately for the cyber insurance claim only is wrong because financial impact documentation is important but not the most valuable security lesson learned. Informing all employees they should report suspicious emails more promptly is wrong because awareness training alone without technical controls is insufficient to prevent recurrence.