
During the identification phase of the PICERL incident response cycle, a security analyst receives an alert for unusual login activity. What is the PRIMARY objective of this phase?
Select an answer to reveal the explanation.
Short Explanation
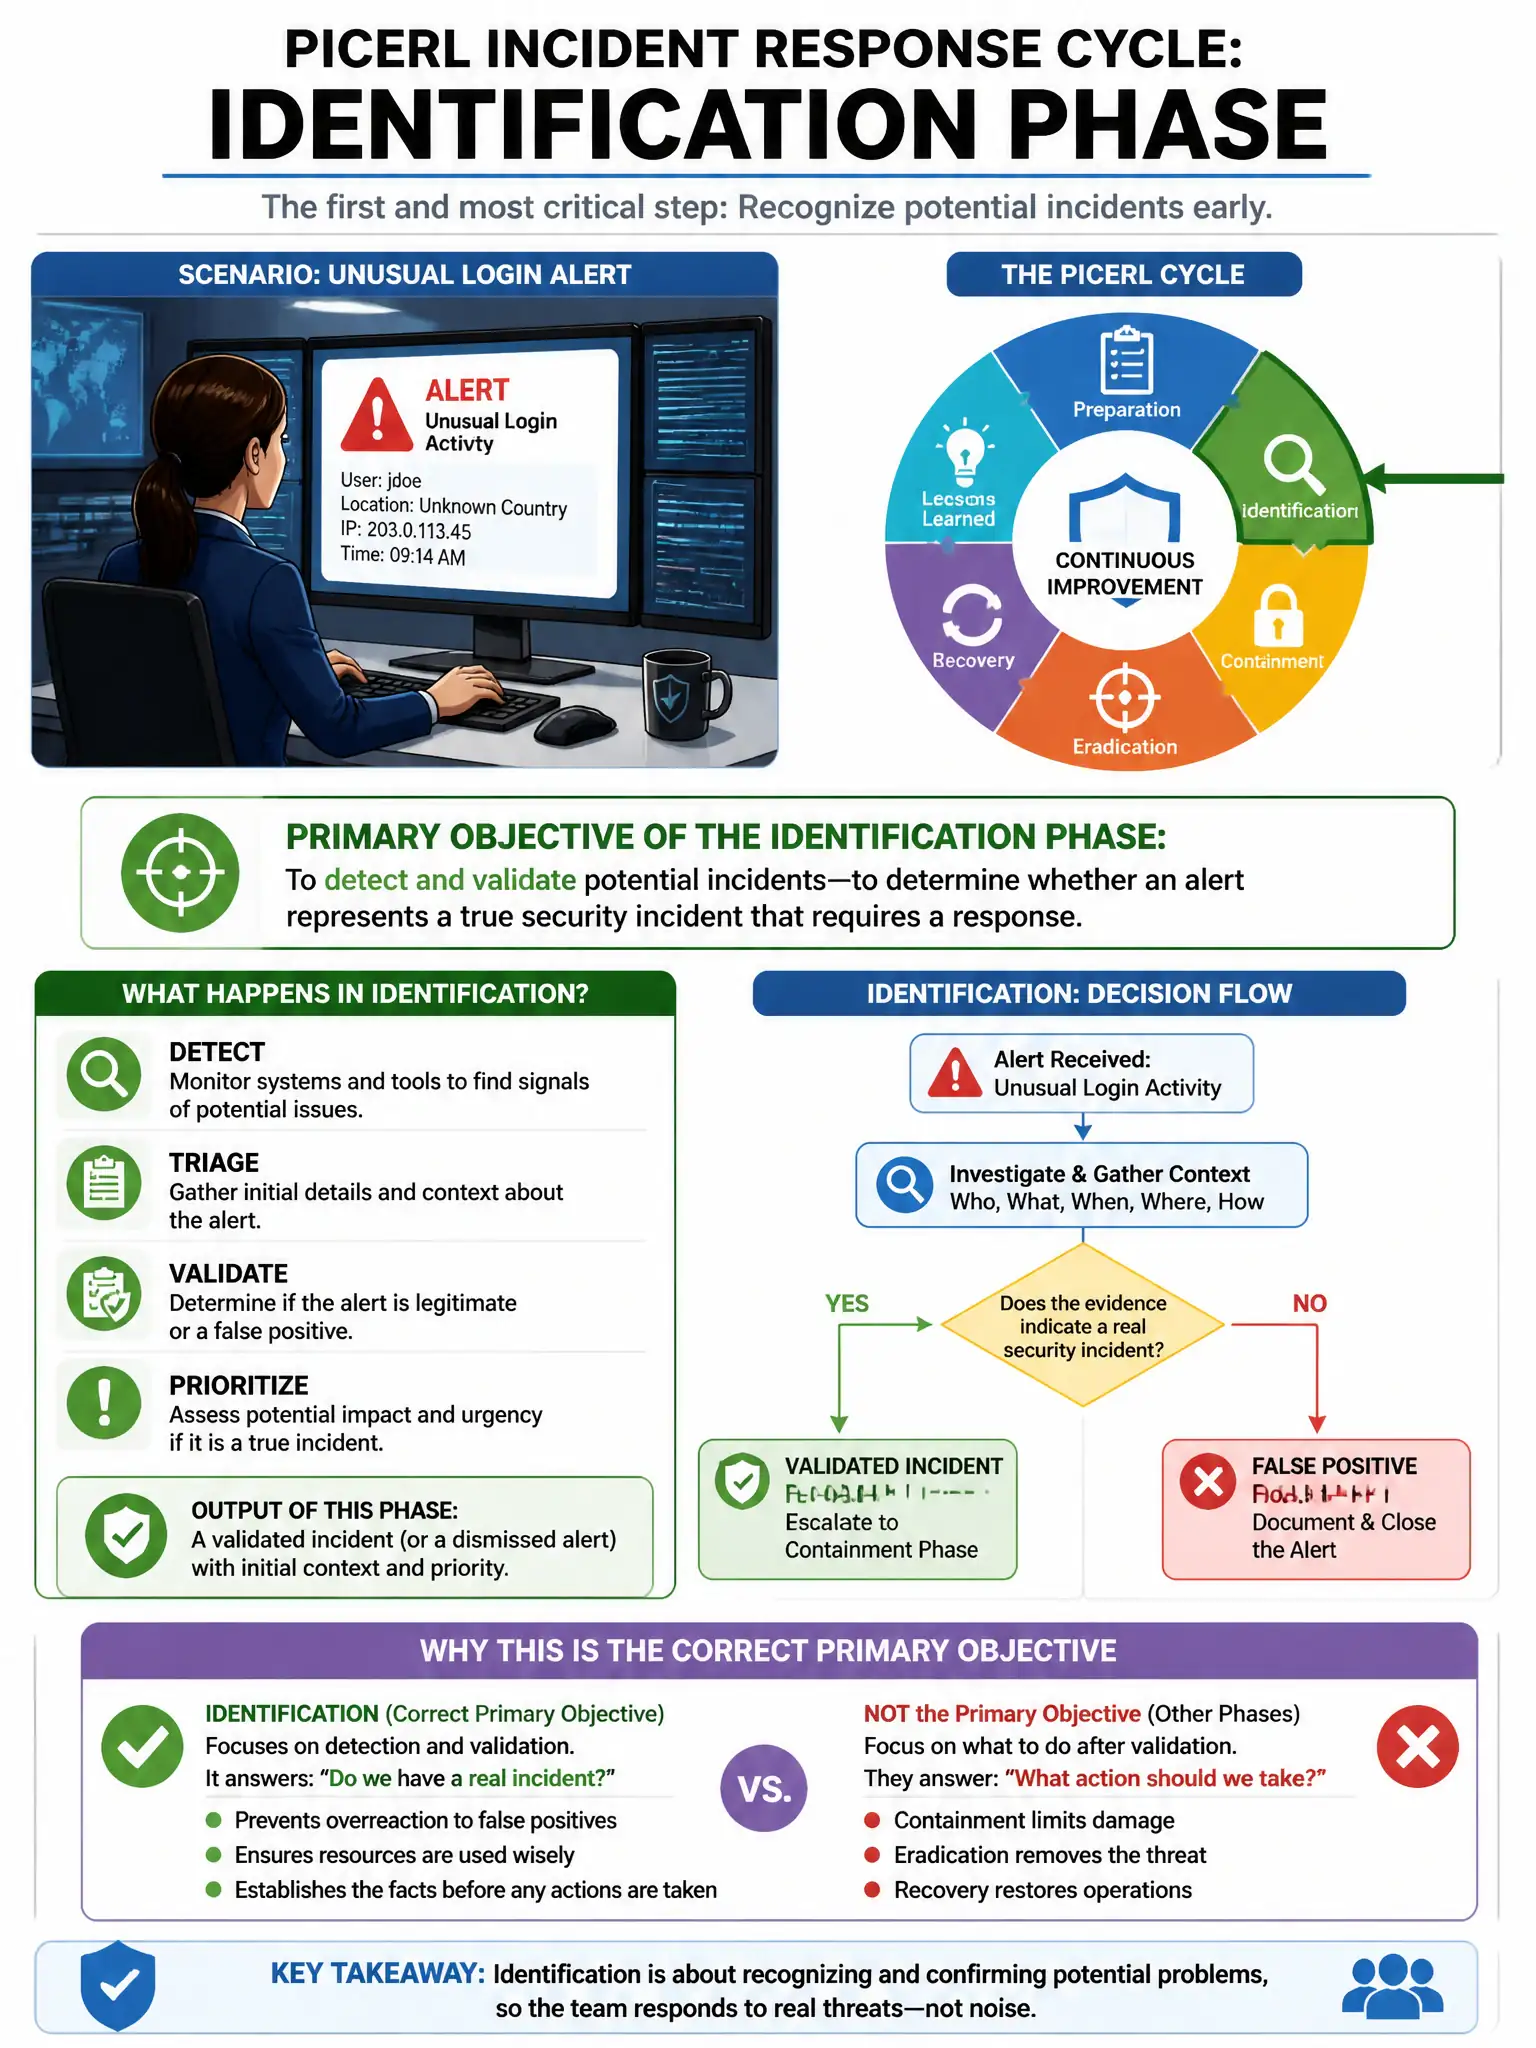
Here's the deal — you're in Identification, so your job is to confirm whether the unusual logins are a real incident and pin down the initial scope. That's what tells you whether to escalate into containment and the rest of the incident response cycle.
Full Explanation
The correct objective is to determine whether the activity constitutes a confirmed security incident and characterize its scope, because Identification confirms whether an event is a true incident, characterizes its nature, and determines initial scope. This analysis drives escalation. The option about removing malicious files and restoring systems is wrong because that occurs in Eradication and Recovery. The option about isolating affected systems immediately is wrong because isolation is Containment. The option about documenting lessons learned and updating procedures is wrong because that is Post-Incident Activity.