
A SOC receives an alert that an internal host is communicating with a known malicious IP. The firewall is blocking the traffic. Which ADDITIONAL action should the SOC take?
Select an answer to reveal the explanation.
Short Explanation
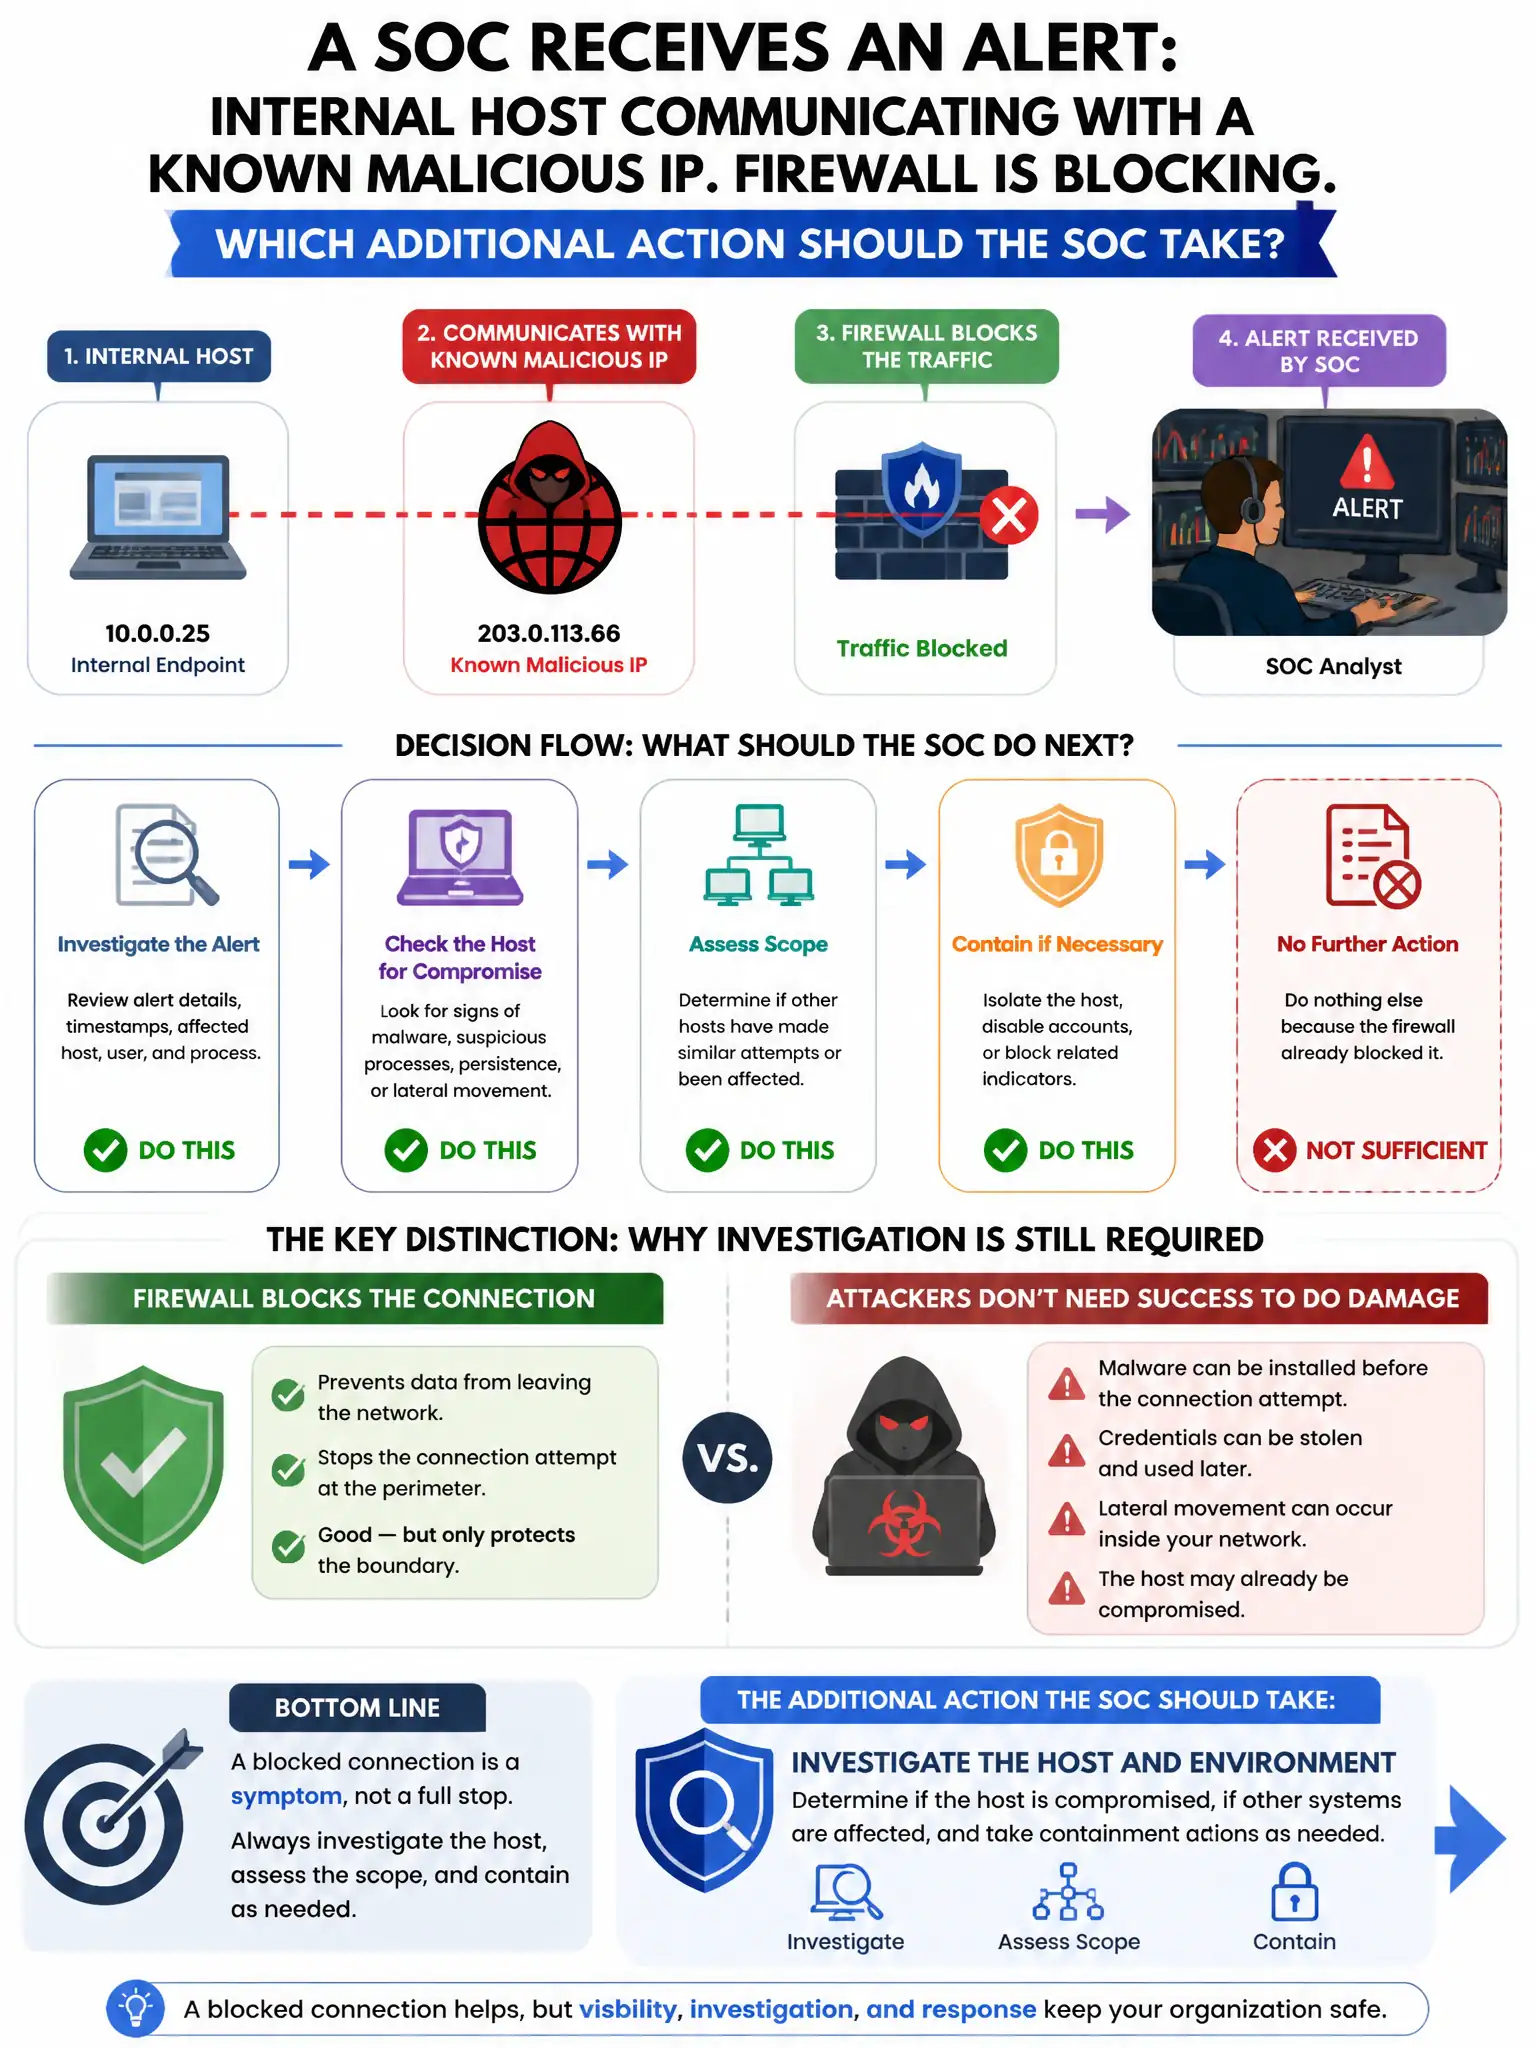
Here's the deal — you should investigate the source host because a host trying to reach a known malicious IP likely means it's compromised, even if the firewall blocked the traffic. Check for malware, persistence mechanisms, and other indicators of compromise.
Full Explanation
Investigate the source host to determine how it attempted to contact the malicious IP, identify any malware, and check for other indicators of compromise. The host attempting to communicate with a known malicious IP indicates likely compromise even if the firewall blocked the connection, so investigate for malware, persistence, and lateral movement. Saying no further action is needed is wrong because the block does not address the underlying compromise. Blocking the destination IP at DNS only and closing the ticket is wrong because DNS blocking alone is insufficient and ignores the compromised host. Archiving the alert for quarterly review is wrong because deferring investigation lets the attacker maintain persistence and cause further damage.