
A ransomware attack has encrypted files on 15 servers. The IR team needs to contain the incident. Which containment action should be performed FIRST?
Select an answer to reveal the explanation.
Short Explanation
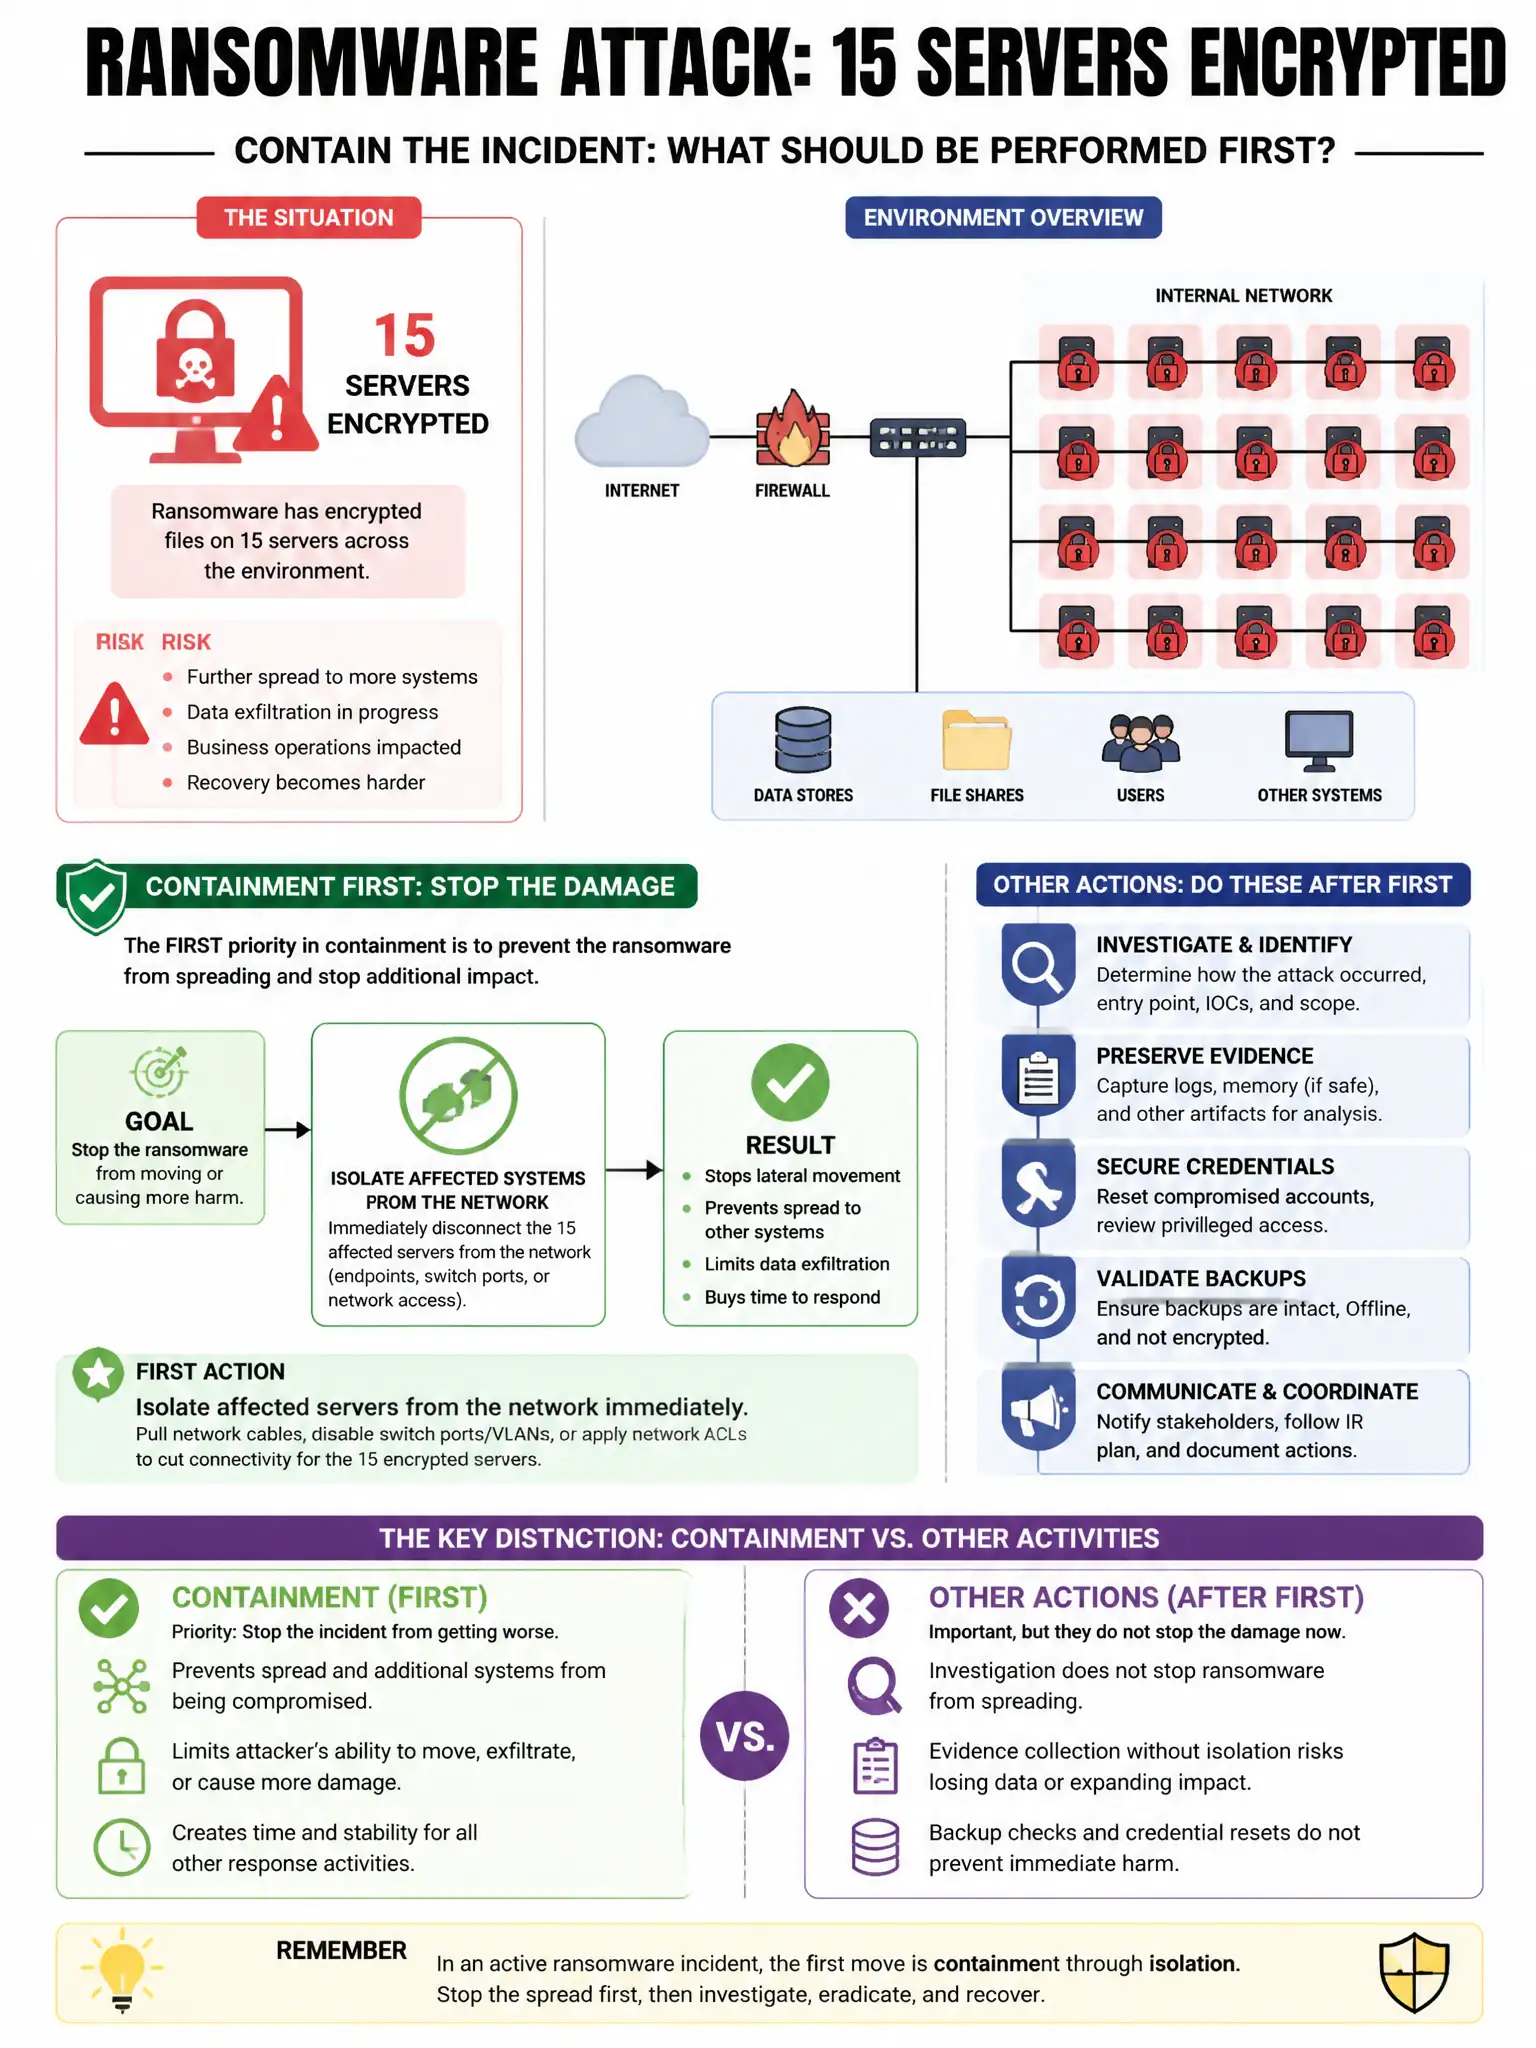
You want to isolate the affected systems from the network first. That stops ransomware from spreading while you preserve volatile evidence, like encryption keys that may still be in memory. Don't hard-shutdown the servers, because that can destroy that evidence.
Full Explanation
Isolating affected systems from the network while preserving volatile evidence by avoiding hard shutdowns is correct. Network isolation stops ransomware from spreading to additional systems, and volatile memory may still hold encryption keys; hard shutdowns can destroy that evidence. Wiping all 15 servers and reinstalling from clean media is wrong because it destroys forensic evidence needed to understand the full attack scope. Paying the ransom is wrong because it funds criminal activity and does not guarantee decryption or address the root cause. Running full antivirus scans before isolation is wrong because it allows continued spread during scanning.