
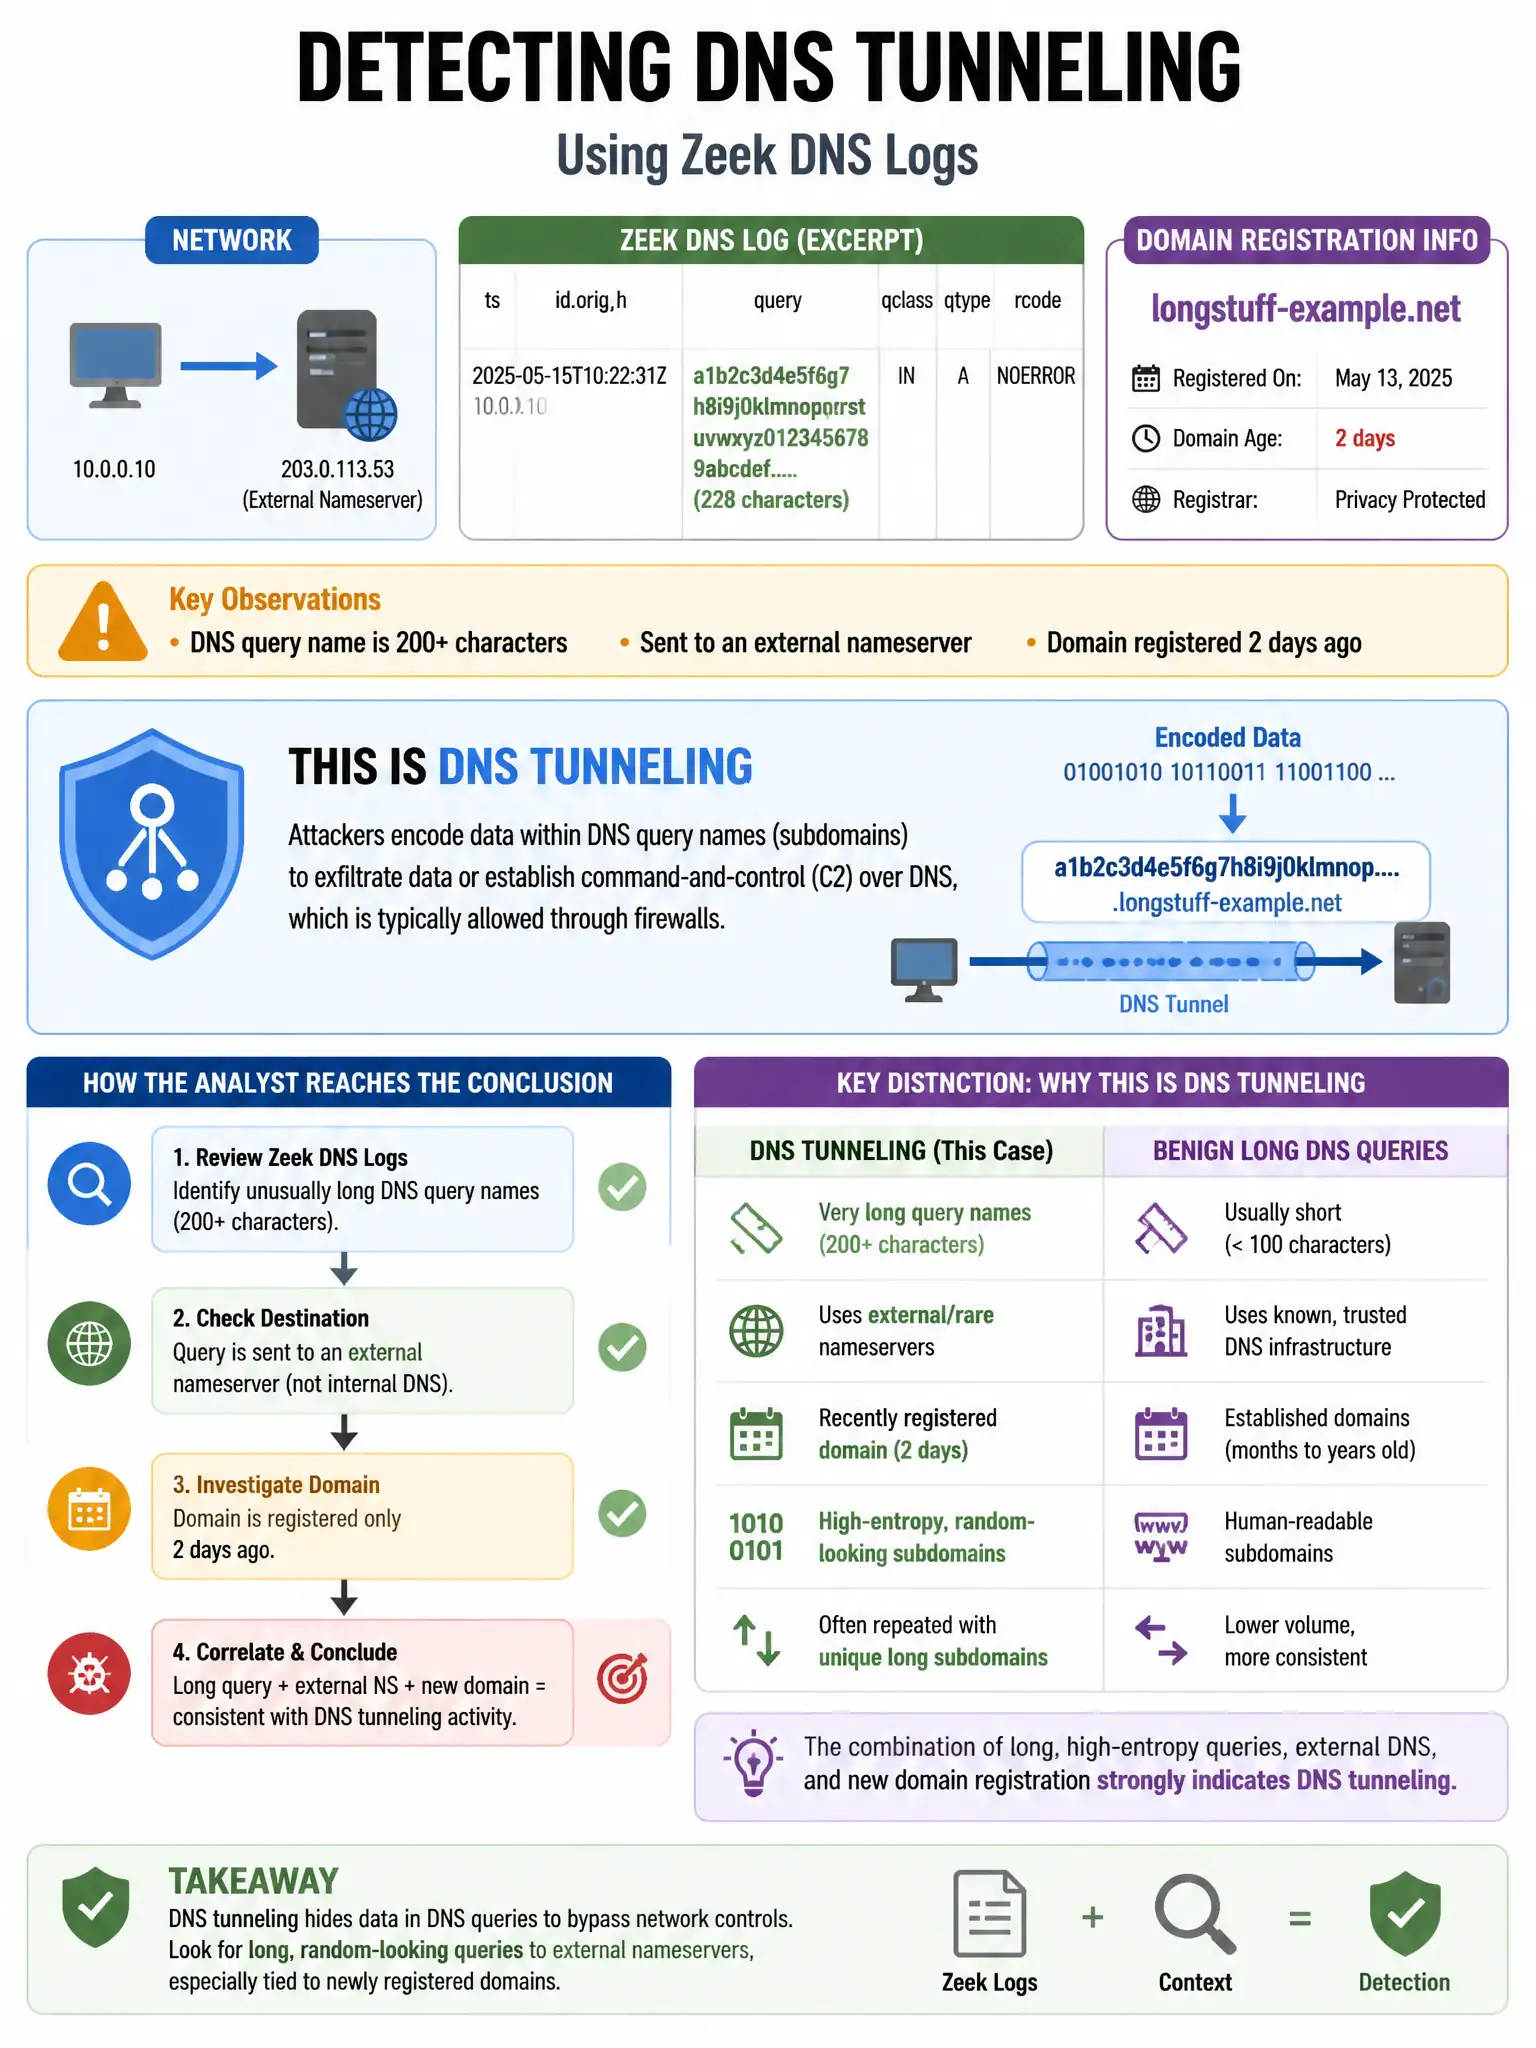
An analyst reviewing Zeek DNS logs finds unusually long DNS query names (200+ characters) being sent to an external nameserver for a domain registered two days ago. What technique does this MOST likely indicate?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — DNS tunneling is what you'd expect here because it encodes data in subdomain labels, making query names abnormally long. Newly registered domains are classic signs of throwaway attacker infrastructure.
Full Explanation
DNS tunneling used to exfiltrate data or communicate with a C2 server is correct because DNS tunneling encodes data in the subdomain portion of DNS queries, resulting in abnormally long query strings. Newly registered domains are a common indicator of attacker infrastructure. DNS load balancing across multiple geographically distributed servers is wrong because DNS load balancing uses normal-length queries to known established DNS servers. DNS over HTTPS (DoH) traffic being misidentified as standard DNS queries is wrong because DoH traffic appears as HTTPS on port 443, not as DNS queries. Misconfigured split-horizon DNS configuration causing query loops is wrong because split-horizon DNS involves returning different responses to different clients, not abnormally long queries.