
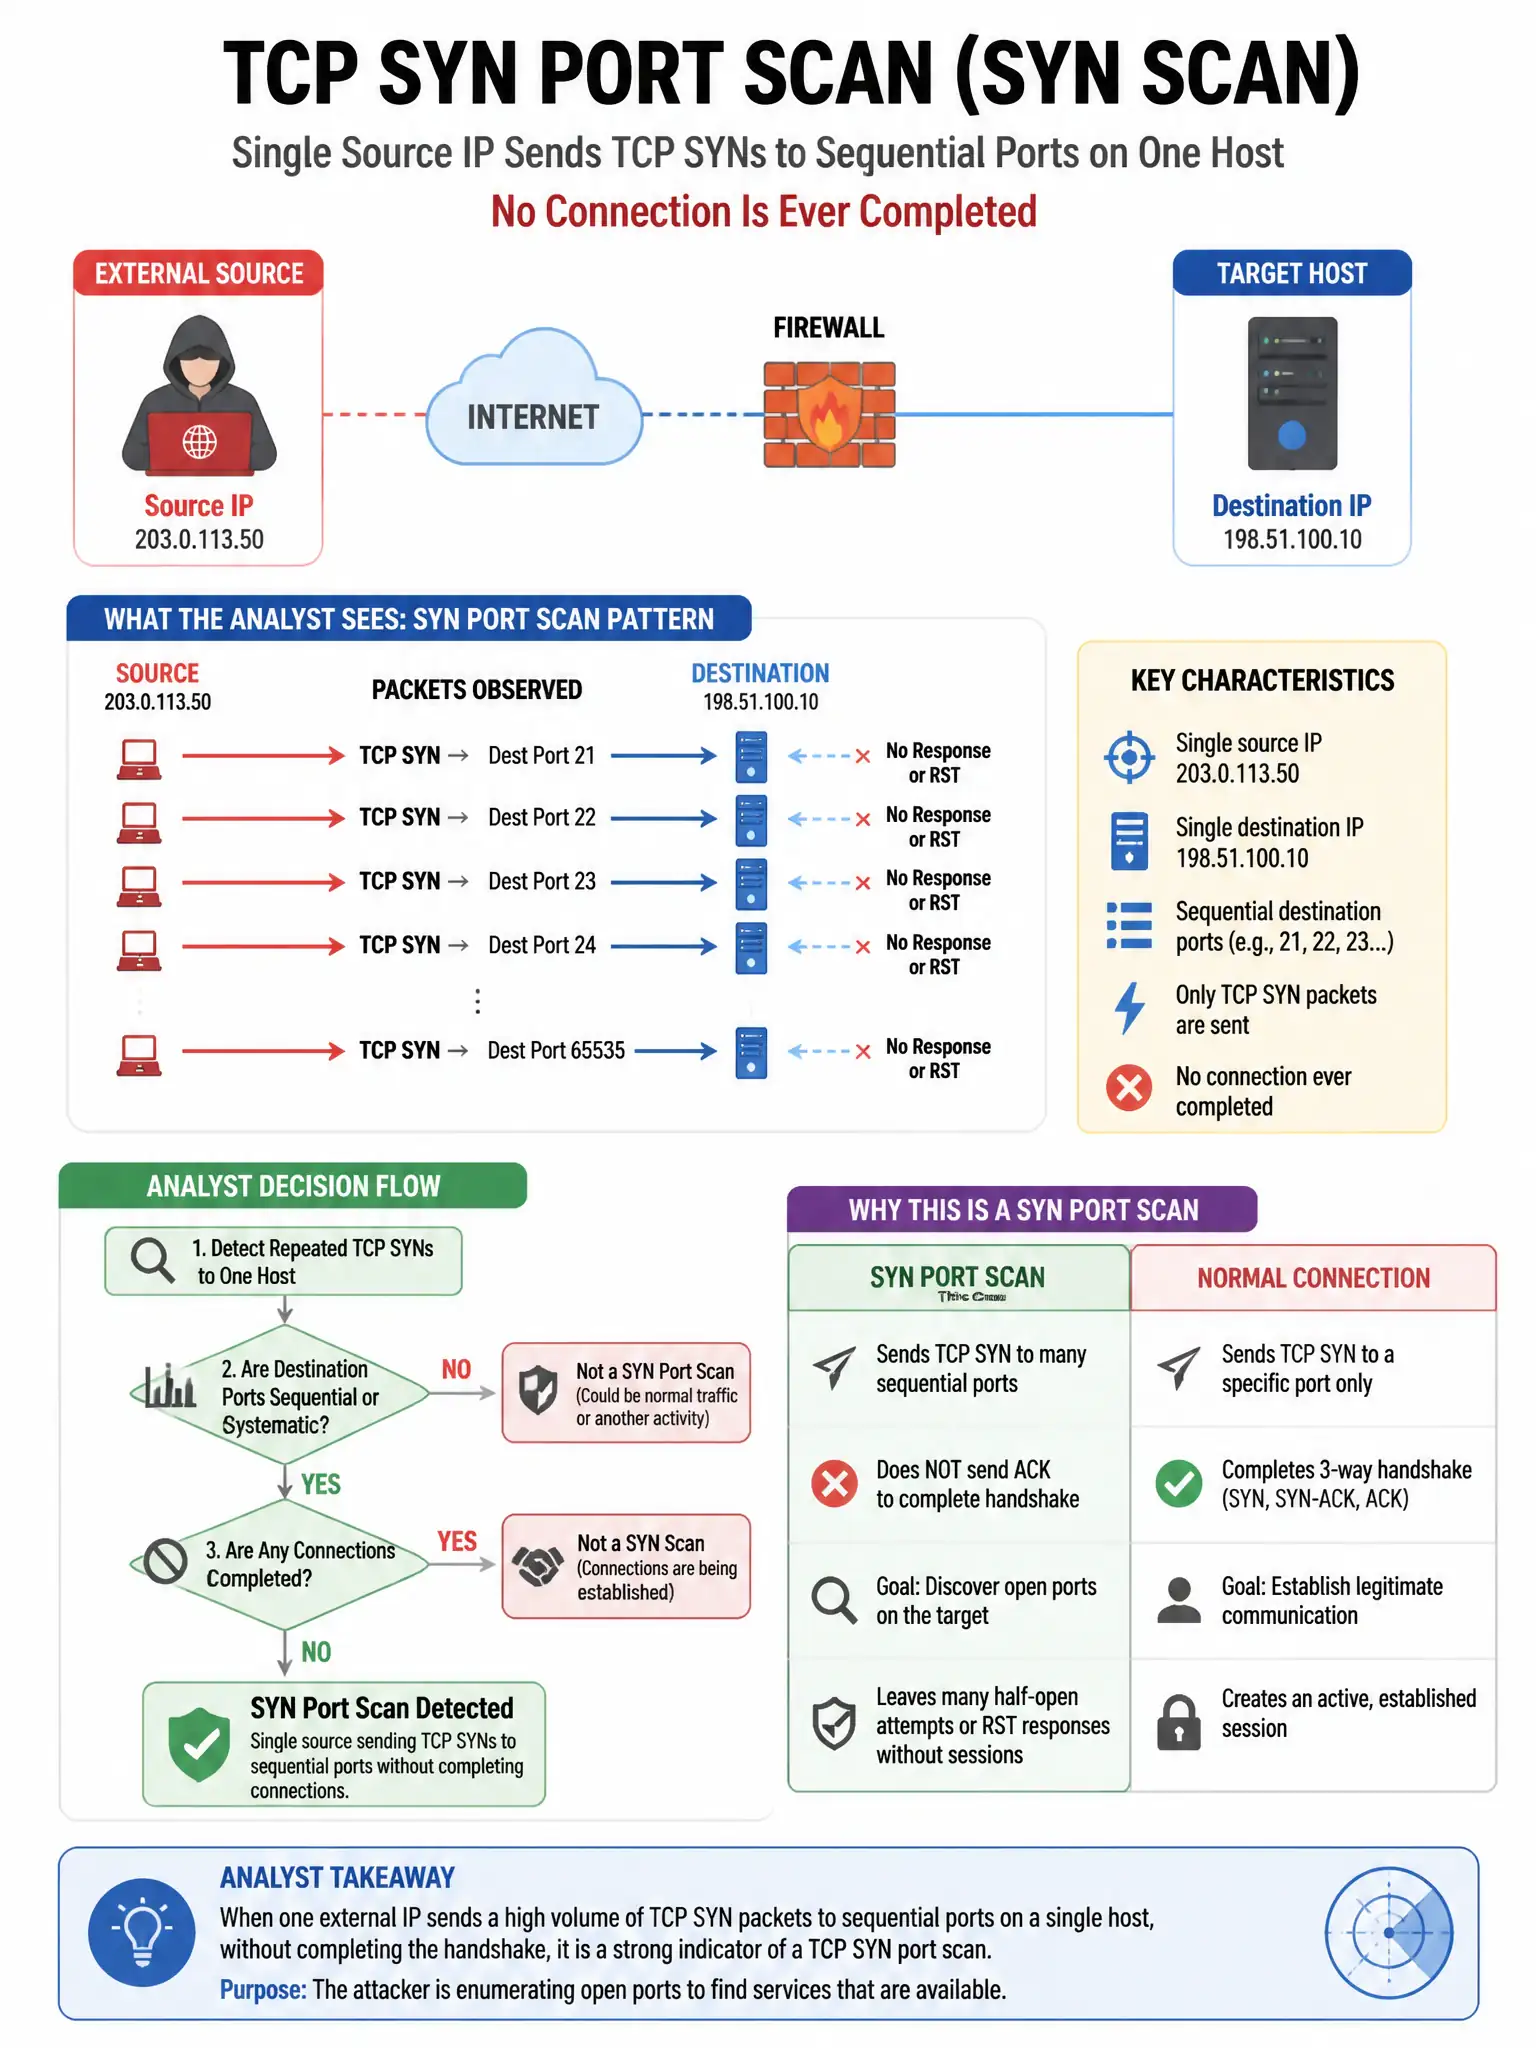
A network security analyst identifies a scan pattern where a single external source IP sends TCP SYN packets to sequential destination ports on a single host without ever completing the three-way handshake. What type of scan is this?
Select an answer to reveal the explanation.
Short Explanation
You're seeing a TCP SYN (stealth) scan because the source sends SYN packets to sequential ports and never completes the three-way handshake. You can tell it's stealthy because it only checks responses like SYN-ACK for open ports and RST for closed ports, so it's faster and less likely to be logged by older systems.
Full Explanation
The correct answer is the TCP SYN (stealth) scan because it sends SYN packets to sequential destination ports on a single host and analyzes responses — SYN-ACK for open ports, RST for closed — without completing the three-way handshake, making it faster and less likely to be logged by older systems. The TCP connect scan is wrong because it completes the full three-way handshake on each port. The UDP scan is wrong because UDP scans send UDP datagrams, not TCP SYNs. The XMAS scan is wrong because an XMAS scan sets FIN, PSH, and URG flags simultaneously, not just SYN.