
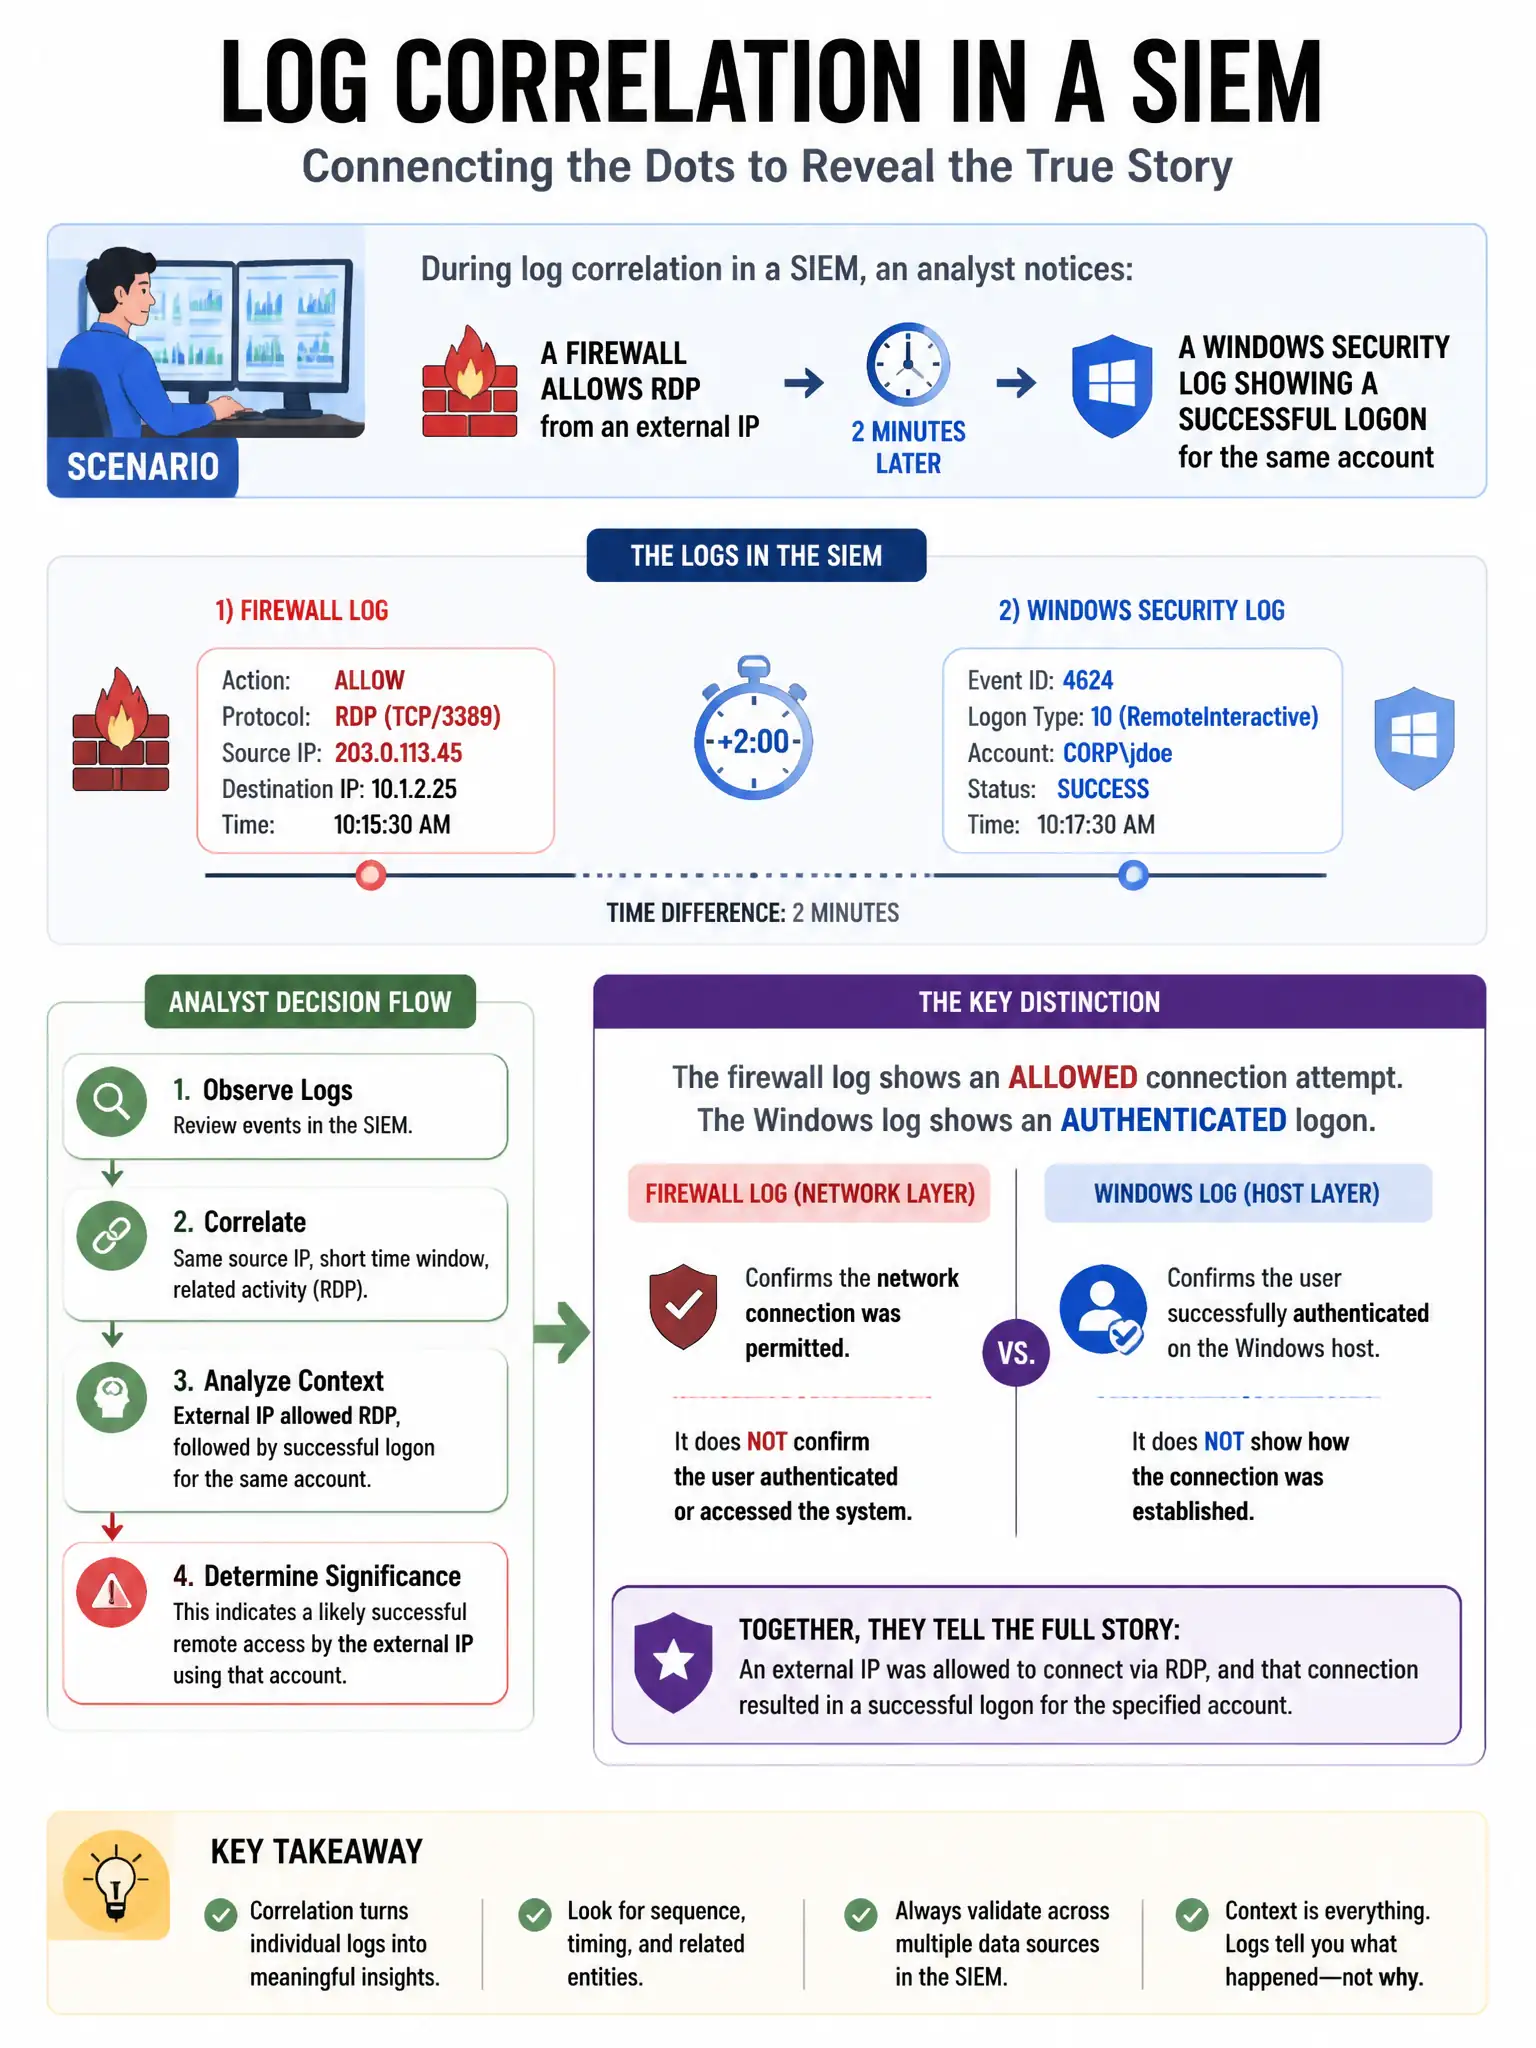
During log correlation in a SIEM, an analyst notices: a firewall allows RDP from an external IP, followed 2 minutes later by a Windows Security log showing a successful logon for a service account, followed by execution of PowerShell with encoded commands. What attack phases does this sequence represent?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you're seeing initial access through external RDP, credential use when the service account logs on, and execution when encoded PowerShell runs. That maps directly to initial access, credential use, and execution.
Full Explanation
The sequence shows initial access via external RDP, use of a service account credential to authenticate, and then execution of obfuscated PowerShell — mapping to initial access, credential use, and execution phases. Reconnaissance and scanning is wrong because scanning would appear before successful authentication and does not include execution. Exfiltration and impact is wrong because exfiltration and impact occur later in the attack chain. Defense evasion and persistence only is wrong because PowerShell encoding is defense evasion but the sequence also clearly shows initial access and execution phases.