
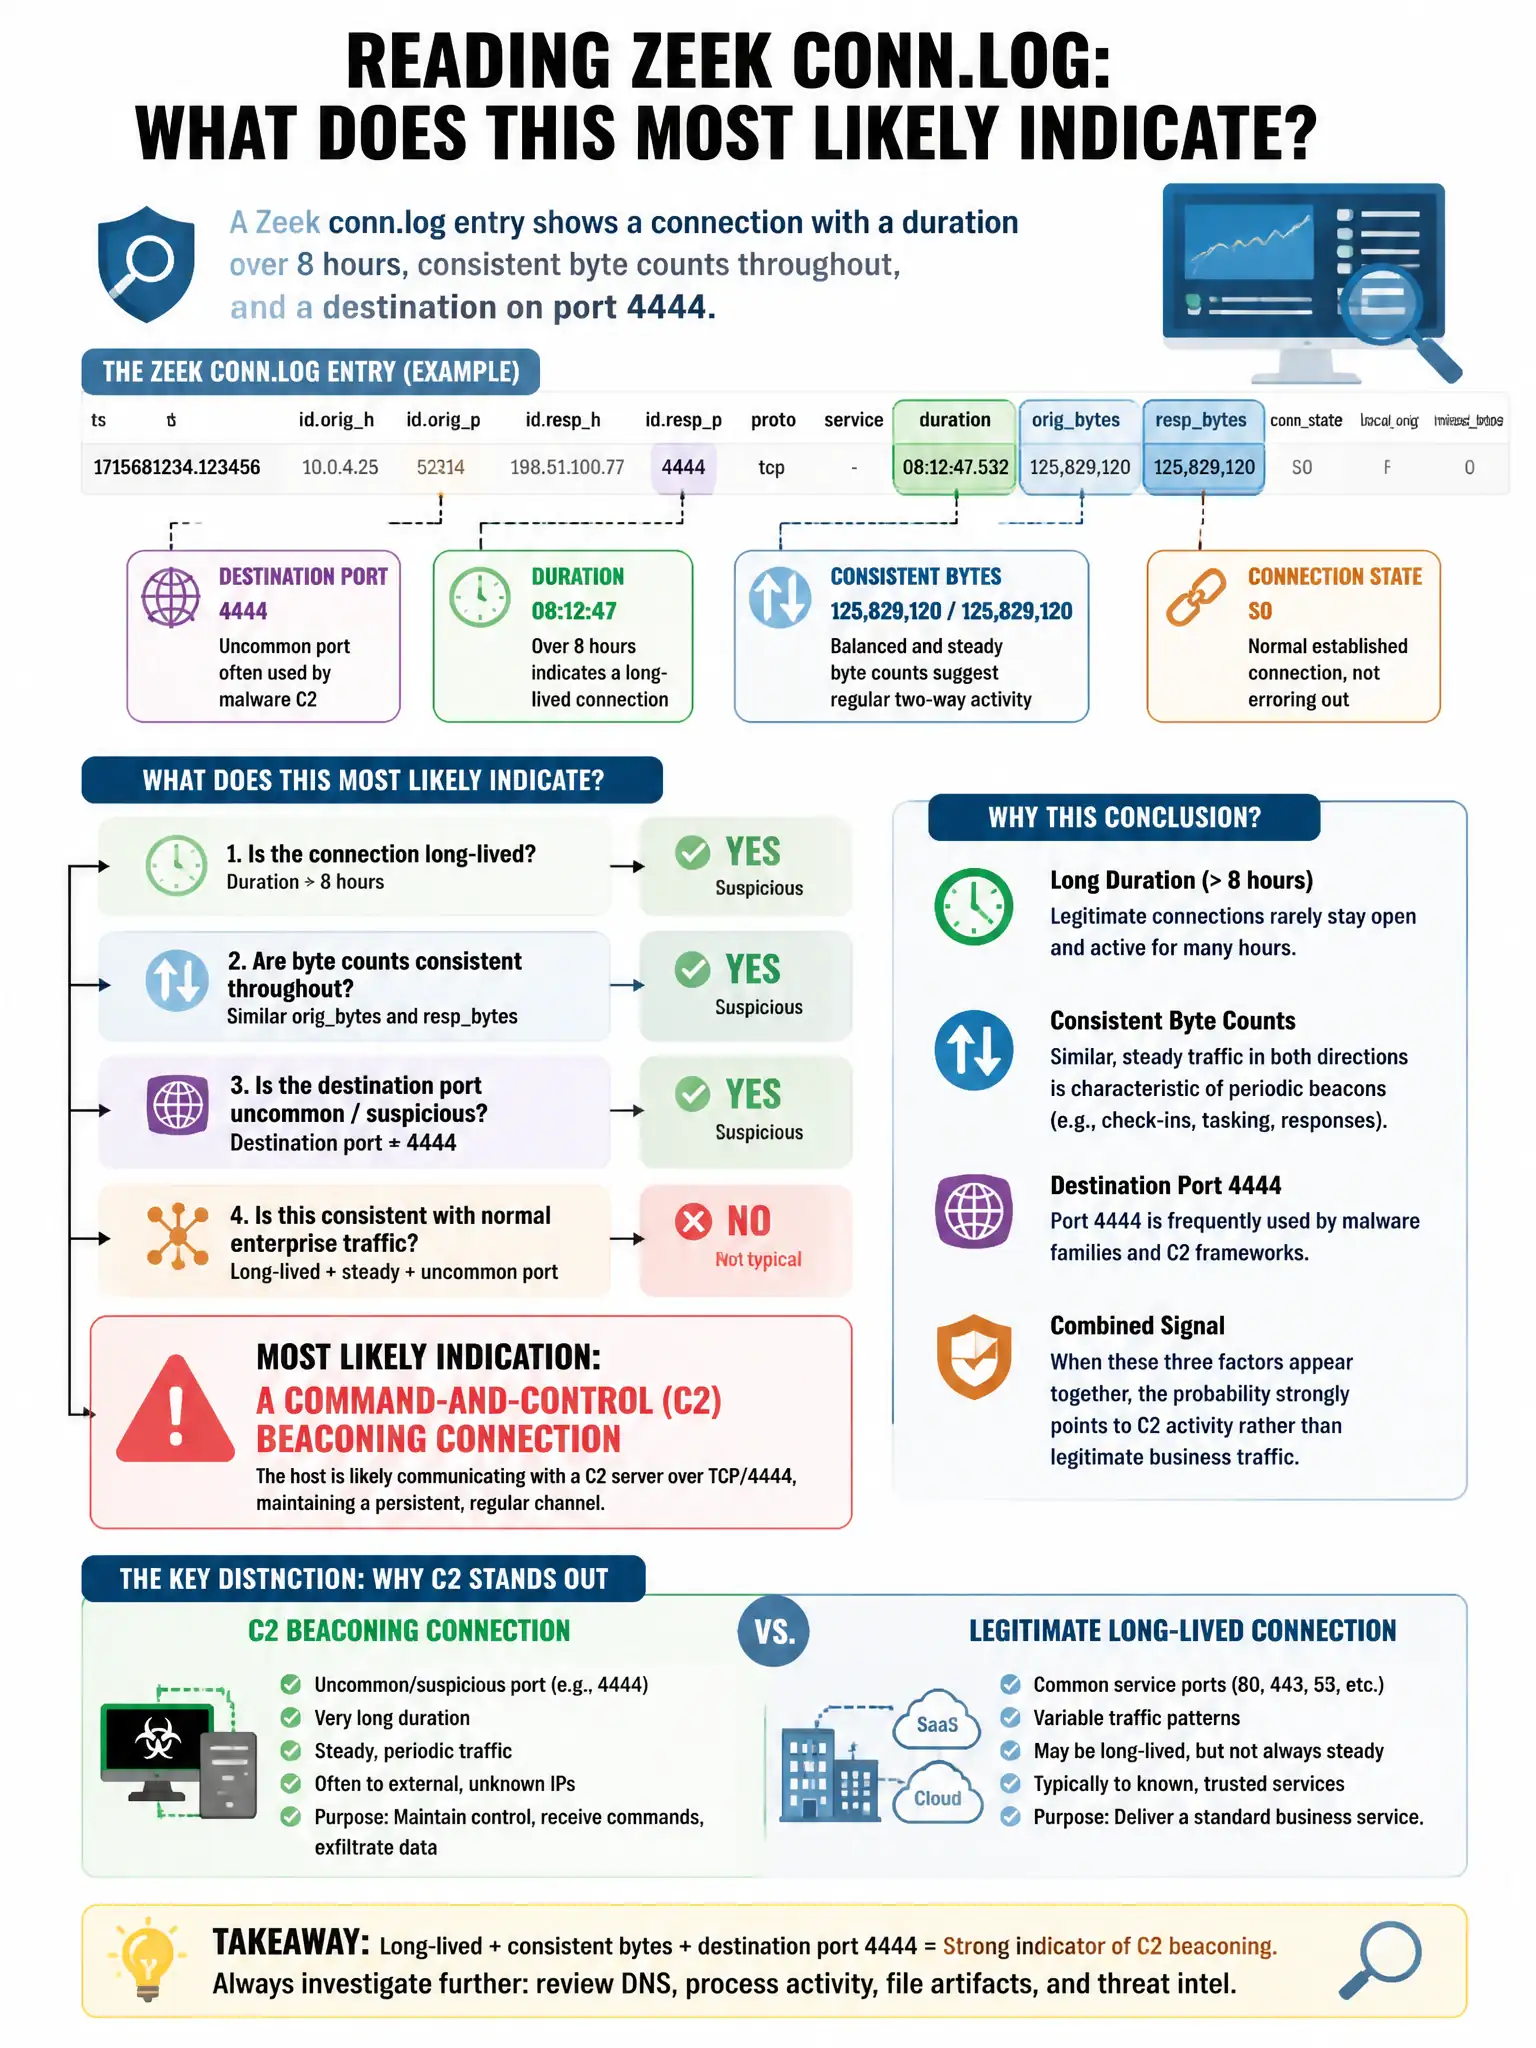
A Zeek conn.log entry shows a connection with a duration over 8 hours, consistent byte counts throughout, and a destination on port 4444. What does this MOST likely indicate?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you're looking at a long-lived reverse shell or C2 persistent connection because an 8-hour connection on port 4444 with steady byte counts is classic for a backdoor keeping a control channel open. Port 4444 is commonly tied to Metasploit reverse shells.
Full Explanation
The long-lived reverse shell or C2 persistent connection fits best because an 8-hour connection on port 4444 with steady byte counts is classic for a backdoor maintaining a control channel, and port 4444 is commonly tied to Metasploit reverse shells. Legitimate large file transfer to a backup server over a non-standard port is unlikely because transfers have a defined beginning and end, not an 8-hour steady pattern. Misconfigured network printer sending repeated status updates is unlikely because printers use well-known protocols on standard ports. Distributed denial-of-service attack in progress targeting the remote IP is unlikely because DDoS involves high-volume traffic from many sources, not one long-lived low-throughput connection.