
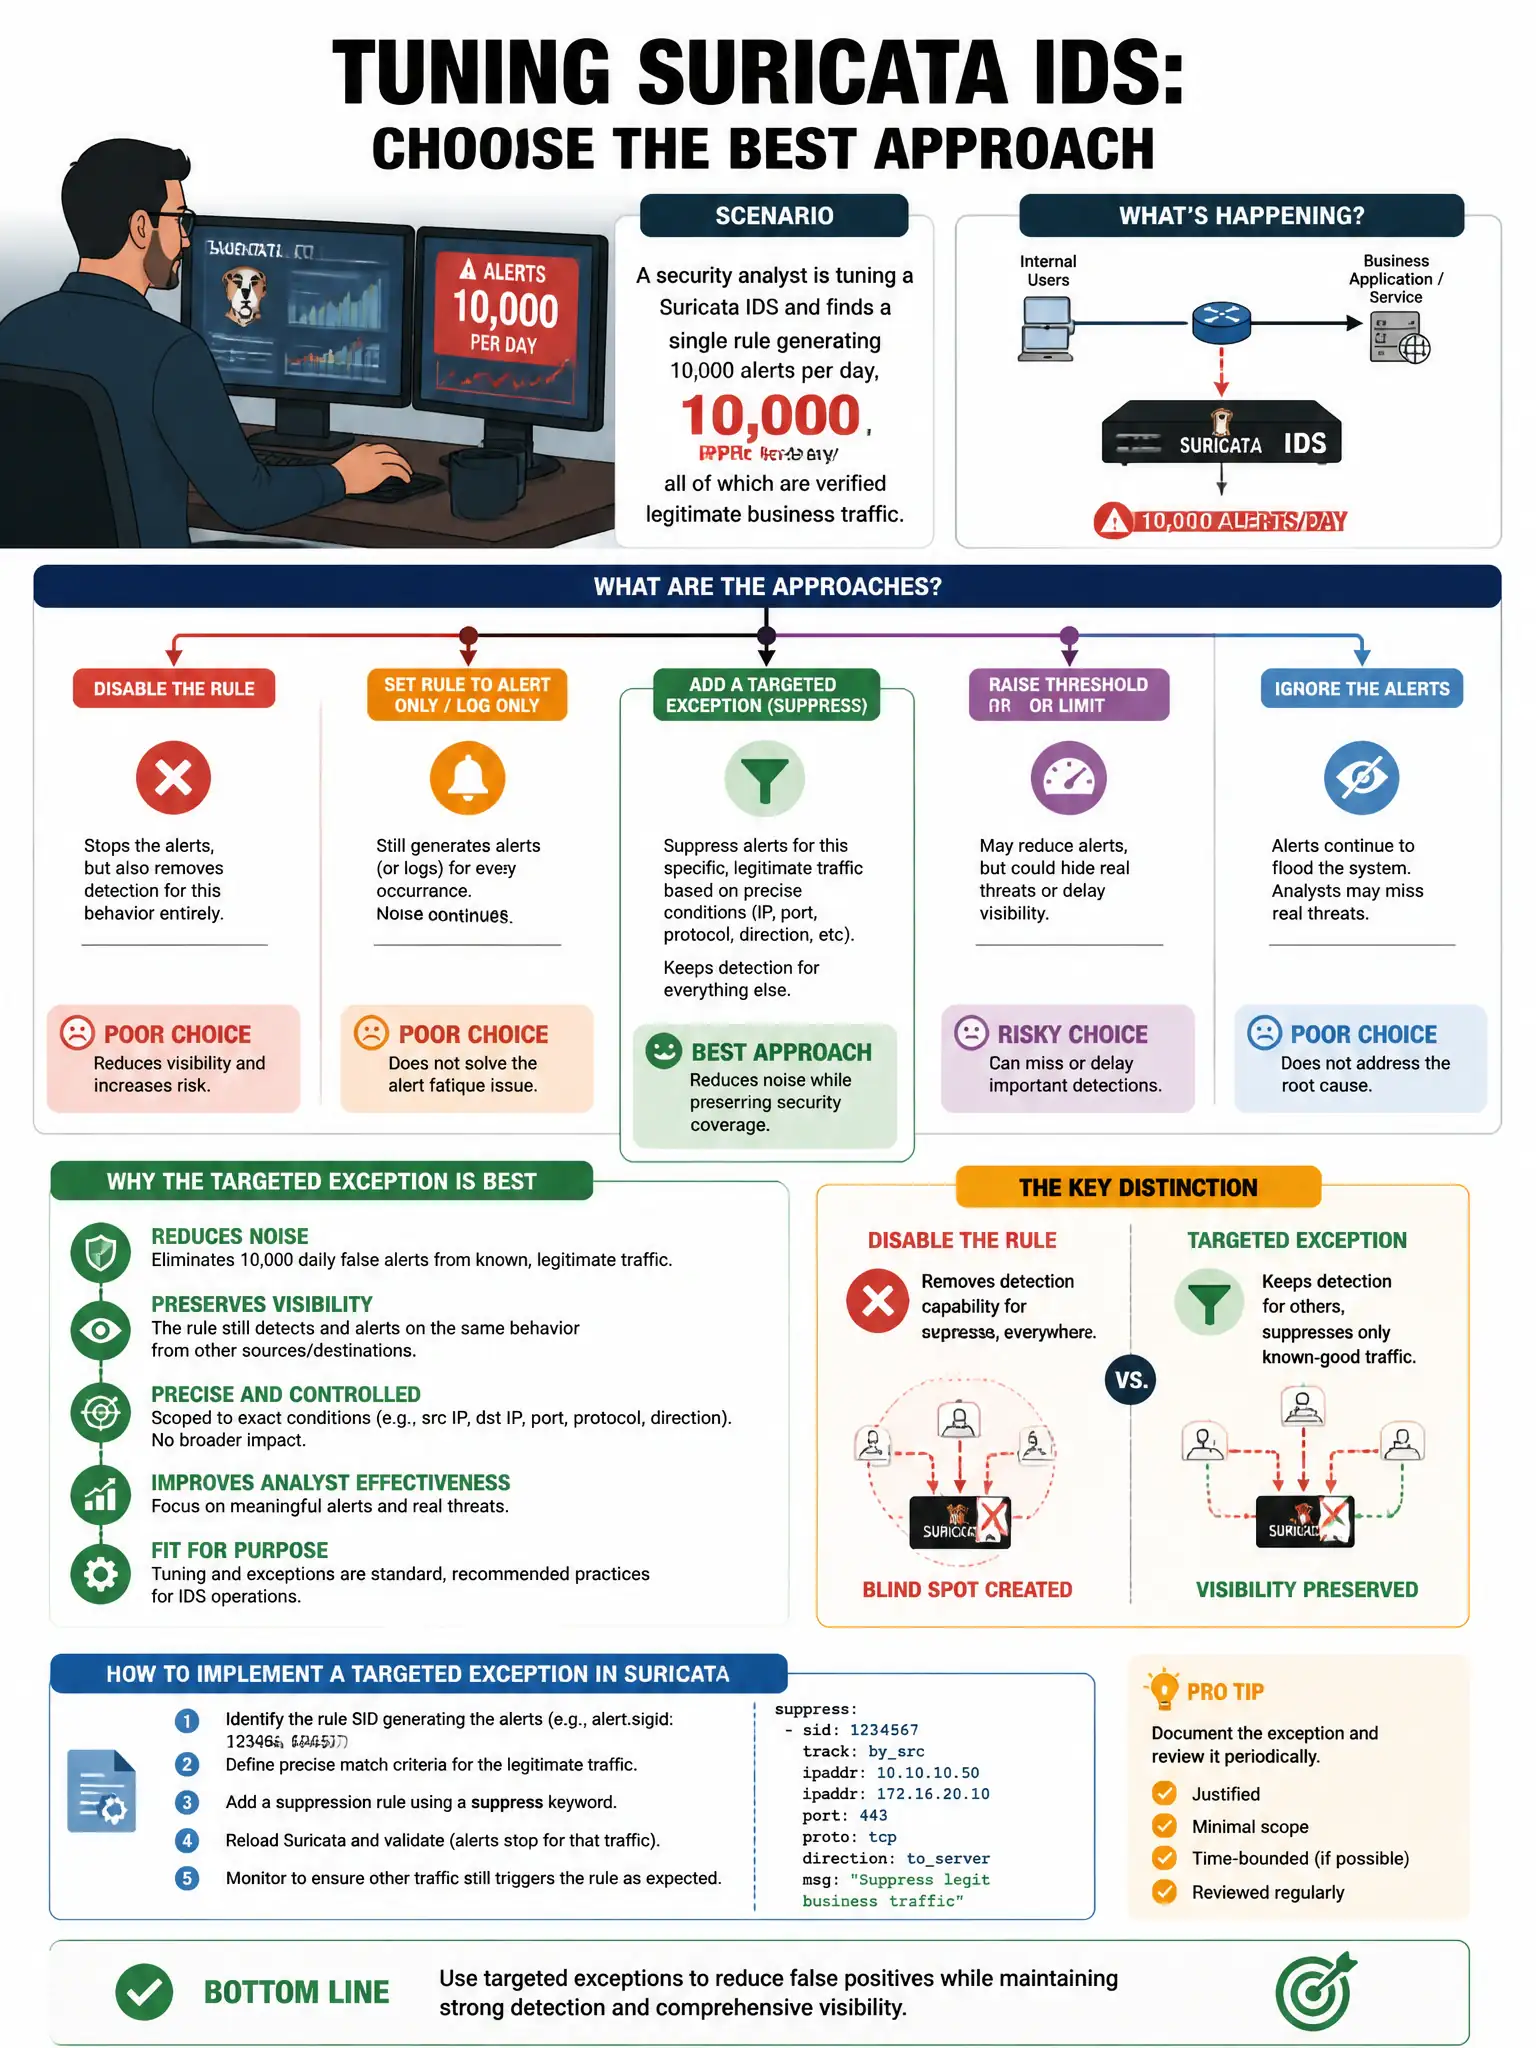
A security analyst is tuning a Suricata IDS and finds a single rule generating 10,000 alerts per day, all of which are verified legitimate business traffic. What is the BEST approach to reduce alert noise while maintaining detection capability?
Select an answer to reveal the explanation.
Short Explanation
You want to suppress or threshold the known-good source and destination pairs so the rule still catches other traffic. That cuts the noise without throwing away the signature.
Full Explanation
The best approach is to create a suppression rule or threshold that exempts known-good source and destination pairs while retaining the alert for other traffic. This lets the analyst whitelist known-good traffic, such as specific IPs, ports, or combinations, while preserving detection for the same signature against other traffic. Deleting the rule from the ruleset entirely is wrong because it eliminates detection of actual attacks in all contexts. Raising the alert severity threshold globally across all rules is wrong because it affects all rules and may suppress legitimate high-severity alerts. Disabling all IDS rules in the affected traffic category until the noise is resolved is wrong because it creates broad detection blind spots.