
A public-health department maps AWS Security Hub controls to its HIPAA-adjacent checklist for continuous evidence. What automation alignment is that?
Select an answer to reveal the explanation.
Short Explanation
You'll only get value when you've mapped Security Hub controls to the checklist rows auditors actually ask about — it's alignment, not just aggregating findings across accounts or exporting them to S3 with retention, and it's not Audit Manager's HIPAA framework which is a different source. Public health needs that crosswalk. Align the outputs to the checklist, period.
Full Explanation
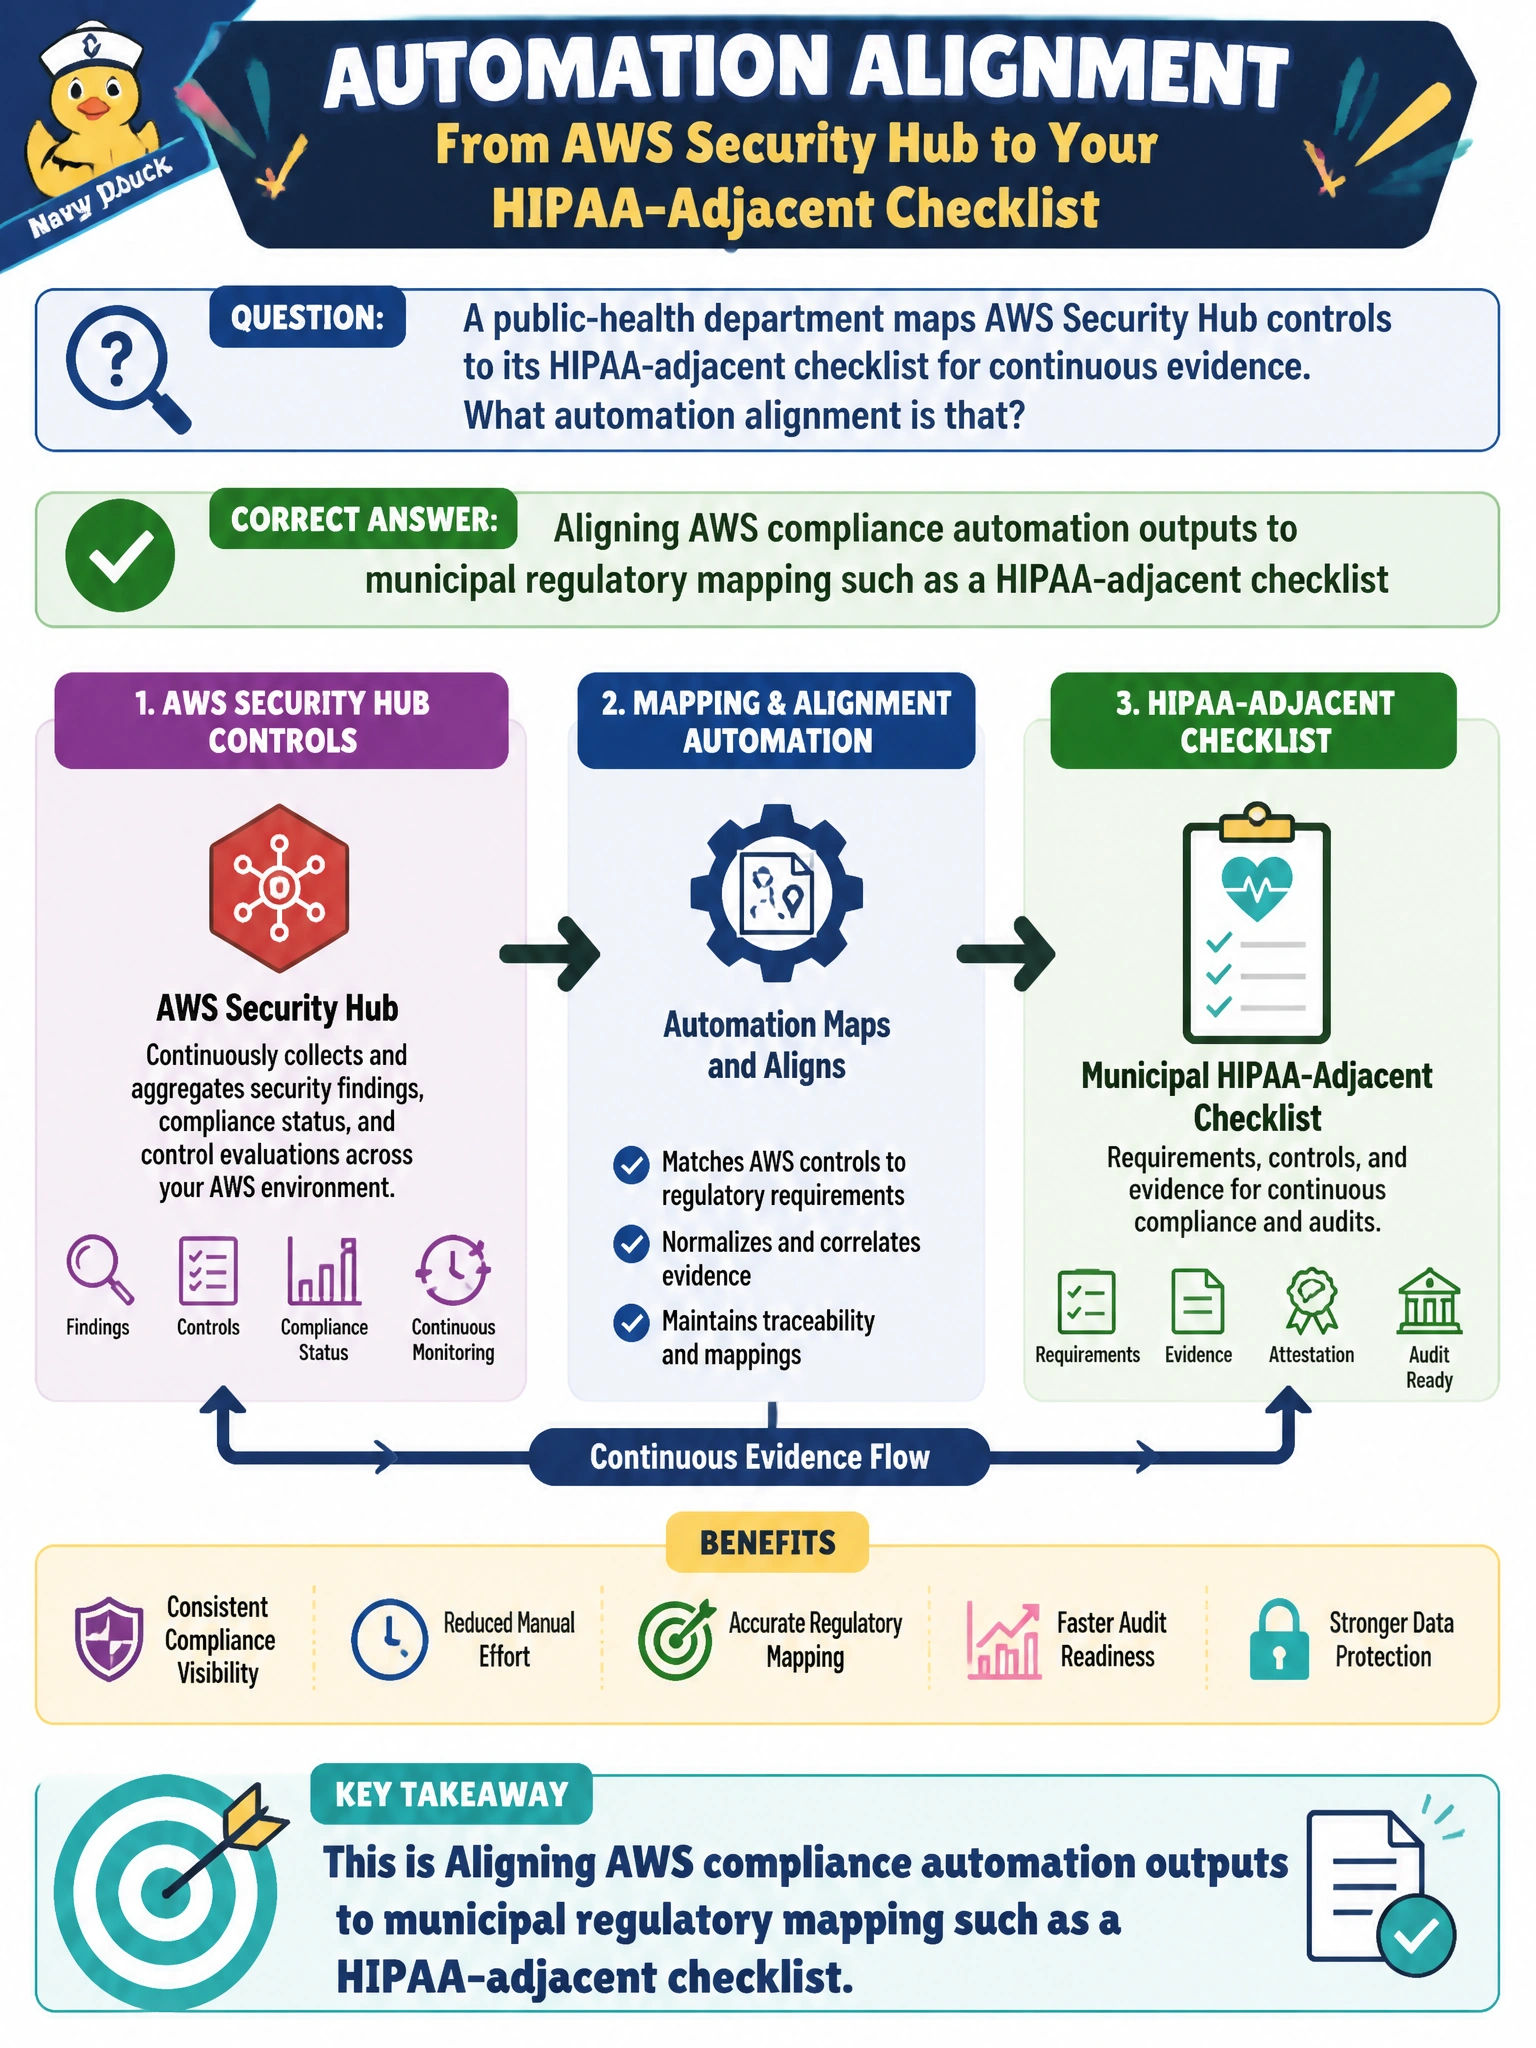
Aligning AWS compliance automation outputs to municipal regulatory mapping such as a HIPAA-adjacent checklist turns Security Hub (and related control results) into continuous evidence a public-health department can present against the controls auditors and compliance officers actually track. Mapping Hub controls to checklist rows creates a crosswalk: encryption, logging, and access findings become evidence items rather than orphan scores. That alignment keeps cloud automation relevant to civic regulatory programs instead of a parallel vanity metric system.
Aggregating Security Hub findings across accounts for municipal mapping to a HIPAA-adjacent checklist fails because aggregation only centralizes findings for visibility and does not itself create the regulatory crosswalk; collecting findings in one place without mapping any finding to a specific HIPAA-adjacent checklist row auditors can cite leaves the alignment undone. Exporting Security Hub findings to S3 with retention for municipal mapping to a HIPAA-adjacent checklist fails because retention preserves raw findings but does not translate them into checklist-aligned evidence; a well-archived finding that was never mapped to a checklist item still leaves the crosswalk undone. Enabling AWS Audit Manager HIPAA framework for automated mapping to a municipal HIPAA-adjacent checklist fails because Audit Manager is a different automation source from Security Hub controls; the stem asks about aligning Security Hub control outputs, not running Audit Manager assessments, so even automated mapping in Audit Manager misses the asked-for Security Hub alignment.
Exam caveat: When the stem mentions mapping Security Hub to a municipal HIPAA-adjacent checklist, the correct idea is regulatory alignment of automation outputs—not aggregating findings across accounts which only centralizes them, exporting findings to S3 with retention which only stores them, or enabling Audit Manager HIPAA framework which is a different automation source than Security Hub controls.
Operational check for public-health cloud compliance: maintain a documented crosswalk from Security Hub controls to checklist items, refresh Hub standards relevant to encryption and logging, sample failed controls into remediation tickets tagged to checklist IDs, and verify quarterly evidence packages cite Hub findings mapped to those civic checklist rows.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.