
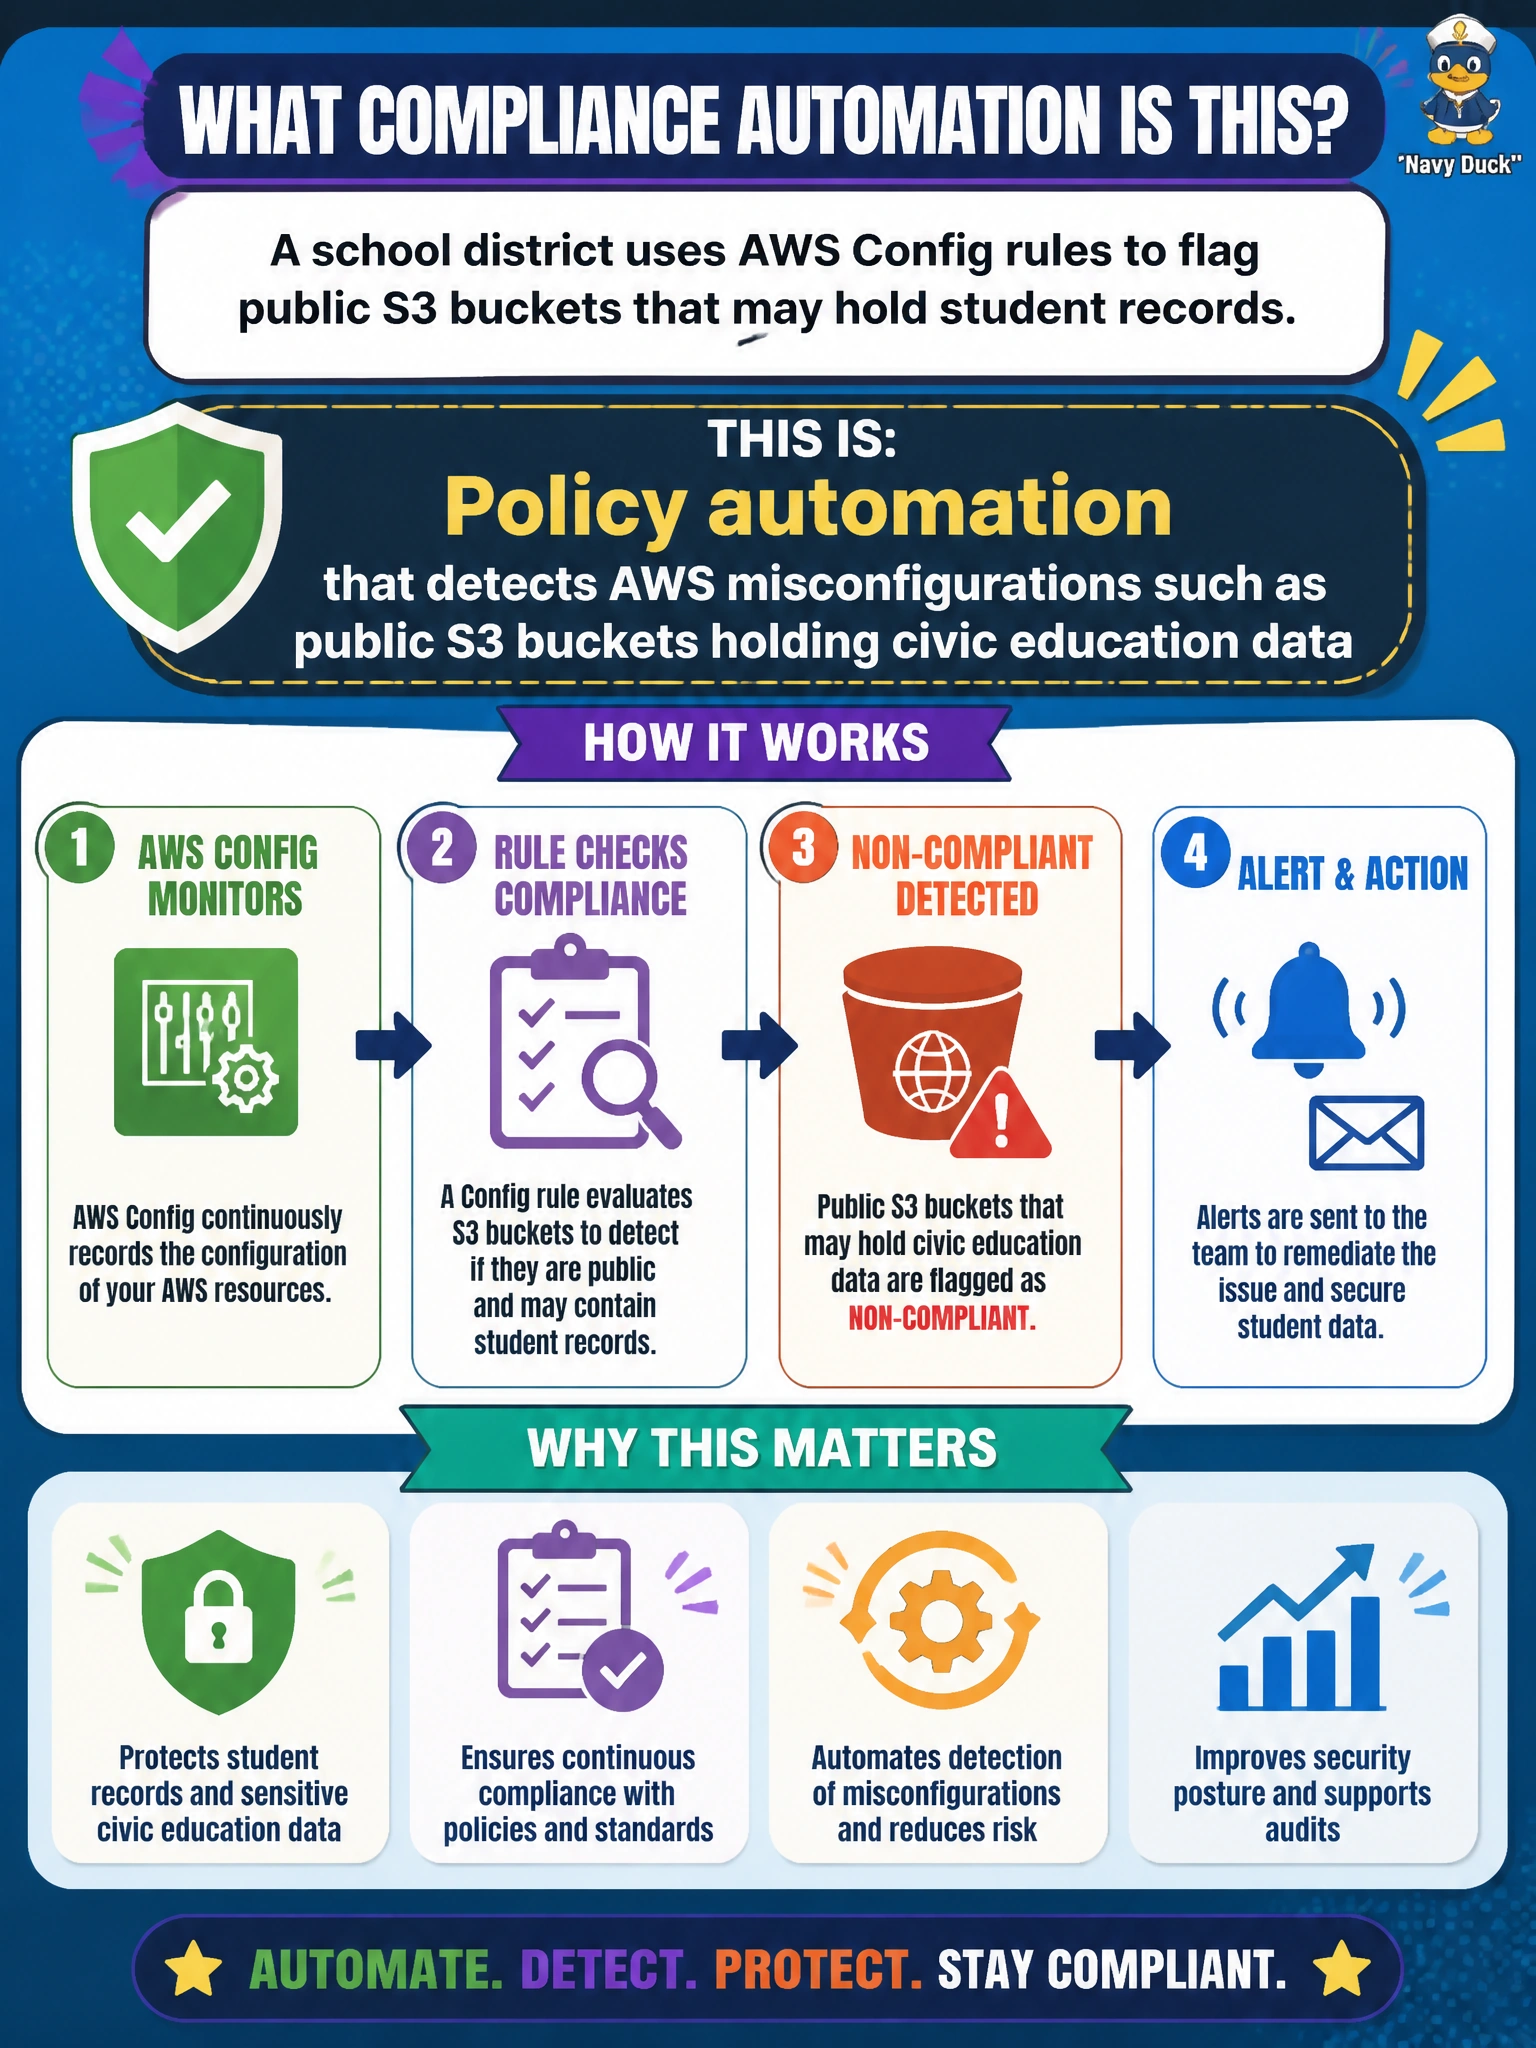
A school district uses AWS Config rules to flag public S3 buckets that may hold student records. What compliance automation is that?
Select an answer to reveal the explanation.
Short Explanation
Config rules are the night watch for student buckets—if something goes public, you'll get a flag now, not just CloudTrail data events after someone's accessed it. Server access logs make you hunt for clues and Glacier moves don't check exposure at all, so you'll still miss the misconfig. Automate the misconfig check.
Full Explanation
Policy automation that detects AWS misconfigurations such as public S3 buckets holding civic education data uses AWS Config rules (and related continuous evaluation) to flag public or overly permissive buckets that may store student records. Continuous detection shortens the window between misconfiguration and school-district awareness, supporting data-protection obligations without waiting for annual binder audits. Automating the check scales across many buckets and accounts typical of district AWS estates.
Policy automation that detects public S3 buckets holding civic education data using S3 server access log analysis fails by concept because server access logs only record access requests after the fact and require separate collection and analysis; they do not continuously evaluate bucket ACLs and policies for public exposure, so misconfigured access remains undiscovered. Policy automation that detects public S3 buckets holding civic education data using CloudTrail S3 data events fails because CloudTrail S3 data events record object-level API activity after the fact rather than continuously evaluating bucket permissions, so publicly exposed buckets are not flagged as misconfigurations in real time. Policy automation that detects public S3 buckets holding civic education data using S3 Lifecycle Glacier transitions fails because transitioning objects to cheaper storage does not evaluate or detect public or overly permissive buckets and does nothing to flag misconfigured access for student records.
Exam caveat: GASAE AWS compliance automation items favor continuous Config-style detection of public S3 risk for civic education data. Reject S3 server access log analysis, CloudTrail S3 data events, and S3 Lifecycle Glacier transitions as substitutes for continuous public-bucket detection.
Operational check for a school district cloud team: enable Config rules that detect public S3 ACLs and policies, plant a non-production public test bucket with synthetic data, confirm the rule flags it promptly, remediate or alert through the district ticket path, and ensure production student-data buckets remain private with continuous evaluation still enabled.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.