
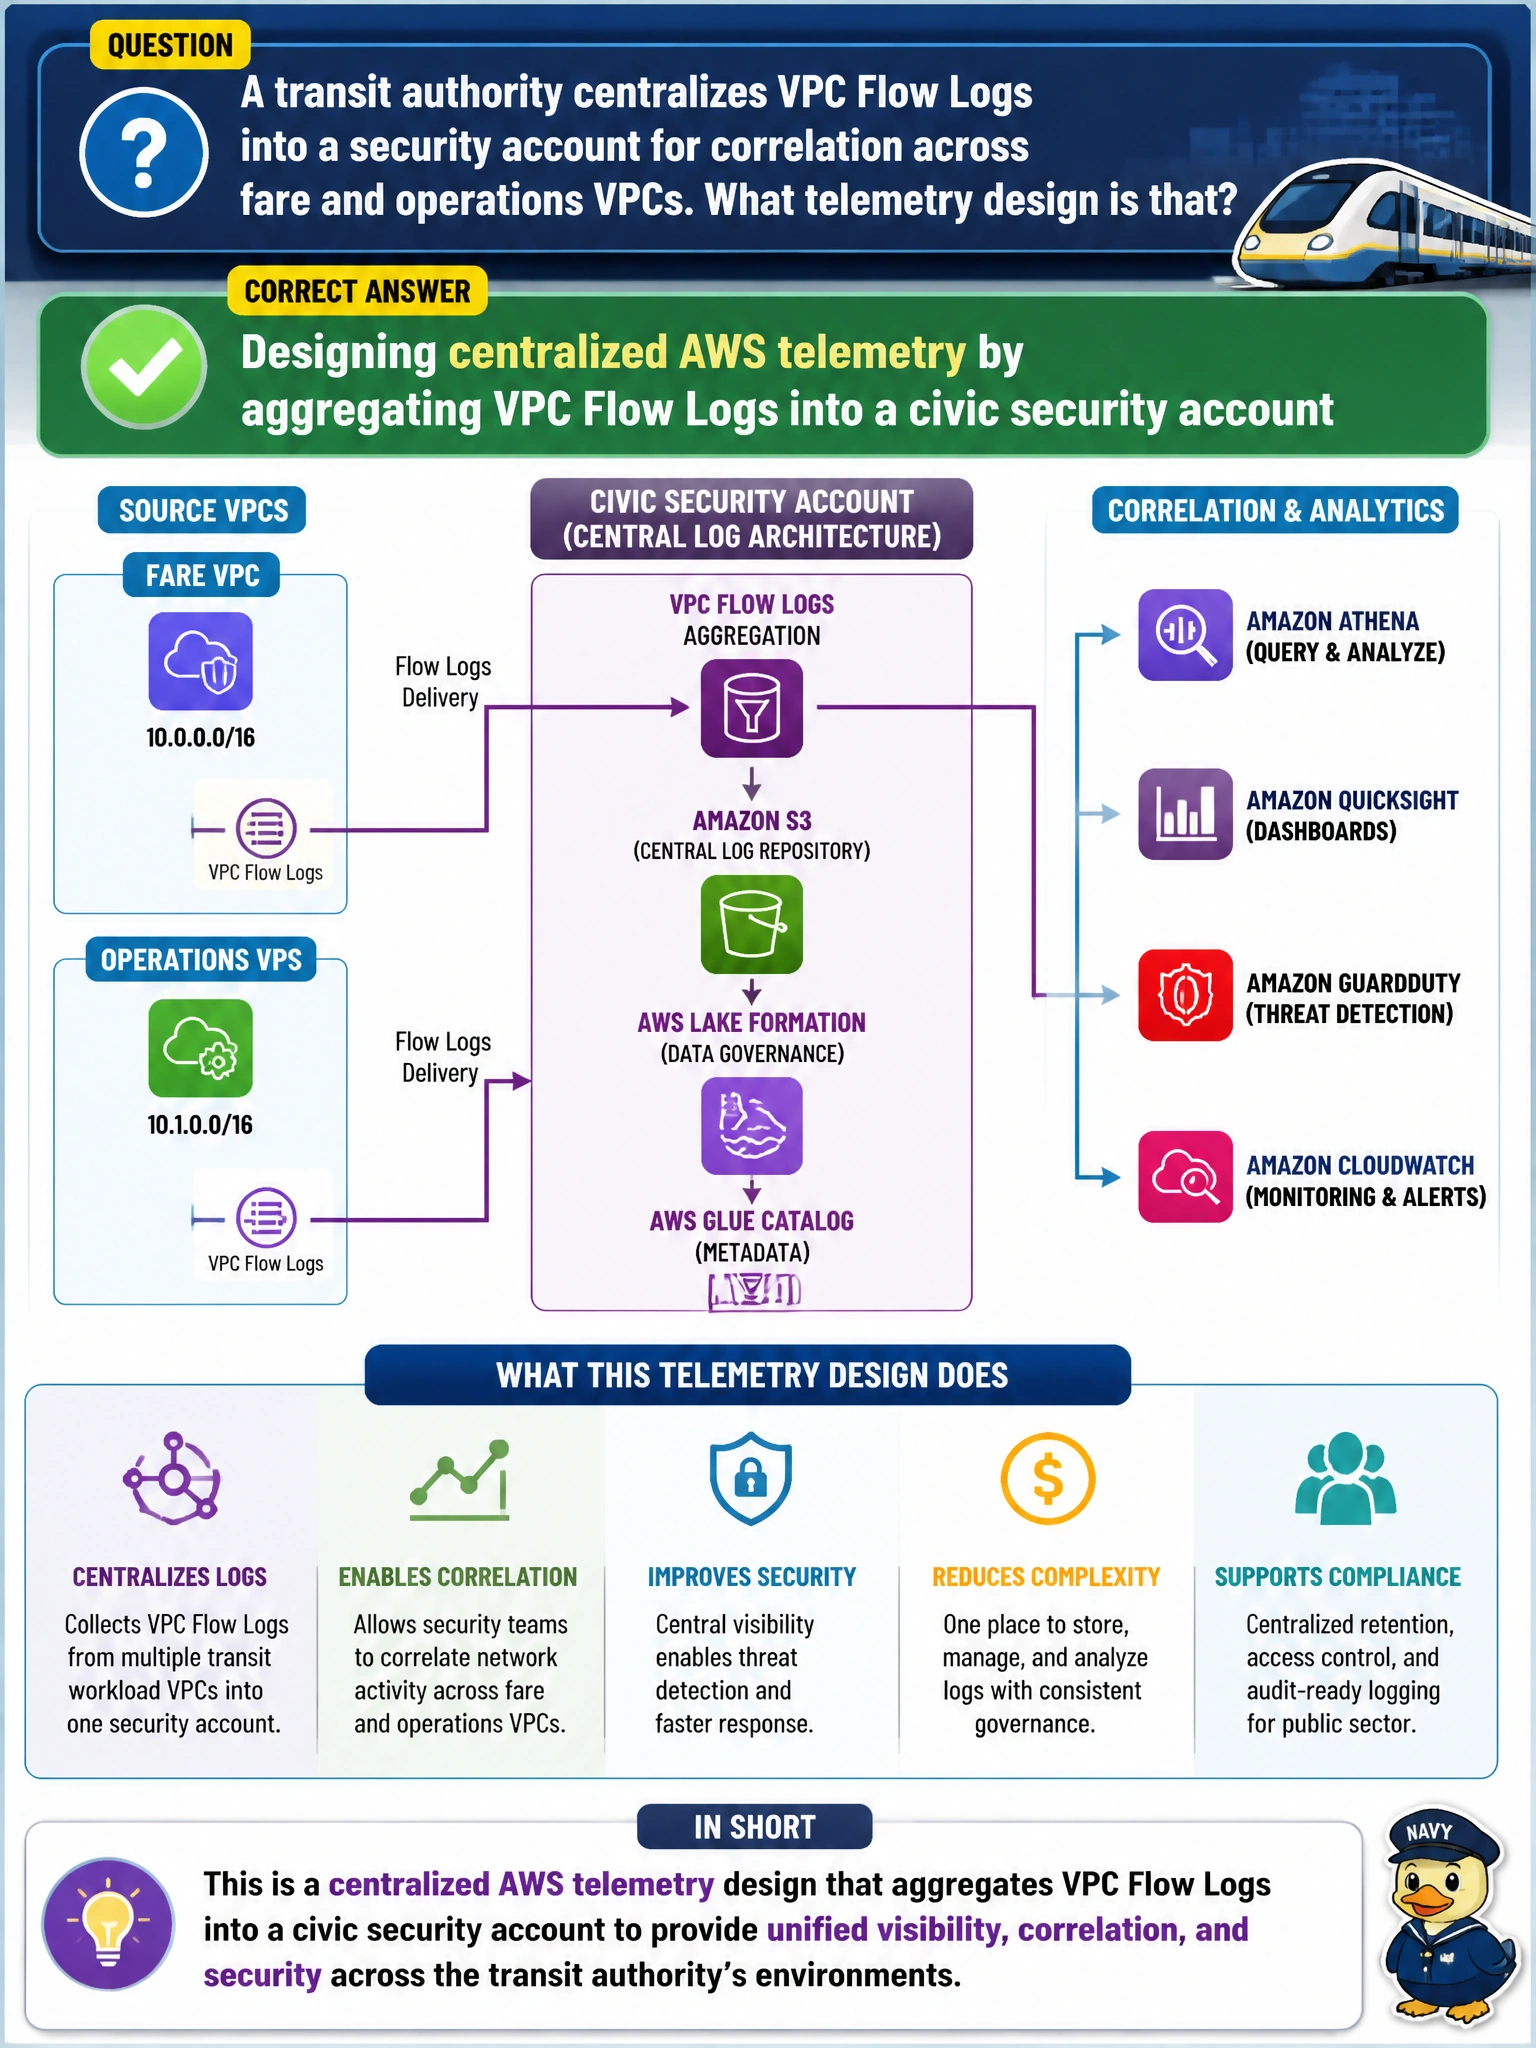
A transit authority centralizes VPC Flow Logs into a security account for correlation across fare and operations VPCs. What telemetry design is that?
Select an answer to reveal the explanation.
Short Explanation
Put the flow logs where you can actually correlate them—a central security account—you're aggregating flow metadata, not capturing payloads or mirroring traffic. Don't expect them to block threats; you'll only get flow metadata for correlation. Centralize the telemetry.
Full Explanation
Designing centralized AWS telemetry by aggregating VPC Flow Logs into a civic security account lets a transit authority correlate network evidence across fare and operations VPCs from one monitored destination. Central aggregation supports SOC correlation, retention controls, and IR investigations that span multiple workload accounts without hopping between siloed log piles. For multi-account municipal AWS orgs, the security account becomes the telemetry hub for flow data that reveals lateral movement, unexpected east-west traffic, and exposure paths affecting rider-facing and operations systems. Designing centralized AWS telemetry by capturing VPC Flow Logs payloads in a civic security account fails by capability because VPC Flow Logs record flow metadata — source, destination, ports, protocol, bytes, and accept/reject — not packet payloads, so they cannot provide packet content for inspection. Designing centralized AWS telemetry by mirroring VPC Flow Logs traffic to a civic security account fails because centralized flow-log telemetry is log aggregation to S3, CloudWatch, or Kinesis, not VPC Traffic Mirroring, which copies raw packets via mirror sessions and targets for separate inspection. Designing centralized AWS telemetry by blocking VPC Flow Logs threats in a civic security account fails because VPC Flow Logs are passive, read-only telemetry for detection and correlation — they record flow evidence but do not inline block threats like security groups, NACLs, or WAF do. Exam caveat: Centralized security-account aggregation of VPC Flow Logs is the expected multi-account telemetry design. Do not confuse capturing VPC Flow Logs payloads, mirroring VPC Flow Logs traffic, or blocking threats with security-account aggregation of flow metadata. Operational check for transit cloud security: enable VPC Flow Logs on fare and operations VPCs, deliver them to a central security account bucket or analytics store with least-privilege SOC access, validate that a sample flow from each VPC appears in the hub, and confirm logs are aggregated as flow metadata, not expected to yield packet payloads, confused with mirrored traffic, or expected to block threats.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.