
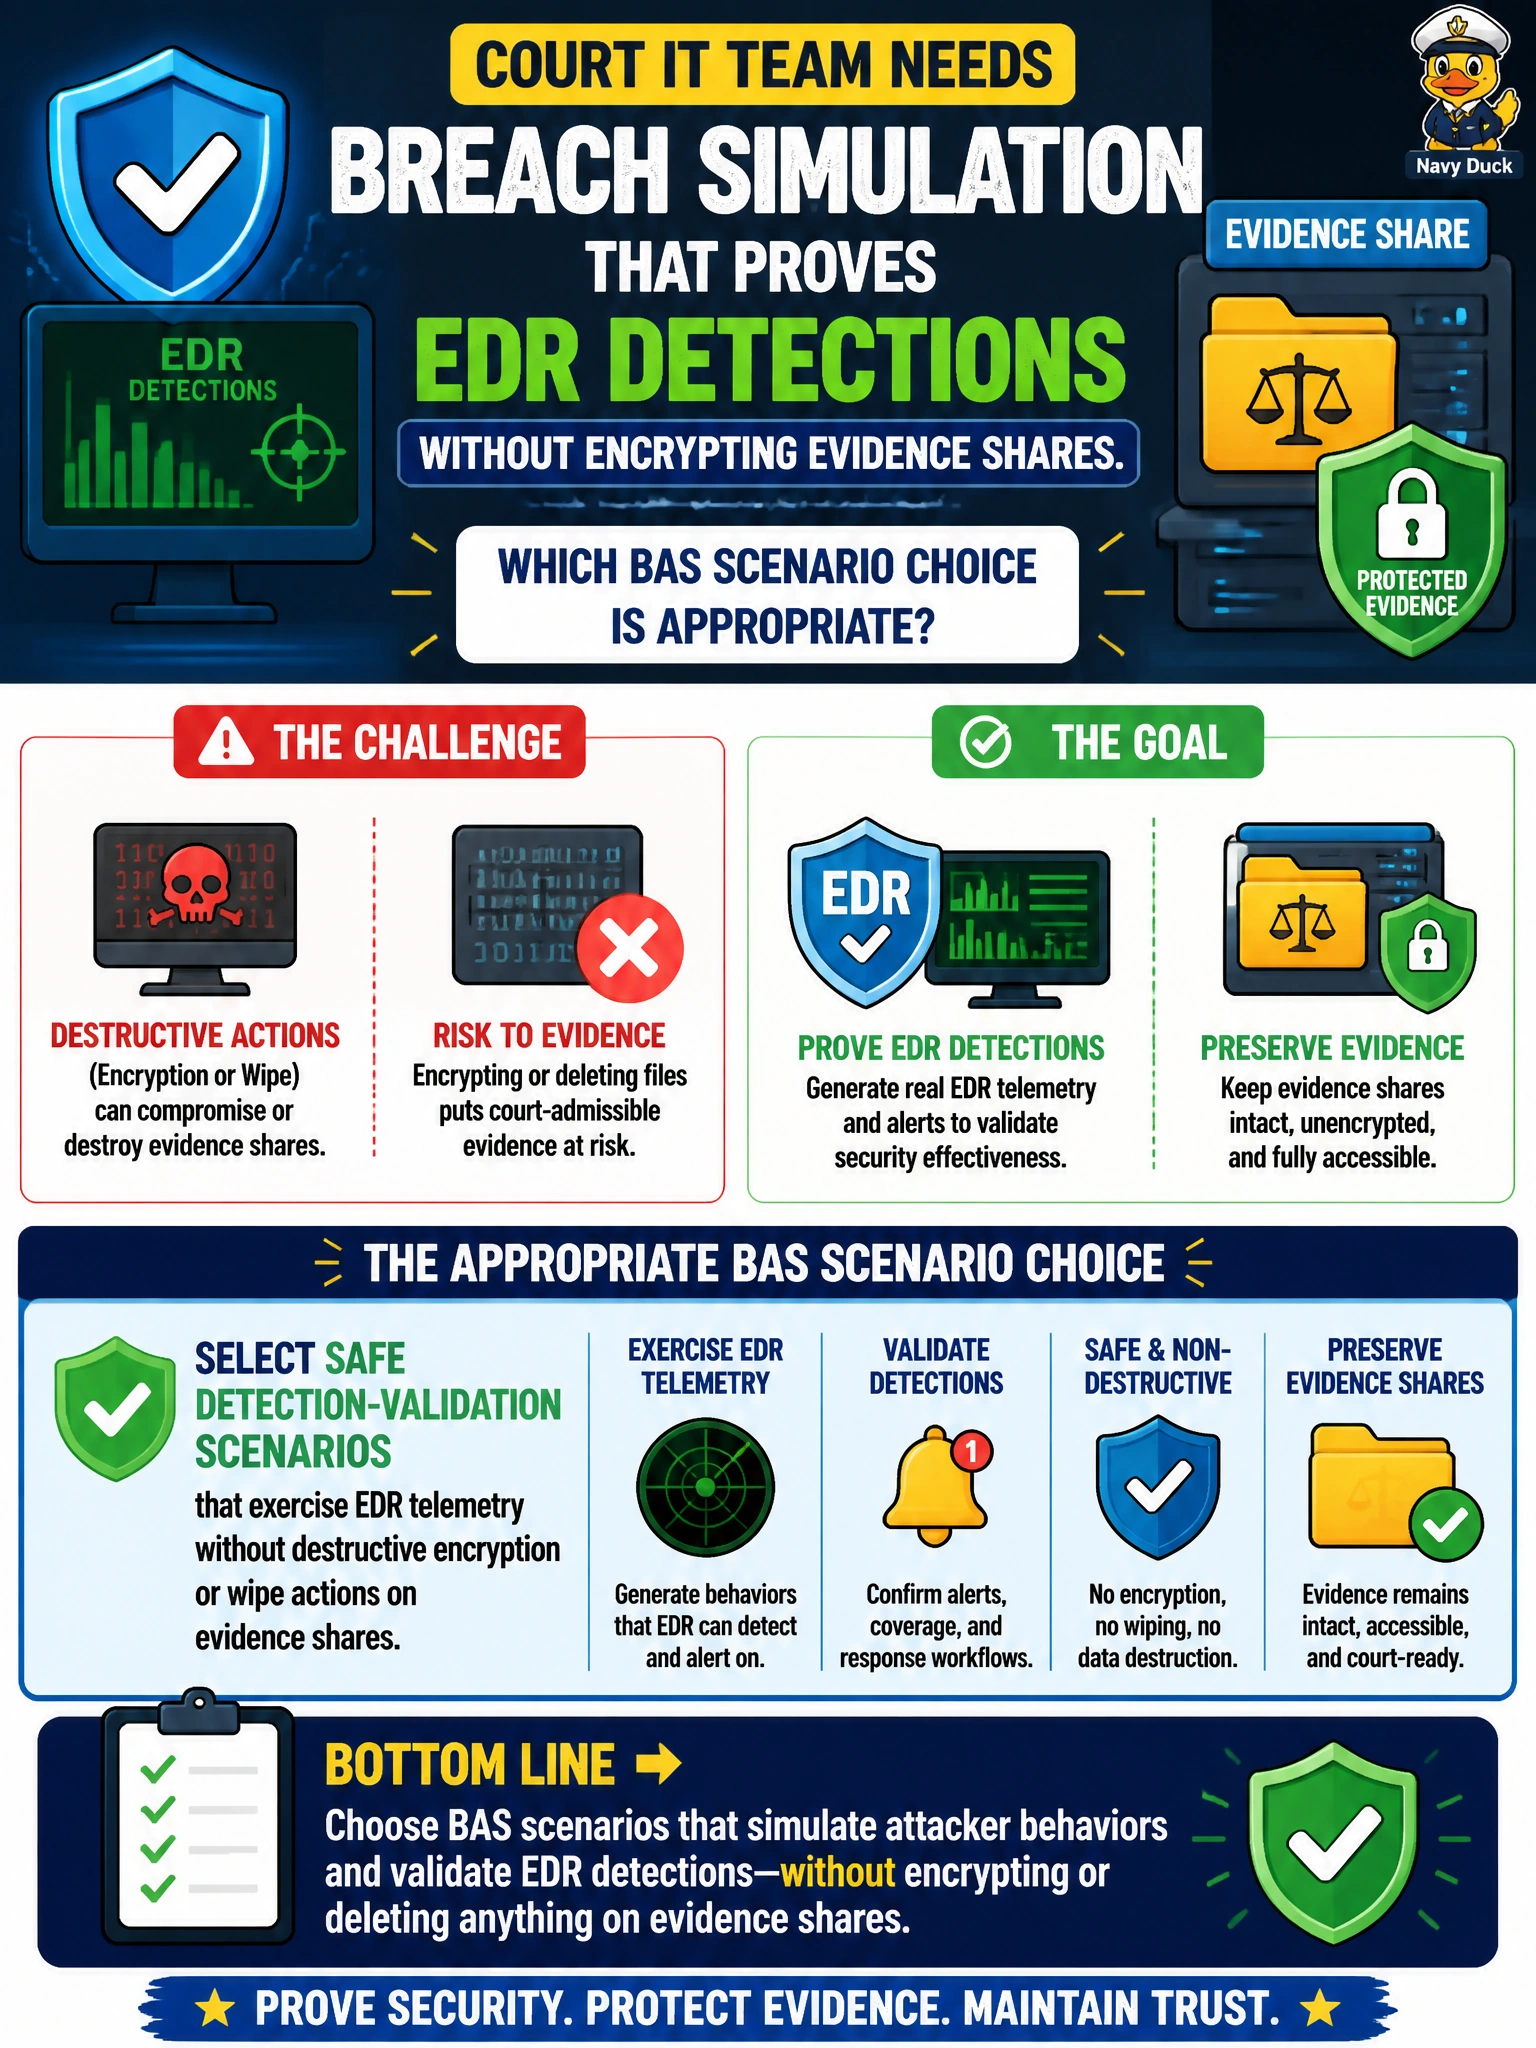
A court IT team needs breach simulation that proves EDR detections without encrypting evidence shares. Which BAS scenario choice is appropriate?
Select an answer to reveal the explanation.
Short Explanation
You want the smoke alarm to chirp, not the courthouse to burn. Don't pick firewall, email, or DLP telemetry — you'll test the wrong sensors, not proof of EDR detection without encrypting or wiping your evidence shares.
Full Explanation
A court IT team that needs breach simulation proving EDR detections without harming evidence shares should select safe detection-validation scenarios that exercise EDR telemetry without destructive encryption or wipe actions on those repositories. Judicial evidence integrity and availability are non-negotiable; purple-team value comes from proving alerts and telemetry for modeled behaviors, not from actually encrypting or deleting case materials. Safe scenarios still stress detection paths while protecting court operations.
Why the other options fail by concept: Selecting safe detection-validation scenarios that exercise firewall telemetry without destructive encryption or wipe actions on evidence shares validates firewall sensor paths rather than proving EDR detections while protecting evidence shares from encrypt or wipe impact. Selecting safe detection-validation scenarios that exercise email telemetry without destructive encryption or wipe actions on evidence shares validates email delivery telemetry rather than proving endpoint EDR detection while protecting evidence shares from encrypt or wipe impact. Selecting safe detection-validation scenarios that exercise DLP telemetry without destructive encryption or wipe actions on evidence shares centers on data-loss prevention signals rather than proving EDR telemetry without destructive actions on evidence stores.
Exam caveat: “safe” still means authorized behaviors on approved hosts—some precursor or benign indicators may be used, but impact actions against evidence stores require separate, explicit DR authorization if ever allowed at all. Operational check: choose BAS scenarios tagged as non-destructive detection checks, verify evidence shares are excluded from encrypt/wipe actions, keep EDR enabled, and confirm alert telemetry for the modeled techniques before closing the court exercise.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.