
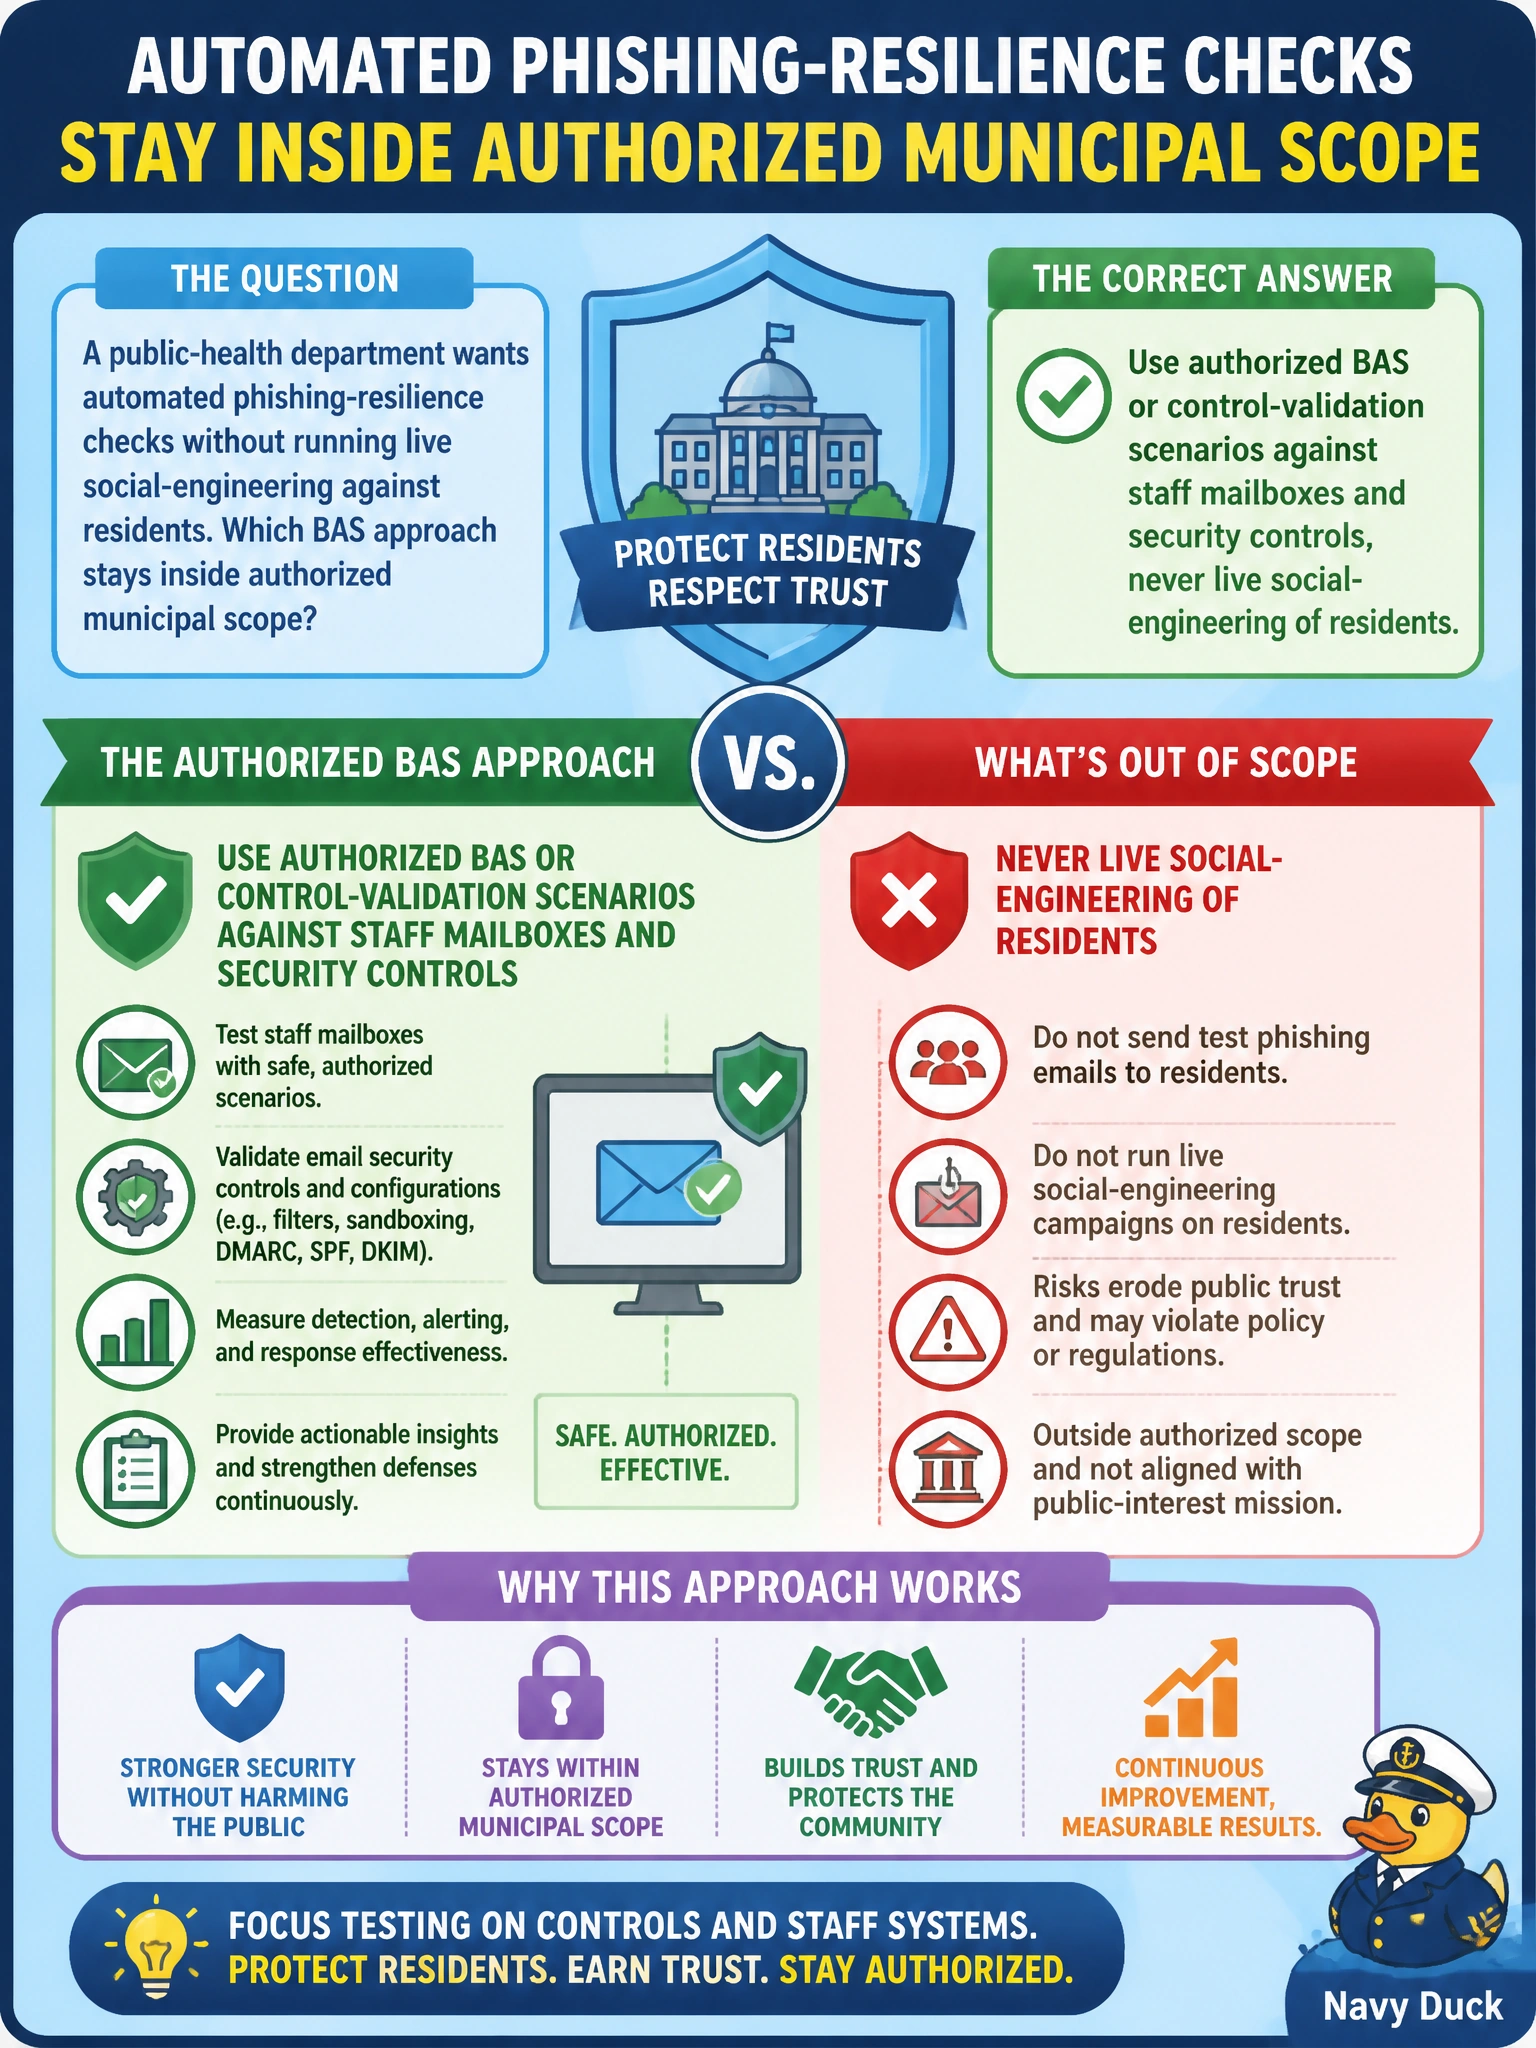
A public-health department wants automated phishing-resilience checks without running live social-engineering against residents. Which BAS approach stays inside authorized municipal scope?
Select an answer to reveal the explanation.
Short Explanation
Staff inboxes under a signed test plan are the gym, but you'll blow that approval if you're pulling sampled resident inboxes into scope, replaying creds to external lookalike domains, or flipping enforcement mode to alter live production mail flow. Keep automated phishing-resilience checks inside authorized staff and control scope.
Full Explanation
A public-health department that wants automated phishing-resilience checks without live social-engineering of residents should use authorized BAS or control-validation scenarios against staff mailboxes and security controls only. Municipal authorization and ethics typically allow testing staff and technical controls under an approved plan; they do not authorize running scenarios in enforcement mode altering live production mail flow, which risks service disruption and exceeds safe BAS control-validation. Keeping BAS inside staff and control scope preserves trust in civic health services while still validating mail filters, EDR, and user-awareness controls for employees.
Why the other options fail by concept: Using authorized BAS or control-validation scenarios against staff mailboxes and security controls plus sampled resident inboxes for coverage still expands testing to live social-engineering of residents outside municipal authorization, violating scope limits and eroding trust in civic health services even to gain broader coverage. Using authorized BAS or control-validation scenarios against staff mailboxes and security controls with credential replay to external lookalike domains still exfiltrates real credentials outside municipal control, turning safe control-validation into unsafe data exposure that violates handling and authorization limits. Using authorized BAS or control-validation scenarios against staff mailboxes and security controls in enforcement mode altering live production mail flow still changes live municipal operations beyond safe-simulation scope, exceeding authorized control-validation and risking outage, misdelivery, and loss of trust.
Exam caveat: even staff-targeted BAS phishing requires written authorization, clear branding/deconfliction rules where policy requires them, and a plan to handle real incident tickets generated by the exercise. Operational check: confirm the test plan names staff mailboxes and security controls as targets, excludes resident/patient populations, routes results to the SOC under change control, and archives approval before any automated phishing-resilience scenario runs.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.