
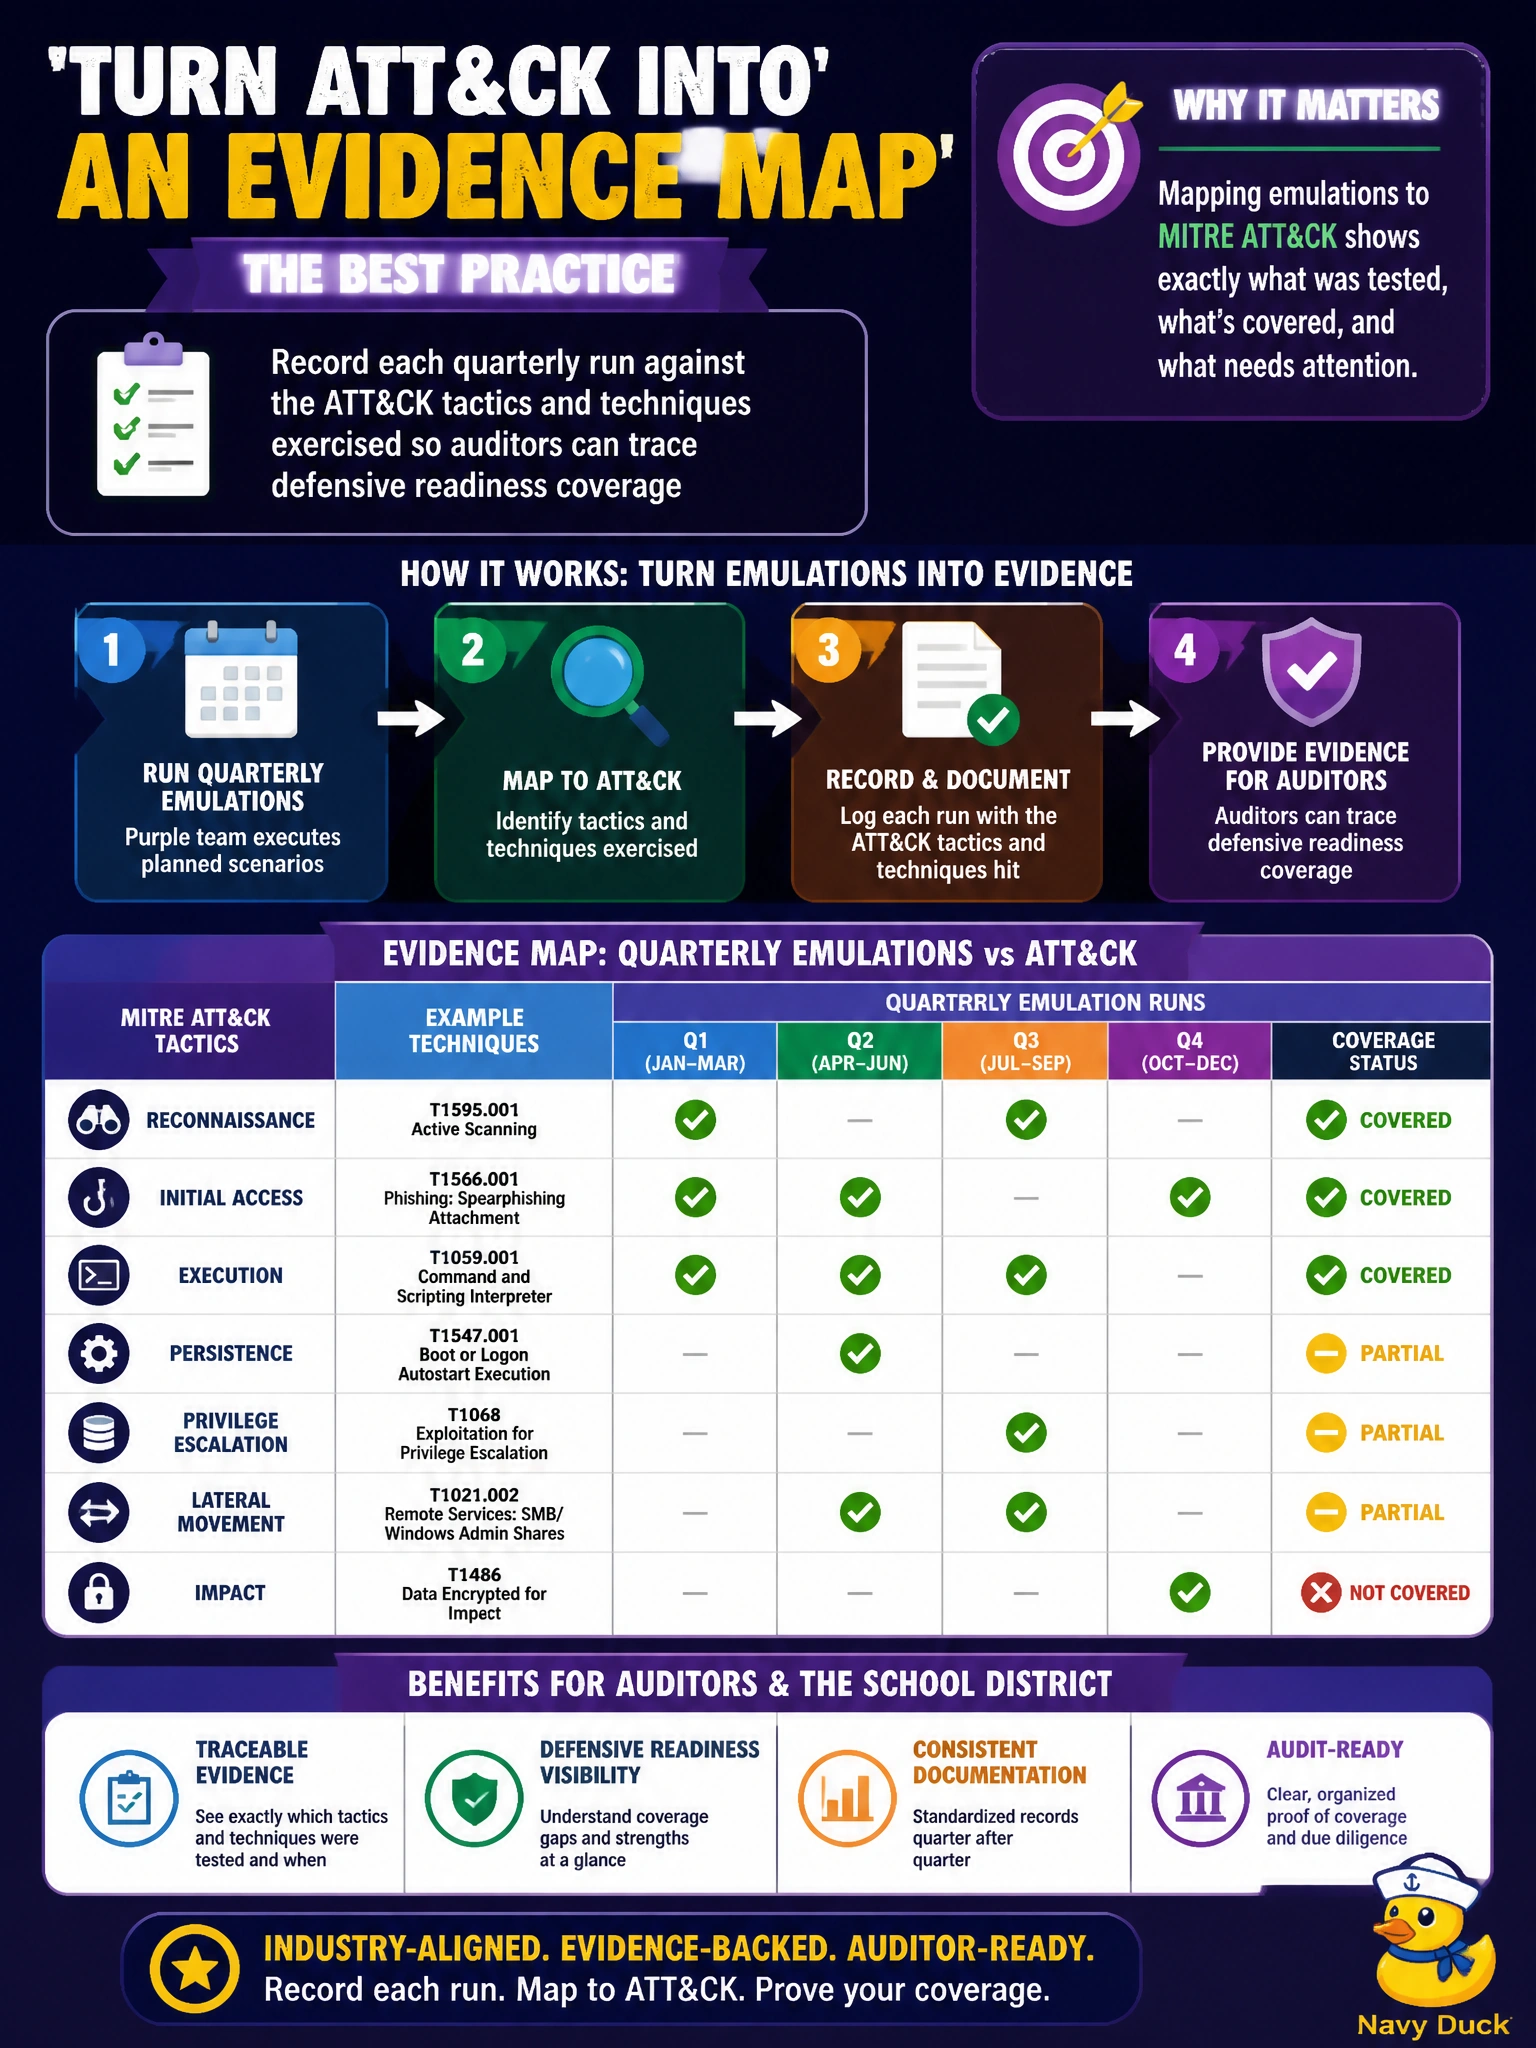
A school-district purple team must document which ATT&CK tactics each quarterly emulation covers for auditors. What practice best turns the framework into an evidence map?
Select an answer to reveal the explanation.
Short Explanation
Auditors want a checklist that says which city streets you actually walked—not just that you rented a GPS. Map each quarterly run to ATT&CK tactics and techniques so coverage is evidence, not folklore.
Full Explanation
A school-district purple team documenting quarterly emulation for auditors should record each run against the ATT&CK tactics and techniques exercised so defensive readiness coverage is traceable. That practice turns the framework into an evidence map: oversight can see which modeled behaviors were actually run, which detections fired, and which gaps remain—without relying on tribal knowledge or tool screenshots alone. Civic audit binders need shared identifiers, not folklore.
Why the other options fail by concept: Logging each quarterly run against the ATT&CK mitigations and vendor advisories referenced tracks patch compliance guidance but does not show which tactics and techniques were actually exercised, so auditors cannot trace defensive readiness coverage. Summarizing each quarterly emulation by the CVE identifiers tied to ATT&CK techniques shows remediation coverage trends, but it does not record which tactics and techniques were emulated with detection outcomes, so auditors cannot trace defensive readiness coverage across quarters. Consolidating each quarterly run against the ATT&CK tactics tested into BAS pass-rate trends gives auditors performance scores over time, but it replaces technique-level evidence of what was exercised and detected with aggregate pass rates, so they cannot validate which controls were actually exercised.
Exam caveat: mapping runs to ATT&CK IDs is necessary but not sufficient—evidence should also note environment, date, authorization, and detection/response outcomes for each technique. Operational check: after each quarterly school-district run, export or write a coverage matrix of tactic/technique IDs to results, attach it to the audit package, and reconcile gaps against the district’s required control-check list before closing the exercise.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.