
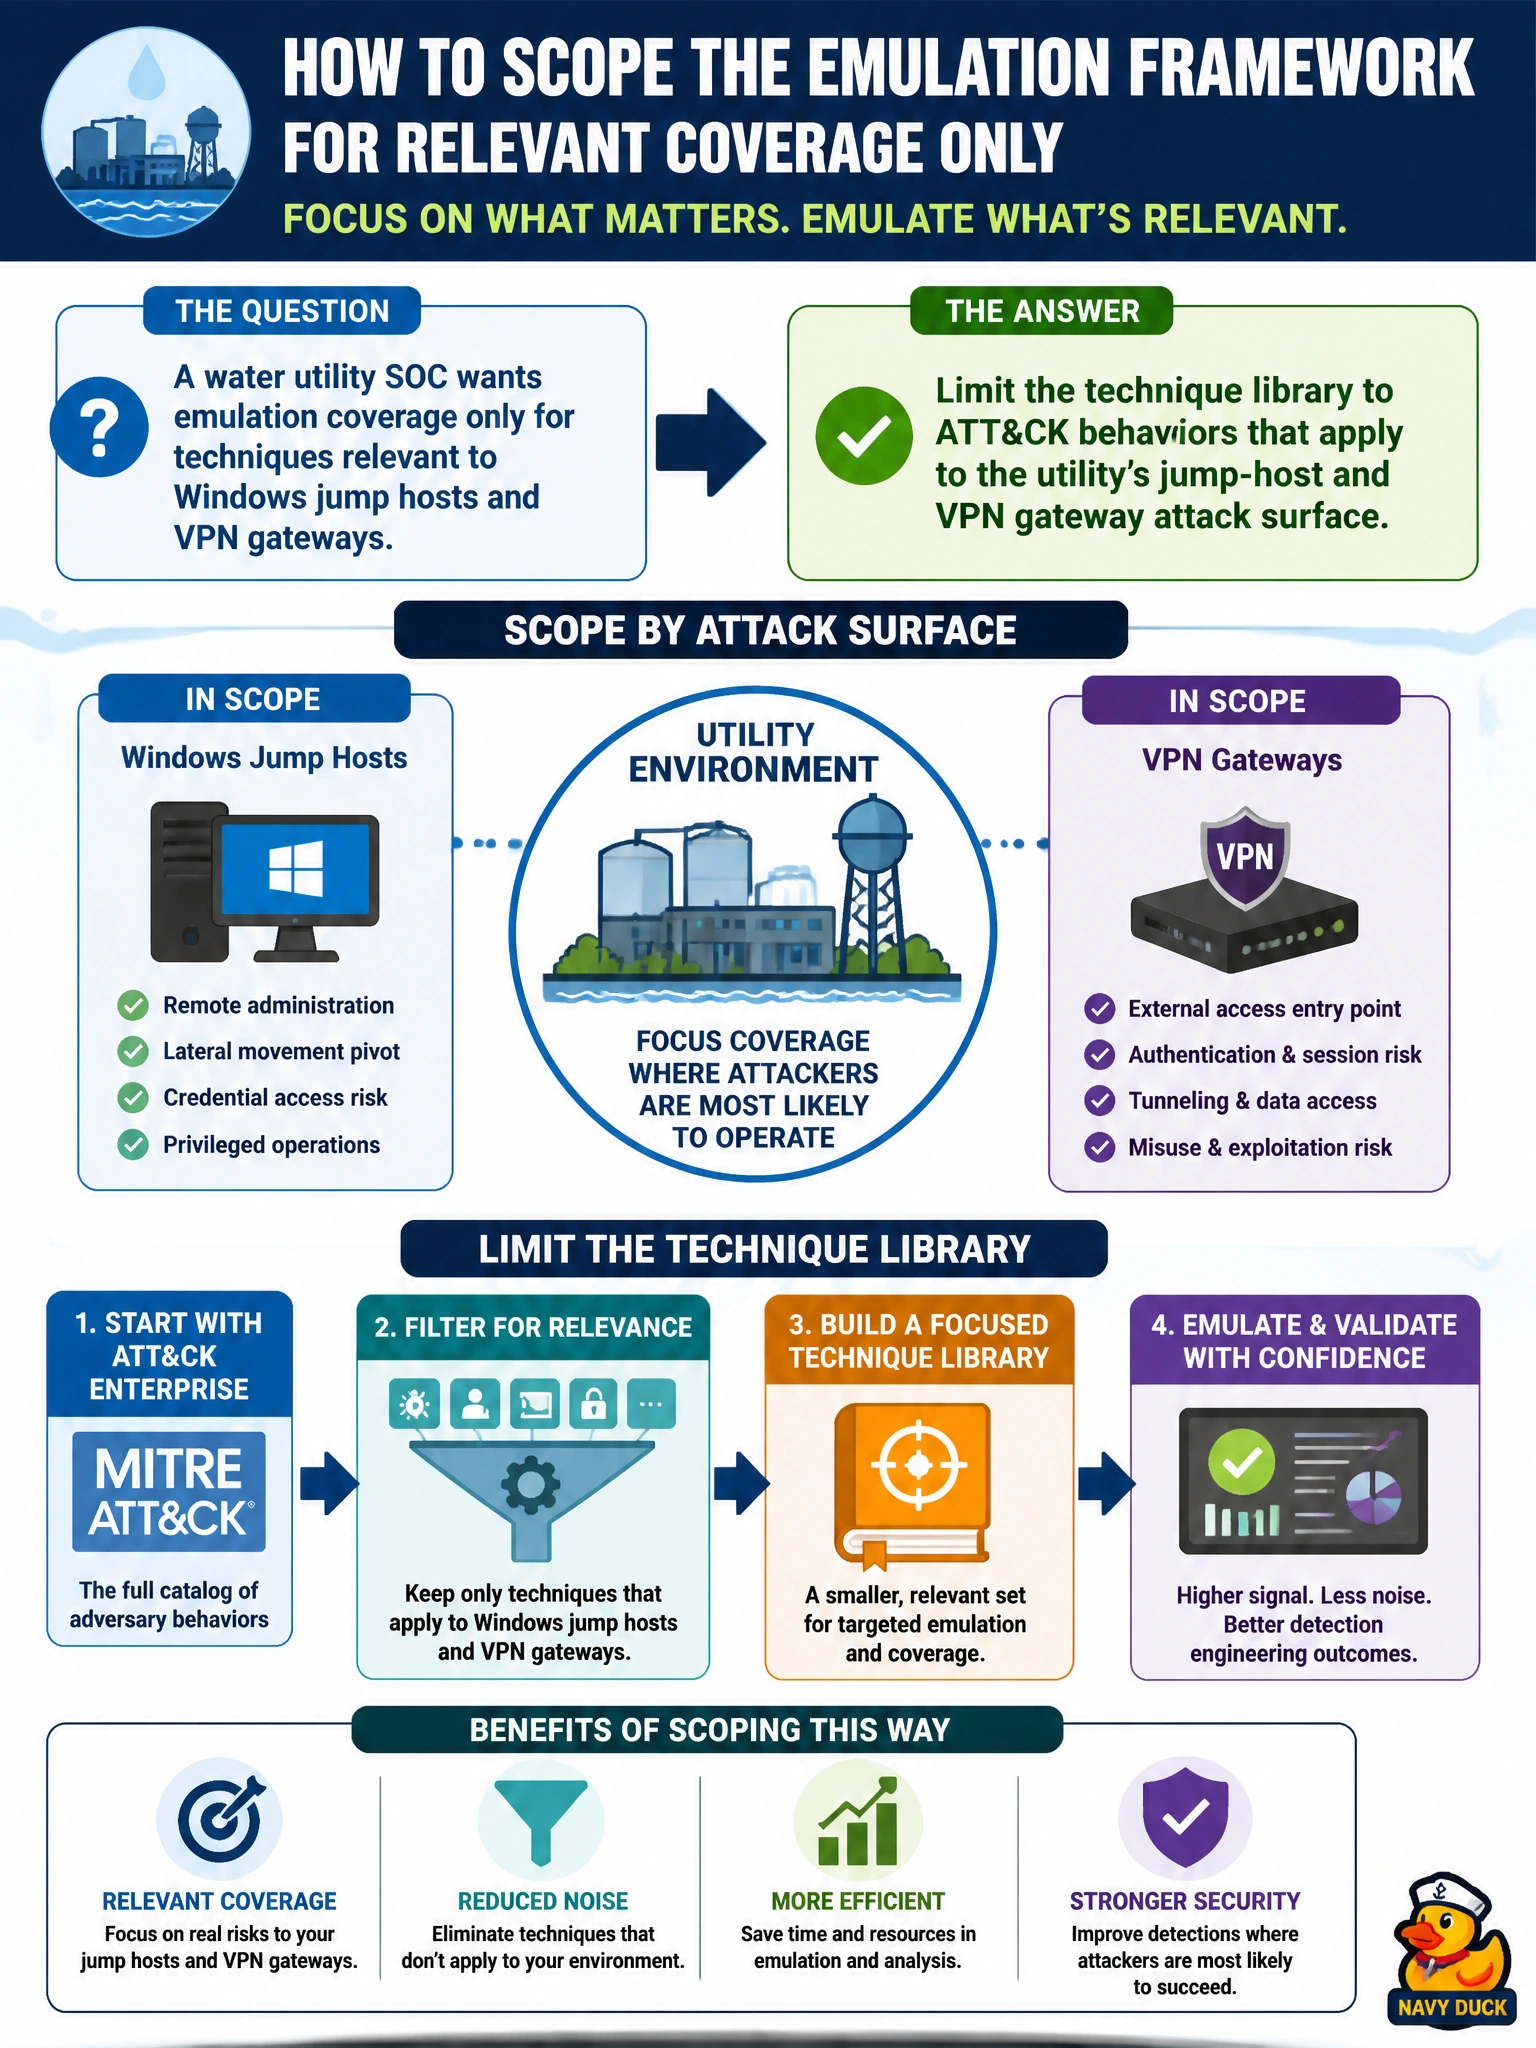
A water utility SOC wants emulation coverage only for techniques relevant to Windows jump hosts and VPN gateways. How should the team scope the emulation framework?
Select an answer to reveal the explanation.
Short Explanation
You'll need Enterprise behaviors that run on those Windows jump hosts and VPN gateways themselves, not ICS behaviors built for controllers. Data sources and mitigations won't give you anything to emulate since they tell you what to log and how to harden, not what the adversary does. Scope your library to techniques that actually touch those gateways so your findings map to real utility risk.
Full Explanation
A water utility SOC that wants emulation coverage only for techniques relevant to Windows jump hosts and VPN gateways should limit the technique library to ATT&CK behaviors that apply to that utility attack surface. Scoping keeps purple-team effort on realistic paths into operator networks, improves signal-to-noise in detections, and reduces unnecessary risk from exercising irrelevant techniques on unrelated systems. Municipal OT-adjacent estates especially need this discipline so validation stays inside authorized windows and change control.
Why the other options fail by concept: Limiting the technique library to ATT&CK ICS behaviors that target the utility’s jump-host and VPN gateway controllers uses the wrong ATT&CK domain because Windows jump hosts and VPN gateways require Enterprise techniques that execute on those assets, not ICS techniques for controllers and OT processes. Limiting the technique library to ATT&CK data sources that monitor the utility’s jump-host and VPN gateway event logs confuses telemetry with adversary behavior because data sources describe what to collect for detection, not techniques to emulate, so it does not produce an executable technique library for detection validation. Limiting the technique library to ATT&CK mitigations that harden the utility’s jump-host and VPN gateway configurations confuses defensive guidance with adversary behavior because mitigations describe how to harden, not techniques to emulate, so it does not produce an executable technique library for detection validation.
Exam caveat: surface-scoped libraries must be revisited when the utility adds new gateway types or cloud management paths; yesterday’s Windows-only map can become incomplete. Operational check: inventory jump-host and VPN gateway OS, identity, and telemetry; select ATT&CK techniques that touch those paths; run emulation only on authorized lab or gated hosts; and archive the scoped technique list with the change record for auditors.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.