
A permitting office analyzes AI system attack surface for governance review. Which inventory is most complete?
Select an answer to reveal the explanation.
Short Explanation
Attack surface for permitting AI isn’t the homepage footer. Inventory APIs, training uploads, admin consoles, and plugins—the real doors attackers care about.
Full Explanation
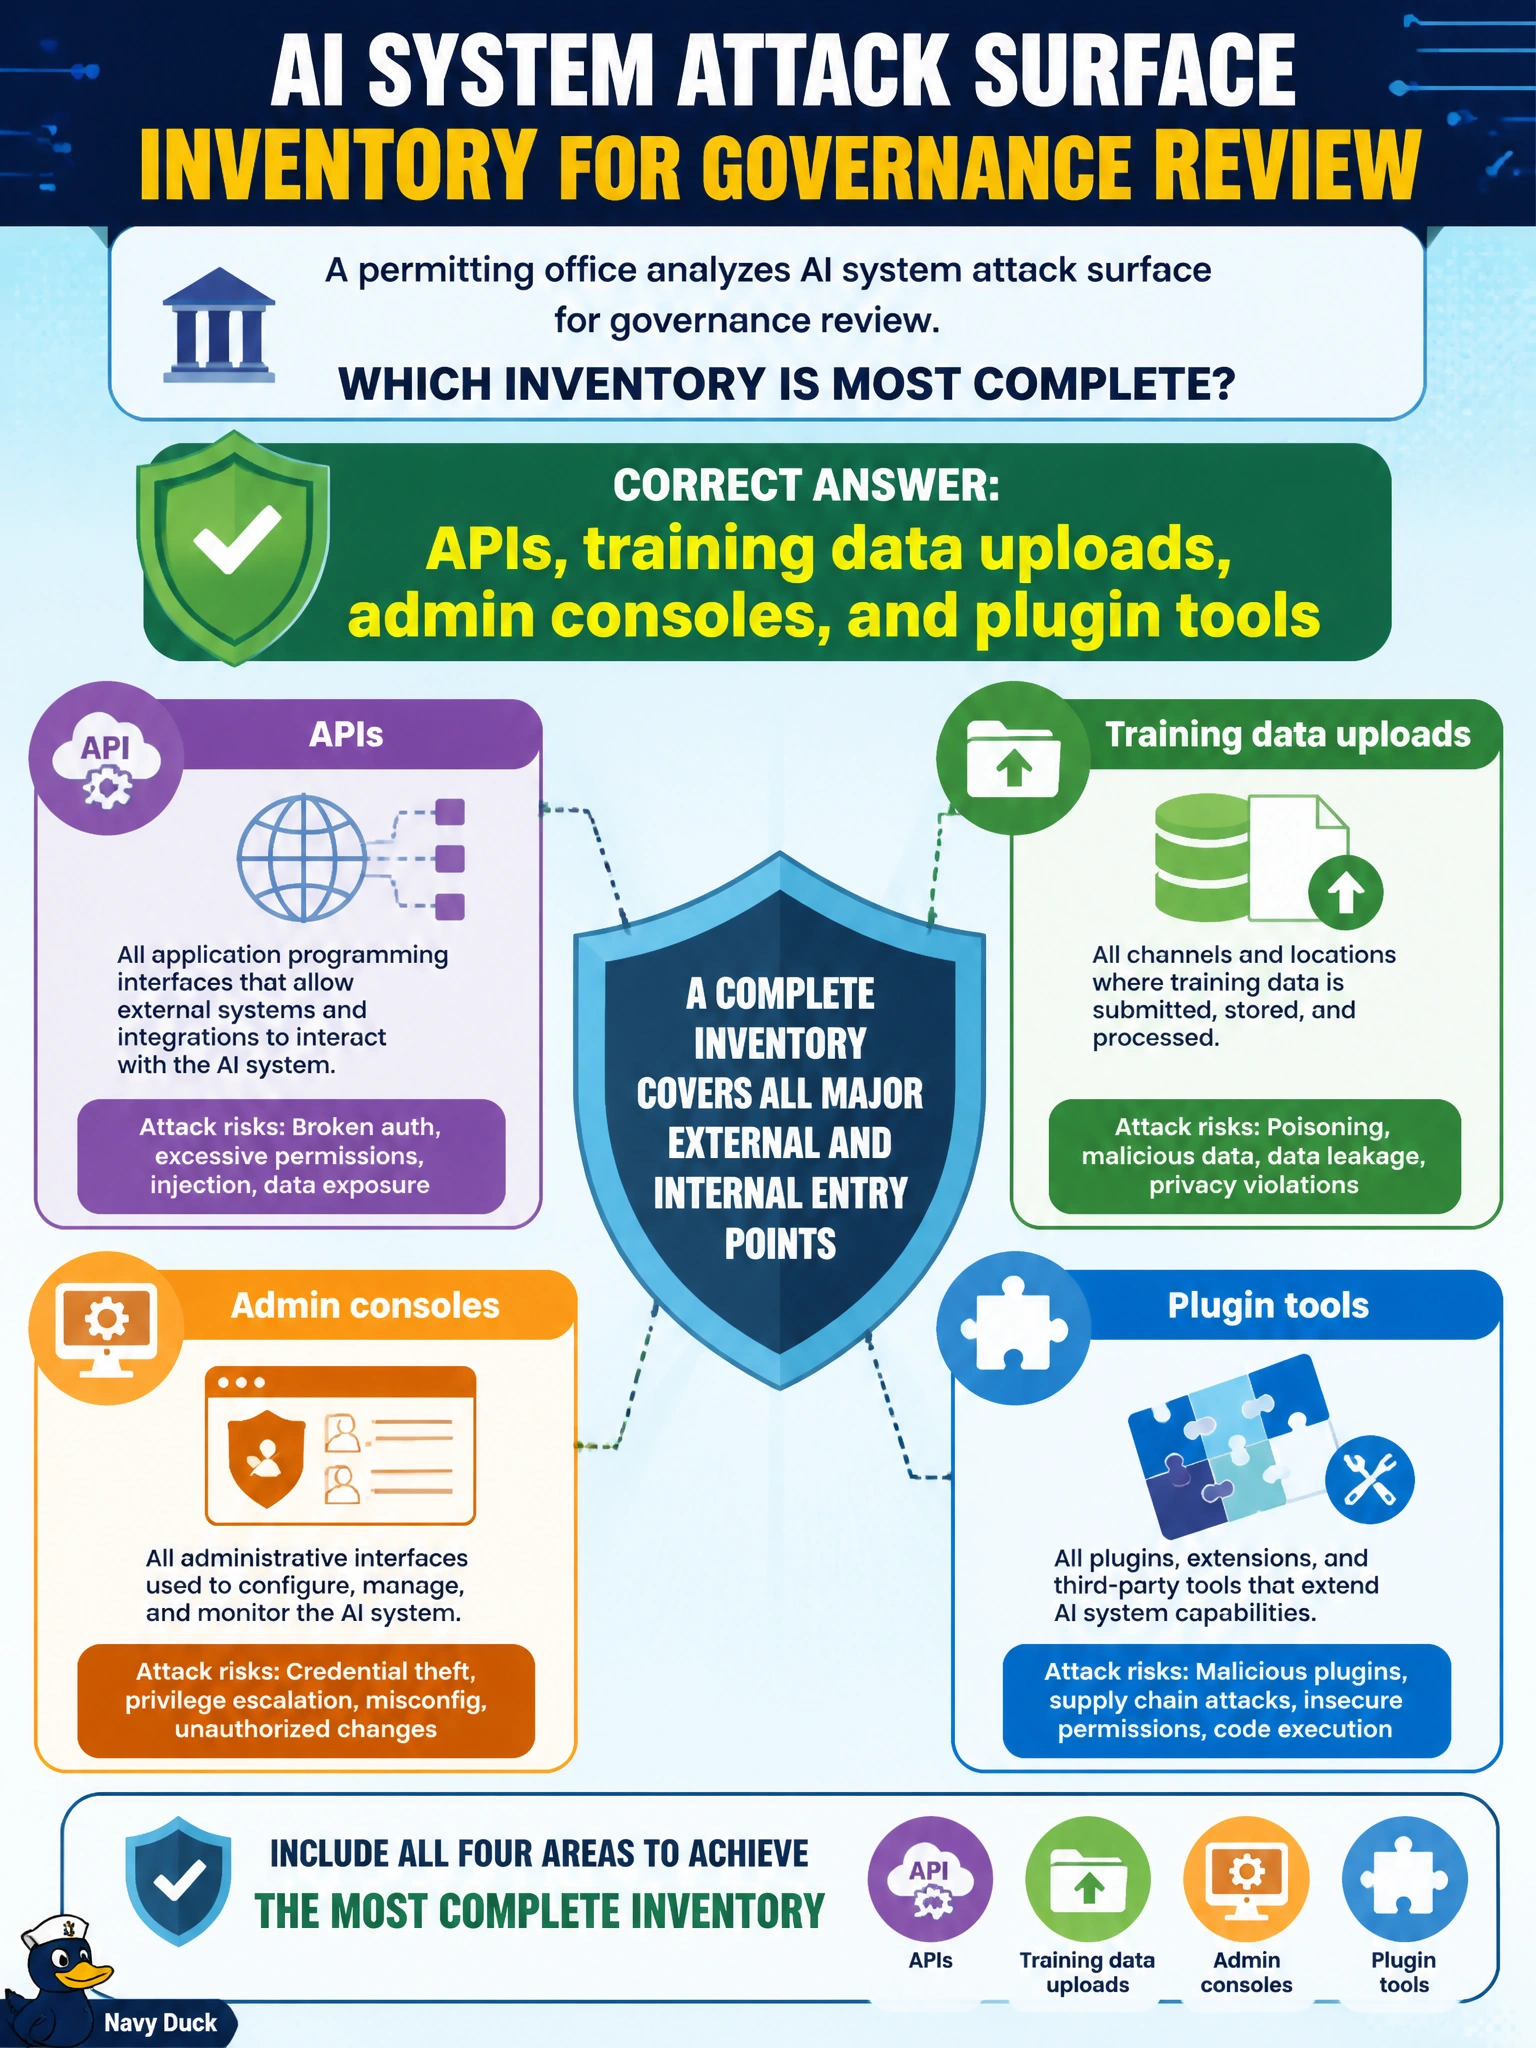
A permitting office analyzing AI system attack surface for governance review is most complete when it inventories APIs, training data uploads, admin consoles, and plugin tools. AI attack surface in municipal permitting is broader than a public webpage: model and data ingress paths, privileged administration, integration plugins, and service APIs are where integrity, privacy, and availability failures often start. A complete inventory lets governance prioritize controls on real entry points.
Inventorying only the public homepage footer links fails by concept because footers rarely expose the operational AI control plane. Inventorying only the conference booth demo laptop fails because a demo endpoint is not the production attack surface of the permitting system. Inventorying only printed user manuals with no runtime entry points fails because documentation is not an executable interface attackers or errant staff use to change models or data.
Exam caveat: plugin tools and training uploads are frequently forgotten in IT inventories focused on web apps; AI governance reviews must add them explicitly. Operational check: produce an attack-surface diagram including APIs, data-upload channels, admin consoles, and plugins; assign control owners per surface; and re-inventory after each major integration change.