
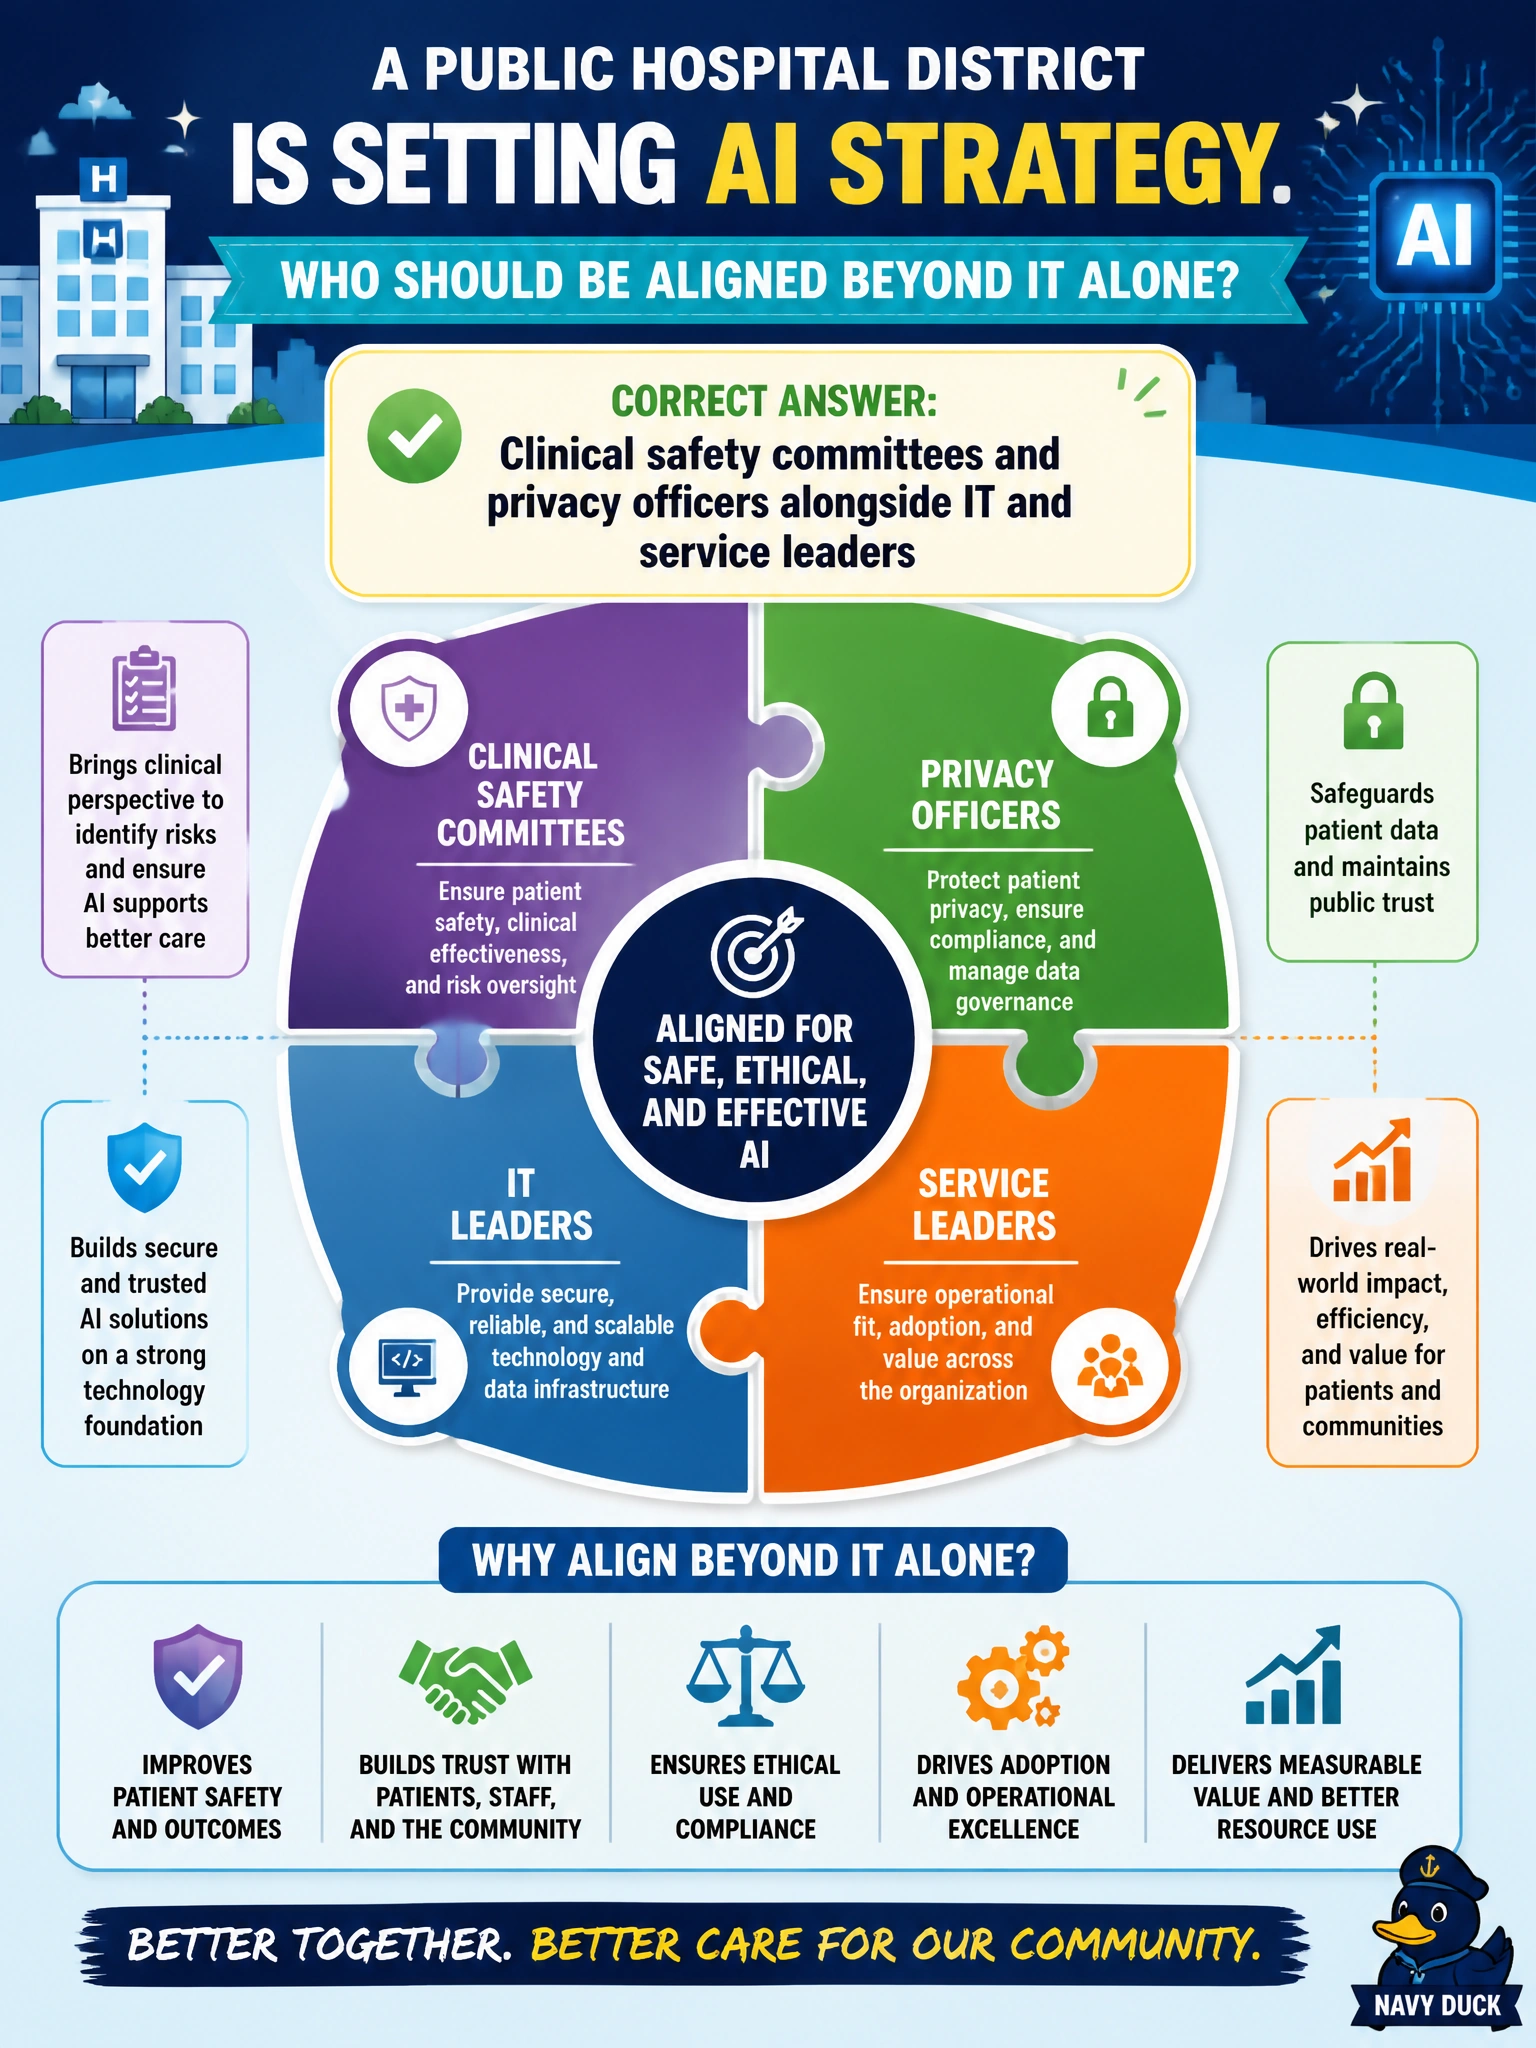
A public hospital district is setting AI strategy. Who should be aligned beyond IT alone?
Select an answer to reveal the explanation.
Short Explanation
Hospital AI isn’t an IT hobby project. Pull clinical safety and privacy into the strategy huddle with IT—or you’ll ship something clever that nobody will touch.
Full Explanation
The correct answer is aligning clinical safety committees and privacy officers alongside IT and service leaders when setting public hospital district AI strategy. Hospital AI can affect diagnosis support, documentation, patient privacy, and workflow safety. Strategy that sits only in IT misses clinical risk acceptance, HIPAA/privacy obligations, and care-team usability. Bringing safety and privacy into the same alignment forum as IT and service leaders creates shared ownership before tools reach patients or clinicians.
Only the facilities landscaping contractor fails by concept because landscaping is not a primary AI safety or privacy stakeholder for clinical systems. Only a single shadow IT enthusiast with a personal API key fails as an anti-governance pattern that bypasses controls. Only marketing, with clinical teams excluded, fails because promotional framing without clinical and privacy leadership endangers patients and compliance.
Exam caveat: cross-functional alignment—especially safety and privacy—is required in healthcare civic AI strategy items. Operational check: charter an AI governance group including clinical safety, privacy, IT, and service leads; require their sign-off on strategy and high-risk use cases; and ban shadow API-key deployments outside approved pathways.