
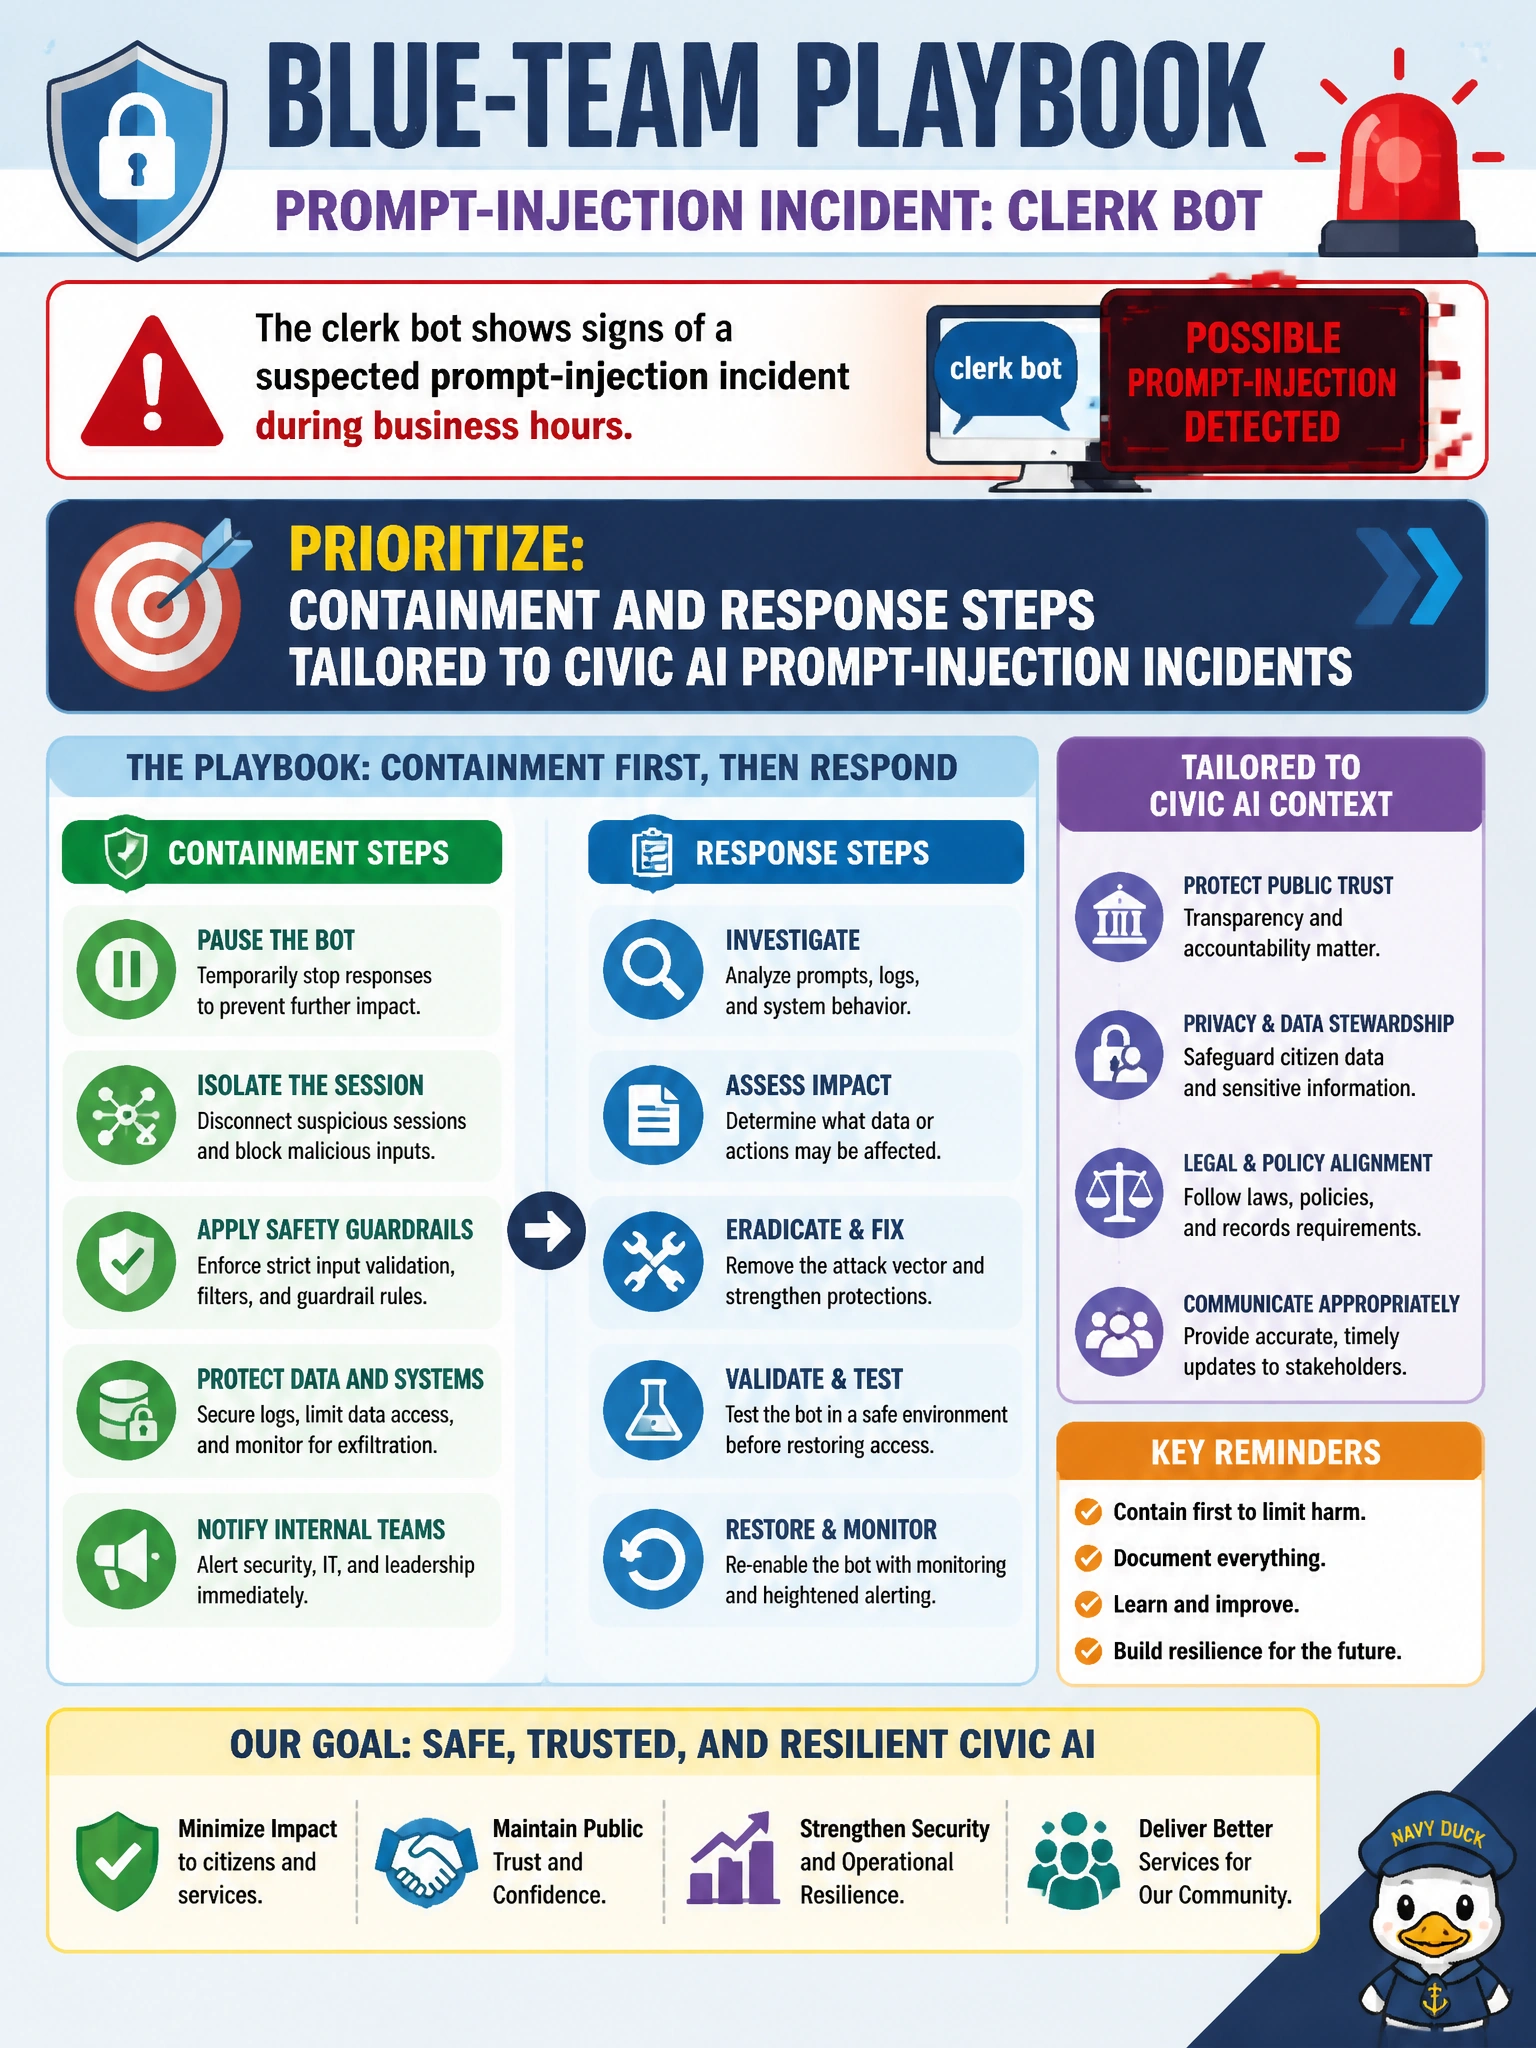
The clerk bot shows signs of a suspected prompt-injection incident during business hours. What should the blue-team playbook prioritize?
Select an answer to reveal the explanation.
Short Explanation
Suspected prompt injection isn’t a “restore from backup and move on” shrug—contain, preserve evidence, then restore service. A quick snapshot restore isn’t an IR playbook.
Full Explanation
When the clerk bot shows signs of a suspected prompt-injection incident during business hours, the blue-team playbook should prioritize containment and response steps tailored to civic AI prompt-injection incidents. Tailored steps typically include throttling or isolating the assistant, preserving prompts, outputs, tool traces, and model/config versions as evidence, rotating or suspending risky tool credentials, notifying privacy/legal if resident data may be exposed, and restoring service only after integrity checks—not simply restoring from the most recent clean backup snapshot, which can return compromised service without containing the injection or preserving forensic evidence. Prompt injection against a clerk assistant can manipulate retrieval, leak records, or cause unauthorized tool actions while the process still looks like normal chat traffic; AI-specific playbooks prevent under-response. Municipal blue teams need these runbooks rehearsed because business-hours incidents also require public communications discipline and continuity for clerk services. Standard email phishing containment procedures for affected corporate staff workstations are built for endpoint malware and stolen credentials, not for a civic AI prompt-injection incident already underway, so they don't tell responders how to contain the clerk bot or preserve model evidence. Restoring the chatbot service from the most recent clean backup snapshot is the generic availability-first response the playbook specifically needs to avoid—it restores service without containing the actual injection or preserving forensic evidence. Tuning chatbot response tone and updating civic FAQ content libraries is a content-maintenance task, not incident response—it does not contain the active injection, preserve the forensic trail, or confirm whether any unauthorized tool action already occurred. The playbook has to prioritize AI-specific containment and evidence preservation, not a restore-from-snapshot shortcut or routine content tuning. Exam caveat: generic malware IR steps may be offered as distractors; when the stem specifies prompt injection on a civic assistant, prefer AI-tailored containment and evidence steps. Operational check: execute a tabletop of clerk-bot injection, verify responders can disable or isolate the bot quickly, collect prompt/tool/model evidence under chain-of-custody, and document communications to privacy and clerk leadership within the playbook SLA.