
A new operator joins the team on Monday. The team lead asks why adding one person to the backup appliance needs a change ticket to the storage group, when the equivalent for every other system in the building is handled by the directory. What should have been configured to make that question legitimate?
Select an answer to reveal the explanation.
Short Explanation
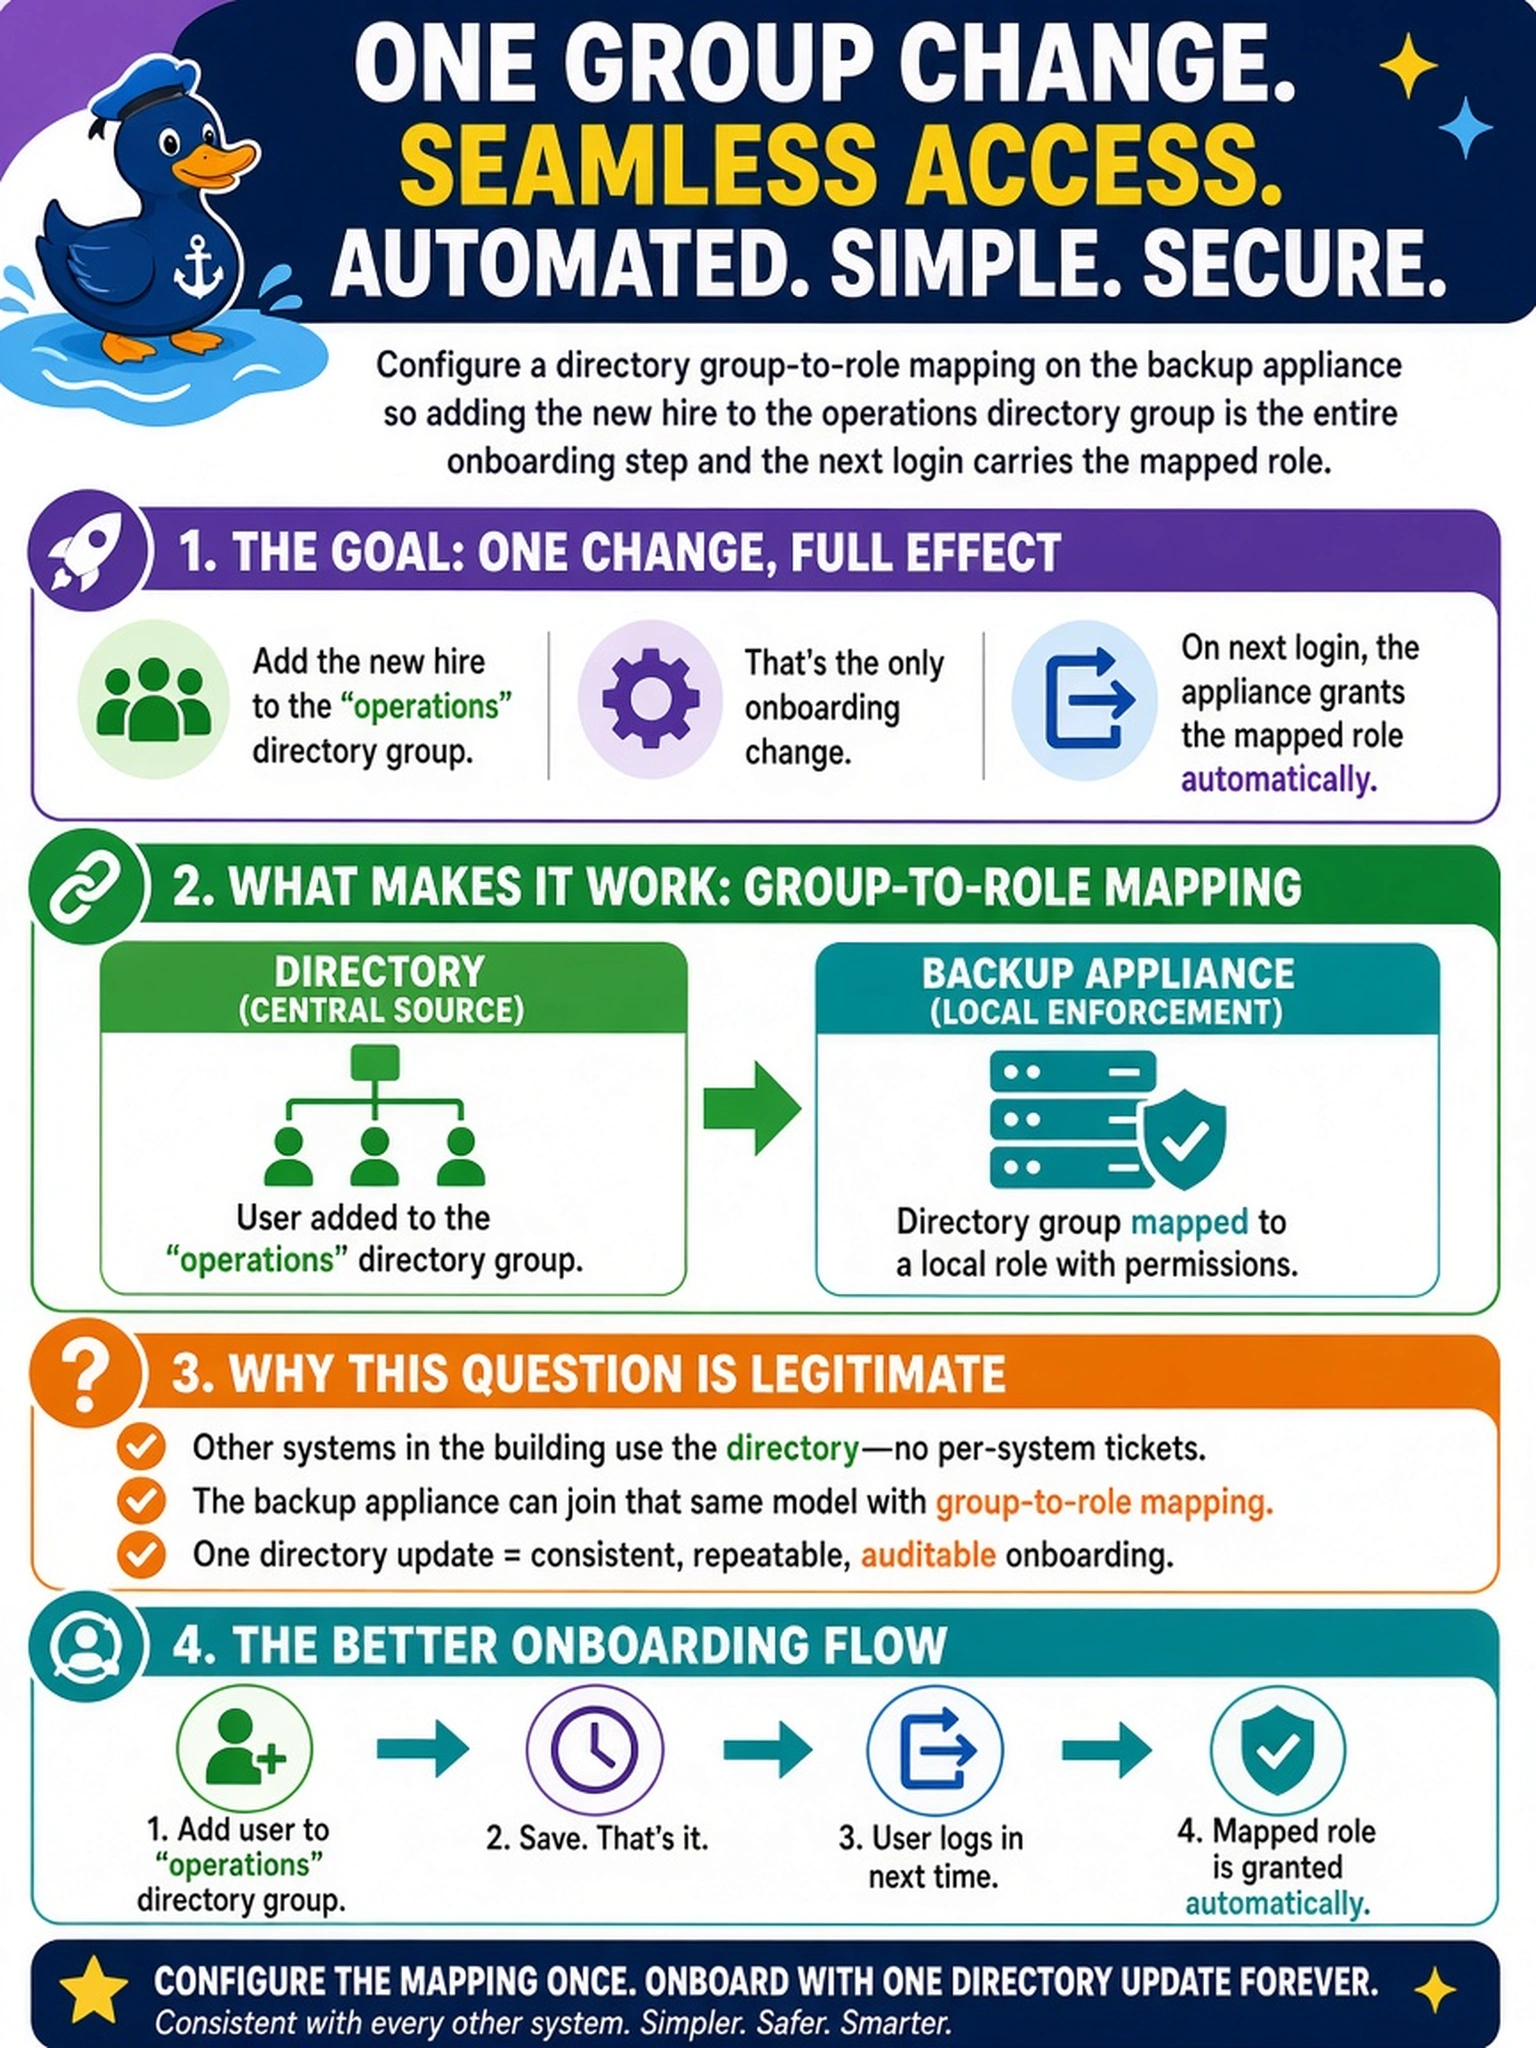
If the directory runs every other system, the appliance should too: map the operations group to a role once, and onboarding becomes one person, one group, done. You stop provisioning humans one appliance at a time - and departures clean themselves up. That change ticket you're dreading is just a configuration gap wearing a process uniform.
Full Explanation
An appliance that needs its own ticket per hire has been left in standalone identity mode: DD OS directory integration can map a named directory group to an appliance role, so the whole onboarding step becomes adding the new operator to the operations group in the directory, with the next login carrying the mapped authority. The appliance enforces the decision while the directory owns it - the same operating model the rest of the estate already runs on, which is why the team lead's question stings. A pre-provisioned pool of local accounts reintroduces device-local credential lifecycle - issuance, custody, rotation, revocation on departure - and quietly hands out unclaimed accounts that blur attribution from day one. A shared operations login is the accountability poison this objective keeps returning to: onboarding friction avoided by merging identities is precisely the finding later audits cannot forgive, and every change loses its name. A runbook script that creates local accounts per ticket automates the wrong model - per-appliance identity provisioning is the very thing directory mapping exists to delete, and each scripted local account is another secret to guard. Exam caveat: group-to-role mapping makes directory group hygiene security-relevant, since the mapping inherits whatever membership discipline the group owners keep. Operational check: add a test user to the mapped group, have that user log in, and confirm the granted role matches the mapping and nothing wider.