
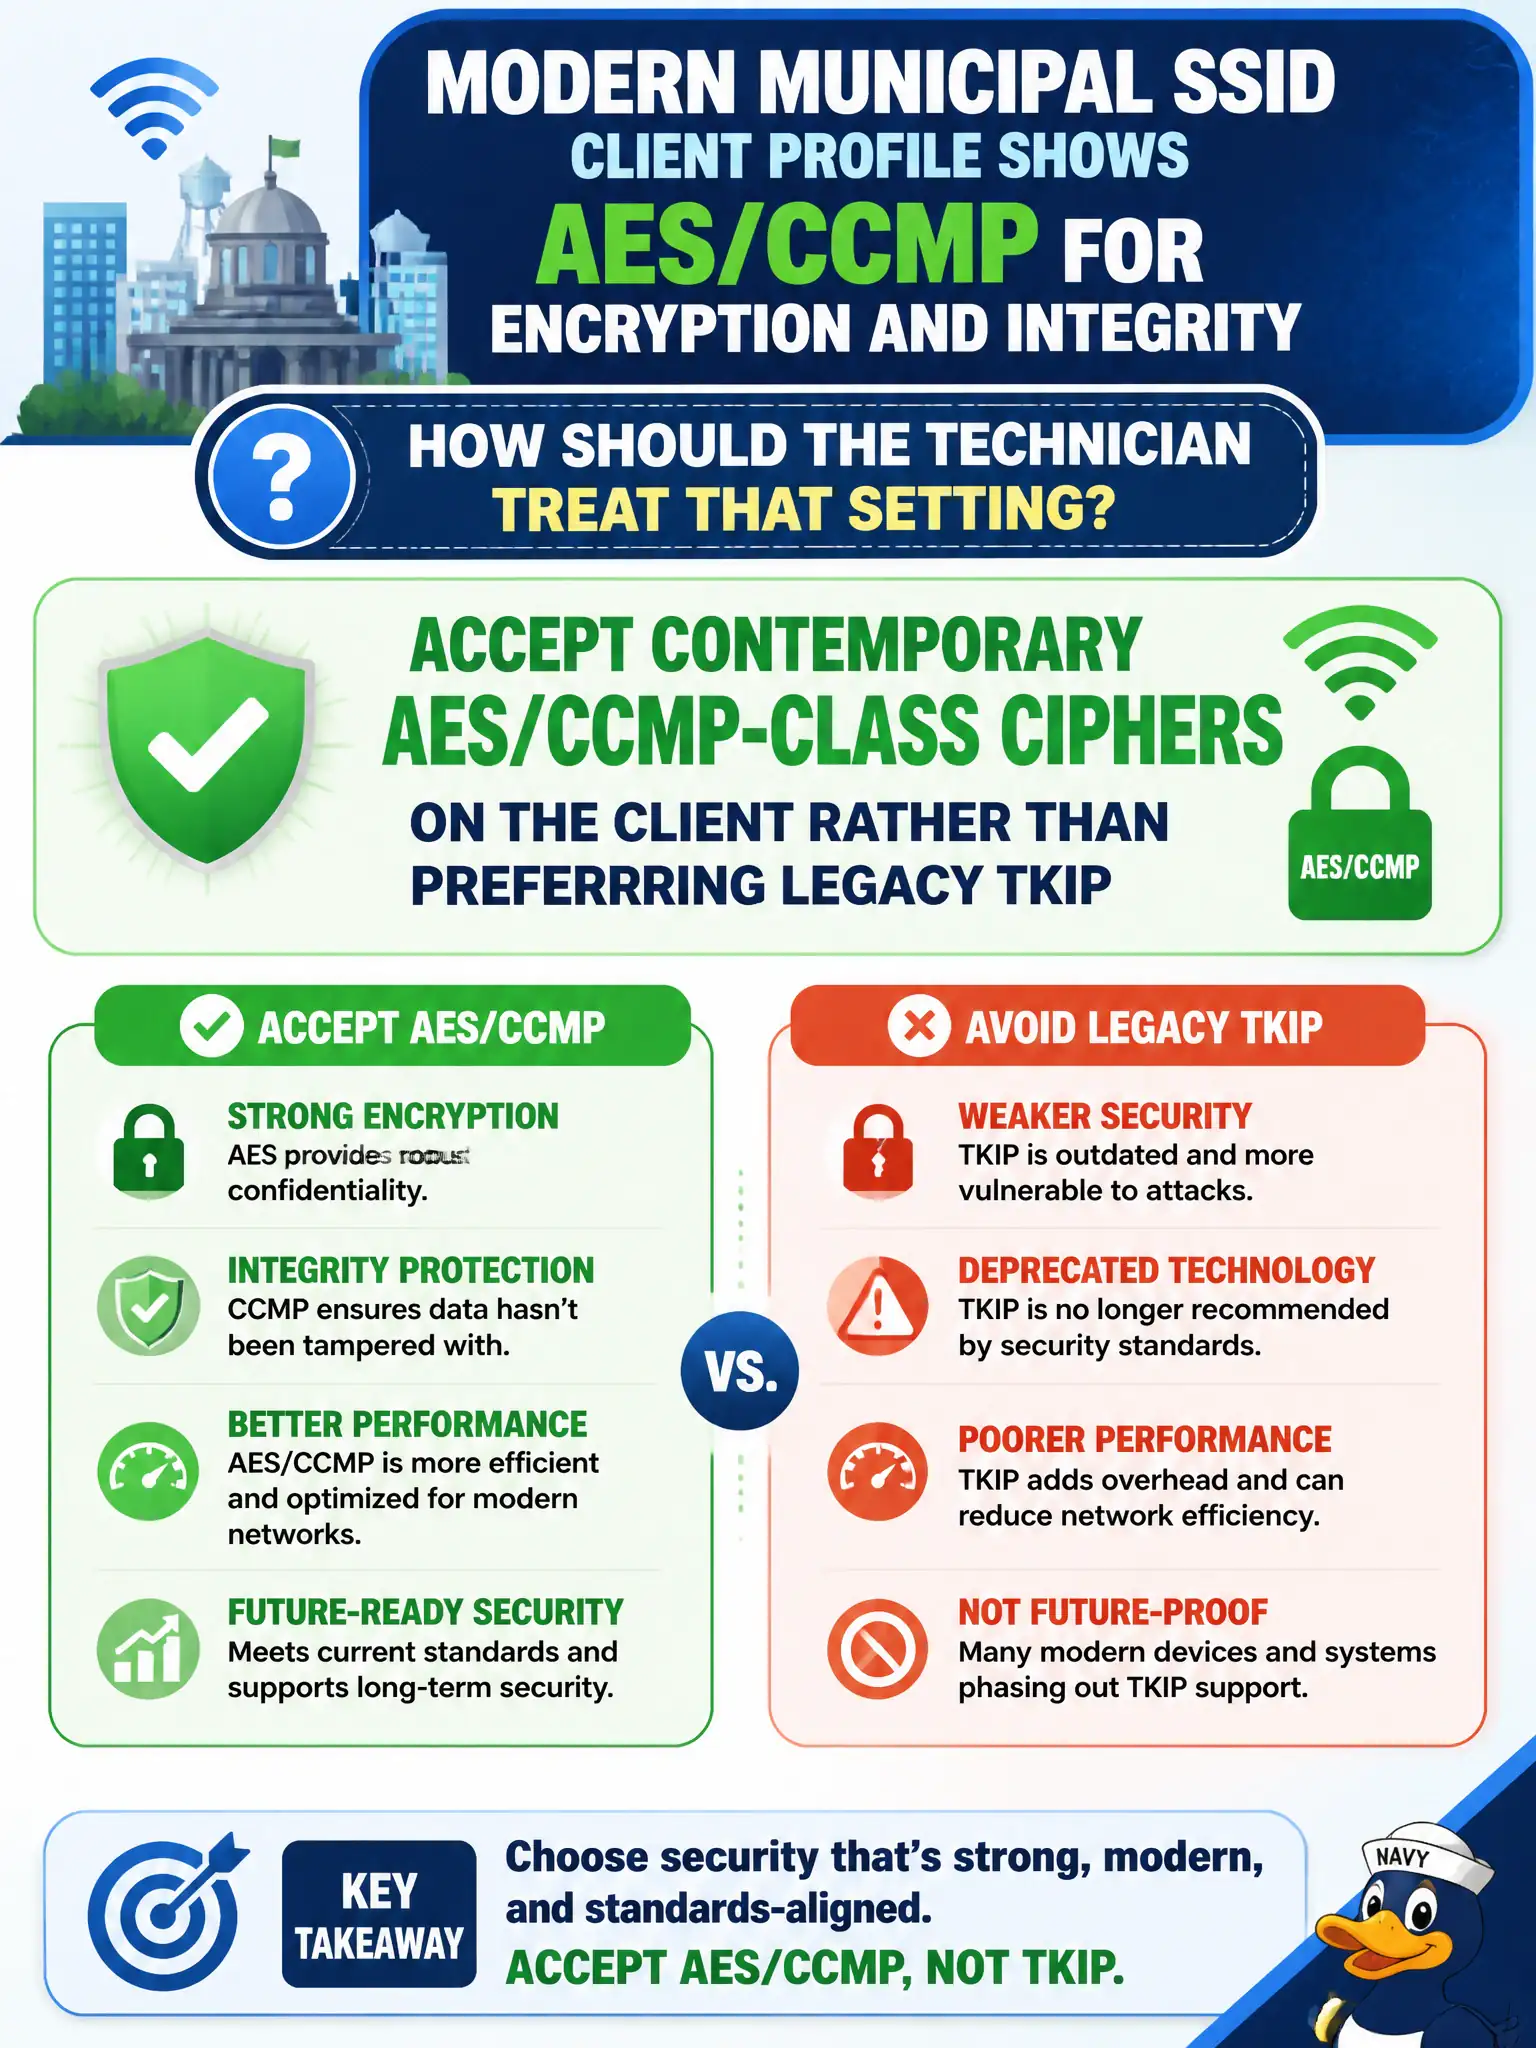
A modern municipal SSID's client profile shows AES/CCMP for encryption and integrity. How should the technician treat that setting?
Select an answer to reveal the explanation.
Short Explanation
AES/CCMP is the modern padlock—leave it on. Dragging the city back to TKIP or WEP for one dusty scanner is the wrong default. MAC lists aren't integrity crypto.
Full Explanation
When a modern municipal SSID's client profile shows AES/CCMP for encryption and integrity, technicians should accept contemporary AES/CCMP-class ciphers on the client rather than preferring legacy TKIP. CCMP based on AES is the expected pairwise cipher for WPA2 and remains central in WPA3 transitions; it provides confidentiality and integrity suited to city staff and guest traffic. Client profiles should not cling to TKIP when the BSS and policy advertise stronger ciphers.
Preferring TKIP because it is 'compatible with everything' reintroduces deprecated cryptography and can force mixed-mode weaknesses on civic WLANs. Disabling all encryption so only MAC filtering remains removes frame protection entirely. Selecting WEP key indexes as the modern integrity choice contradicts current municipal hardening guidance and CWT expectations for contemporary client cipher selection.
Exam caveat: recognize AES/CCMP as the correct modern client cipher posture versus TKIP/WEP nostalgia distractors. Operational check: inspect a connected city laptop's link status or driver details for CCMP/AES, confirm the profile is not set to TKIP-only, and remediate any mixed-mode SSID still advertising TKIP for staff.