
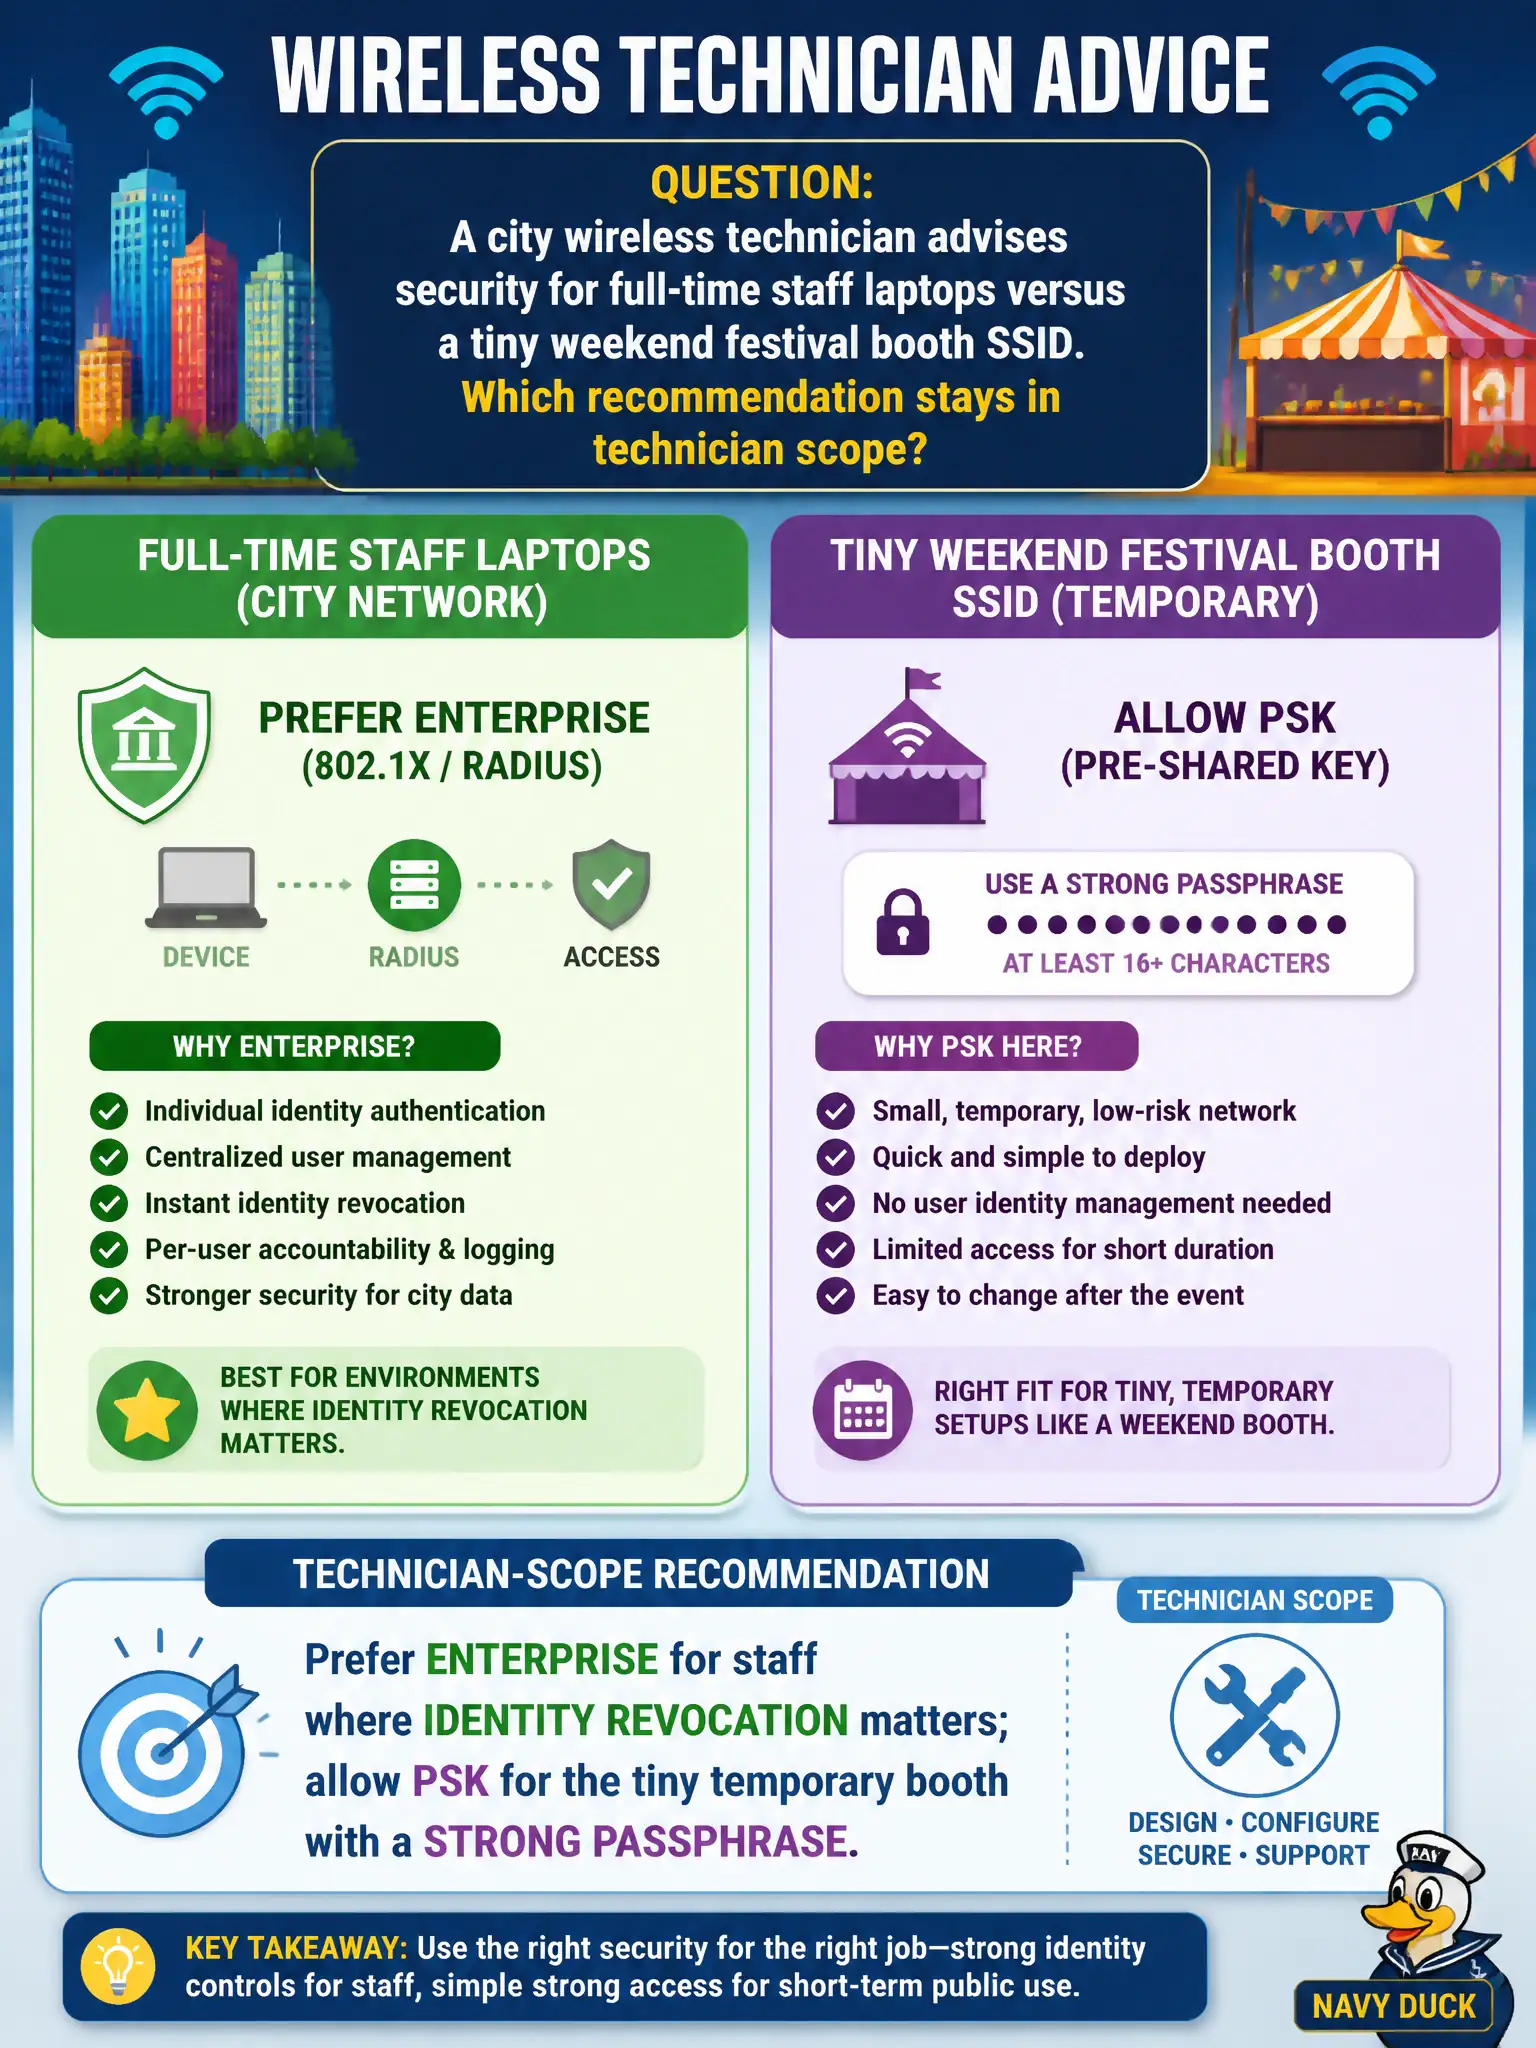
A city wireless technician advises security for full-time staff laptops versus a tiny weekend festival booth SSID. Which recommendation stays in technician scope?
Select an answer to reveal the explanation.
Short Explanation
Staff who need offboarding get Enterprise; a weekend booth can live on a strong PSK. One weak key for everyone is lazy and risky. You don't need a full WIPS design just to pick Personal versus Enterprise.
Full Explanation
Municipal wireless design should prefer Enterprise for full-time staff laptops where identity, accounting, and credential revocation matter, while allowing PSK/Personal for a tiny temporary event network that intentionally shares one passphrase. Staff devices need per-user or per-device 802.1X so a departing employee can be disabled in directory without rotating a citywide PSK. A weekend festival guest SSID with a short lifespan may accept Personal mode for operational simplicity when policy explicitly permits it.
Applying one citywide PSK to every permanent staff laptop undermines revocation and auditability that Enterprise provides. Forcing Enterprise certificates onto a one-day pop-up kiosk SSID that was designed as Personal adds complexity without matching the temporary use case. Open authentication for all staff traffic because 'government networks are trusted' abandons encryption and identity controls the city requires for finance and HR laptops.
Exam caveat: choose security mode from identity and lifecycle needs, not from a blanket rule that government always means Enterprise or always means PSK. Operational check: document which civic SSIDs are Enterprise versus Personal, verify staff laptops use Enterprise profiles with working RADIUS, and ensure temporary event PSKs are rotated or retired when the event ends.