
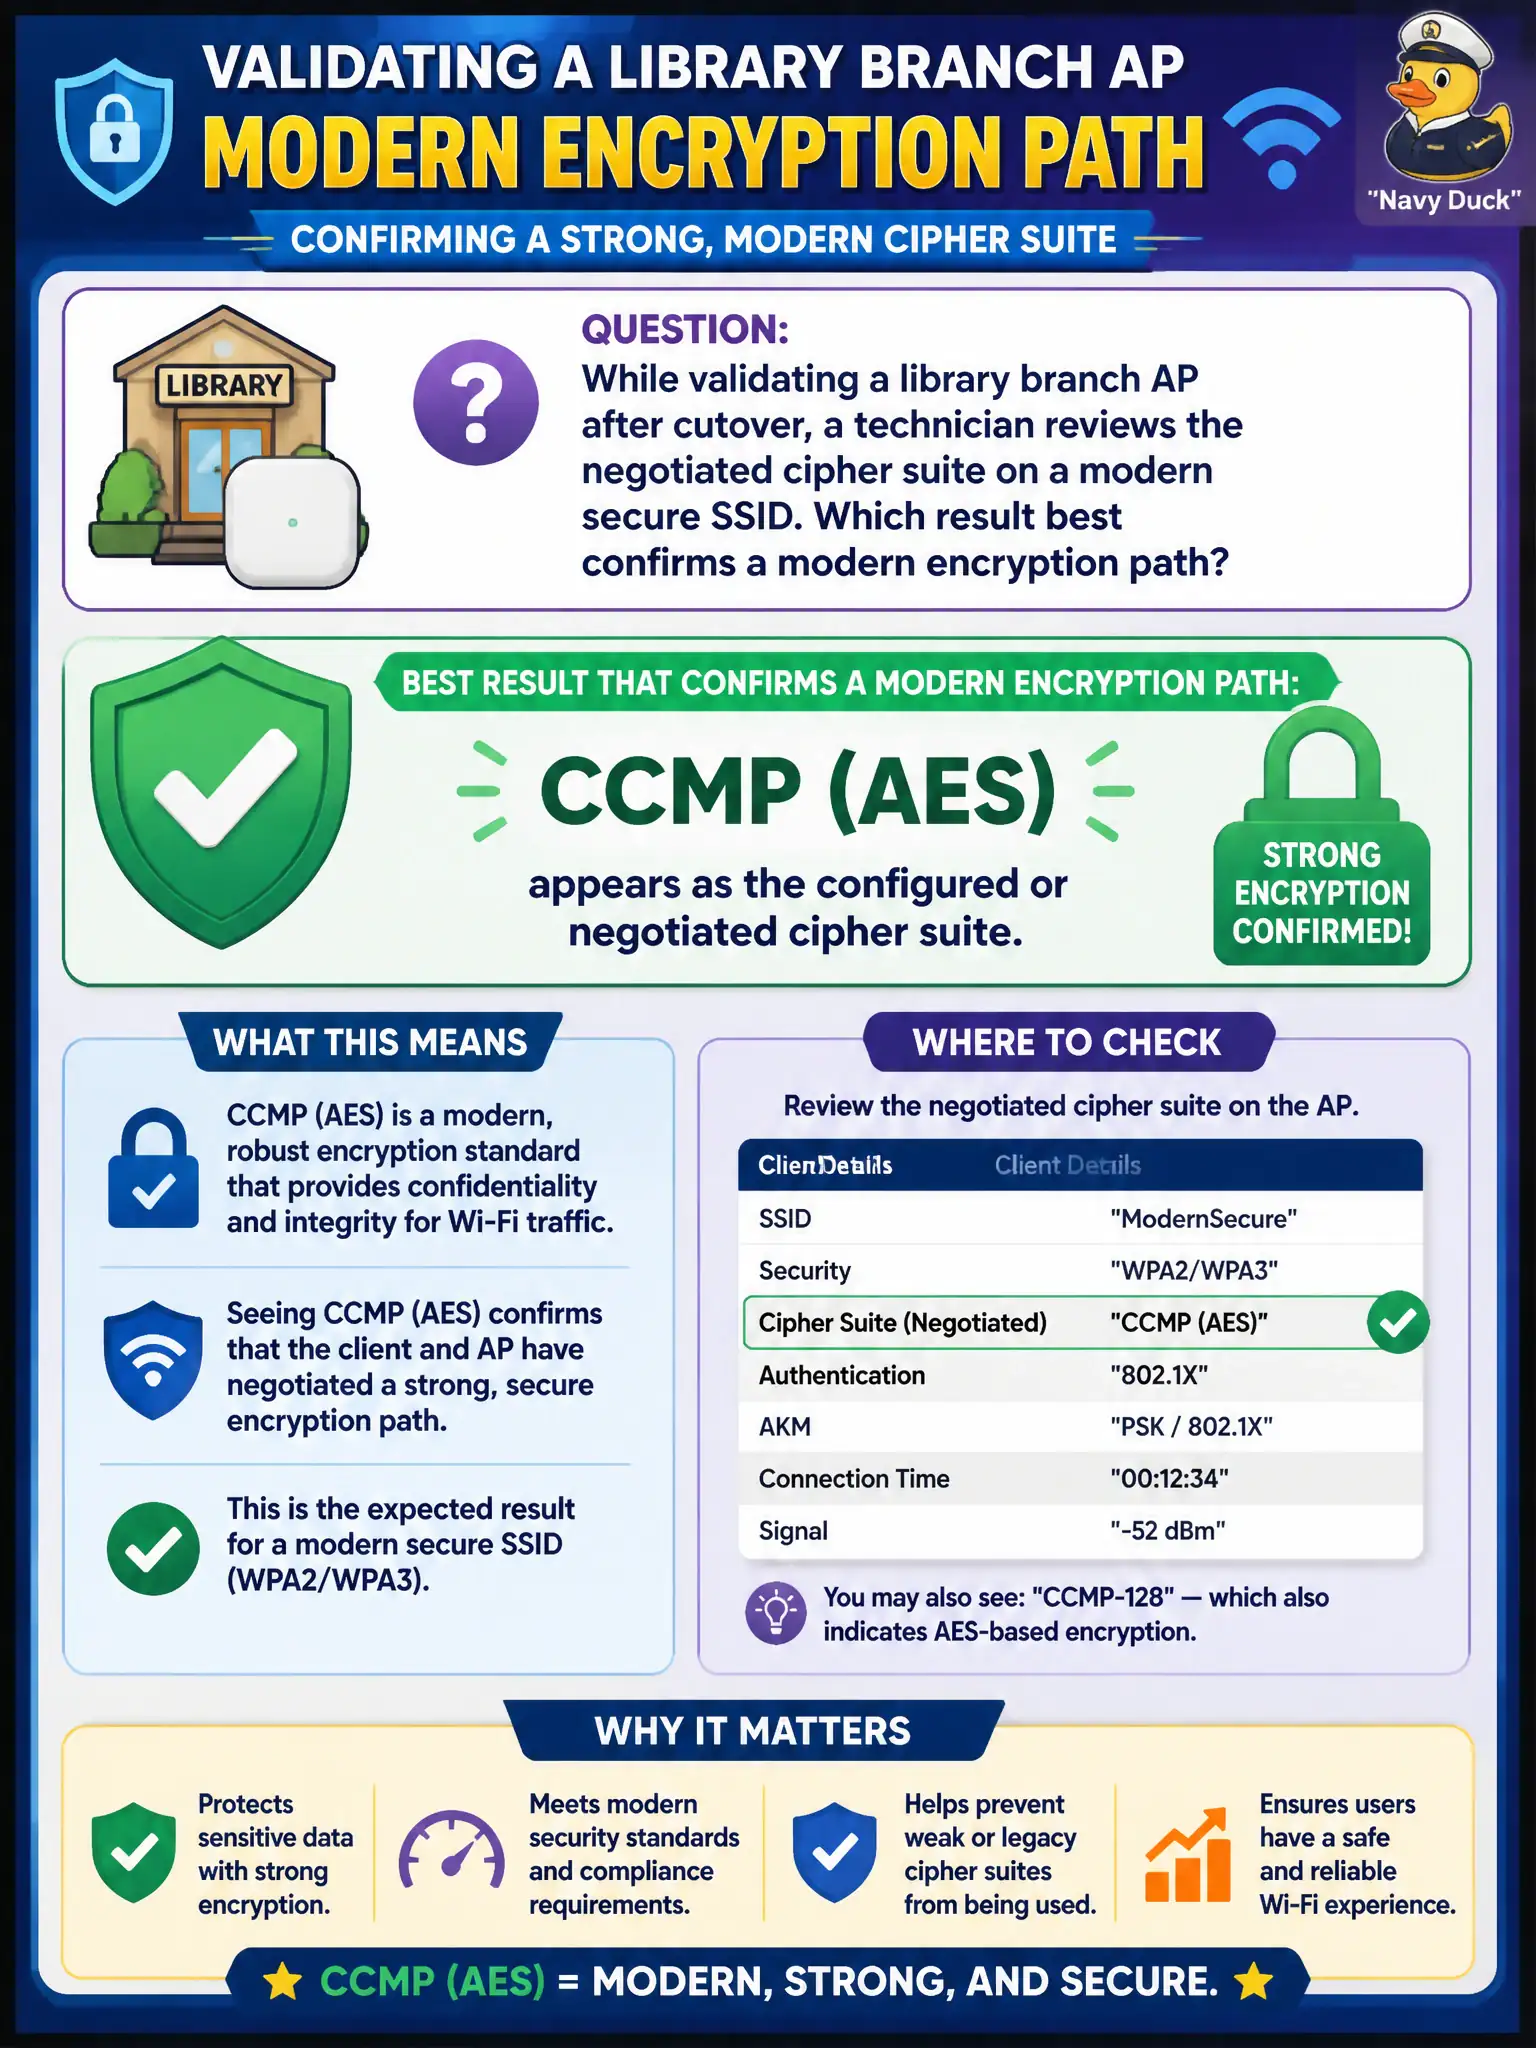
While validating a library branch AP after cutover, a technician reviews the negotiated cipher suite on a modern secure SSID. Which result best confirms a modern encryption path?
Select an answer to reveal the explanation.
Short Explanation
CCMP/AES is the green check for modern Wi-Fi encryption. If the suite is still shouting WEP or TKIP-only, the modern path is not actually in play—MAC filtering is not a cipher.
Full Explanation
While validating a library-branch AP after cutover, seeing CCMP (AES) as the configured or negotiated cipher suite best confirms a modern encryption path. CWTS-level verification looks for AES-class pairwise ciphers rather than legacy WEP or TKIP-only outcomes. A municipal secure SSID that actually lands on CCMP/AES demonstrates that modern cipher policy is in effect for associated clients.
Only WEP-40 listed as the pairwise cipher fails the modern path because WEP is obsolete and insecure. TKIP as the sole cipher with no CCMP/AES option fails by concept: TKIP is a legacy transitional cipher, not the modern AES baseline municipal designs expect. Showing no cipher because MAC filtering replaced encryption fails because MAC filtering is not encryption and cannot substitute for a cipher suite on a secure civic SSID.
Exam caveat: cipher suite evidence beats marketing labels. An SSID named “Secure” that negotiates WEP or TKIP-only is not modern encryption in practice.
Operational check: associate a test laptop to the library staff or secure SSID; inspect connection details or AP client stats for CCMP/AES; escalate if WEP or TKIP-only appears; record the cipher check in the cutover validation notes.