
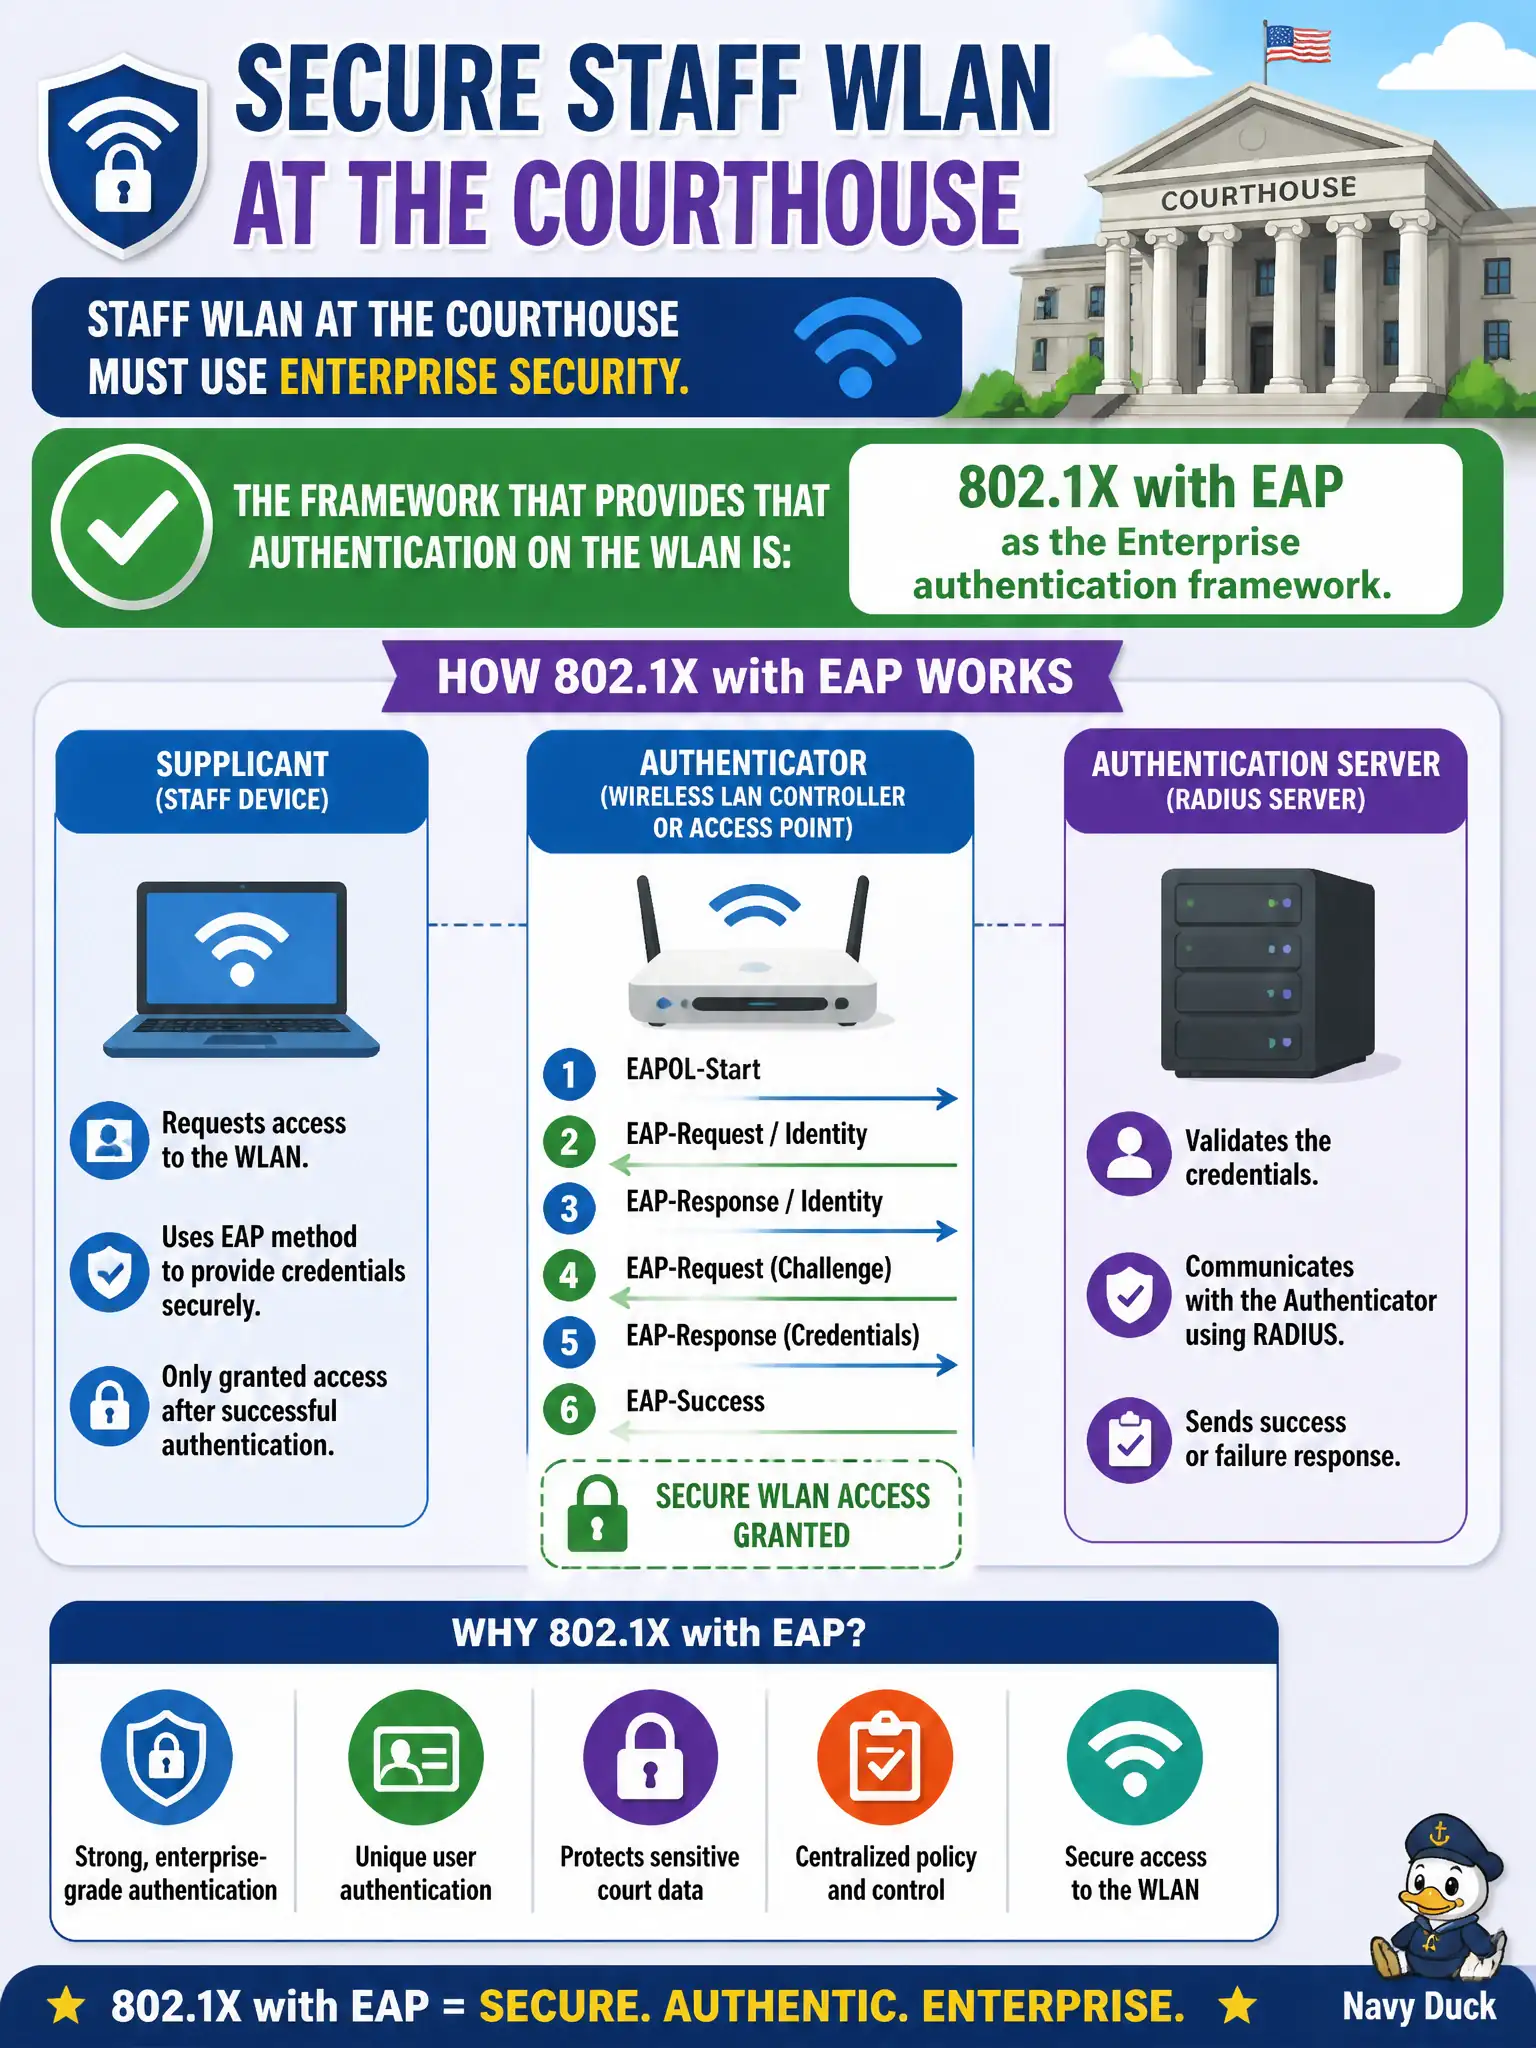
Staff WLAN at the courthouse must use Enterprise security. Which framework provides that authentication on the WLAN?
Select an answer to reveal the explanation.
Short Explanation
Enterprise Wi-Fi needs a real ID check at the door: 802.1X with EAP. A captive portal, a group PSK, or a MAC list from the badge printer is not that framework.
Full Explanation
Staff WLAN at the courthouse that must use Enterprise security relies on 802.1X with EAP as the Enterprise authentication framework. That framework delivers per-user (or per-machine) credentials via EAP methods into WPA2/WPA3-Enterprise, supporting accountability for court staff devices. Recognizing 802.1X/EAP is foundational CWTS Enterprise literacy.
Captive-portal only with a shared guest password for employees is a guest workflow, not staff Enterprise auth. PSK Personal mode with a twenty-character departmental passphrase remains shared-secret Personal security. MAC filtering synchronized from a badge printer’s DHCP table is spoofable and not Enterprise authentication.
Exam caveat: Enterprise WLAN authentication framework = 802.1X with EAP—not portals, PSKs, or MAC lists.
Operational check: configure the courthouse staff SSID for WPA2/WPA3-Enterprise using 802.1X/EAP against the city RADIUS, test a named user, and verify guest portal SSIDs remain separate. Municipal technicians document the verified setting in the as-built packet so the next shift inherits a known-good civic configuration rather than tribal knowledge. Municipal technicians document the verified setting in the as-built packet so the next shift inherits a known-good civic configuration rather than tribal knowledge.