
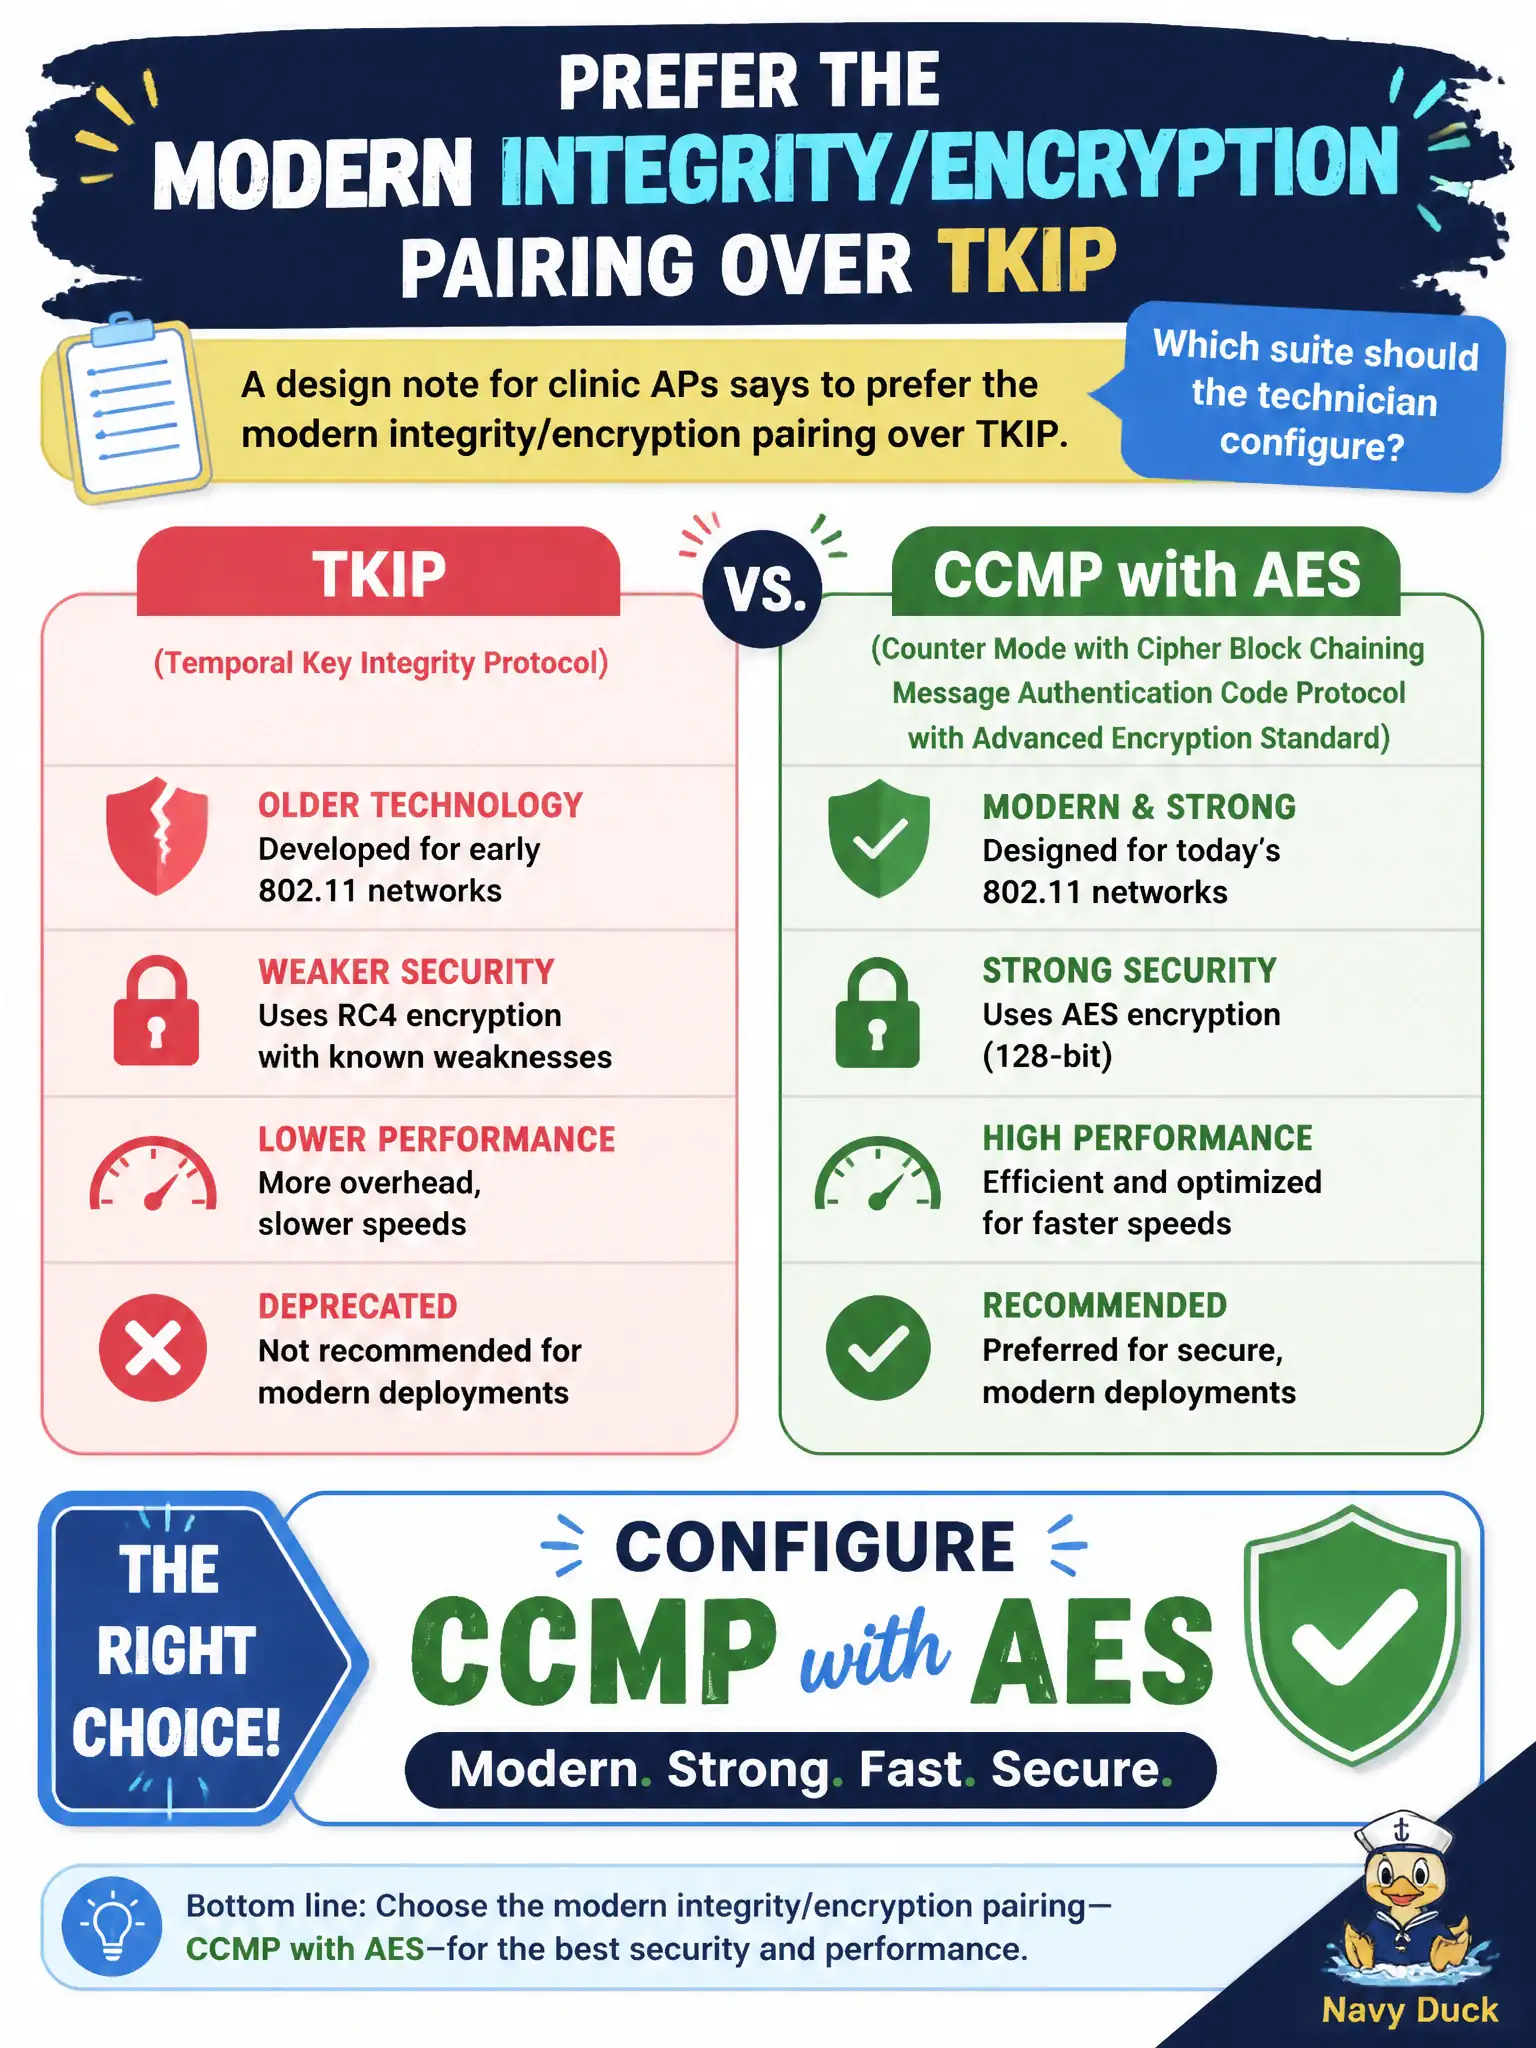
A design note for clinic APs says to prefer the modern integrity/encryption pairing over TKIP. Which suite should the technician configure?
Select an answer to reveal the explanation.
Short Explanation
When the design says "modern pairing," it means CCMP with AES—the sturdy lockset—not WEP, not TKIP's old integrity kludge, and not hoping every laptop runs its own VPN.
Full Explanation
Design notes for clinic APs that say to prefer the modern integrity/encryption pairing over TKIP are pointing at CCMP with AES. CCMP/AES is the standard robust security network cipher suite replacing TKIP’s transitional design. Configuring it on municipal clinic SSIDs aligns install work with current security baselines.
WEP with dynamic 104-bit keys remains broken legacy crypto. TKIP with Michael integrity checks only is the deprecated pairing being replaced. Open System with optional IPsec on each laptop pushes protection to ad-hoc host VPN and skips WLAN RSN cipher requirements.
Exam caveat: modern integrity/encryption pairing = CCMP/AES, not WEP, TKIP/Michael, or per-laptop IPsec substitutes.
Operational check: set clinic SSIDs to CCMP/AES under WPA2/WPA3, confirm TKIP/WEP are disabled, test clinical workstation association, and screenshot the cipher suite for the clinic security file. Municipal technicians document the verified setting in the as-built packet so the next shift inherits a known-good civic configuration rather than tribal knowledge. Municipal technicians document the verified setting in the as-built packet so the next shift inherits a known-good civic configuration rather than tribal knowledge.