
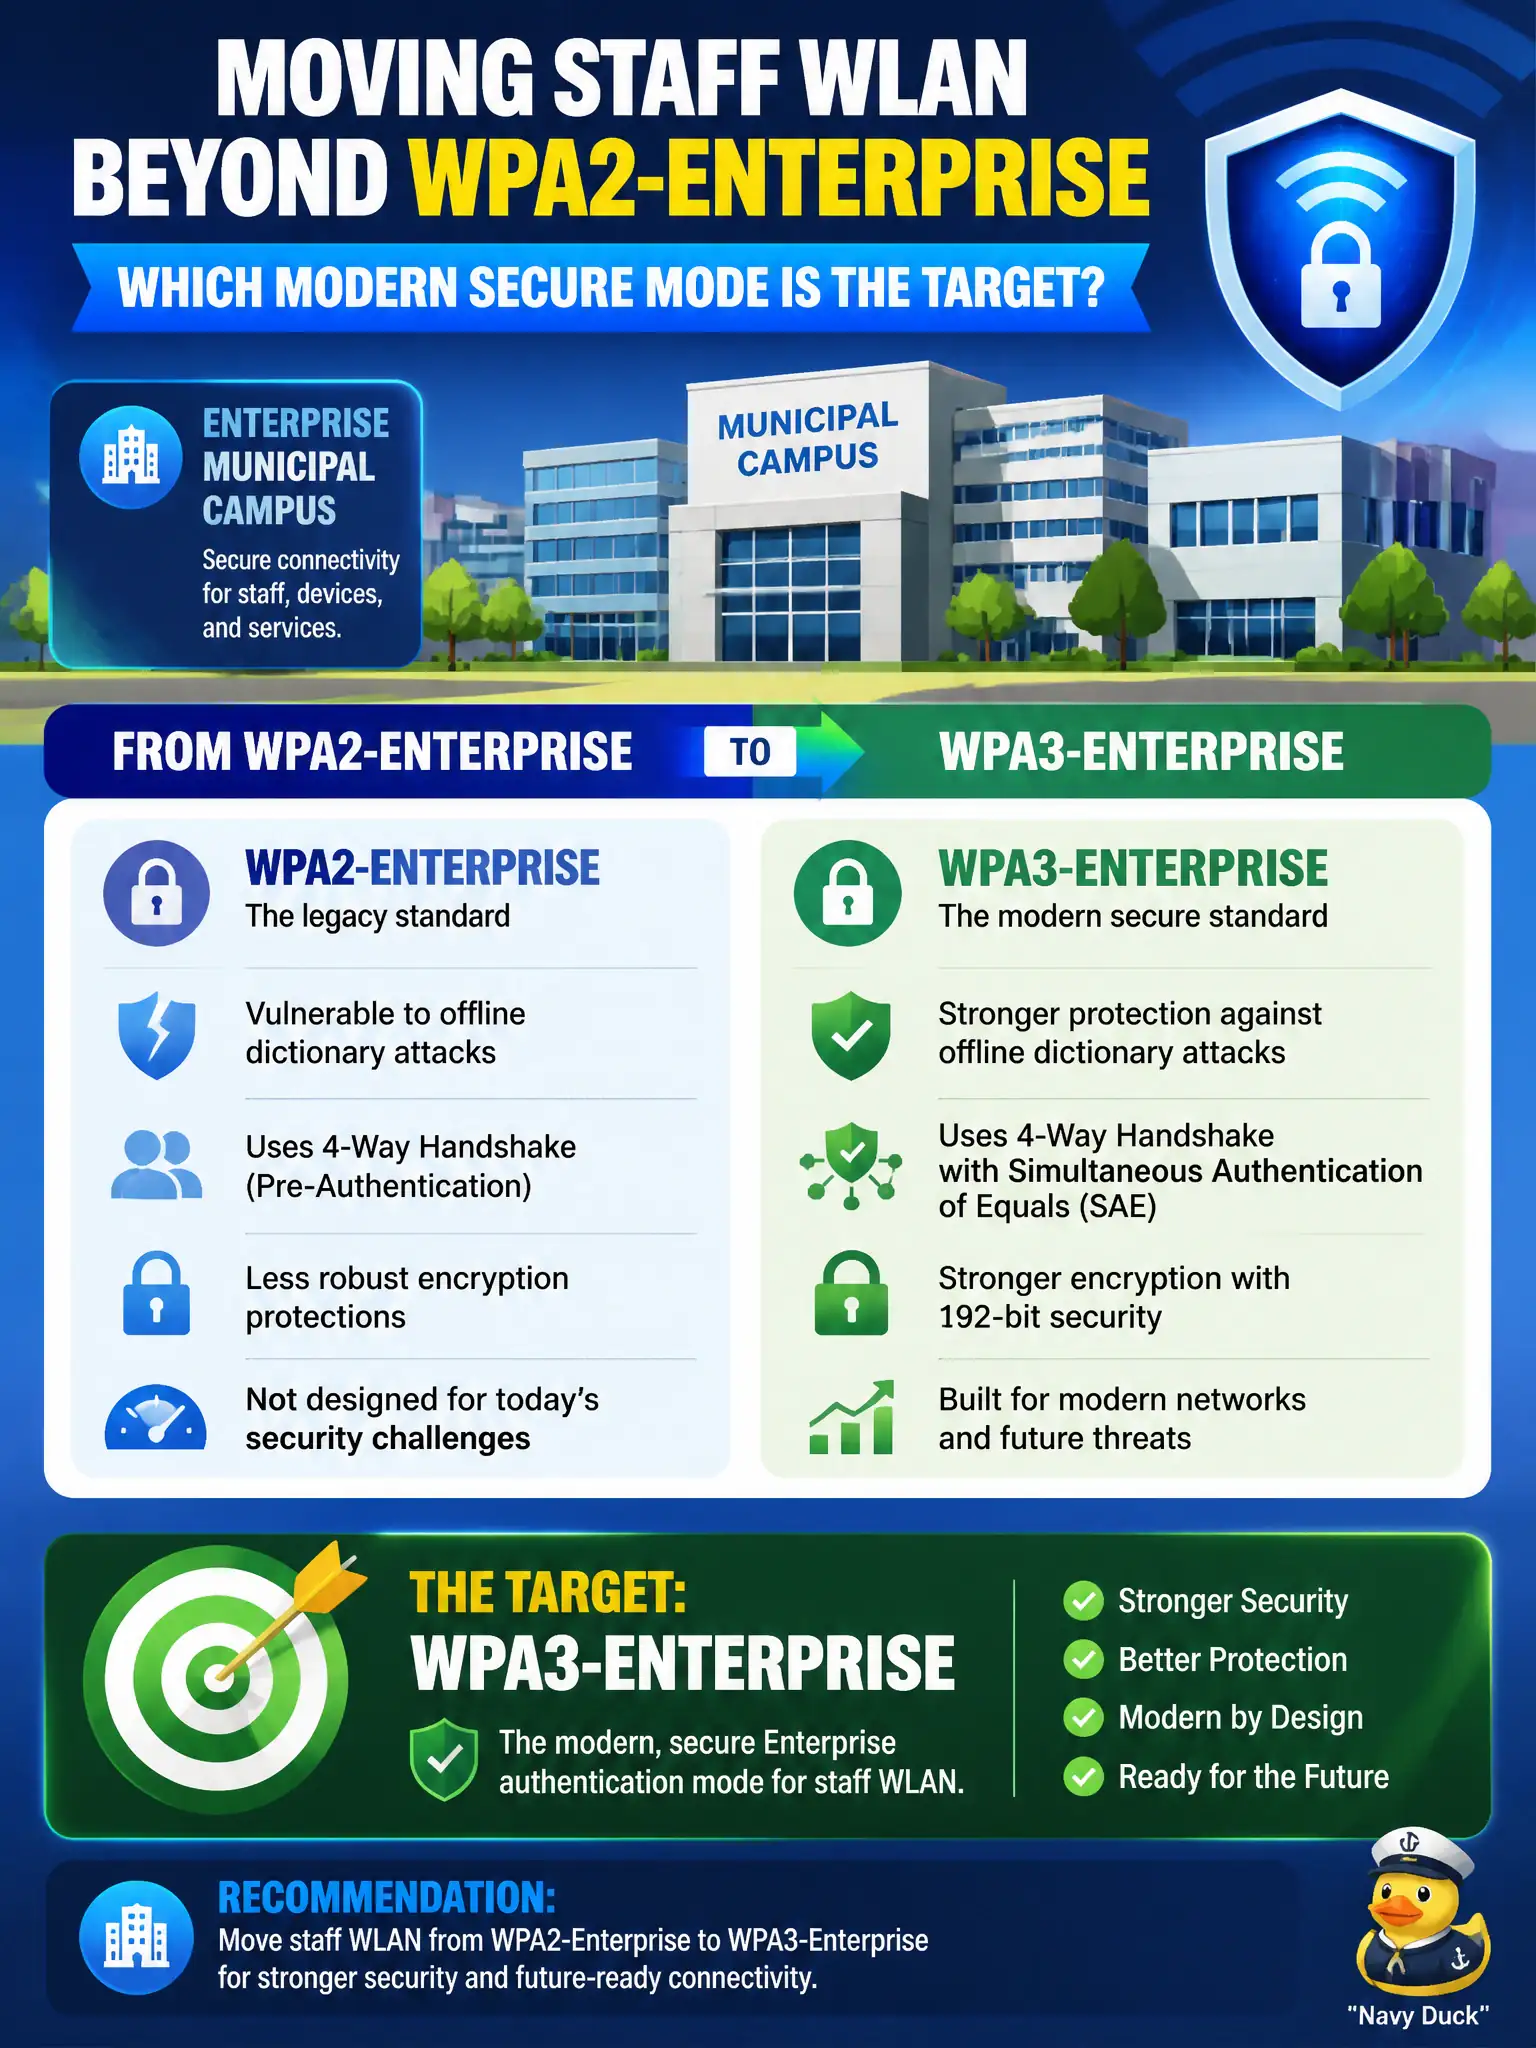
An enterprise municipal campus is moving staff WLAN beyond WPA2-Enterprise. Which modern secure mode should the technician recognize as the target?
Select an answer to reveal the explanation.
Short Explanation
Campus staff networks graduate to WPA3-Enterprise when the design calls for it. That is the modern Enterprise lane—not WEP templates, WPA-Personal mixed stickers, or hide-SSID theater.
Full Explanation
Enterprise municipal campuses moving staff WLAN beyond WPA2-Enterprise should recognize WPA3-Enterprise as the modern secure Enterprise authentication mode target. WPA3-Enterprise continues the 802.1X/EAP model with strengthened security properties appropriate for courthouse and city campus staff networks. Technicians should identify it as the upgrade path rather than inventing pseudo-Enterprise controls.
WEP-Enterprise with dynamic keying from an old controller template is not a modern target. WPA-Personal mixed mode advertised as “Enterprise compatible” is still Personal/legacy framing. Hidden SSID plus MAC filtering labeled as campus Enterprise security is obscurity and spoofable filtering—not Enterprise auth.
Exam caveat: the modern Enterprise mode name to recognize is WPA3-Enterprise—not WEP templates, Personal mixed mode, or cloaking/MAC bundles.
Operational check: note WPA3-Enterprise as the campus target in the migration plan, validate controller/AP and RADIUS readiness, pilot a staff SSID, and retire narratives that call MAC+hidden “Enterprise.” Municipal technicians document the verified setting in the as-built packet so the next shift inherits a known-good civic configuration rather than tribal knowledge.