
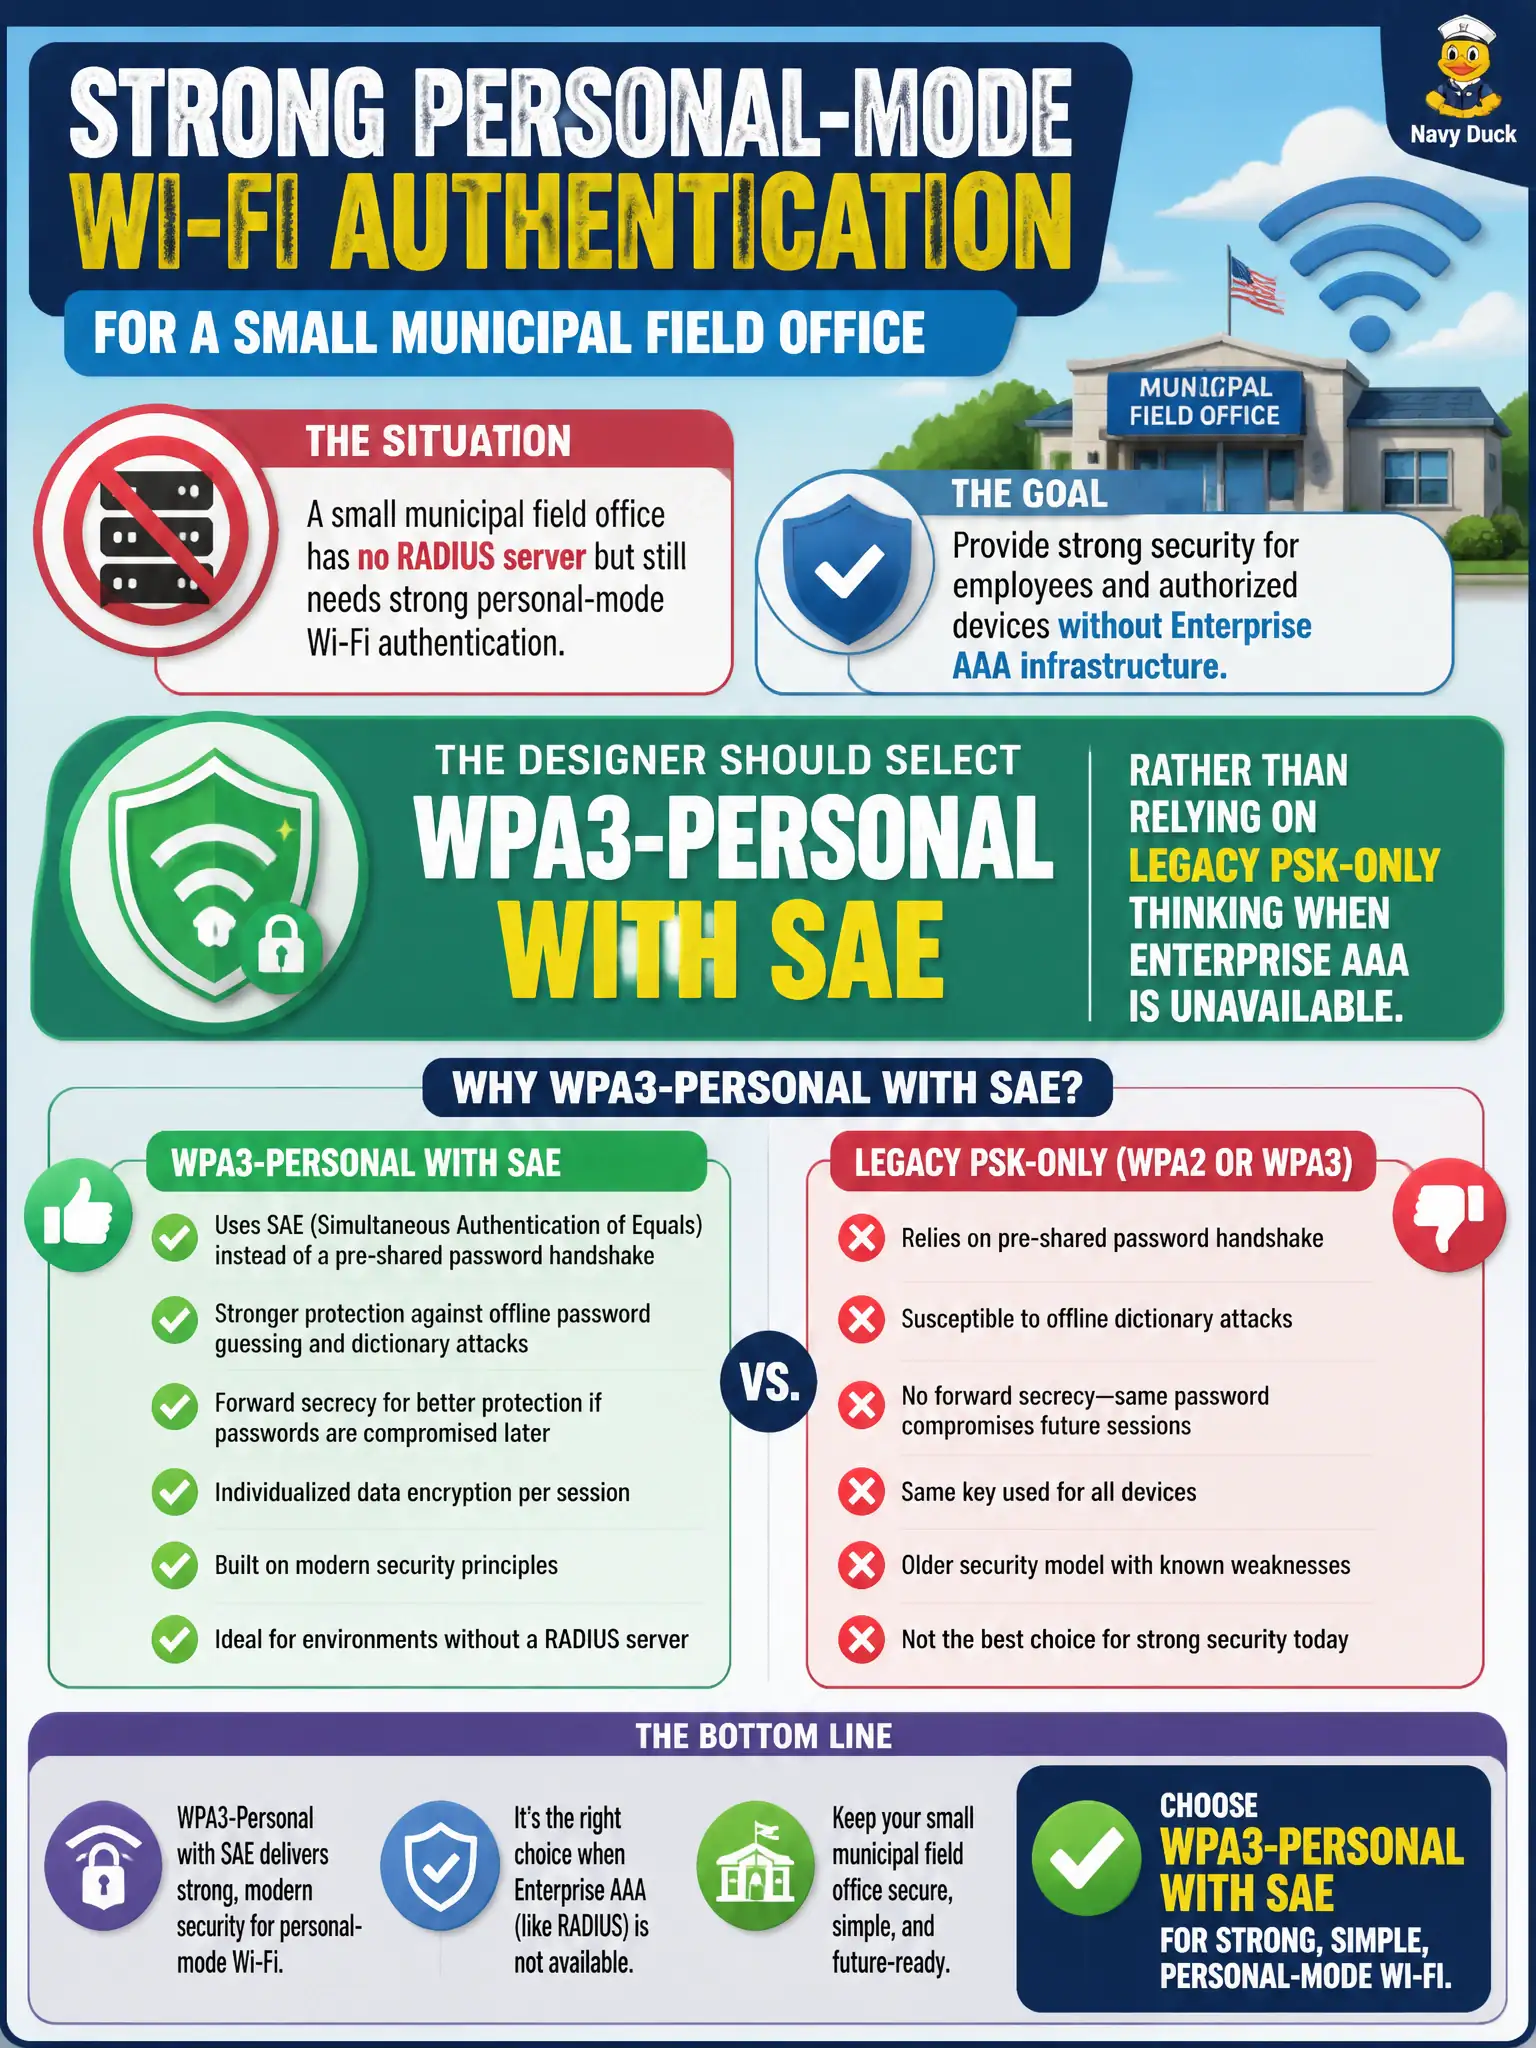
A small municipal field office has no RADIUS server but still needs strong personal-mode Wi-Fi authentication. What should the designer select?
Select an answer to reveal the explanation.
Short Explanation
No RADIUS does not mean “leave the door open” or drag WEP out of retirement. WPA3-Personal with SAE is the modern personal lock for that little field office. Shared PSK nostalgia without SAE is yesterday’s answer.
Full Explanation
A small municipal field office without RADIUS still needs strong personal-mode authentication, which points to WPA3-Personal with SAE rather than legacy PSK-only thinking when Enterprise AAA is unavailable. Open authentication with MAC allow-lists only lacks modern personal AKM and is trivially spoofable. WEP shared-key mode needs no RADIUS but is deprecated and unsafe. Disabling encryption so clients connect faster removes confidentiality and authentication strength entirely. Exam caveat: absence of RADIUS does not justify open or WEP; WPA3-Personal SAE is the modern Personal-mode answer when Enterprise cannot be fielded yet. Operational check: set the field-office SSID to WPA3-Personal SAE with a long random passphrase, validate client support, document any Transition Mode exception with risk acceptance, and schedule Enterprise if the office later gains AAA. Record the design choice in the municipal branch WLAN standard. In municipal WLAN operations, record the rationale in the change ticket so future on-call staff know which control was chosen and which failure modes the rejected options would create for city services. Re-validate after the next maintenance window that the same control still holds under the infrastructure versions and client fleets used by the civic environment.