
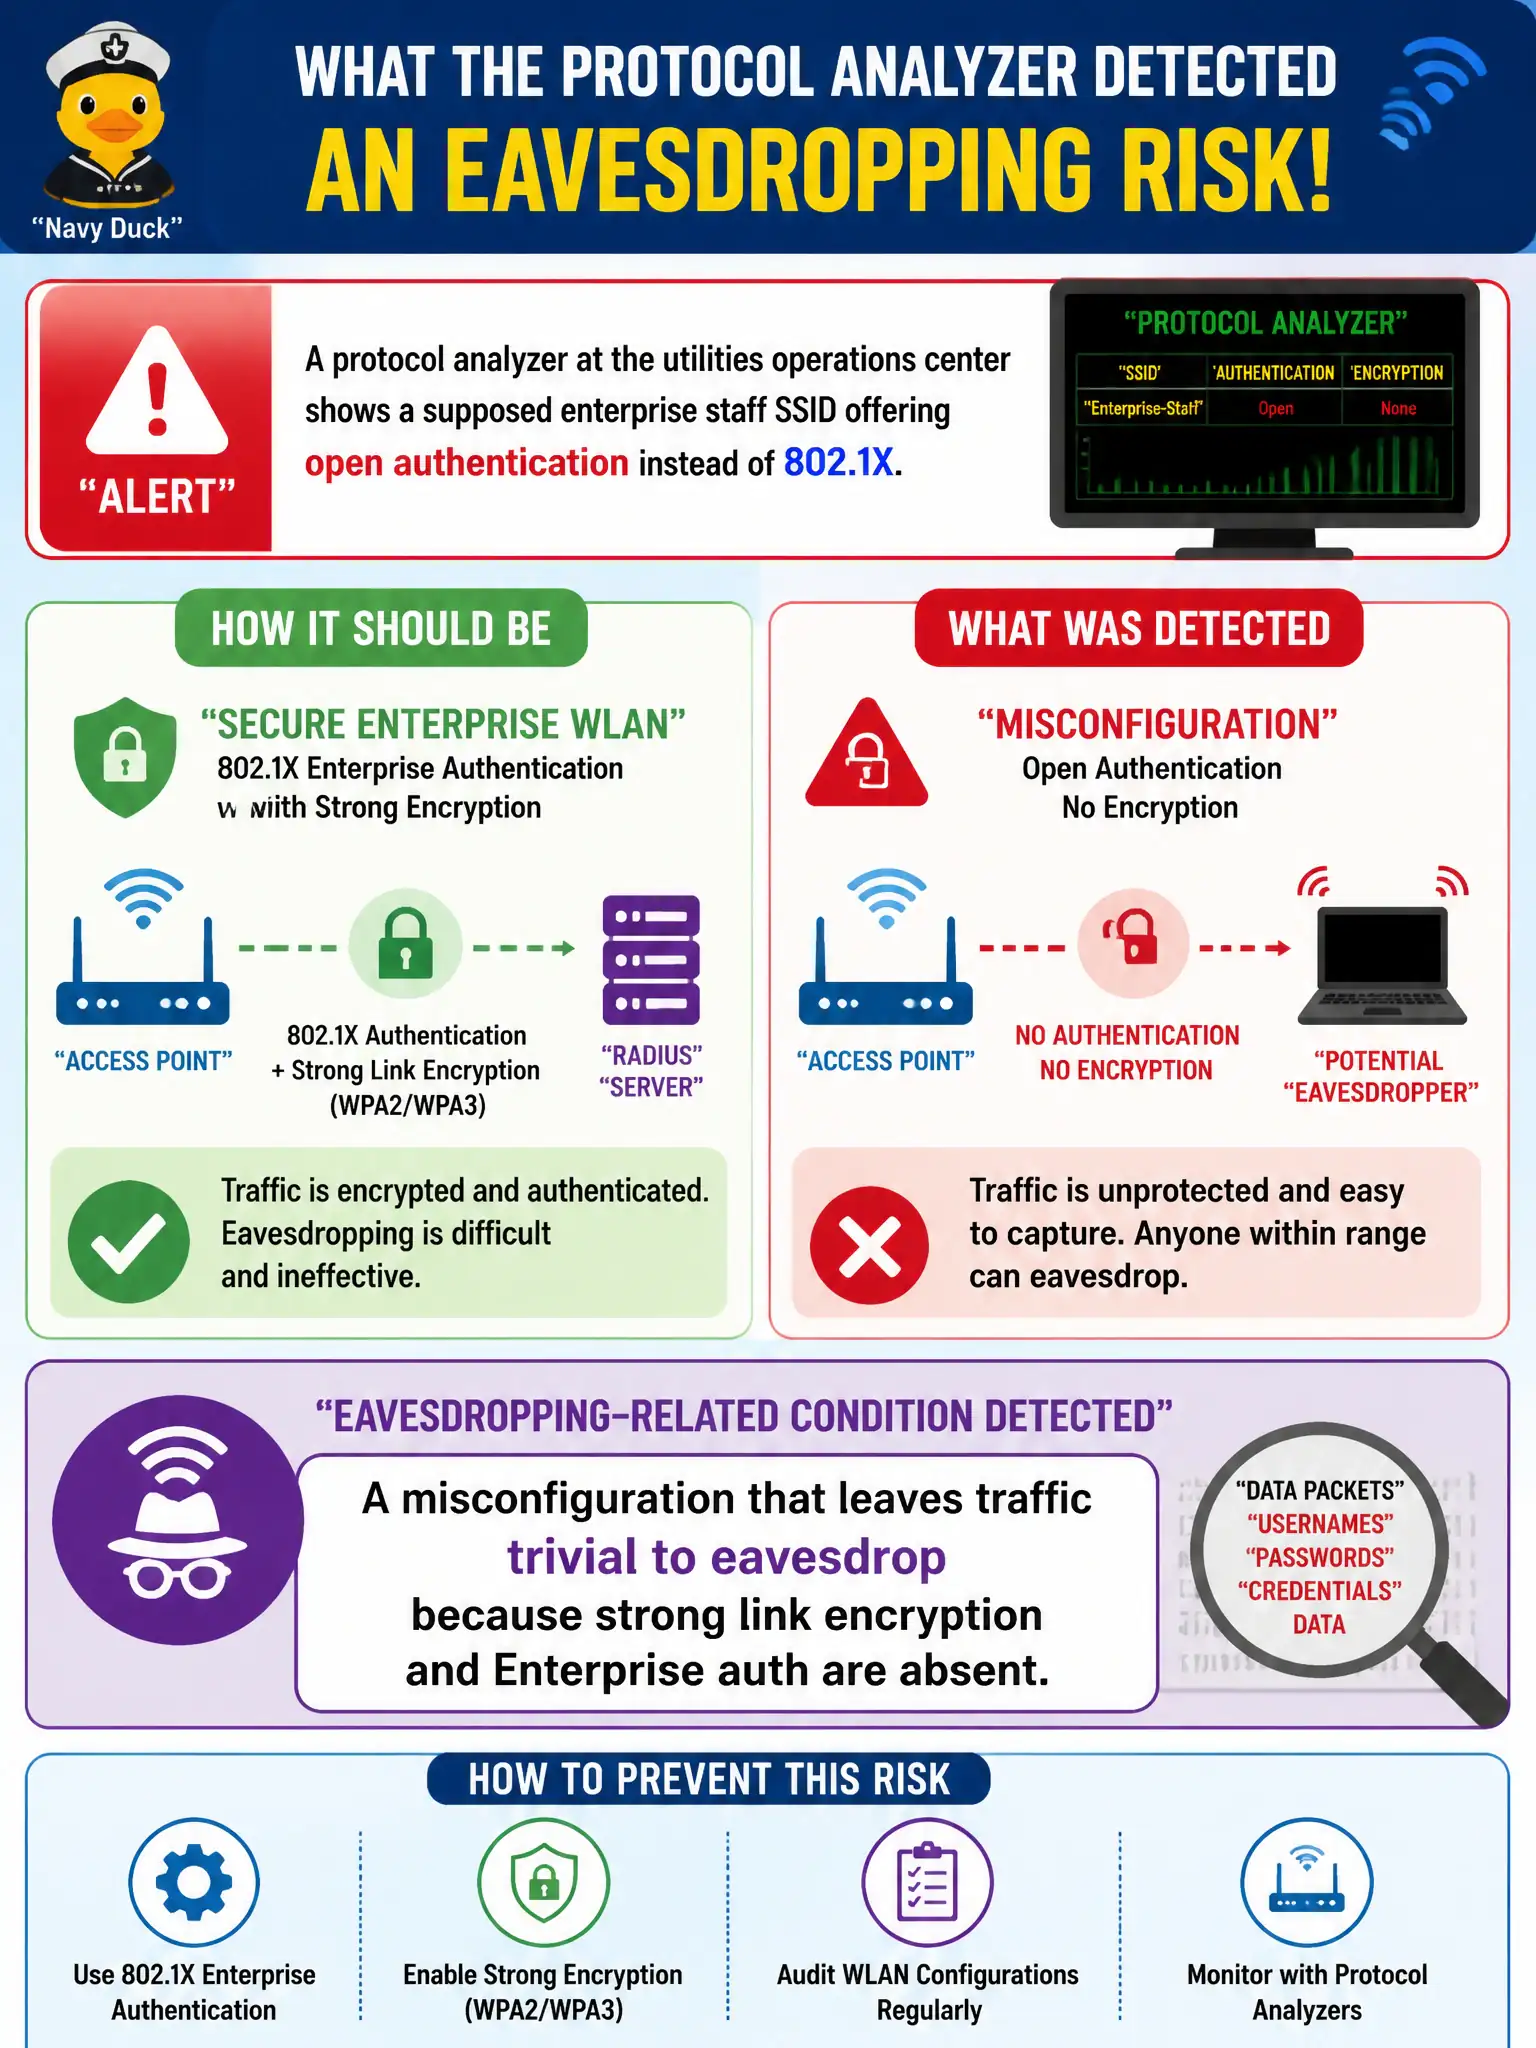
A protocol analyzer at the utilities operations center shows a supposed enterprise staff SSID offering open authentication instead of 802.1X. What eavesdropping-related condition has been detected?
Select an answer to reveal the explanation.
Short Explanation
If the “secure staff” SSID is hanging a wide-open sign, anyone can listen—and that is the eavesdropping jackpot. The analyzer just caught a misconfig that makes confidentiality fail by default. Fix auth and encryption; do not celebrate open mode on staff.
Full Explanation
A protocol analyzer at the utilities operations center showing a supposed enterprise staff SSID offering open authentication instead of 802.1X has detected a misconfiguration that leaves traffic trivial to eavesdrop because strong link encryption and Enterprise auth are absent. An open "staff" SSID is a critical confidentiality failure for utilities operations traffic. Correct WPA3-Enterprise 192-bit negotiation with GCMP-256 would show strong EAP and ciphers, not open authentication. Healthy PMF mandatory mode with no configuration drift does not present as open auth. Expected OWE transition mode solely on the public visitor SSID would be scoped to guest, not impersonating or mis-setting the enterprise staff SSID. Utilities ops centers must treat any open staff SSID advertisement as an urgent configuration or spoofing incident. Exam caveat: distinguish a true controller misconfiguration from an evil twin advertising open auth with the staff name—both are serious but remediation paths differ. Operational check: verify the BSSID against authorized inventory, if sanctioned fix the SSID profile to 802.1X with approved ciphers immediately, if unsanctioned contain the twin, and sample client associations to force reconnection to the secured profile.