
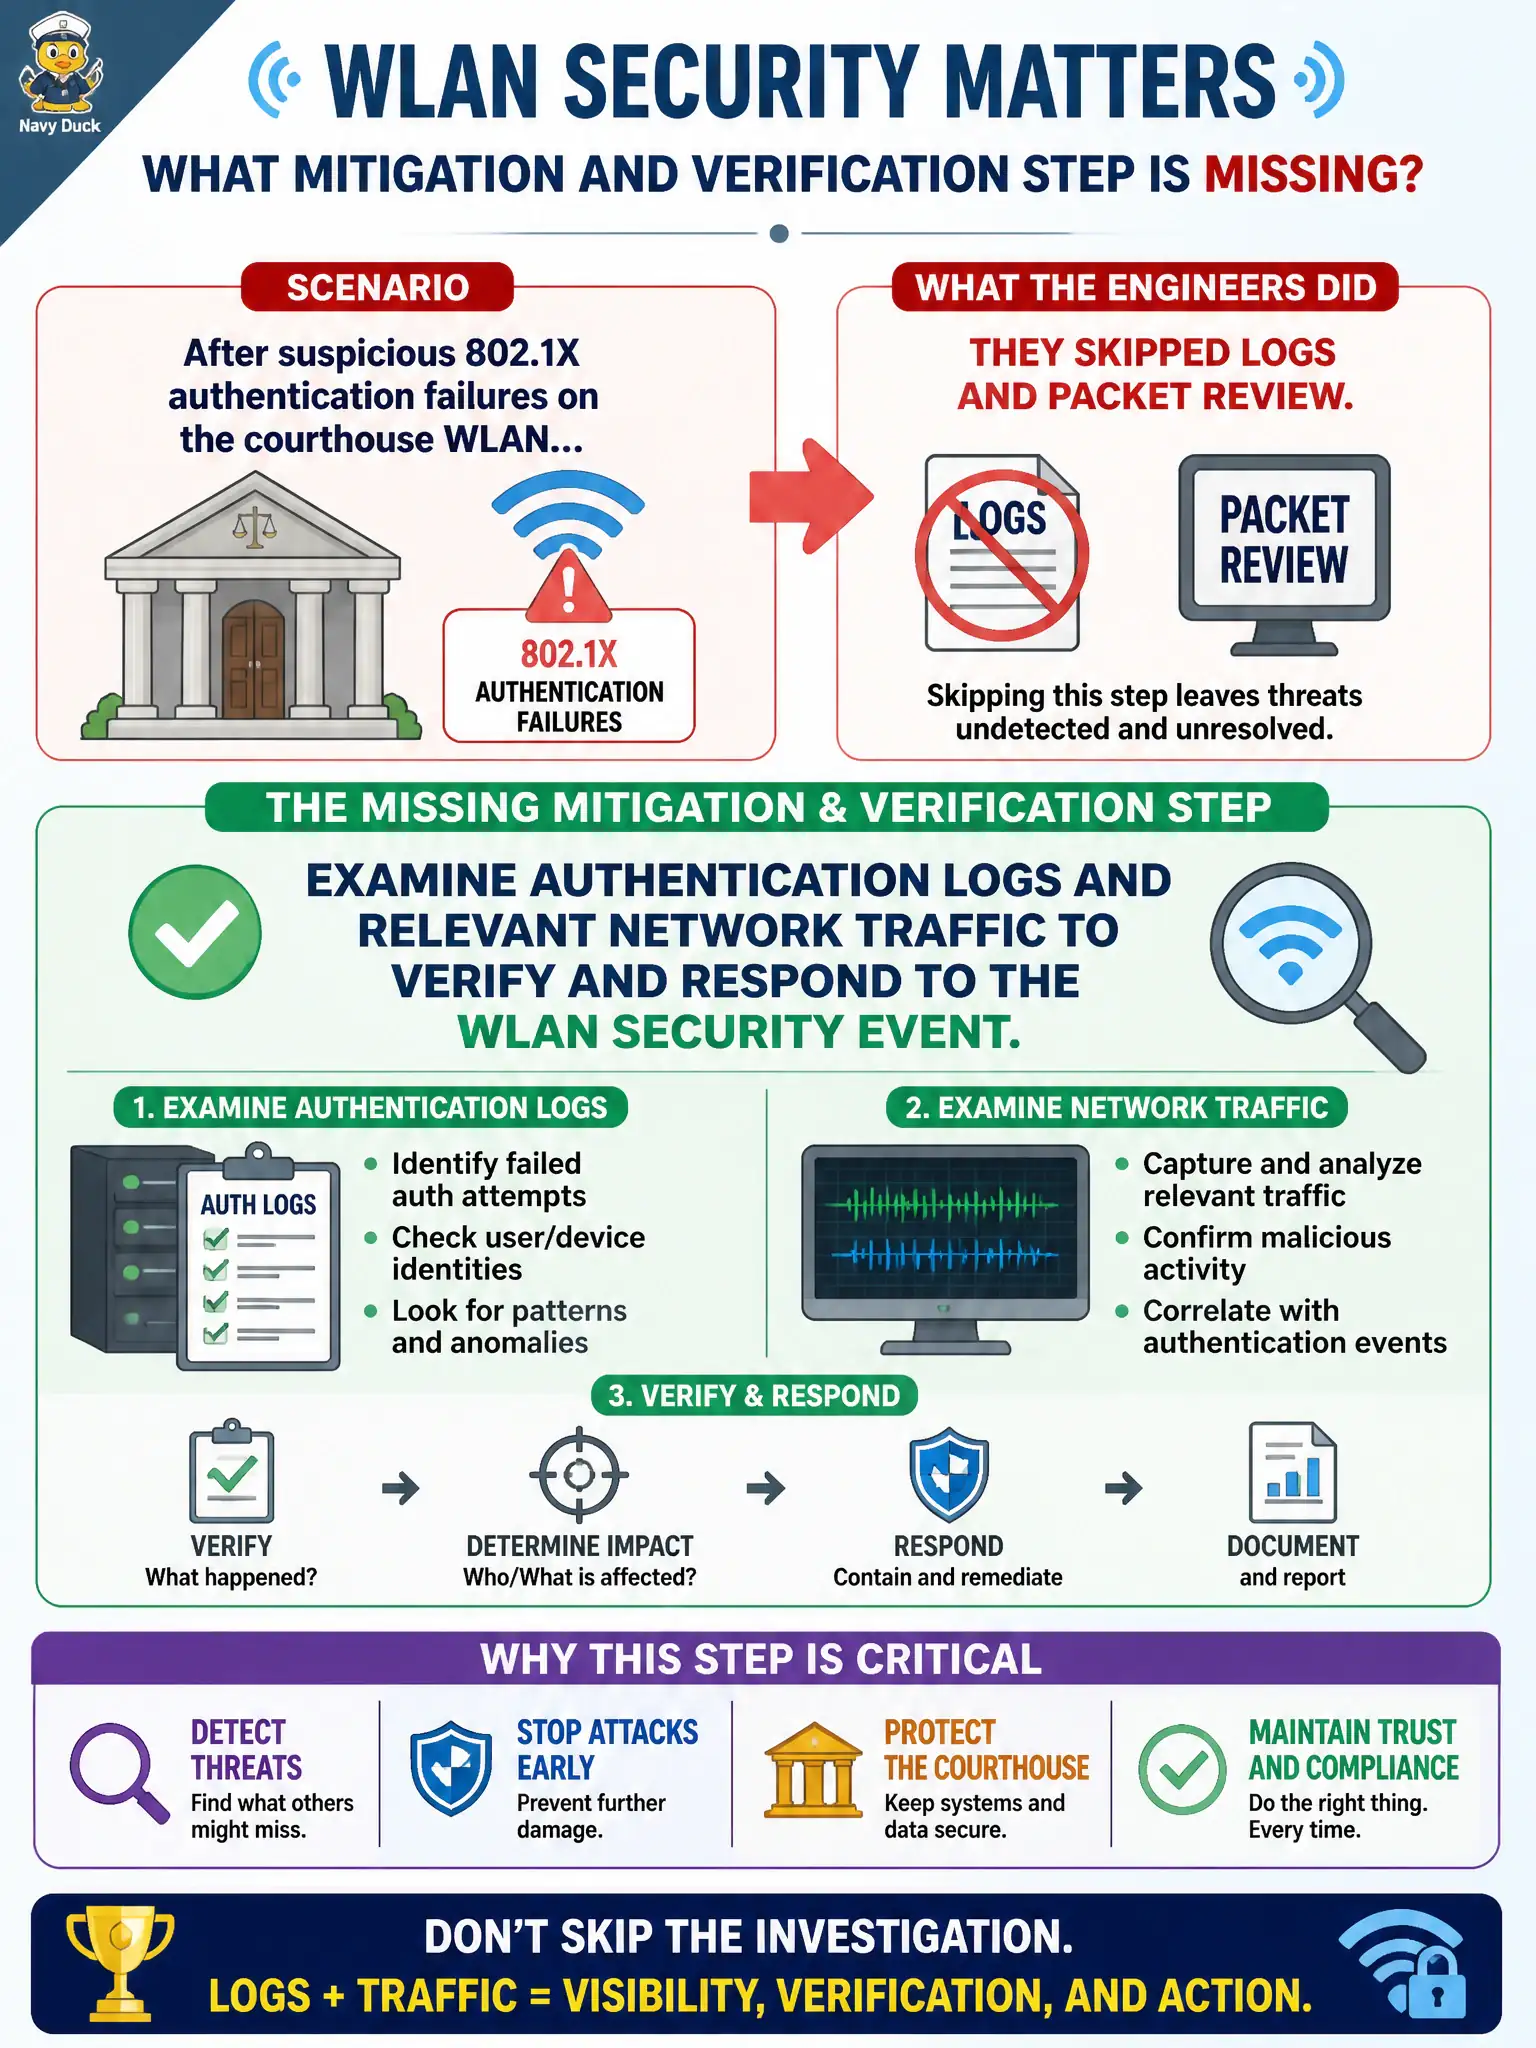
After suspicious 802.1X authentication failures on the courthouse WLAN, engineers skip logs and packet review. What mitigation and verification step is missing?
Select an answer to reveal the explanation.
Short Explanation
Weird auth failures are clues, not wallpaper. Read the RADIUS and controller logs—and peek at the traffic—before you declare the courthouse Wi-Fi fine.
Full Explanation
After suspicious 802.1X authentication failures on the courthouse WLAN, skipping logs and packet review omits examining authentication logs and relevant network traffic to verify and respond to the WLAN security event. AAA rejects, EAP failure codes, correlating MAC addresses, and wireless captures distinguish credential stuffing, misissued certificates, evil-twin portals, rogue RADIUS, and simple client misconfiguration before any broad remediation. Factory-resetting every switch in the building without collecting evidence destroys state and may not address the wireless authentication issue at all. Disabling all AAA logging so failure counts look healthier hides the incident and violates monitoring expectations. Assuming failures are cosmetic and clearing counters without investigation risks missing an active attack against civic court staff and attorneys. Verification and scoped response precede mass disruptive changes. Exam caveat: mitigation and verification for authentication anomalies center on log and traffic analysis before mass resets or blind configuration wipes. Operational check: pull RADIUS and controller logs for the failure window, identify usernames, MACs, and EAP types, capture wireless traces if an evil twin is suspected, contain confirmed malicious BSSIDs, remediate affected clients with evidence retained, and only then consider wider infrastructure resets if justified.