
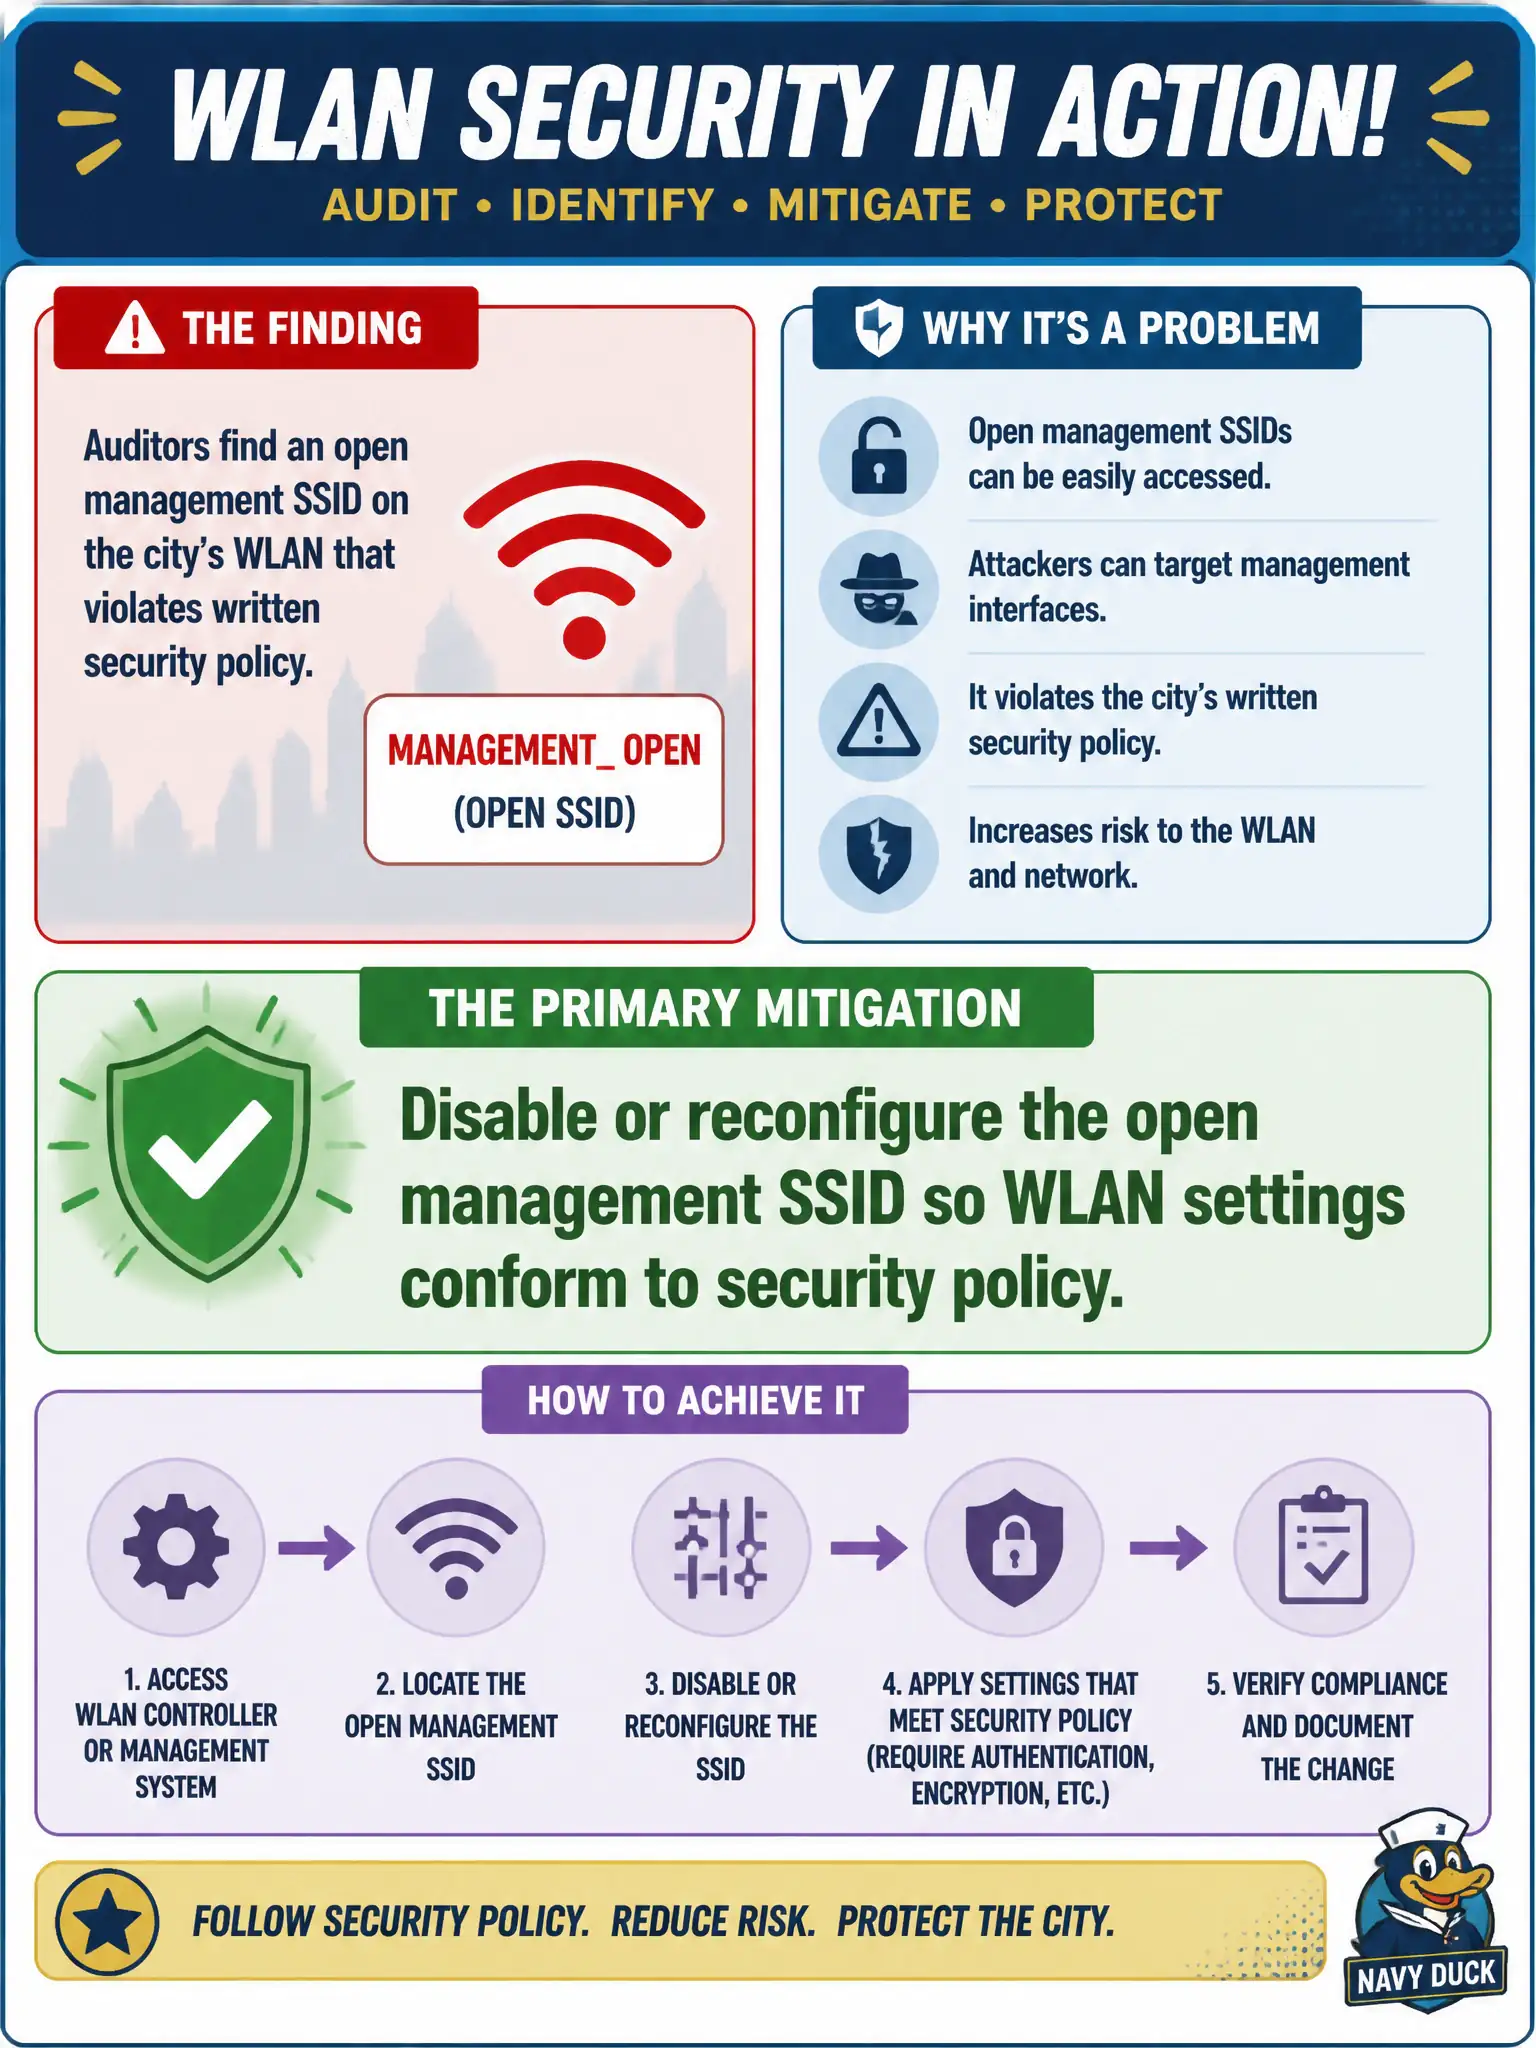
Auditors find an open management SSID on the city's WLAN that violates written security policy. What is the primary mitigation?
Select an answer to reveal the explanation.
Short Explanation
An open management SSID is a wide-open admin door. Do not just write a ticket poem—shut it down or lock it down so the city WLAN matches policy.
Full Explanation
When auditors find an open management SSID on the city's WLAN that violates written security policy, the primary mitigation is to disable or reconfigure the open management SSID so WLAN settings conform to security policy. Open management connectivity invites unauthorized administration, credential harvesting, and eavesdropping on management traffic across civic infrastructure. Filing a ticket note describing the finding while leaving the open management SSID online documents awareness without remediation and leaves the audit finding open. Adding more marketing text to the open SSID beacon without changing security settings is irrelevant to management-plane risk. Moving the open management SSID to a higher channel number only changes RF channeling, not authentication or encryption posture. Civic management access should use secure, authenticated, logged paths consistent with policy—VPN, wired AAA, or an enterprise-secured management SSID—not open wireless. Exam caveat: configuration conformance to policy is the direct remediation for policy-violating SSID settings; documentation alone is insufficient. Operational check: disable the open management SSID or convert management access to an approved secure method, verify no break-glass workflows still depend on it, update controller templates to prevent drift, and provide auditors with before-and-after configuration evidence and ticket closure.