
A compromised municipal AP cannot be patched yet. What mitigation should the CWSP select in the meantime?
Select an answer to reveal the explanation.
Short Explanation
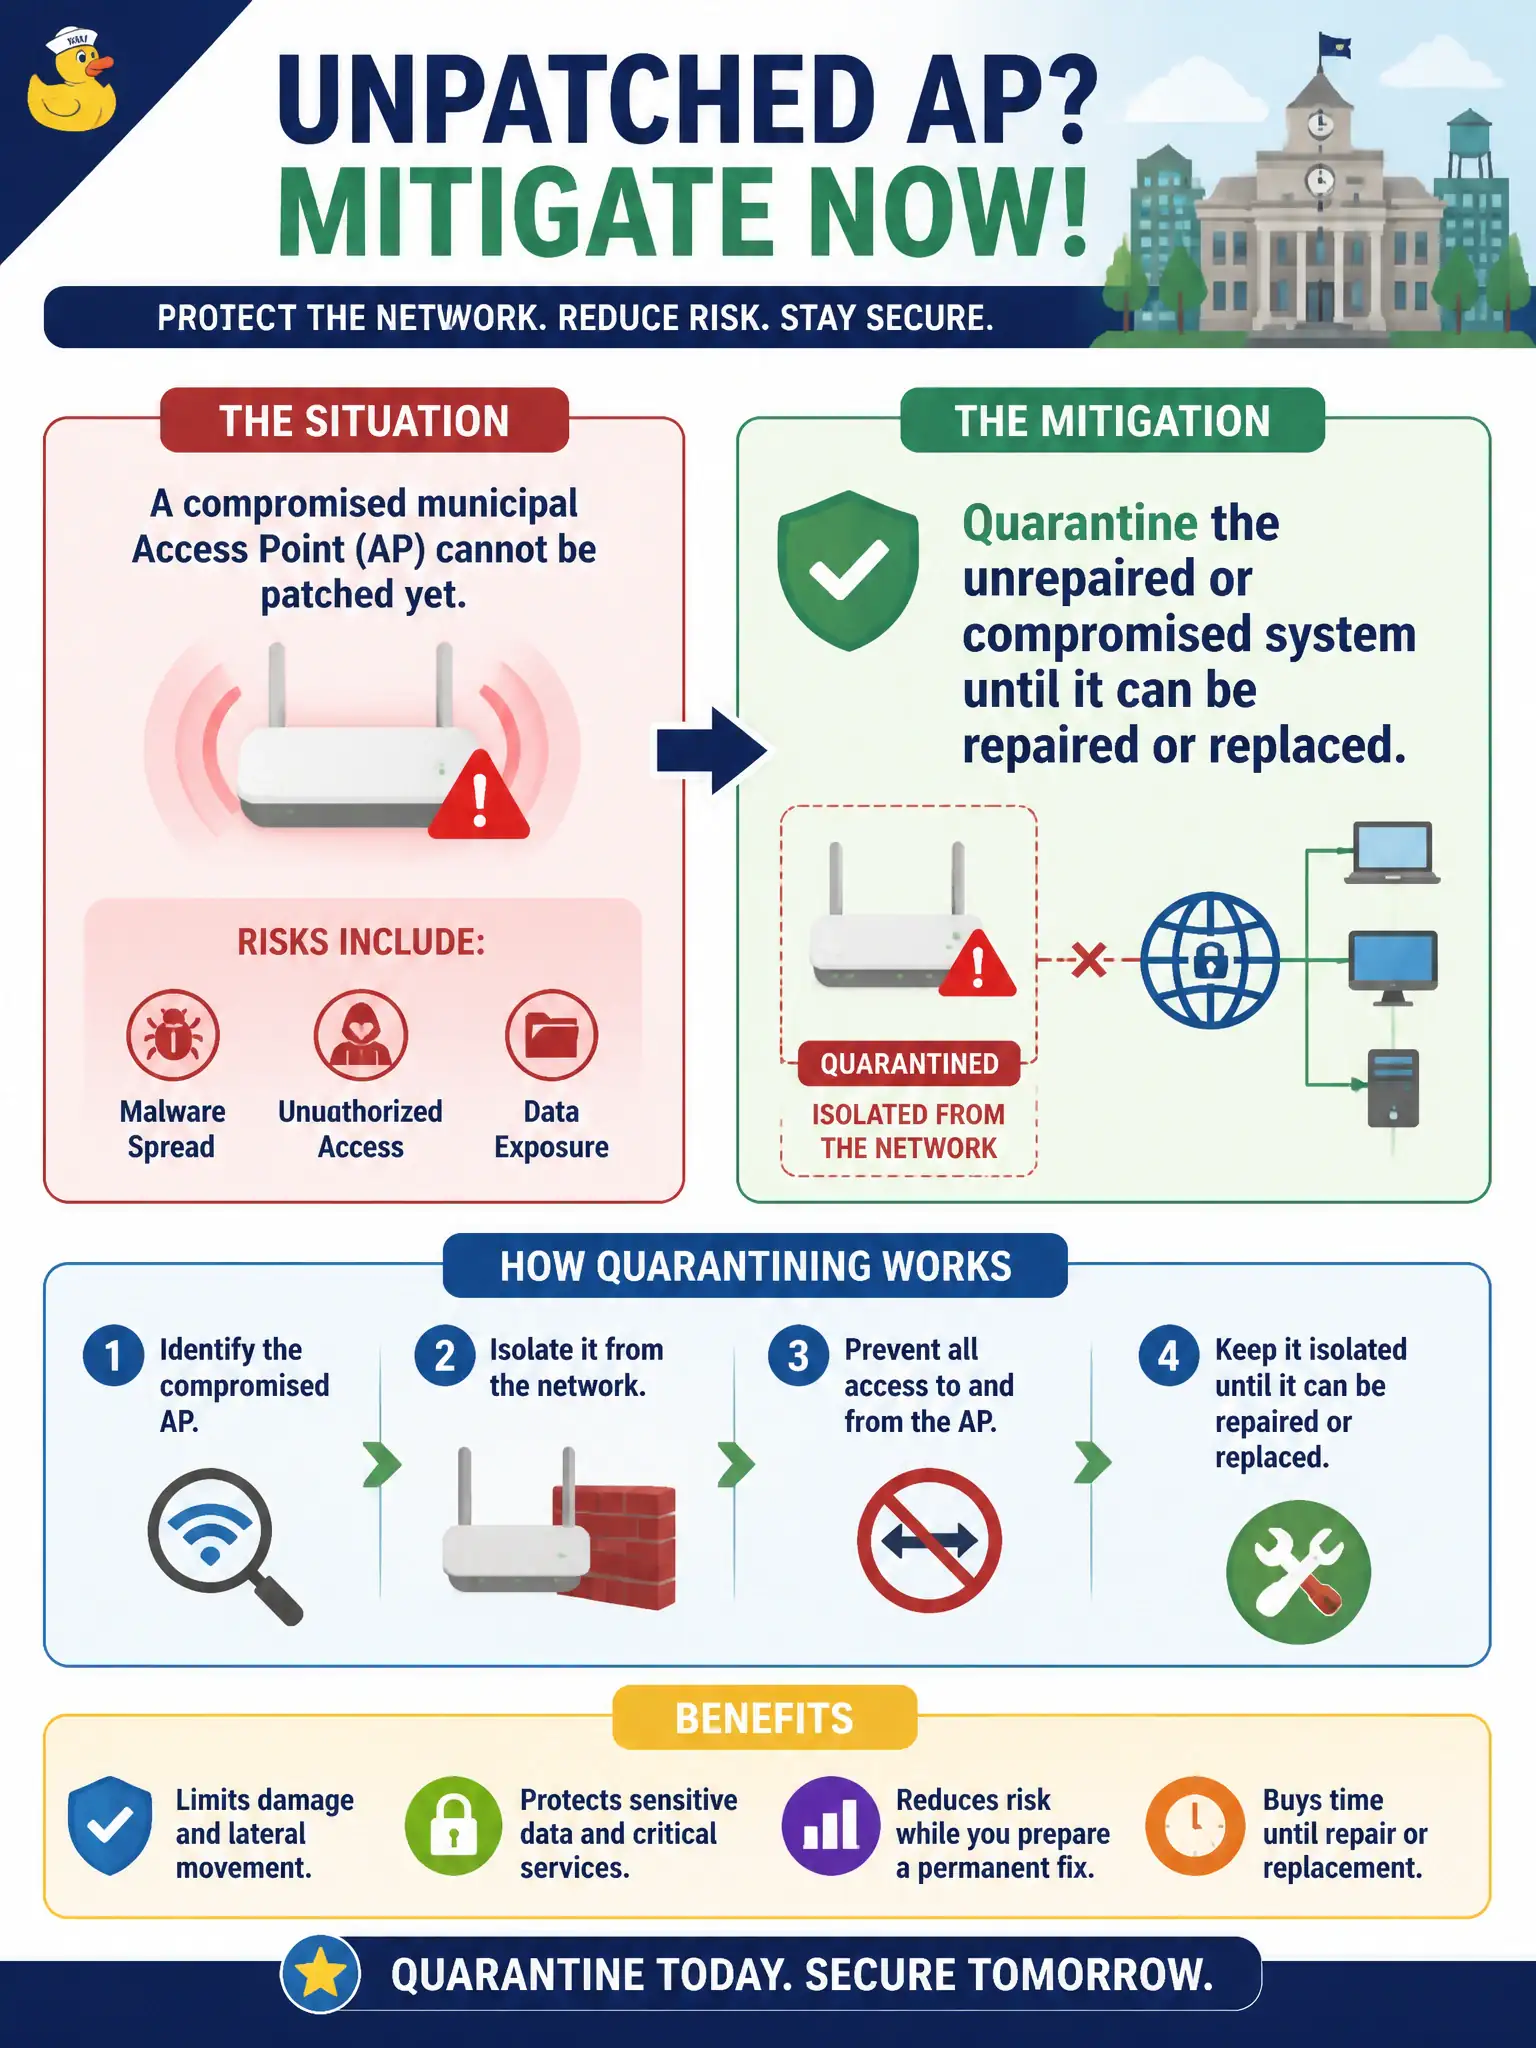
Sick AP, no patch yet? Pull it out of the healthy herd. Quarantine the compromised city radio so it cannot keep infecting or eavesdropping while you wait on a fix.
Full Explanation
When a compromised municipal AP cannot be patched yet, the CWSP should quarantine the unrepaired or compromised system until it can be repaired or replaced. Quarantine limits lateral movement, credential theft, and RF trust abuse while preserving evidence and allowing a clean rebuild or RMA under known-good firmware. Leaving it in production and increasing guest bandwidth as a distraction keeps a known-bad radio inside the trust boundary serving civic users. Publishing the AP's admin password so more staff can "monitor" it expands the compromise and destroys accountability. Only updating the SSID emoji and continuing normal operations is cosmetic non-remediation that fails incident response standards. Civic playbooks should treat compromised APs like compromised servers: isolate wired and wireless paths, investigate, rebuild or replace, rotate secrets, then rejoin under managed configuration with heightened monitoring. Exam caveat: quarantine may mean switchport shutdown, RF containment, removal from management groups, or physical pull—choose methods that stop both wired and wireless trust abuse. Operational check: shut down or contain the AP's switchport and radio, rotate any credentials or certificates that AP could have exposed, image or replace from known-good firmware, re-provision under management with logging verified, and document chain-of-custody for forensics if the incident requires it.