
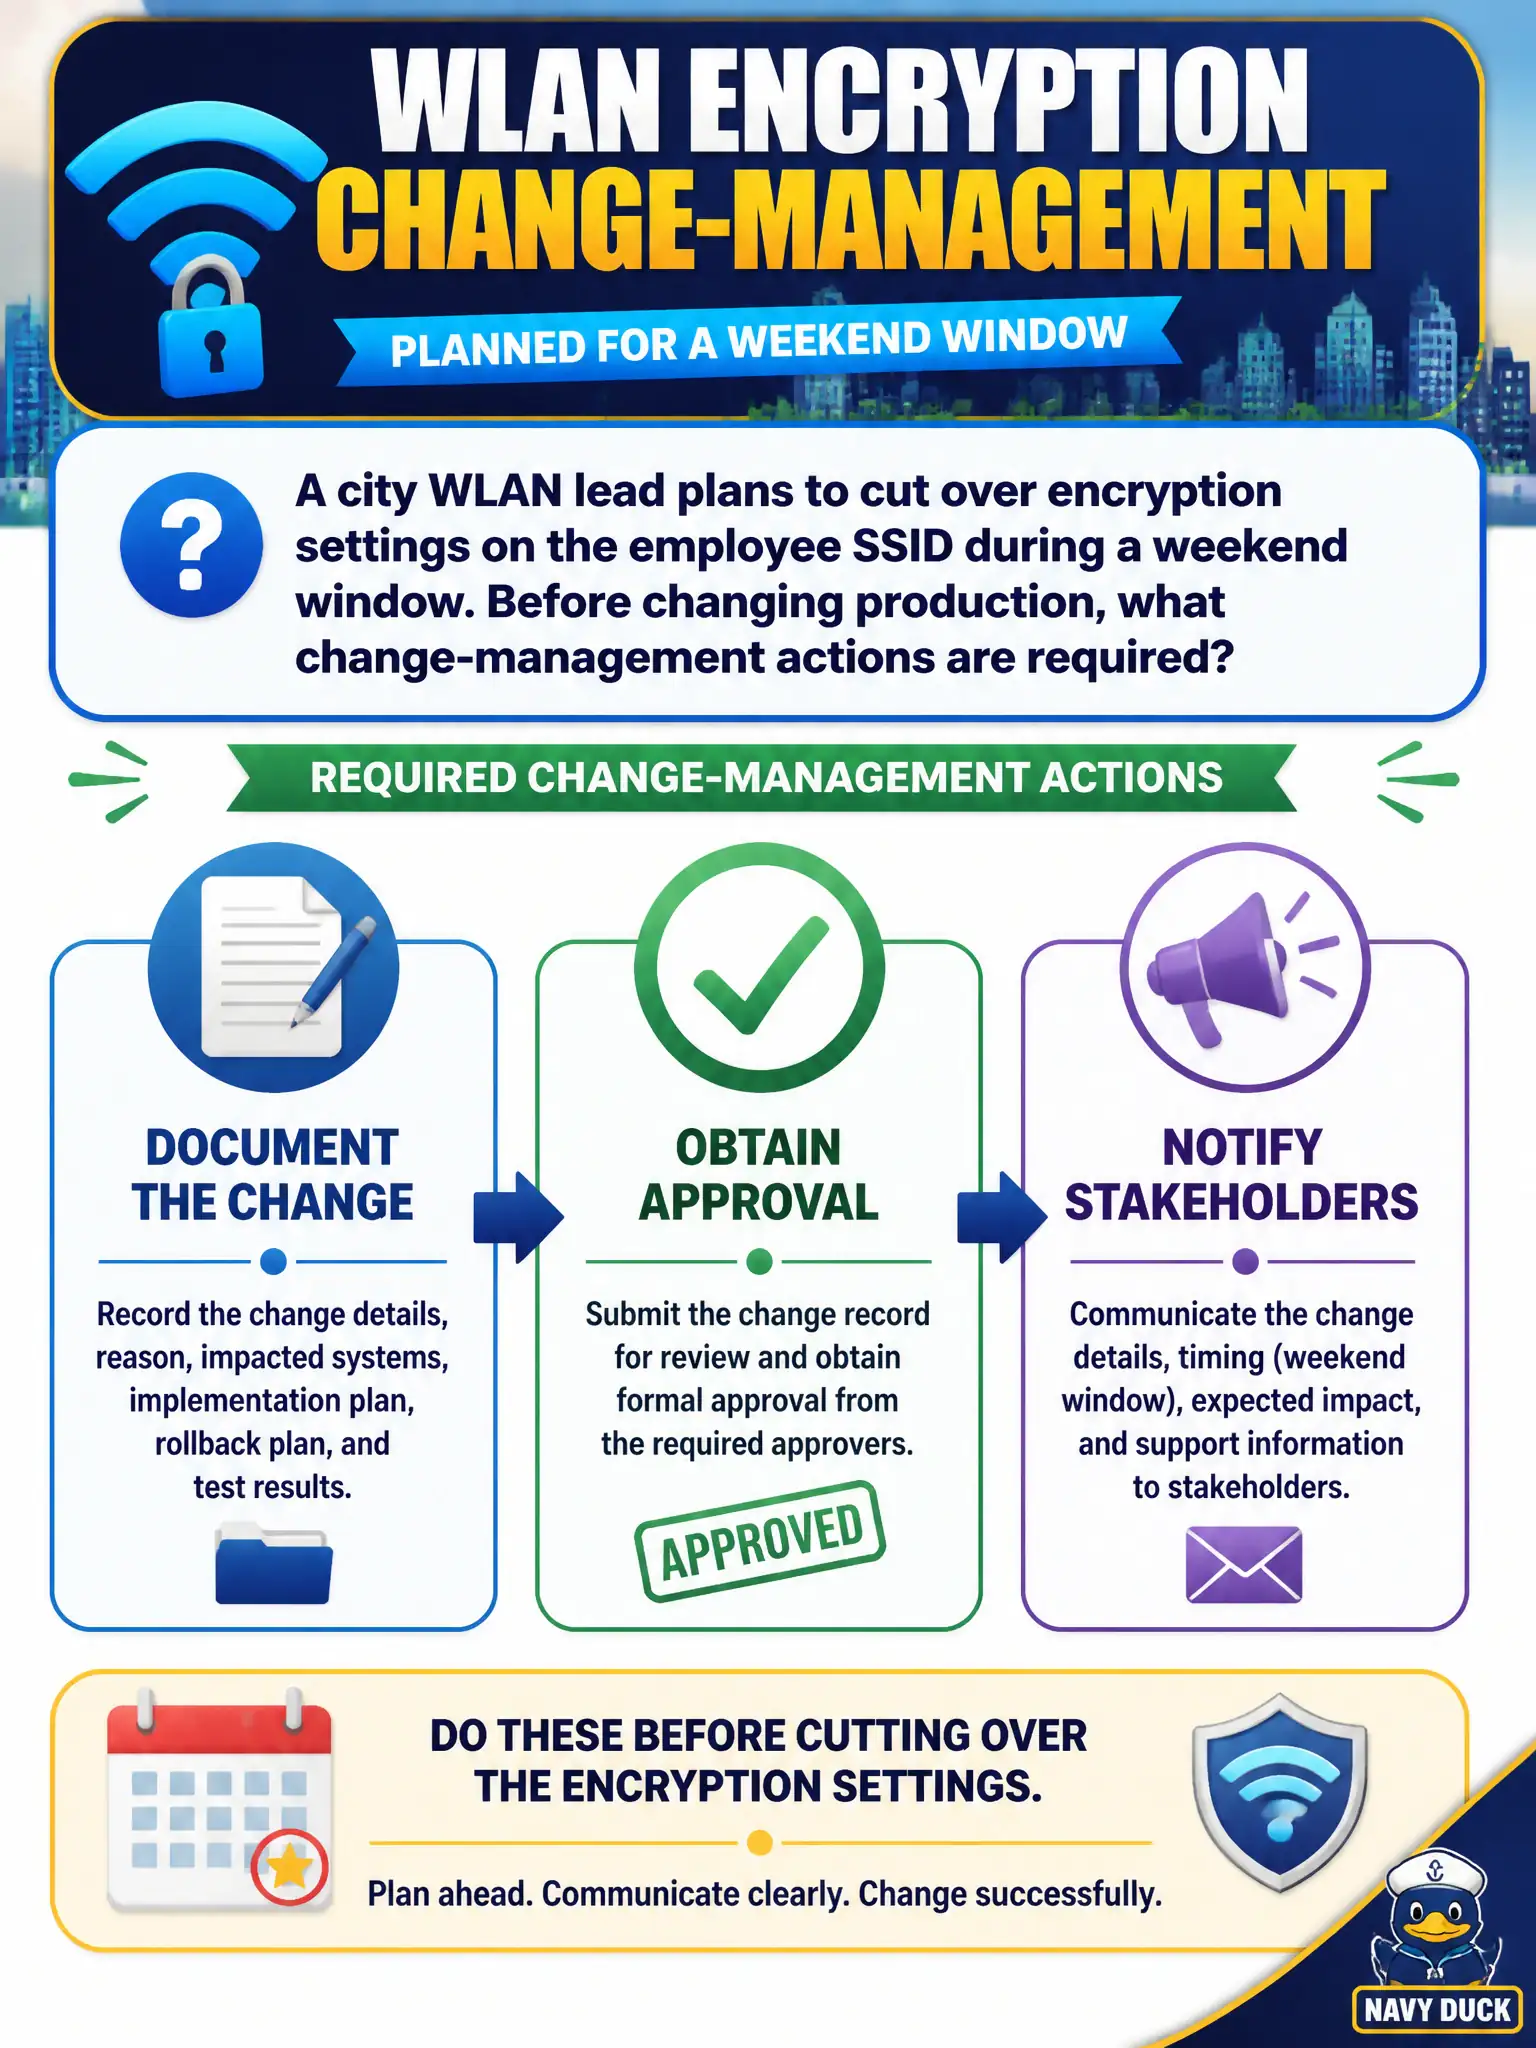
A city WLAN lead plans to cut over encryption settings on the employee SSID during a weekend window. Before changing production, what change-management actions are required?
Select an answer to reveal the explanation.
Short Explanation
Encryption cutovers are not secret weekend hobbies. Write it down, get the nod, and tell the people who will feel the impact. Silent flips are how Monday morning turns into an outage war room.
Full Explanation
In municipal WLAN environments, managing changes to encryption settings on an employee SSID requires a disciplined change-management process to ensure network security and operational continuity. Proper procedure involves documenting the planned change, securing approval from authorized personnel, and notifying all relevant stakeholders before implementing the new encryption settings. This approach ensures accountability, allows for risk assessment, and prepares support teams for potential issues during the cutover. Implementing changes silently without prior documentation risks untracked configuration drift and complicates troubleshooting if problems arise. Skipping approval under the assumption that encryption upgrades are always emergencies neglects the importance of governance and oversight, potentially bypassing critical risk evaluations. Notifying only the ISP marketing team while excluding WLAN operations and help desk ignores the operational impact and support responsibilities, leading to uncoordinated responses and user dissatisfaction. It is important to note that even routine security changes in civic WLANs must follow formal change management to maintain compliance and service reliability. A practical check is to verify that the change plan includes a rollback procedure, stakeholder notification list, and approval signatures before proceeding with the encryption update during the scheduled weekend window.