
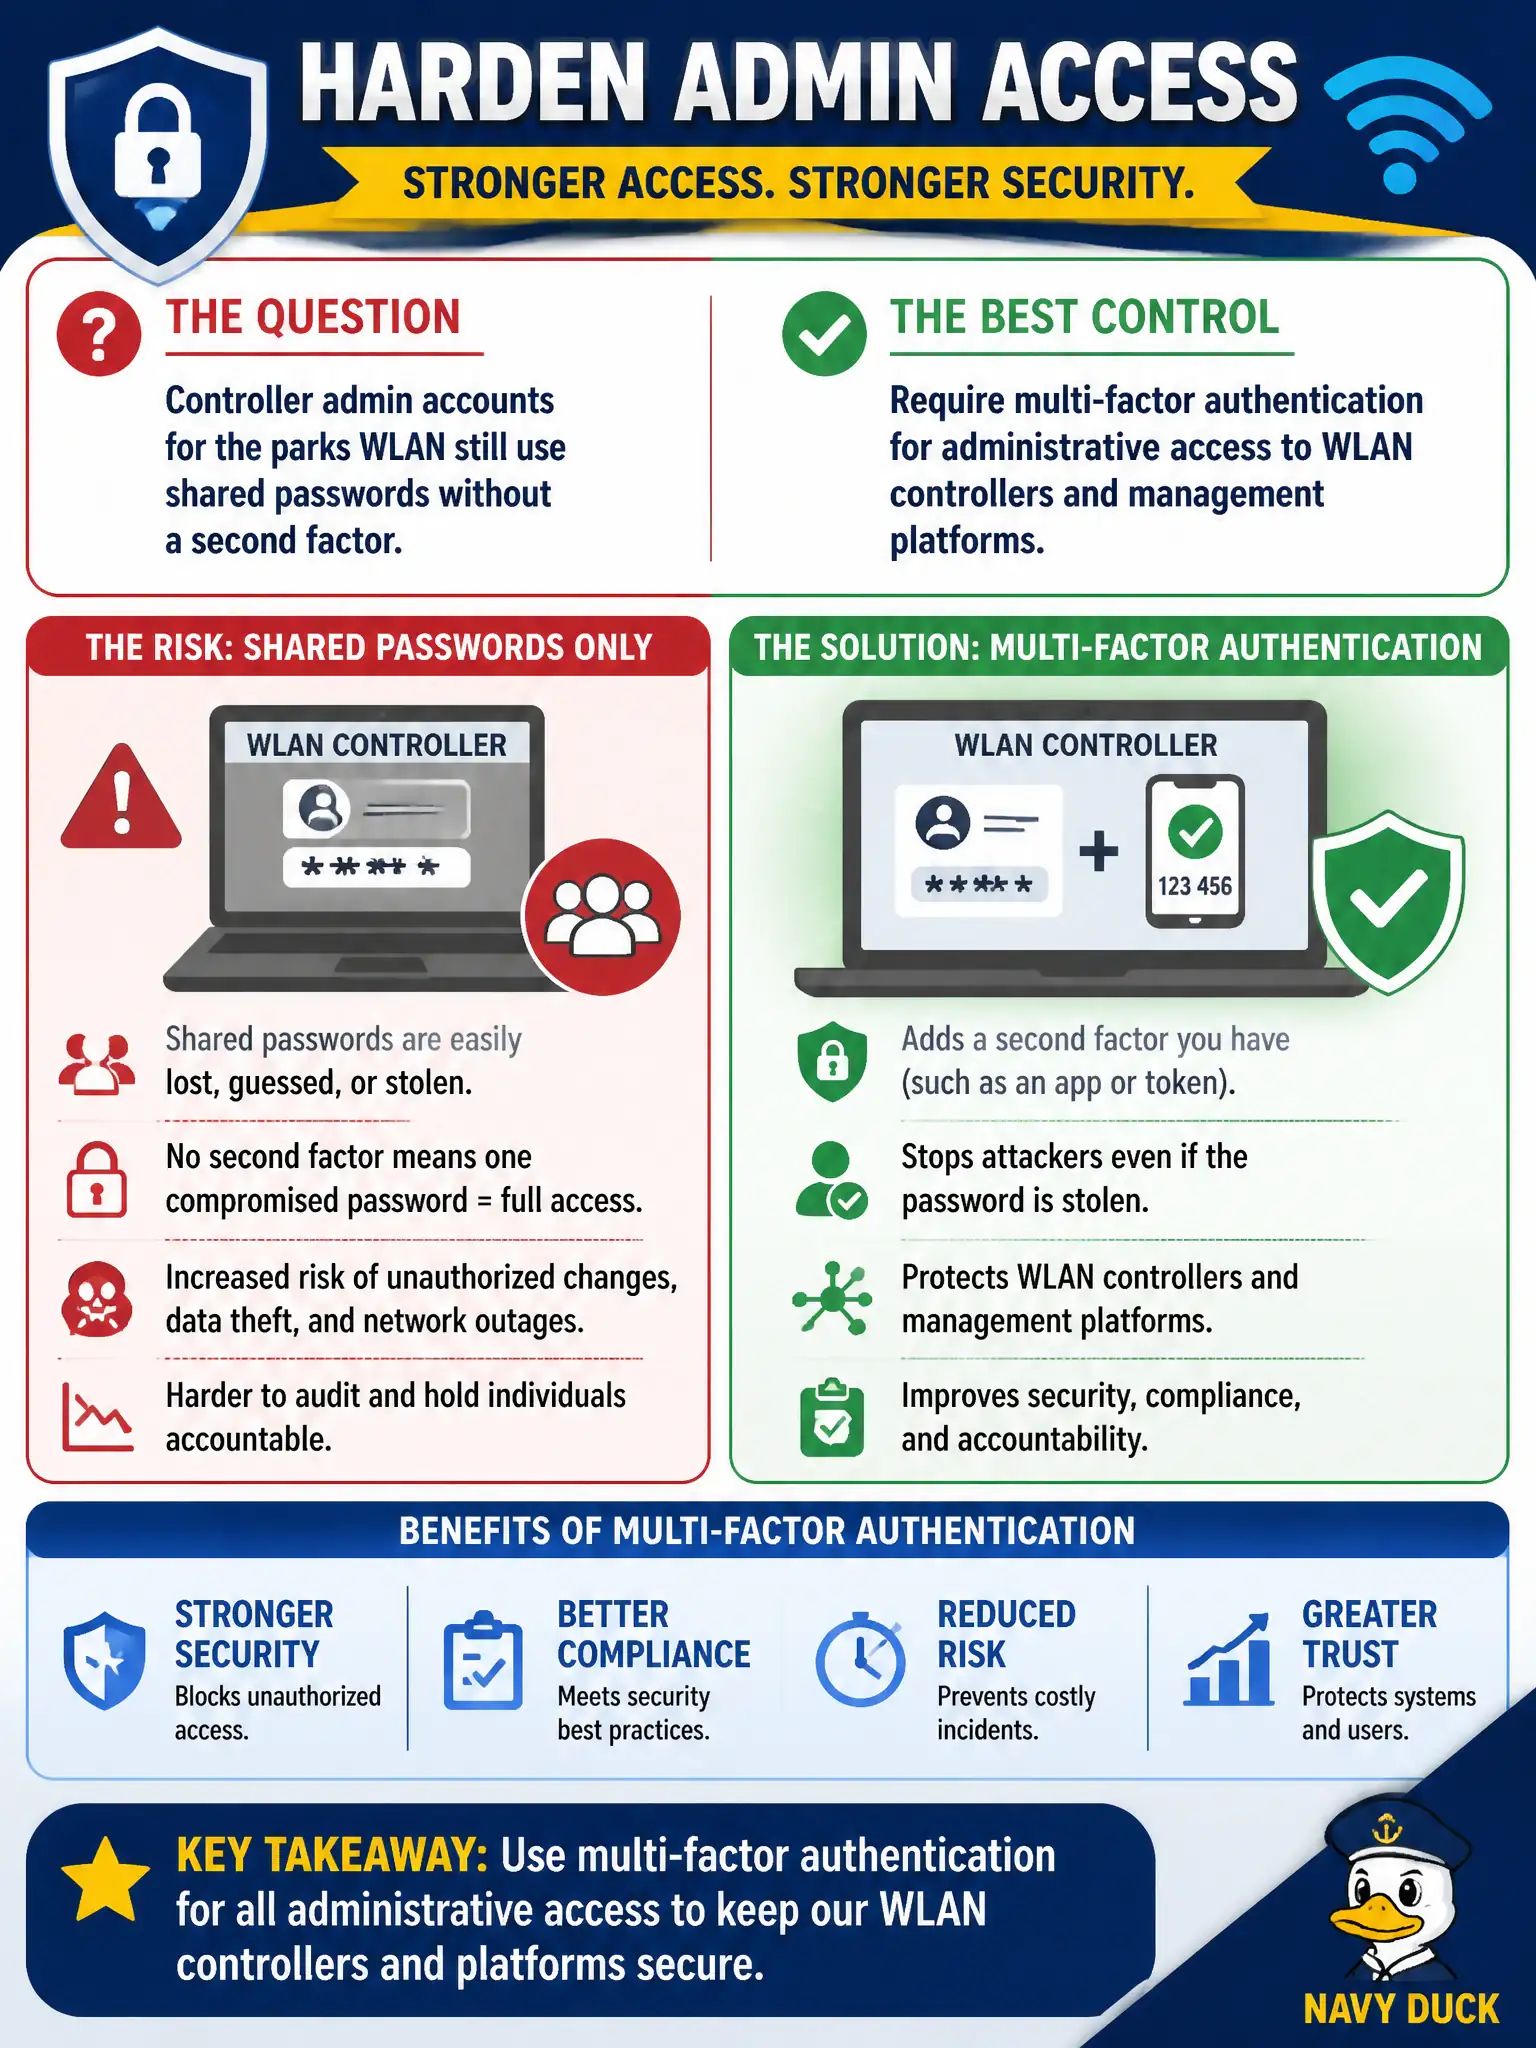
Controller admin accounts for the parks WLAN still use shared passwords without a second factor. What control best hardens administrative access?
Select an answer to reveal the explanation.
Short Explanation
Whoever can admin the controller owns the air. Put MFA on that door. Shared glove-box passwords and guest SNMP are how the network gets lost without a fight.
Full Explanation
Controller admin accounts for the parks WLAN that still use shared passwords without a second factor should require multi-factor authentication for administrative access to WLAN controllers and management platforms. Shared passwords without MFA turn one leak or shoulder-surf into full wireless estate control. Civic outdoor and parks infrastructure is too impactful for single-factor shared admin culture.
Printing the shared password weekly and storing copies in unlocked truck glove boxes maximizes exposure. Disabling all controller logging so stolen passwords leave no forensic trail is anti-forensics. Allowing anonymous read-write SNMP from the guest SSID for convenience is catastrophic.
Exam caveat: MFA should bind to named admin identities, not a shared “wifiadmin” token everyone knows. Operational check: enforce MFA on controller/NMS login, eliminate the shared password, and verify a login attempt without the second factor fails while audit logs capture the event. In municipal WLAN programs, capture the decision in the wireless standard and re-check it at change review so the next project inherits the same control bar instead of rediscovering the failure during an outage. In municipal WLAN programs, capture the decision in the wireless standard and re-check it at change review so the next project inherits the same control bar instead of rediscovering the failure during an outage.