
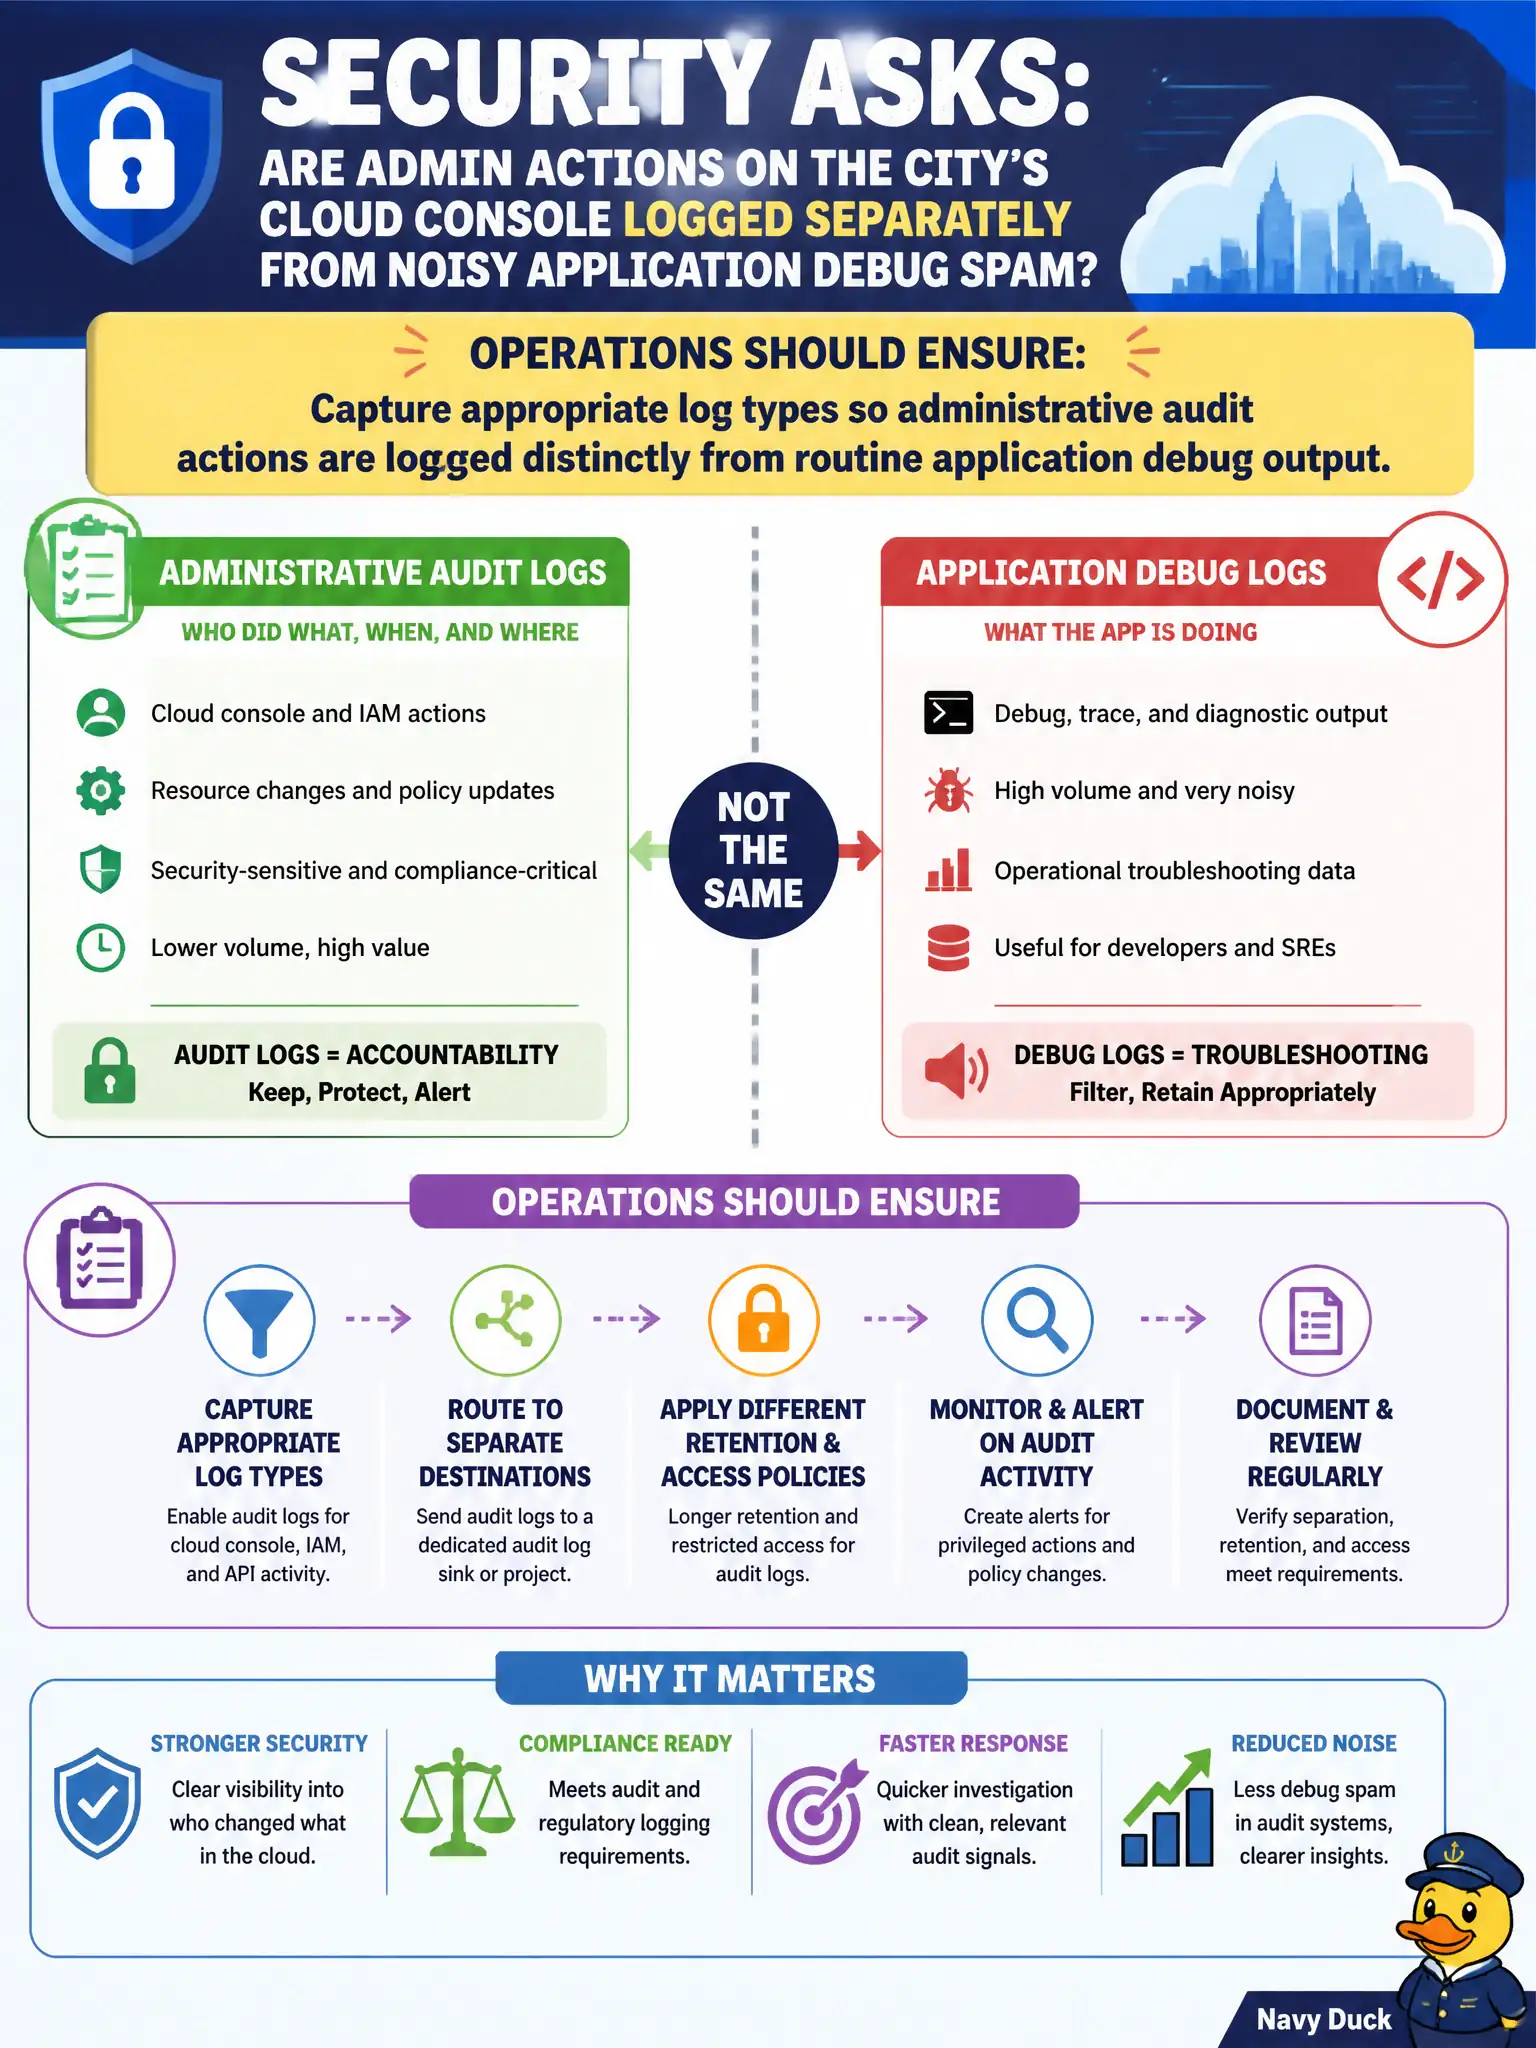
Security asks whether admin actions on the city’s cloud console are logged separately from noisy application debug spam. What should operations ensure?
Select an answer to reveal the explanation.
Short Explanation
Admin actions are the vault camera footage; debug spam is hallway chatter—you don’t file them in the same shoebox. Keep audit-quality logs for privileged work separate from noisy app debug so security can find who did what. Mixing them is how evidence disappears in the noise.
Full Explanation
Capturing appropriate log types so administrative audit actions are logged distinctly from routine application debug output lets security investigate console privilege use without drowning in debug spam from city apps. Mixing admin audit events into the same debug stream with no separation or retention difference weakens investigations and retention control. Logging only debug traces and never recording privileged console actions fails accountability for admin activity. Storing admin actions solely in personal chat messages between engineers fails durable, auditable evidence. Exam caveat: log types matter—audit/admin versus application debug—with different retention and access. Operational check: enable cloud audit logs separately, restrict who can read them, set longer retention for admin events, and sample a privileged change in a drill. In municipal platform operations, record the chosen control and the rejected alternatives in the change record so future on-call engineers understand the failure modes avoided for citizen services. Re-check the decision after the next provider feature change or compliance update to ensure the same answer still holds for the city's estate. Confirm monitoring, access reviews, and backup coverage still align with the selected approach before closing the civic hypercare period.