
A city hall-rental test lead asks which named instrument specifies requirements for managing AI systems in the organization and promotes consistent, reliable GenAI-in-testing practice. Which answer is correct?
Select an answer to reveal the explanation.
Short Explanation
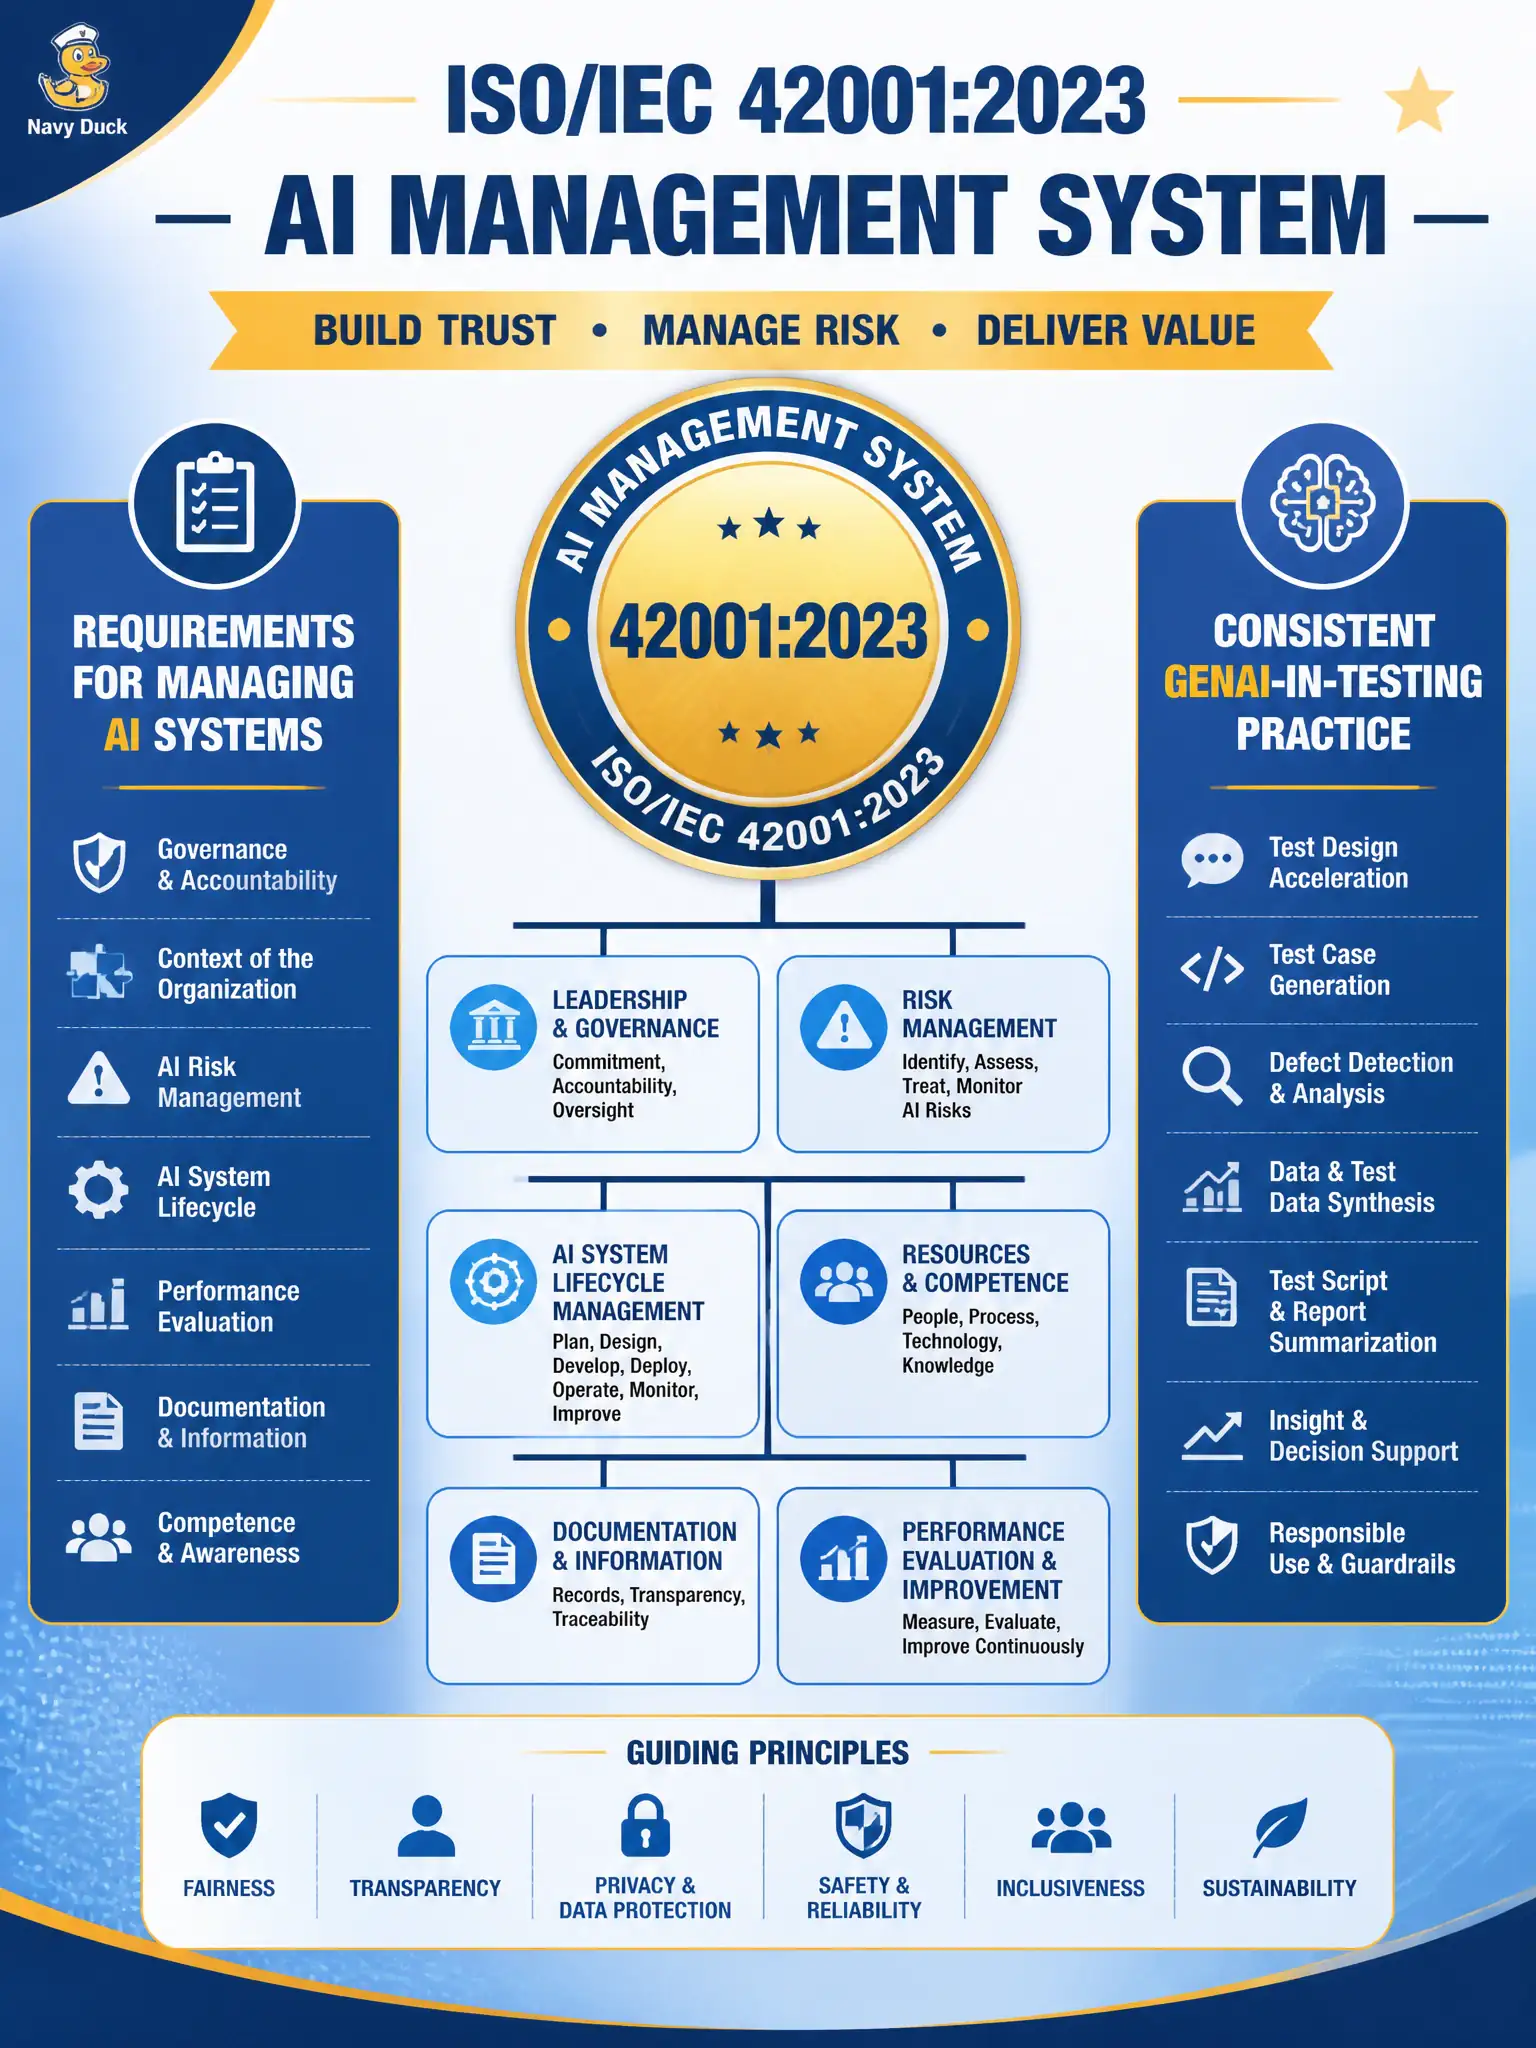
When the question is “how do we manage AI systems as an organization,” reach for ISO/IEC 42001:2023. It is the AI management-system standard that supports consistent GenAI-in-testing practice. Do not swap it with NIST’s framework, 23053’s ML framework, or GDPR’s data-protection role.
Full Explanation
City hall-rental test leads asking which instrument specifies requirements for managing AI systems in the organization and promotes consistent, reliable GenAI-in-testing practice should select ISO/IEC 42001:2023 as the AI management-system standard. Organizational management of AI is that standard’s job.
NIST AI RMF 1.0 as a binding municipal statute fails by concept: NIST RMF is a framework, not a binding statute, and not the management-system requirements standard named here. ISO/IEC 23053:2022 as the EU risk-classification regulation fails—23053 is an ML framework, not the EU regulation. GDPR as the fairness/transparency guidelines framework fails: GDPR is data-protection law, not the AI management-system standard.
Exam caveat: match instrument to role—management-system requirements → 42001.
Operational check: reference 42001 in hall-rental AI governance charters; do not relabel GDPR or NIST as the management-system standard; keep a one-page map of the four named instruments for staff. Hall-rental AI governance charters should cite ISO/IEC 42001:2023 when stating management-system requirements and avoid calling NIST or GDPR by that management-system name. Keep a four-instrument pocket card so staff can point to 42001 for organizational AIMS clauses during audits.