
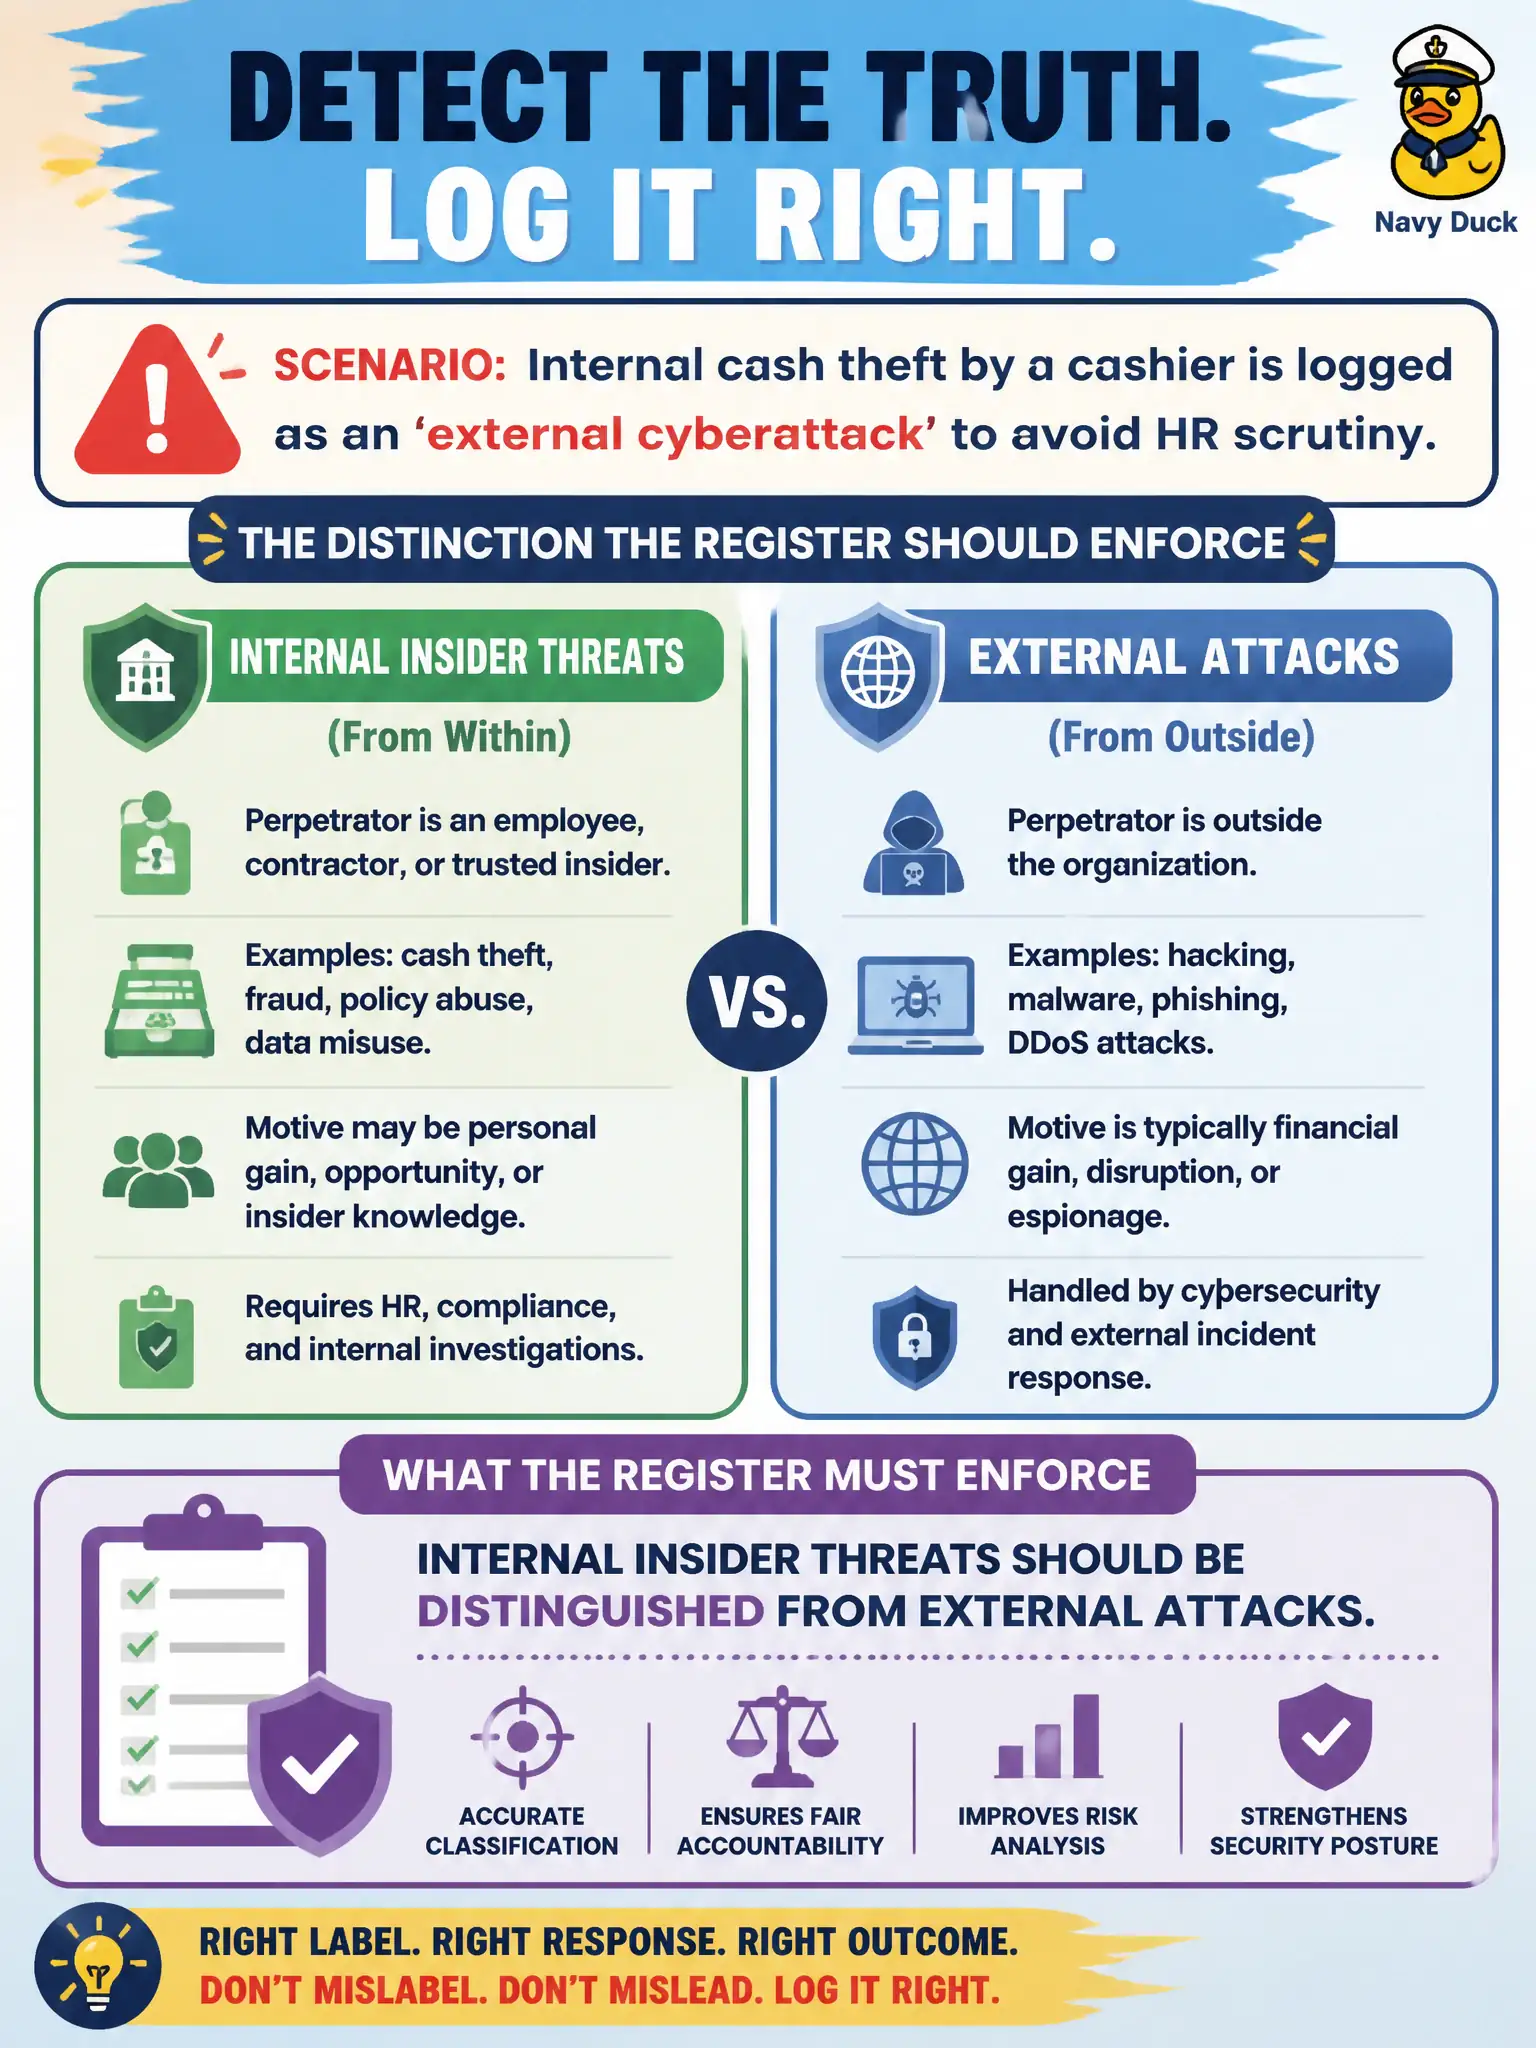
Internal cash theft by a cashier is logged as an 'external cyberattack' to avoid HR scrutiny. What distinction should the register enforce?
Select an answer to reveal the explanation.
Short Explanation
A cashier skimming the till is an insider problem, not a mysterious hacker from the internet. Mislabeling it as external cyber just hides the people controls that matter.
Full Explanation
Internal insider threats such as cashier cash theft must be distinguished from external attacks on the register. Logging internal theft as an "external cyberattack" to avoid HR scrutiny misclassifies actor, controls, and investigation path. Labeling all fraud as cyber regardless of actor confuses channels. Banning HR-related issues from operational registers hides people-driven financial crime. Preferring external labels whenever insurance forms ask for them subordinates truth to forms. Exam caveat: insider versus external distinction drives detective controls, HR process, and law-enforcement coordination. Operational check: reclassify the theft as internal/occupational fraud, involve HR and finance per policy, strengthen cash handling and surveillance controls, and keep cyber labels for actual external technical attacks. Brief the treasurer on segregation-of-duties checks at the civic cashiering point. In municipal practice, record the rationale in the risk procedure or committee minutes so future staff apply the same rule under budget pressure. Re-validate after the next seasonal peak or org-chart change to confirm the civic control still holds as designed for residents and staff.