
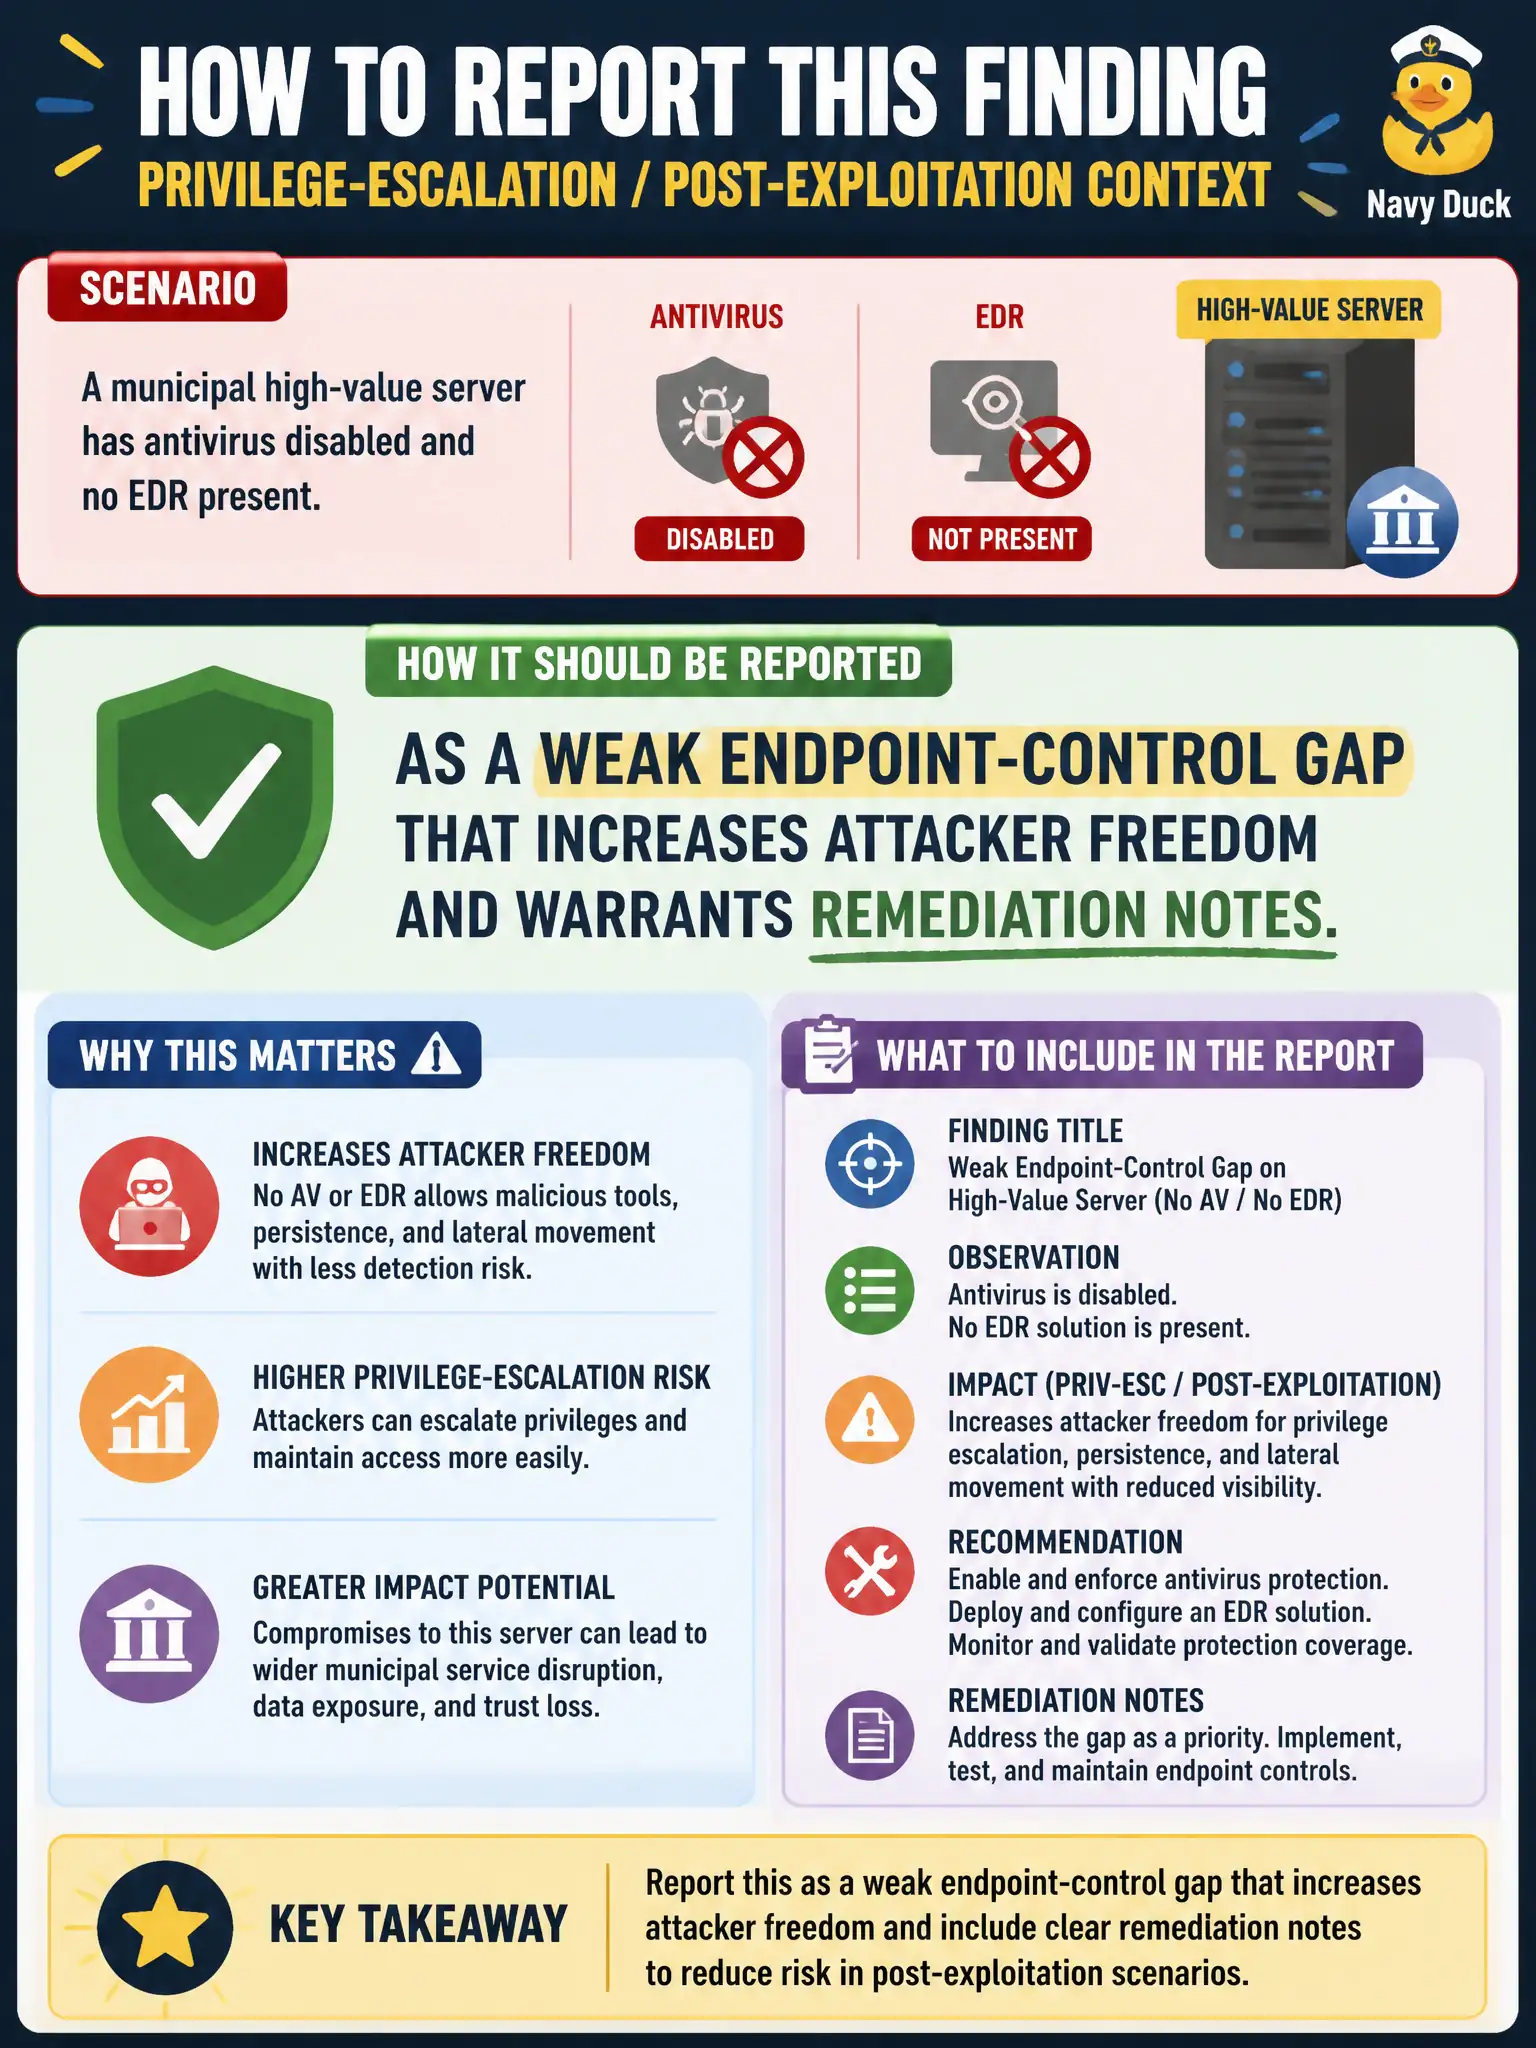
A municipal high-value server has antivirus disabled and no EDR present. How should the tester report that condition in a privilege-escalation / post-exploitation context?
Select an answer to reveal the explanation.
Short Explanation
No AV or EDR on a crown-jewel box is like leaving the alarm system unplugged. It does not invent vulnerabilities by itself, but it makes post-ex and priv-esc freer and noisier for defenders. Report the control gap and keep proving impact with real findings.
Full Explanation
A municipal high-value server with antivirus disabled and no EDR should be reported as a weak endpoint-control gap that increases attacker freedom during privilege escalation and post-exploitation. Note the gap and remediation need without claiming every technique automatically succeeds.
Missing tools do not place the server out of scope by themselves. Absence of AV/EDR is not a guarantee that every LPE technique works without evidence. Network firewalls alone do not provide complete host compromise prevention when endpoint controls are missing.
Exam caveat: explain detection debt as environmental context that raises likelihood and reduces response capability.
Operational check: document missing agents, correlate with successful stealthy actions observed under RoE, and recommend hardened EDR deployment and monitoring especially on civic crown-jewel servers. In municipal operations, record the rationale in the engagement notes so future assessors know which control was chosen and which failure modes the rejected options would create for city services. Re-validate after the next maintenance window that the same finding class still applies under the estate's current patch and configuration baseline.