
A county Windows foothold is new. Before choosing a privilege-escalation path, what situational awareness should come first?
Select an answer to reveal the explanation.
Short Explanation
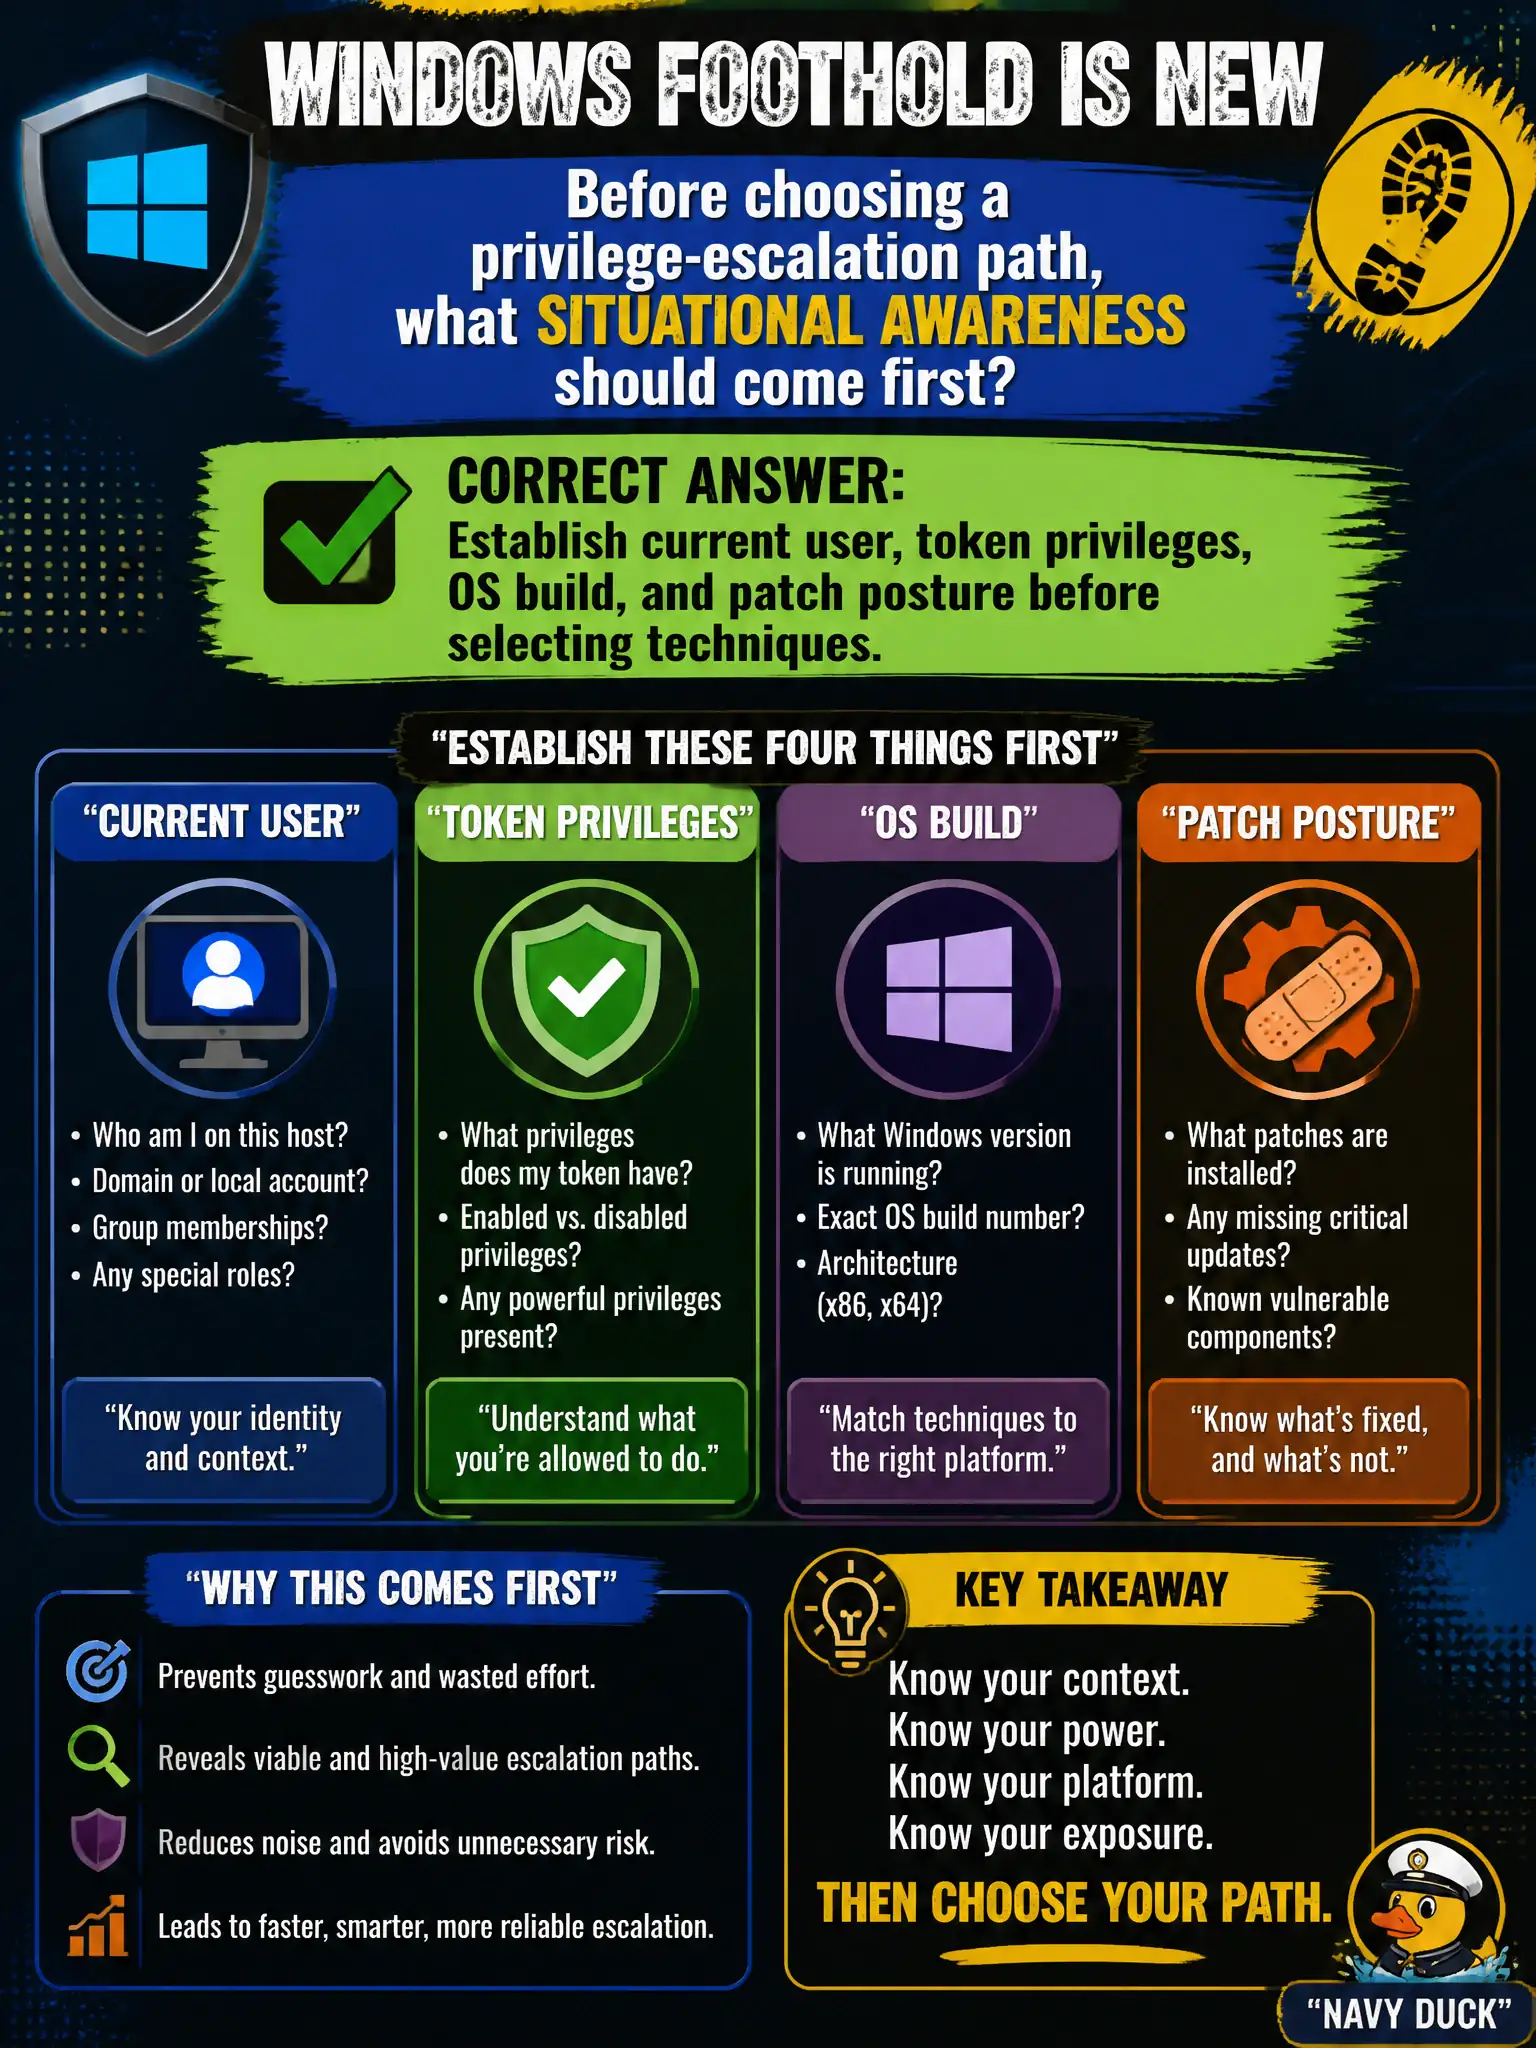
You would not pick a lock before checking which door you are standing at. On Windows, start with who you are, what privileges the token holds, and what build/patch level the box is on. That situational awareness keeps you from firing the wrong technique into the dark.
Full Explanation
On a new county Windows foothold, situational awareness precedes technique selection: establish current user, group memberships, token privileges, OS build, and patch posture before choosing privilege-escalation paths. Matching method to evidence reduces noise and avoids fragile or out-of-policy exploits.
Immediately deploying every public potato-class exploit without checking privileges or build is poor methodology. Permanently disabling the host firewall as a mandatory first step is unauthorized and harmful. Assuming Domain Admin already exists and skipping local enumeration abandons Windows LPE discipline.
Exam caveat: local admin/SYSTEM on one host remains distinct from domain privilege—keep that boundary clear in planning.
Operational check: gather whoami/privilege/build evidence with approved tools, map obvious service and task misconfigs, then select techniques aligned to findings. Document the host's municipal role for impact context. In municipal operations, record the rationale in the engagement notes so future assessors know which control was chosen and which failure modes the rejected options would create for city services. Re-validate after the next maintenance window that the same finding class still applies under the estate's current patch and configuration baseline.