
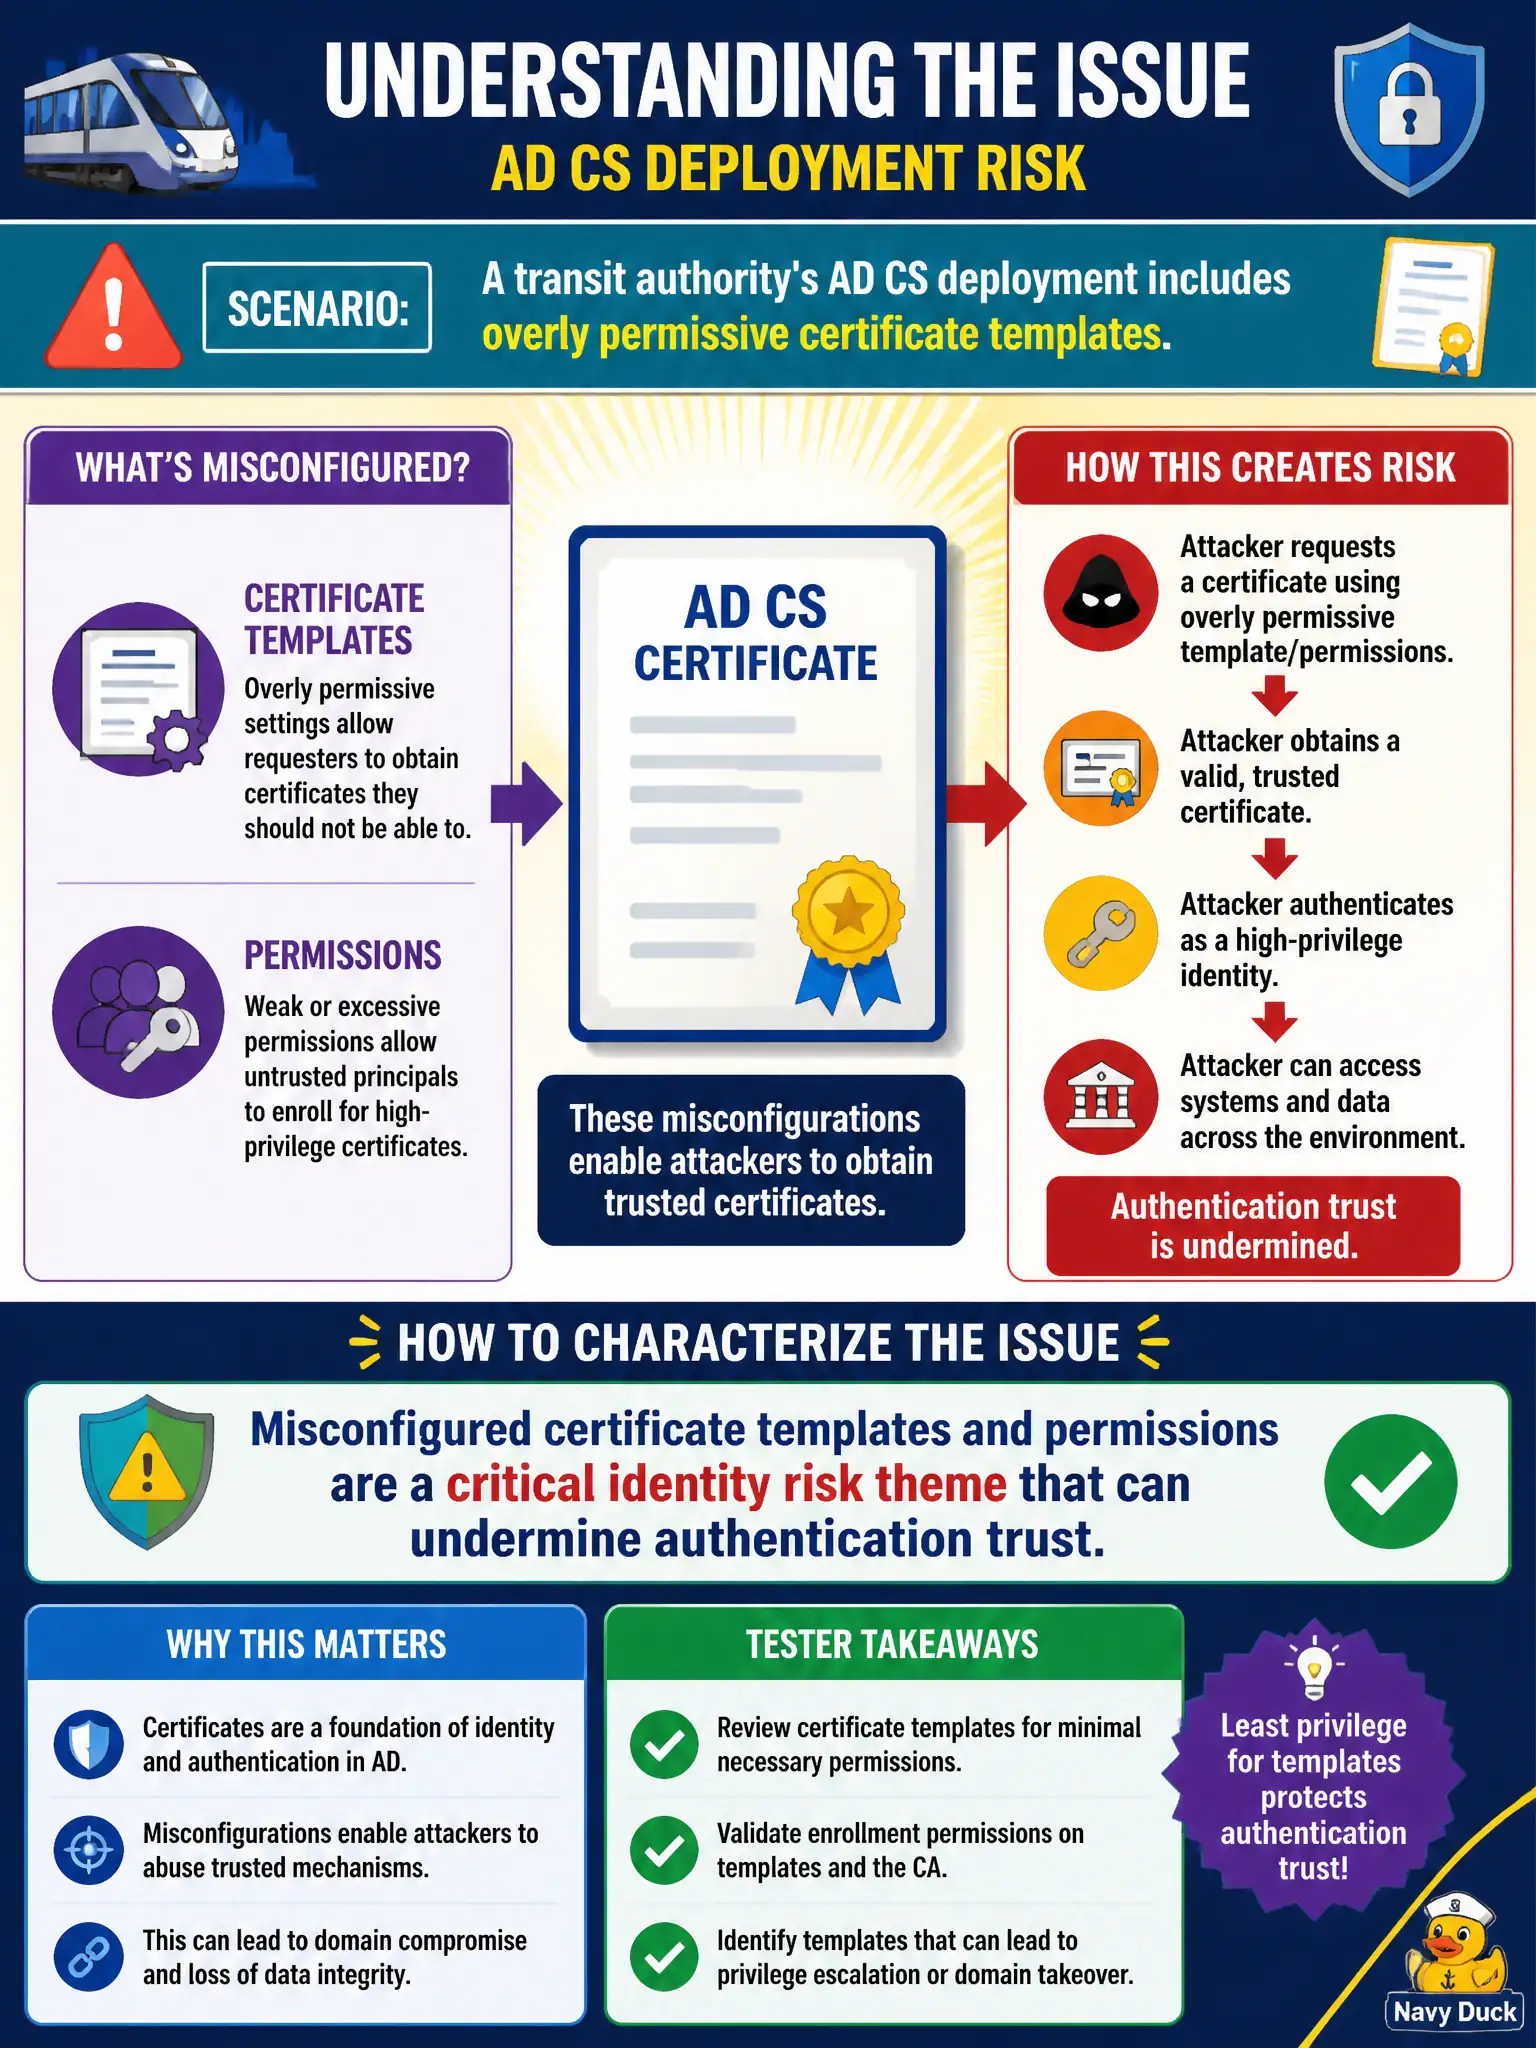
A transit authority's AD CS deployment includes overly permissive certificate templates. How should the tester characterize the issue?
Select an answer to reveal the explanation.
Short Explanation
Certificates are trust tokens. If templates are wide open, you have basically left the badge printer on free mode. Call AD CS template misconfigs what they are — high-impact identity risk — without writing an exploit novella.
Full Explanation
A transit authority’s AD CS deployment with overly permissive certificate templates should be characterized as a critical identity risk theme that can undermine authentication trust. Certificate templates are not merely printer watermark controls. AD CS misconfigurations remain relevant even if domain controllers are patched monthly—patching does not fix template permissions. Permissive templates are not required for every user mailbox and should be reported when they over-grant enrollment or EKUs. Exam caveat: treat ESC-class themes as configuration risk narratives, not exploit cookbooks in the main report. Operational check: review template enrollment permissions and extended key usages with authorized access, recommend locking down enrollment and manager approval where needed, and coordinate revocation/monitoring with the transit PKI owners. In municipal operations, record the rationale in the engagement notes so future testers and city defenders understand which approach was chosen and which failure modes the rejected options would create for civic services. Re-validate the same judgment after the next change window so the control still holds under the city’s current tooling, identity posture, and RoE amendments.