
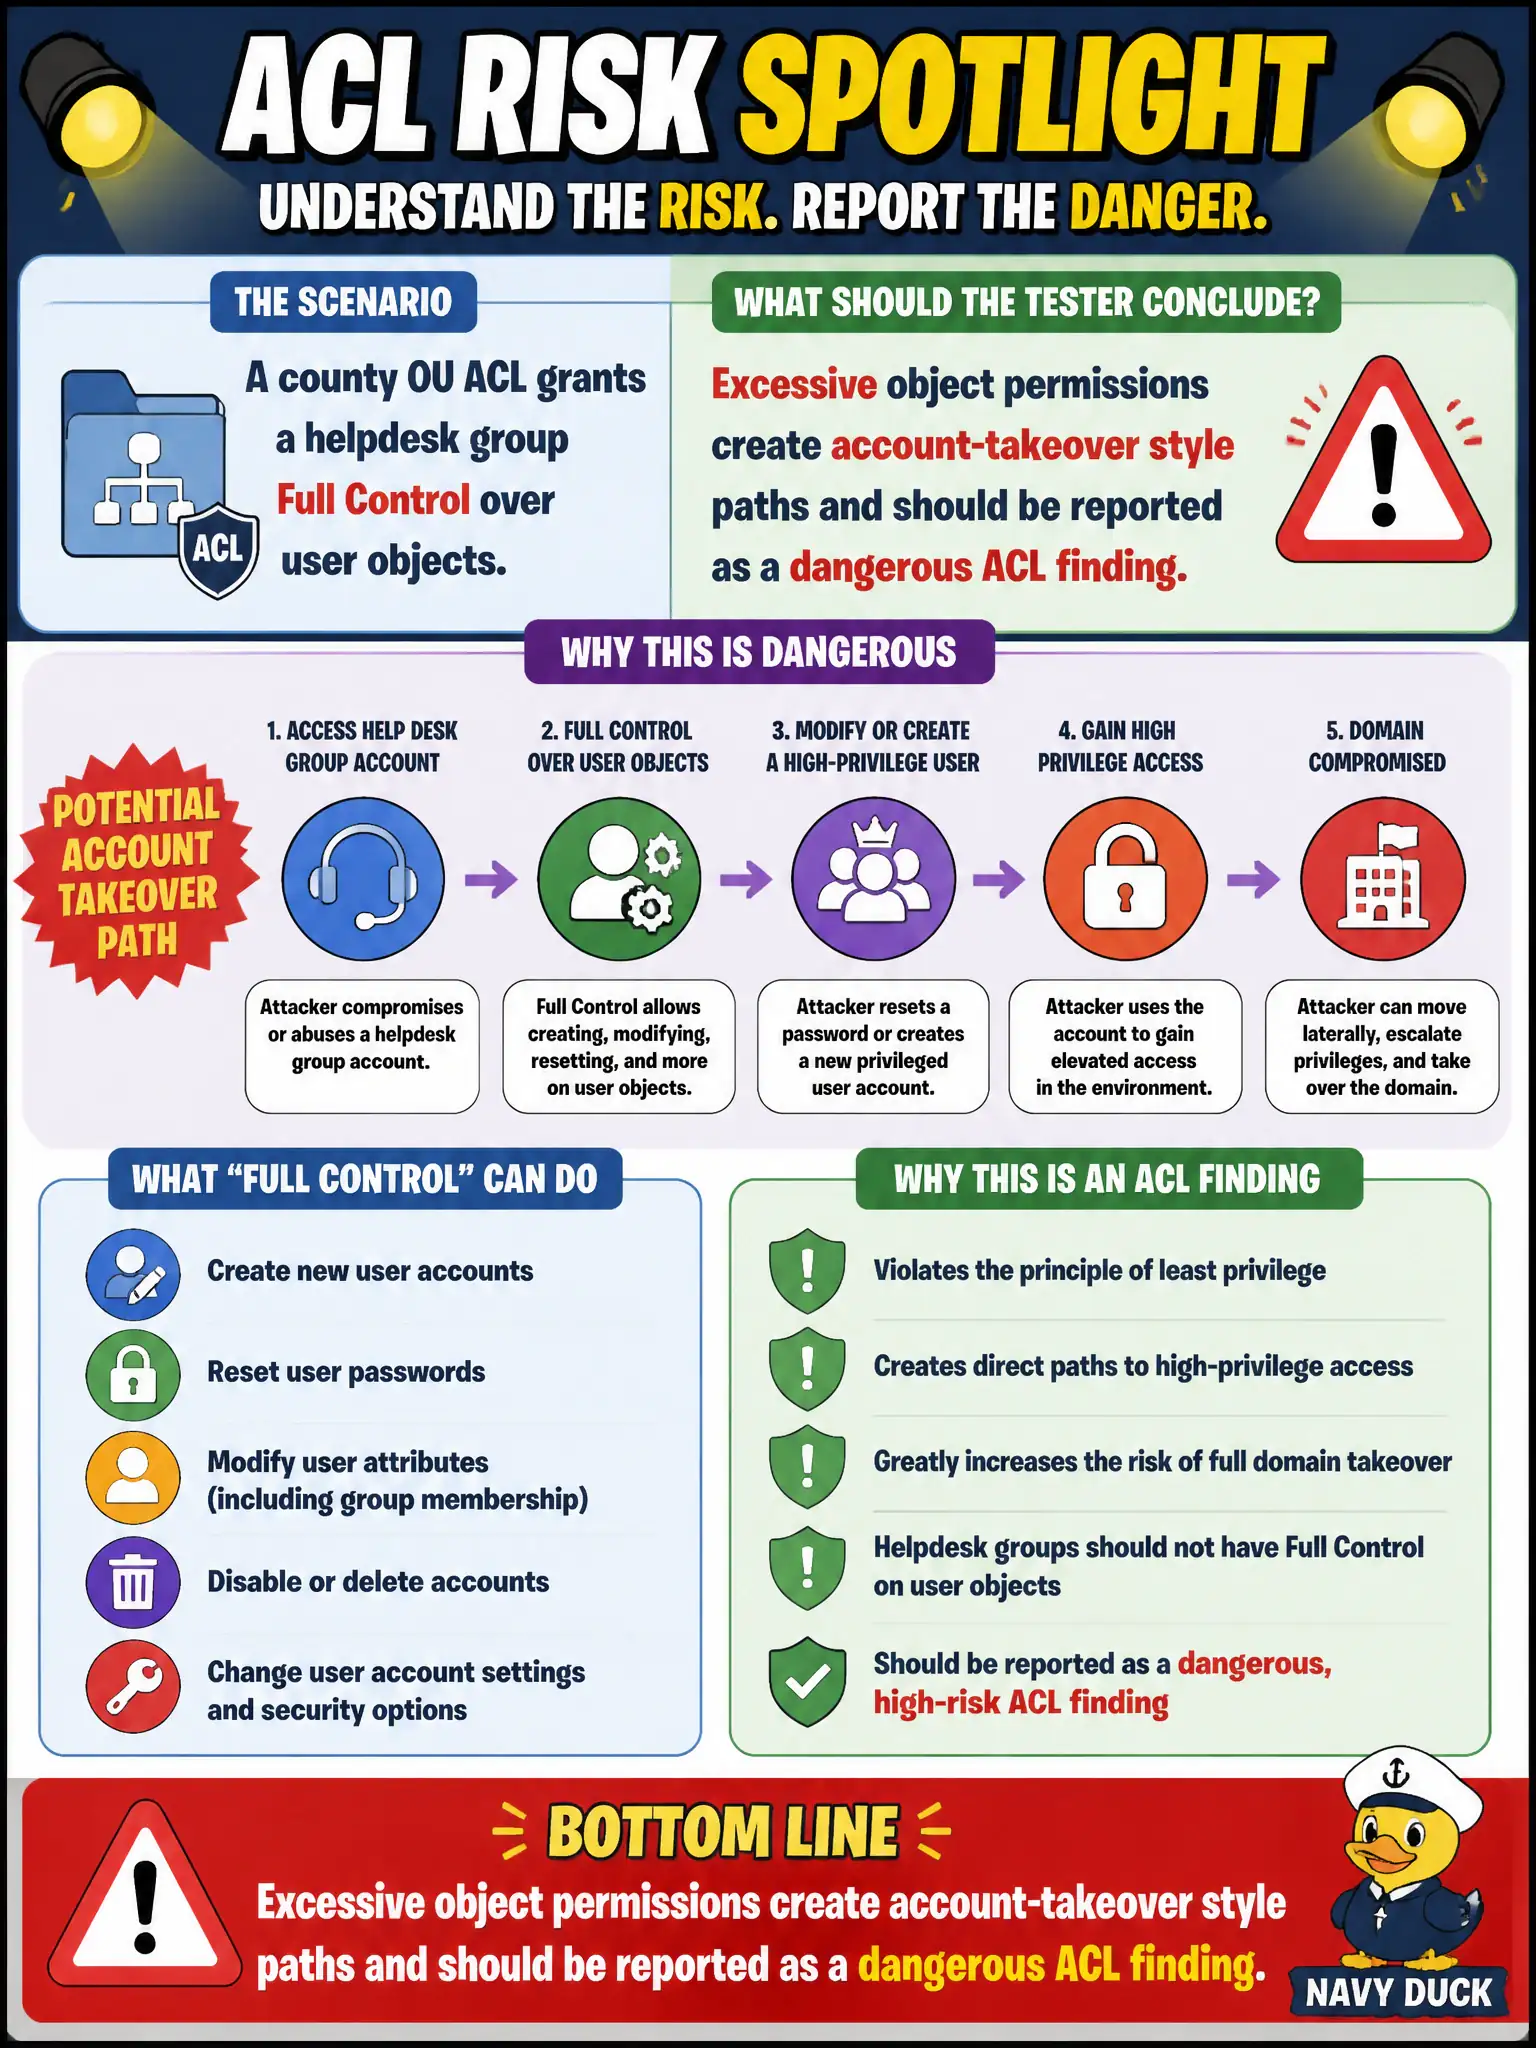
A county OU ACL grants a helpdesk group Full Control over user objects. What should the tester conclude?
Select an answer to reveal the explanation.
Short Explanation
Full Control on user objects is not a participation trophy — it can mean reset, modify, and take over. If helpdesk has that on an OU, you have found a dangerous ACL path worth elevating.
Full Explanation
If a county OU ACL grants a helpdesk group Full Control over user objects, the tester should conclude that excessive object permissions create account-takeover style paths and should be reported as a dangerous ACL finding. Helpdesk Full Control is not a cosmetic permission with no abuse potential. OU ACLs absolutely can affect account security beyond Domain Admins alone. Full Control is not limited to reading thumbnail photos and should not be waved off as low priority. Exam caveat: directory ACL review is a first-class AD assessment activity. Operational check: export the relevant ACL entries, explain takeover potential in municipal terms, recommend least-privilege helpdesk roles (reset/unlock without Full Control), and monitor privileged directory changes while remediation proceeds. In municipal operations, record the rationale in the engagement notes so future testers and city defenders understand which approach was chosen and which failure modes the rejected options would create for civic services. Re-validate the same judgment after the next change window so the control still holds under the city’s current tooling, identity posture, and RoE amendments. Keep secret material and session artifacts in the approved vaulted workflow rather than chat paste or unprotected tickets used by mixed municipal teams.