
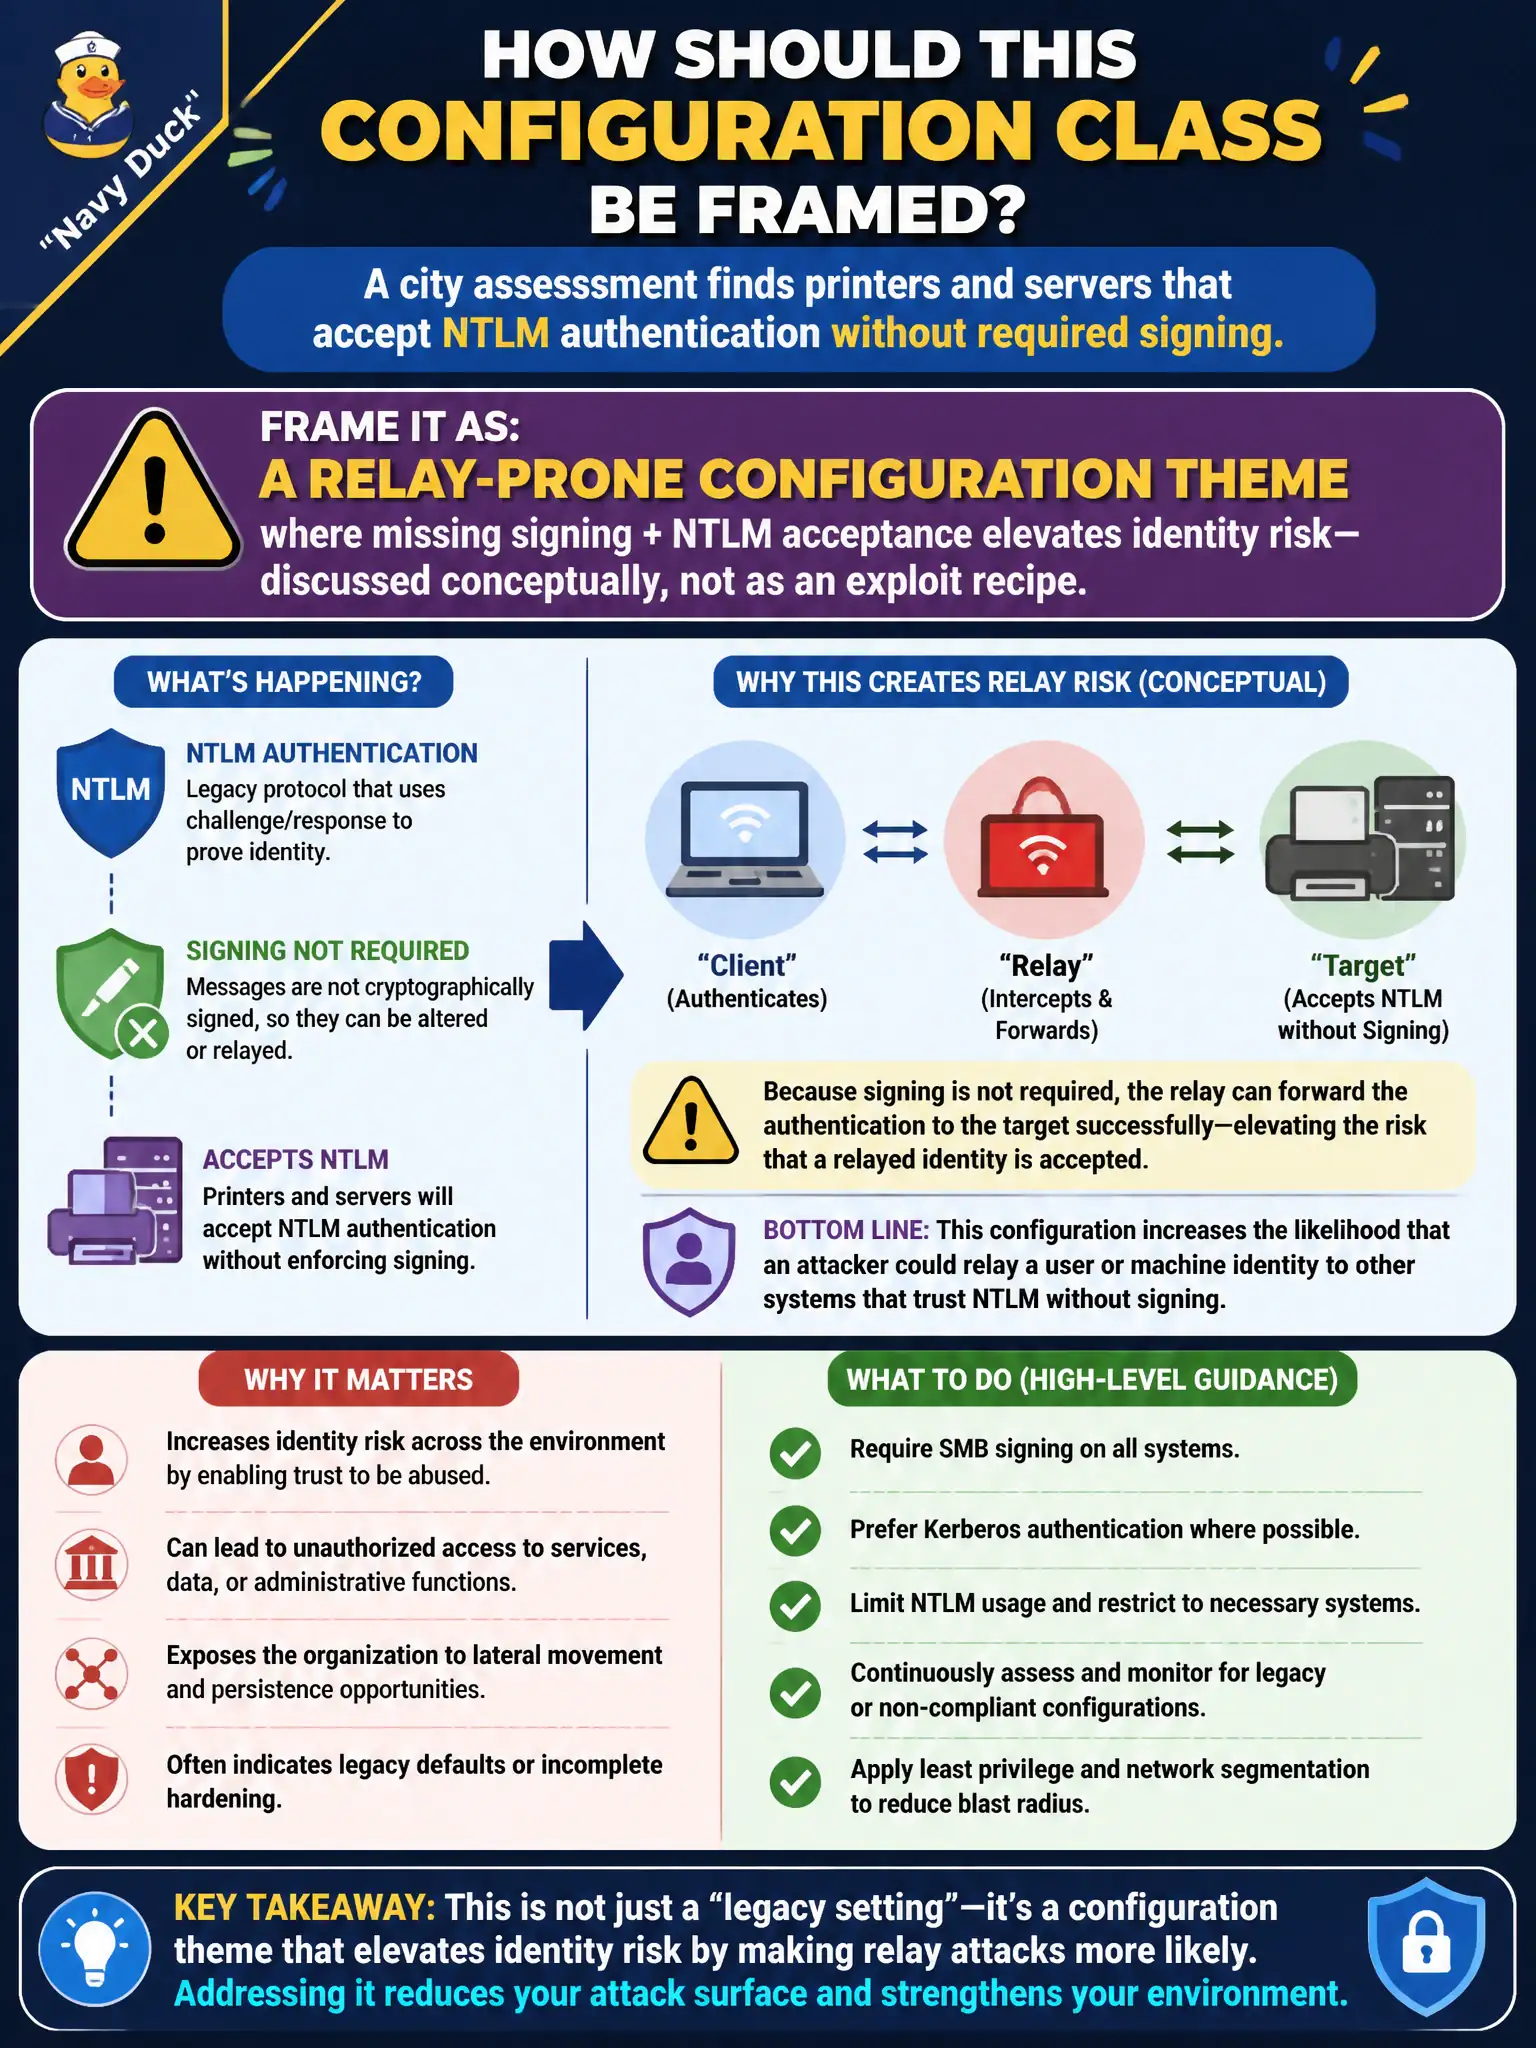
A city assessment finds printers and servers that accept NTLM authentication without required signing. How should this configuration class be framed?
Select an answer to reveal the explanation.
Short Explanation
NTLM without signing is like accepting a handed-off badge without checking the face. That gap is the classic setup for relay-shaped problems. Flag the config class; you do not need a lab walkthrough to make the point.
Full Explanation
When a city assessment finds printers and servers that accept NTLM authentication without required signing, frame the configuration class as a relay-prone theme where missing signing plus NTLM acceptance elevates identity risk—discussed conceptually, not as an exploit recipe. That configuration does not prove relay-class attacks are impossible. It should not be dismissed as an untouchable requirement for cloud backup agents without analysis. It is not evidence that smart cards have replaced all password authentication. Exam caveat: report the hardening gap and remediation controls; avoid turnkey relay instructions in the public finding text. Operational check: inventory signing requirements and NTLM acceptance on representative hosts, recommend SMB signing and EPA/channel-binding controls, restrict NTLM where feasible, and retest policy application after GPO changes. In municipal operations, record the rationale in the engagement notes so future testers and city defenders understand which approach was chosen and which failure modes the rejected options would create for civic services. Re-validate the same judgment after the next change window so the control still holds under the city’s current tooling, identity posture, and RoE amendments.