
A network team needs months of data showing which internal hosts communicate with which external addresses, on which ports, and how much data moves, without storing packet payloads. Which source BEST meets this requirement?
Select an answer to reveal the explanation.
Short Explanation
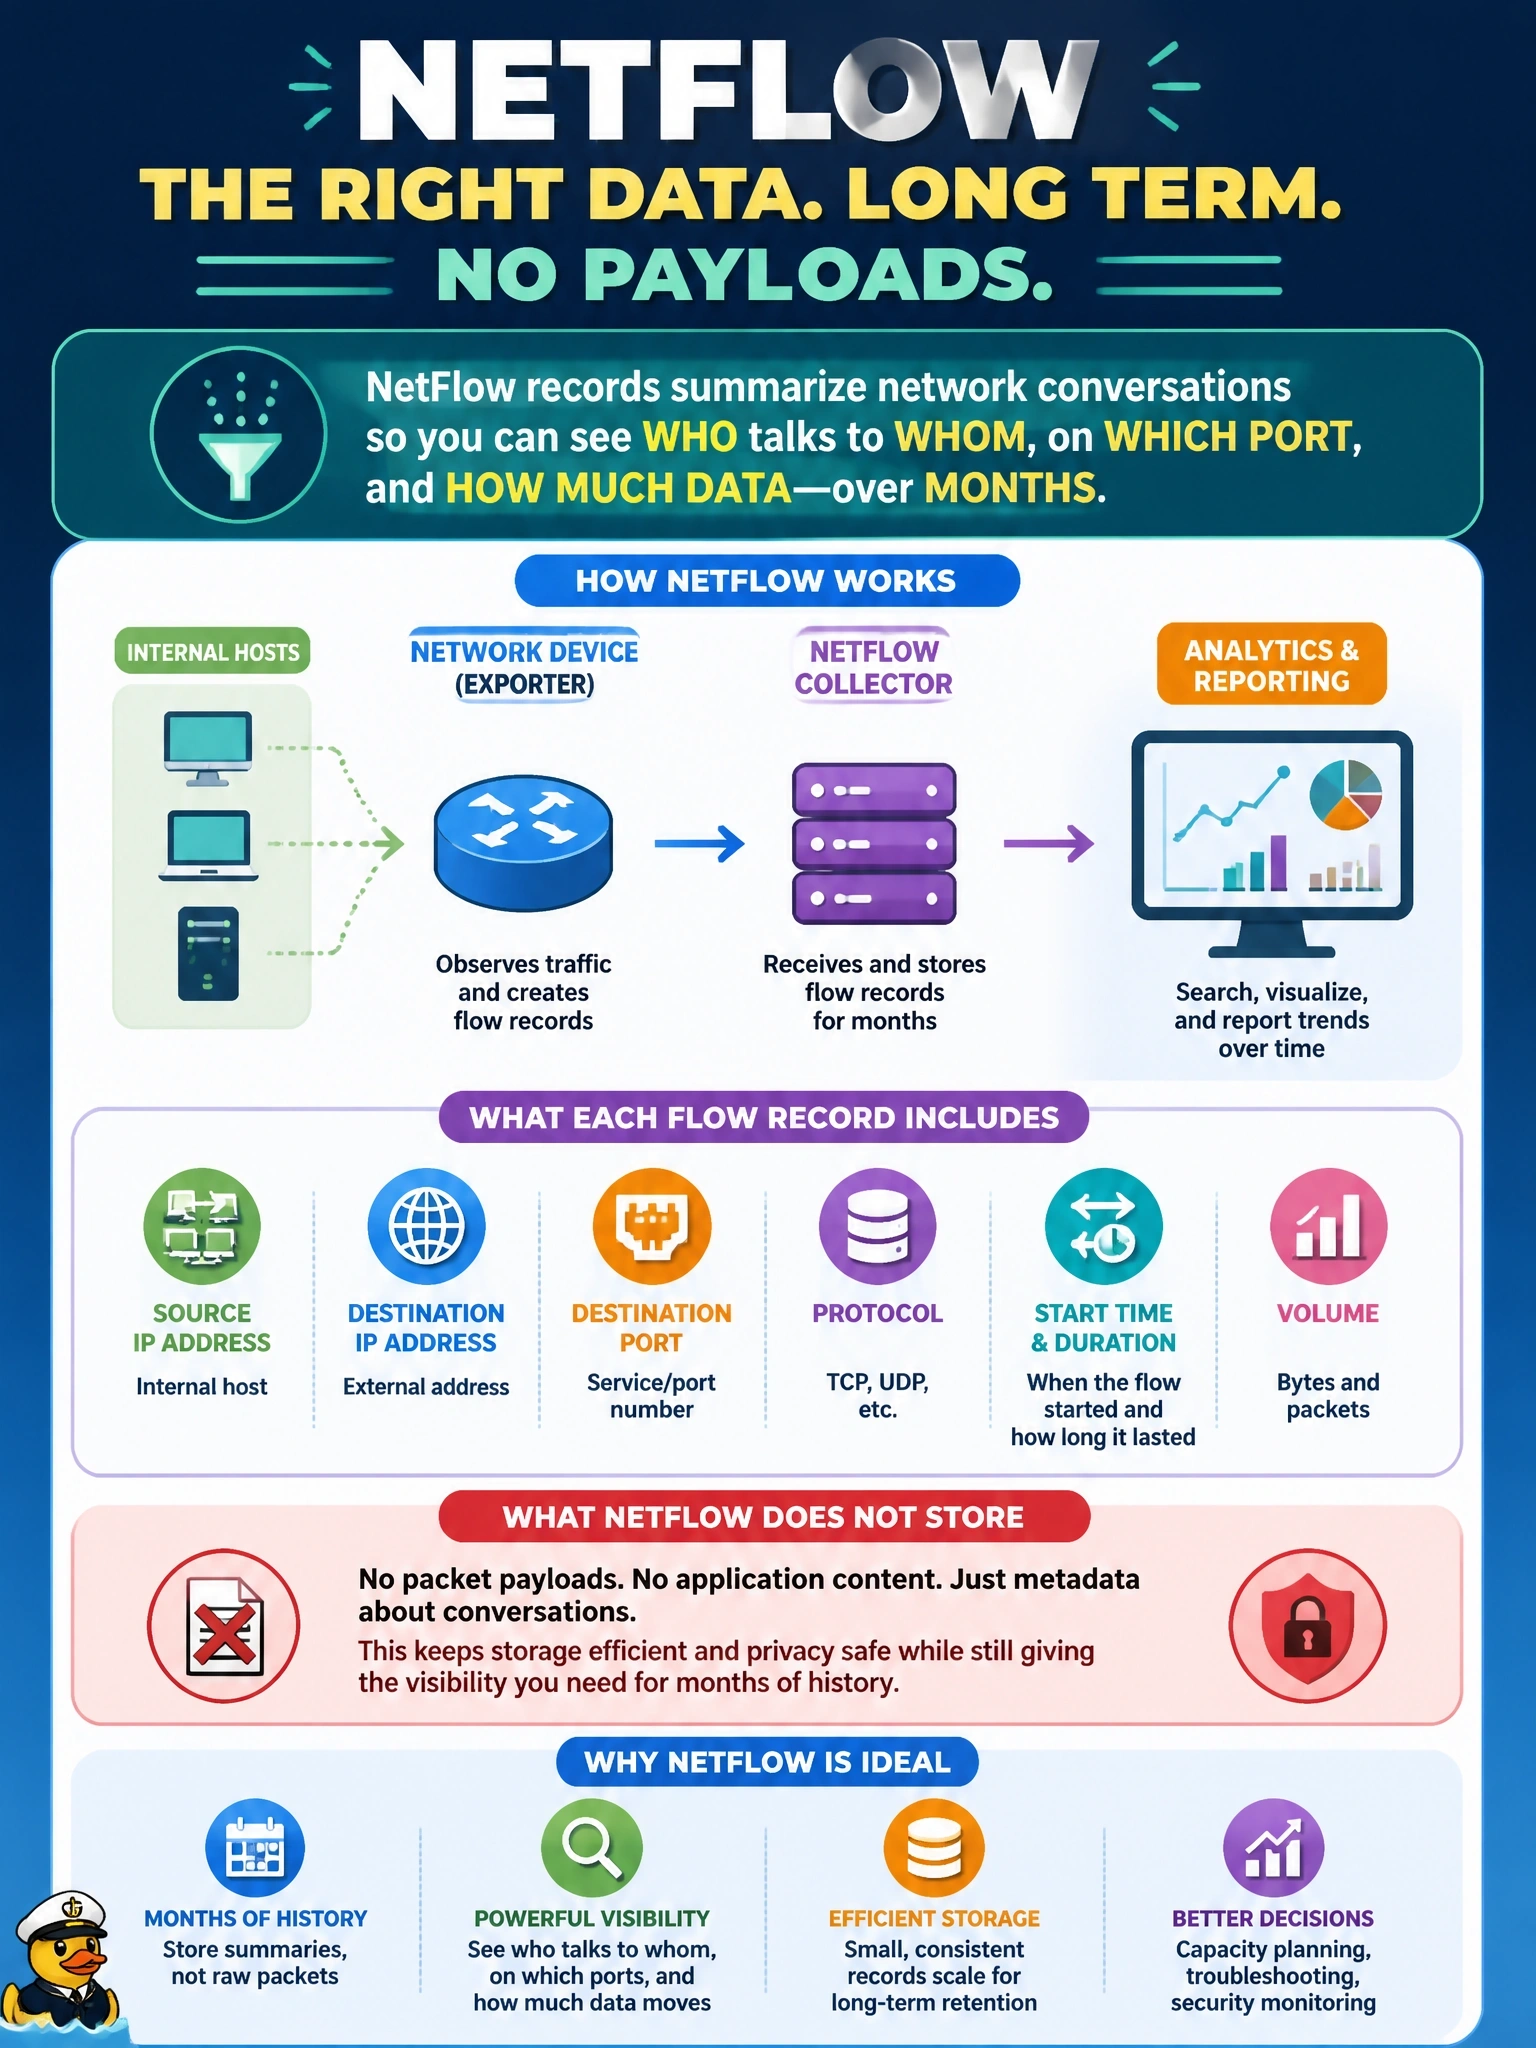
NetFlow is the phone bill, not the phone recording - who called whom, when, and for how long, but not what was said. That's exactly what you want when you need months of history without storing payloads. SNMP counters only tell you how busy each line was, not who was on it.
Full Explanation
NetFlow and similar flow protocols export metadata about network conversations: source and destination addresses, ports, protocol, timestamps, and byte and packet counts. Because flow records omit payloads, they are compact enough to keep for long periods and are well suited to traffic analysis, baselining, and spotting unusual destinations or large transfers. That matches the requirement precisely. Full packet capture records complete packets, including payloads, which the scenario explicitly does not want, and keeping months of it is costly in storage and raises privacy concerns. A packet analyzer is ideal for deep inspection of a short window, not for long-term conversation history. Syslog messages from server operating systems describe host events such as logins and service changes; they do not systematically record every network conversation and its volume. SNMP polling of interface counters reports how much traffic crossed each port, but it does not identify which hosts communicated with which addresses, so it cannot answer the who-talked-to-whom question. Exam caveat: flow data shows that a transfer happened, not what it contained; investigations may still need targeted packet capture. Operational check: confirm flow export is enabled on edge devices and verify the collector shows records for a known test connection.